
commons-text-goat
 tulhan/commons-text-goat
An intentionally vulnerable webapp to get your hands dirty with CVE-2022-42889.
educationexploitationlabs-practice+3
1
tulhan/commons-text-goatAn intentionally vulnerable webapp to get your hands dirty with CVE-2022-42889.
 arkha-corvus/letsdefend-soc235-atlassian-confluence-broken-access-control-0-day-cve-2023-22515-eventid-197
I was presented with a high-severity alert indicating a potential exploit attempt of CVE-2023-22515, a zero-day vulnerability in Atlassian…
 mobilelinux/iovy_root_research
A root tool based on the [CVE-2015-1805 vulnerability](https://access.redhat.com/security/cve/cve-2015-1805) It supports 32 and 64bit, get sys call…
 paulvkitor/log4shellwithlog4j2_13_3
Springboot web application accepts a name get parameter and logs its value to log4j2. Vulnerable to CVE-2021-44228.
 elw0od/pentesterlab
OrangeBadge - Exercise CVE-2018-6574: go get RCE
 s-h-3-l-l/katoolin3
Get your favourite Kali Linux tools on Debian/Ubuntu/Linux Mint
 neweracracker/loic
Deprecated - Low Orbit Ion Cannon - An open source network stress tool, written in C#. Based on Praetox's LOIC project. USE ON YOUR OWN RISK. WITHOUT…
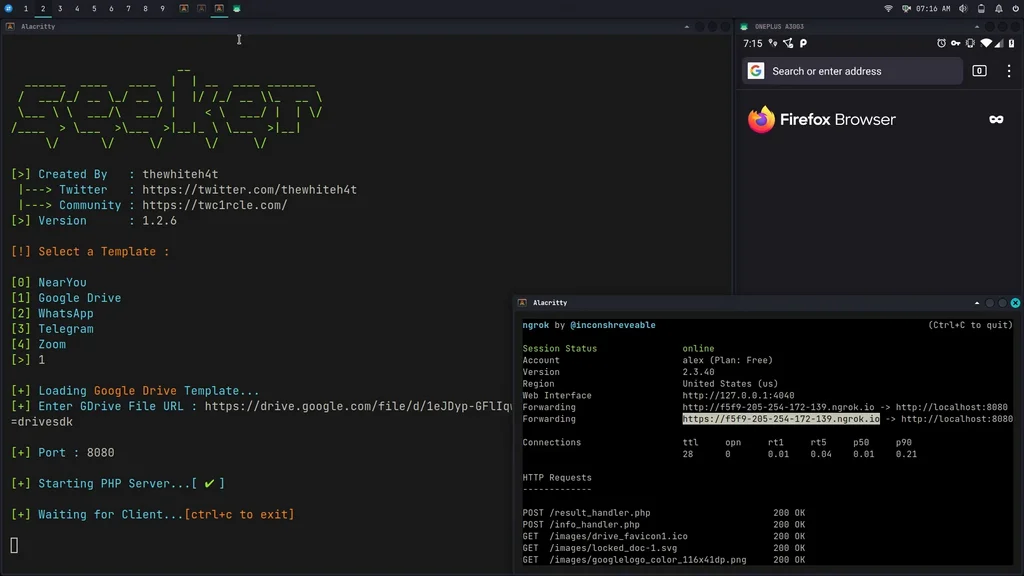 thewhiteh4t/seeker
Accurately Locate Smartphones using Social Engineering
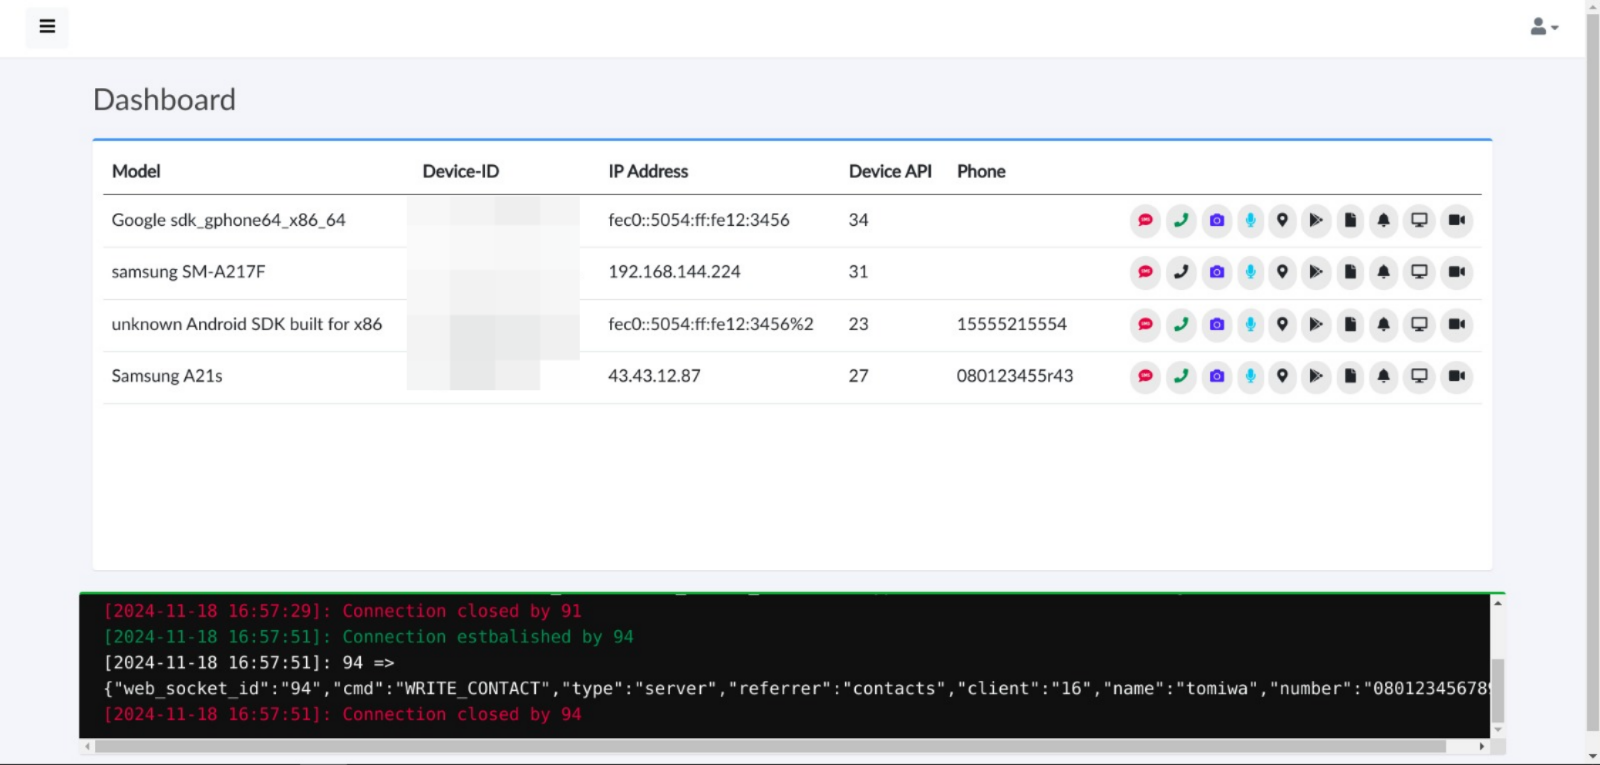 tomiwa-ot/moukthar
Android remote administration tool
 davideolgiati/partyloud
A simple tool to generate fake web browsing and mitigate tracking
 fransr/hot-jar-swapping-urlclassloader
Demo of the URLClassLoader JAR-swapping showing the ability to replace and exploit an already loaded JAR with inner classes
 therealjunior/mtk-su-reverse-cve-2020-0069
reversing mtk-su
 al1ex/cve-2021-4034
Local Privilege Escalation in polkit's pkexec (CVE-2021-4034)
 wack0/cve-2022-35841
small writeup on EnterpriseModernAppManager::ProvisionApplication bug
 shinthink/cve-2026-15282
Instant Appointment <= 1.2 — Unauthenticated Arbitrary File Upload to RCE via add_service_front AJAX | CVSS 9.8
 digamma-ai/cve-2020-8835-verification
Coq-based formal verification of a Linux kernel eBPF verifier vulnerability (CVE-2020-8835) with reproducible build environment and proof artifacts.
 zzzz0317/log4j2-vulnerable-spring-app
CVE-2021-44228