
sshfinder
 kabiri-labs/sshfinder
Parallel SSH service discovery and security auditor that scans any port, validates SSH banners, and audits authentication methods, weak cryptography,…
cryptographyinformation-gatheringnetwork-security+5
3
kabiri-labs/sshfinderParallel SSH service discovery and security auditor that scans any port, validates SSH banners, and audits authentication methods, weak cryptography,…
 chuzhongyun/cve-2026-53359-kernel-fix
Linux 内核升级指南 - 修复 CVE-2026-53359
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 linuxkernelcontent/dirtycow
Below code takes advantage of a known vulnerability [Dirty COW (CVE-2016-5195)] 🔥
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 yevh/cve-2020-5752-druva-insync-windows-client-6.6.3---local-privilege-escalation-powershell-
Druva inSync Windows Client 6.6.3 - Local Privilege Escalation (PowerShell) RCE
 nxploited/cve-2026-13714
Realtyna Organic IDX plugin + WPL Real Estate < 5.3.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 resi-le/nxloader
An app that enables payload injection into a Switch console from an Android device by exploiting the CVE-2018-6242 vulnerability
 liumuqing/cve-2021-3899_poc
race condition in apport lead to Local Privilege Escalation on Ubuntu

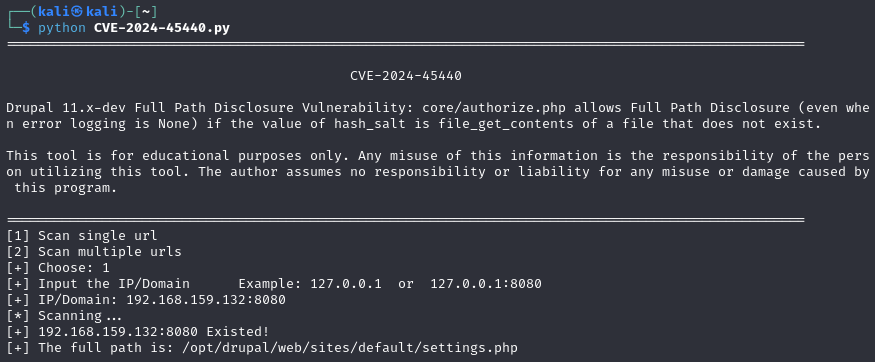 w0r1i0g1ht/cve-2024-45440
Drupal CVE-2024-45440
 b4dboy17/dirty-pipe-oneshot
Compled version of CVE-2022-0847 aka Dirty Pipe. Just one shot to root them all :D
 0x0w1z/cve-2025-61777
CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
 1337-llama/cve-2020-0688-python3
Exploit updated to use Python 3.
 mastercode112/upgraded_bluebourne-cve-2017-0785-
upgraded of BlueBourne CVE-2017-0785 to python3
 johanneslks/cve-2026-32945
PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
 alexmullins/dsa
Analysis of CVE-2016-3959 and a Proof of Concept Attack Against a Go SSH Server.
 karzsghr/s2-046_s2-045_poc
S2-046|S2-045: Struts 2 Remote Code Execution vulnerability(CVE-2017-5638)