

msf-auxiliarys
 r00t-3xp10it/msf-auxiliarys
My collection of metasploit auxiliary post-modules
exploit-frameworkspenetration-testingpenetration-testing-frameworks+2
191
r00t-3xp10it/msf-auxiliarysMy collection of metasploit auxiliary post-modules
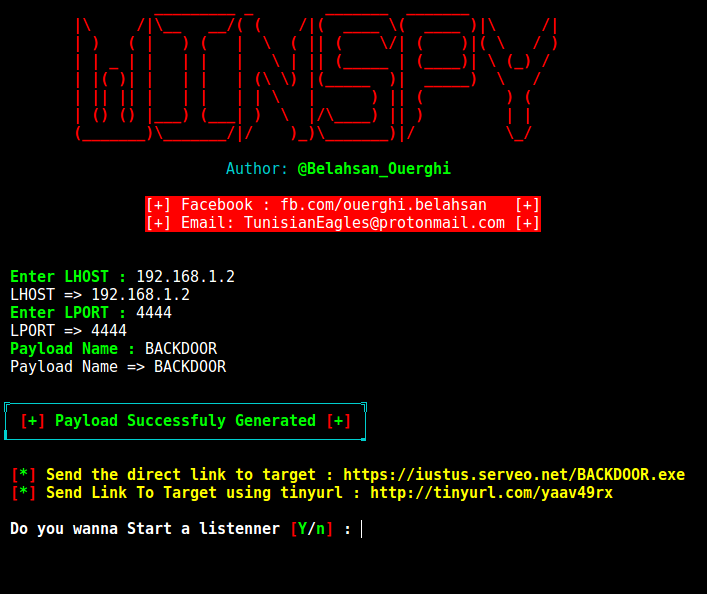 cyb0r9/winspy
Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…
 getrektboy724/betterxencrypt
A better version of Xencrypt.Xencrypt it self is a Powershell runtime crypter designed to evade AVs.
 outflanknl/wdtoggle
A Beacon Object File (BOF) for Cobalt Strike which uses direct system calls to enable WDigest credential caching.
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
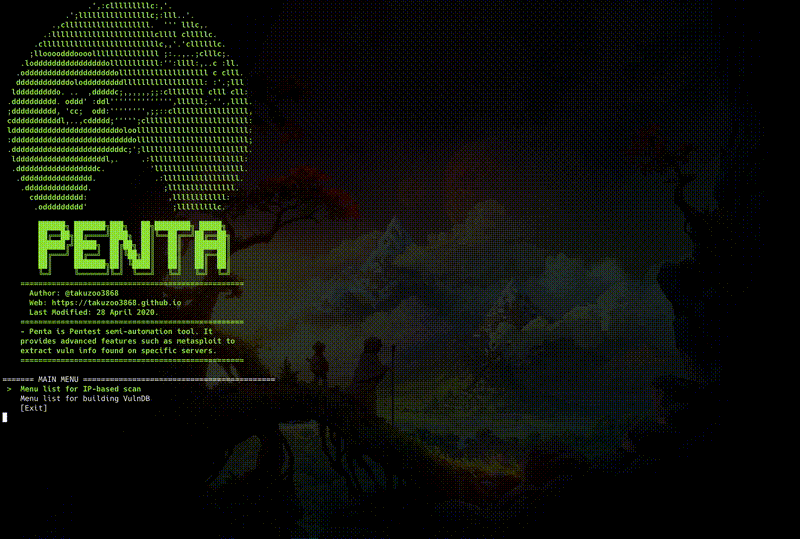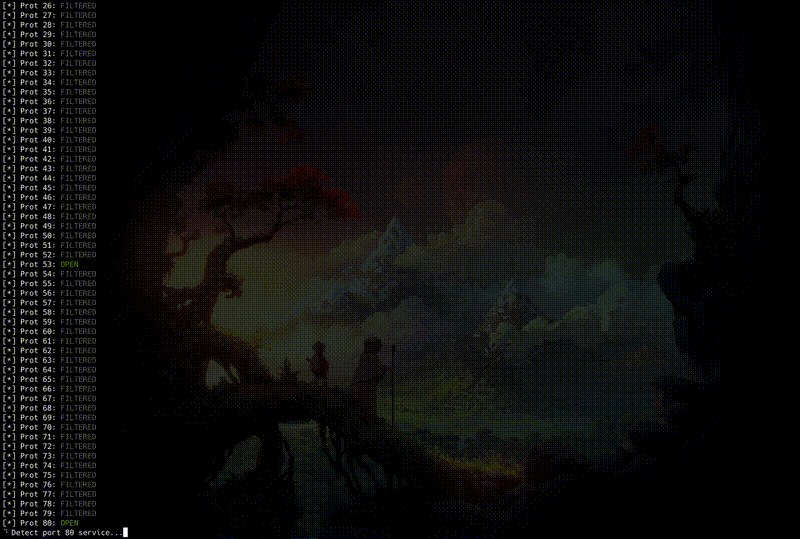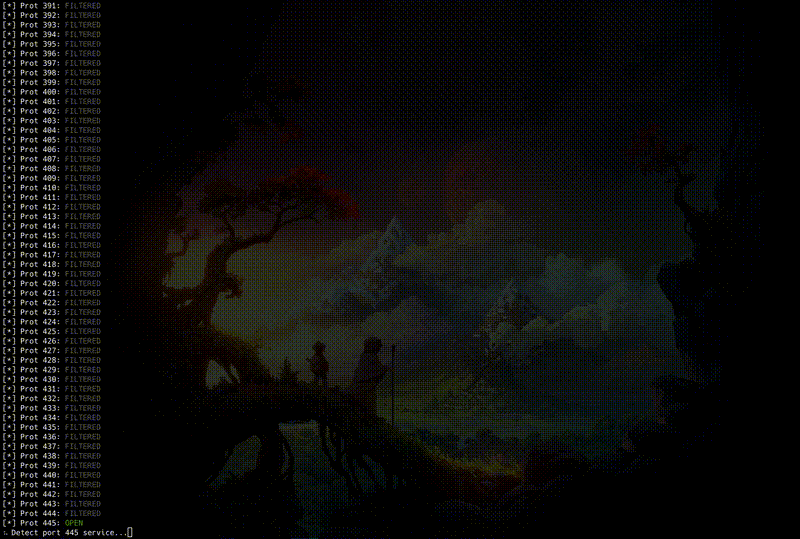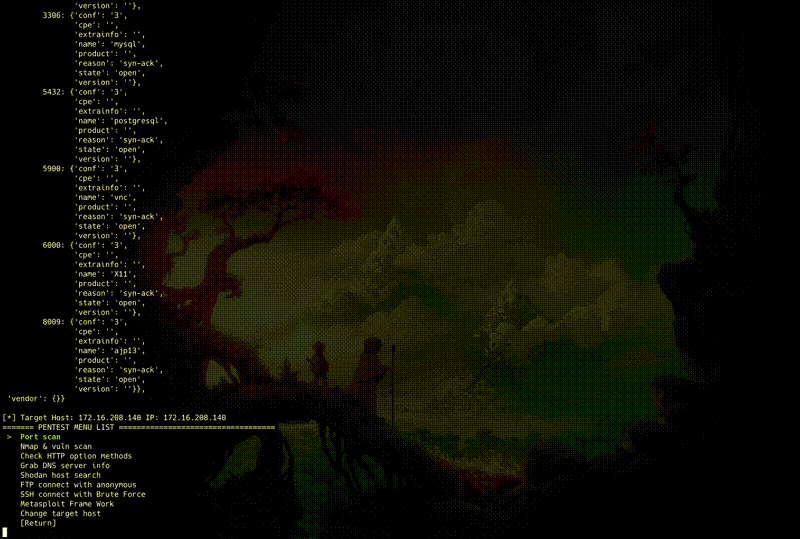 takuzoo3868/penta
Open source all-in-one CLI tool to semi-automate pentesting.

 pimps/ysoserial-modified
That repository contains my updates to the well know java deserialization exploitation tool ysoserial.
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 nvisosecurity/pycobalthound
pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.
 pownjs/pown
Pown.js is a security testing an exploitation toolkit built on top of Node.js and NPM.
 mogwaisec/mjet
Mogwai Java Management Extensions (JMX) Exploitation Toolkit
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
 octoberfest7/kdstab
BOF combination of KillDefender and Backstab
 zcgonvh/cve-2017-7269
fixed msf module for cve-2017-7269
 chaitanyaharitash/kimi
Script to generate malicious debian packages (debain trojans).
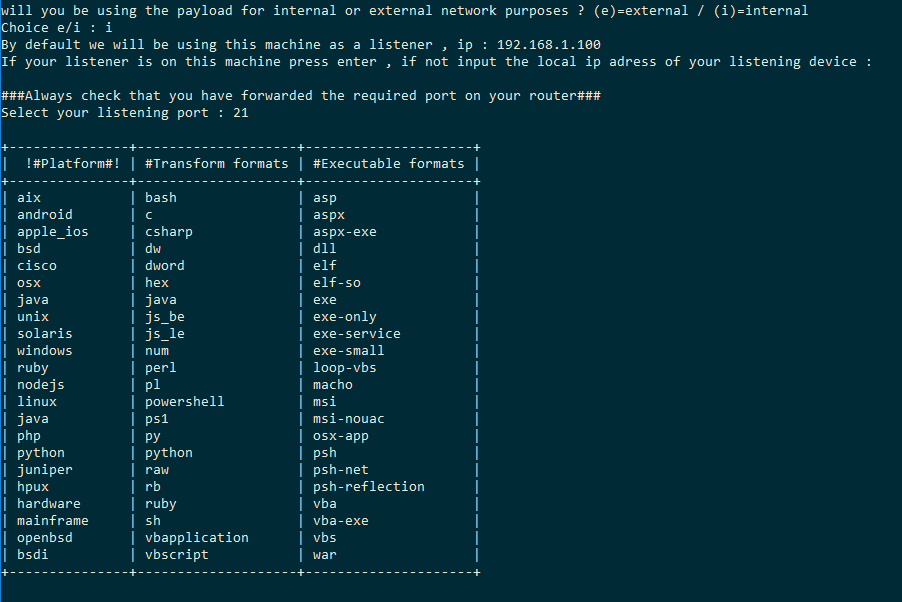 ceh-tn/the-axer
Automated payload generator wrapping msfvenom to streamline creation of platform-specific, encoded, and binded payloads for penetration testing…
 nestho/impacket-rs
High-performance, memory-safe pure-Rust redesign of Impacket protocols and Active Directory tools for Linux, macOS, and Windows.