
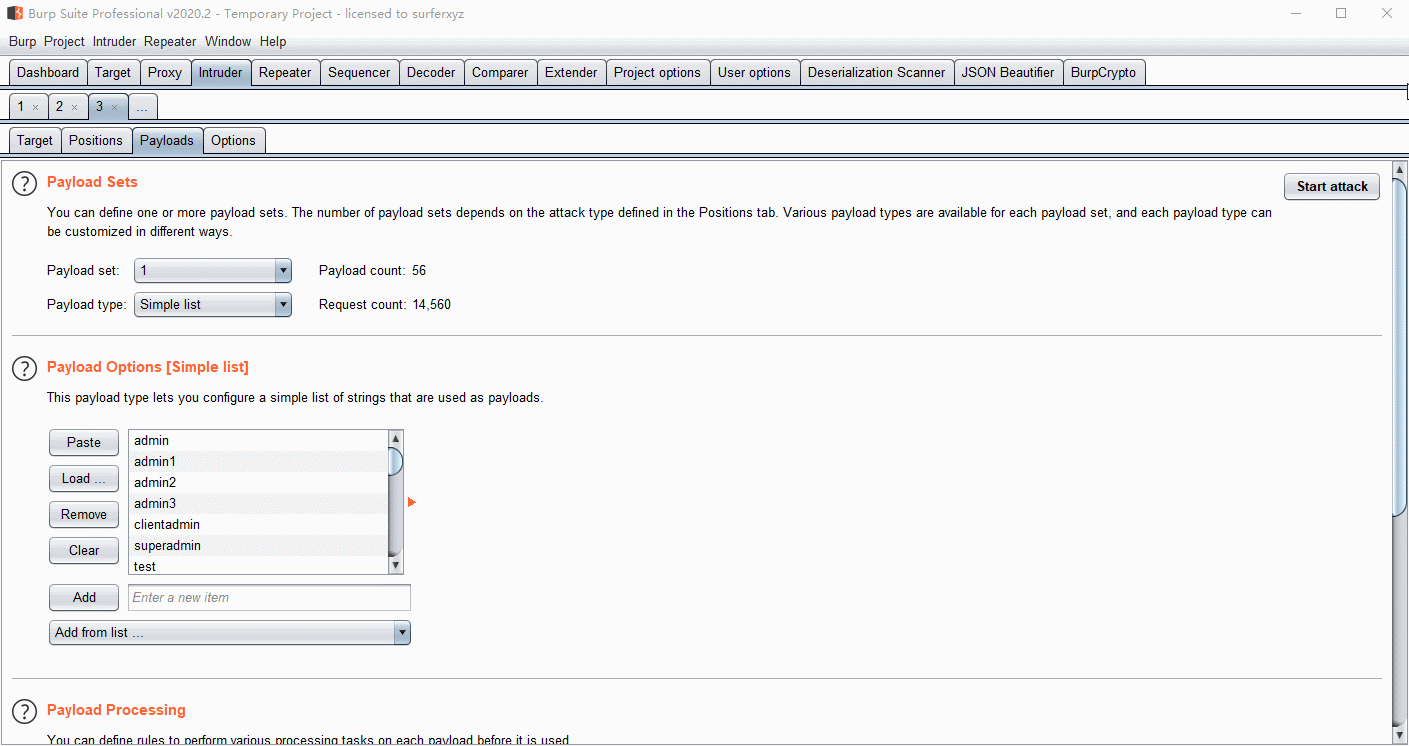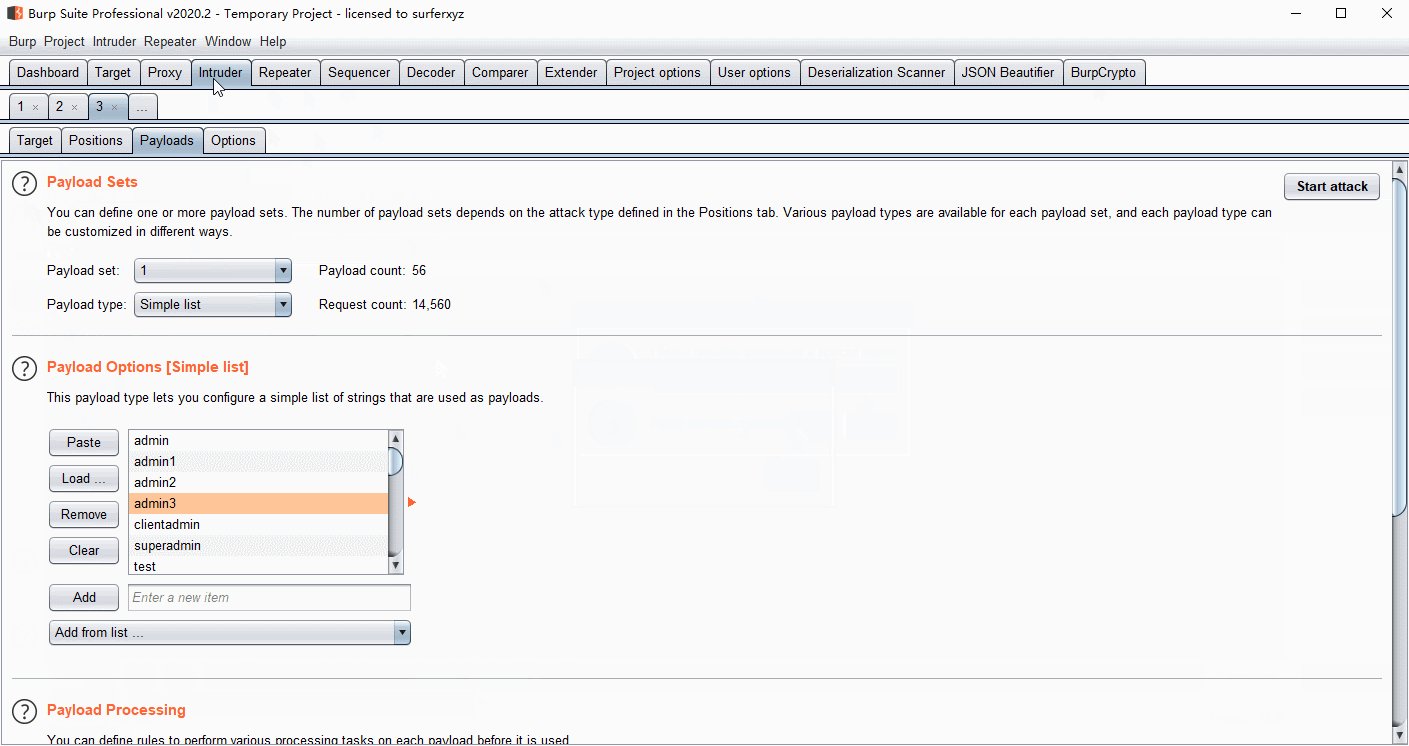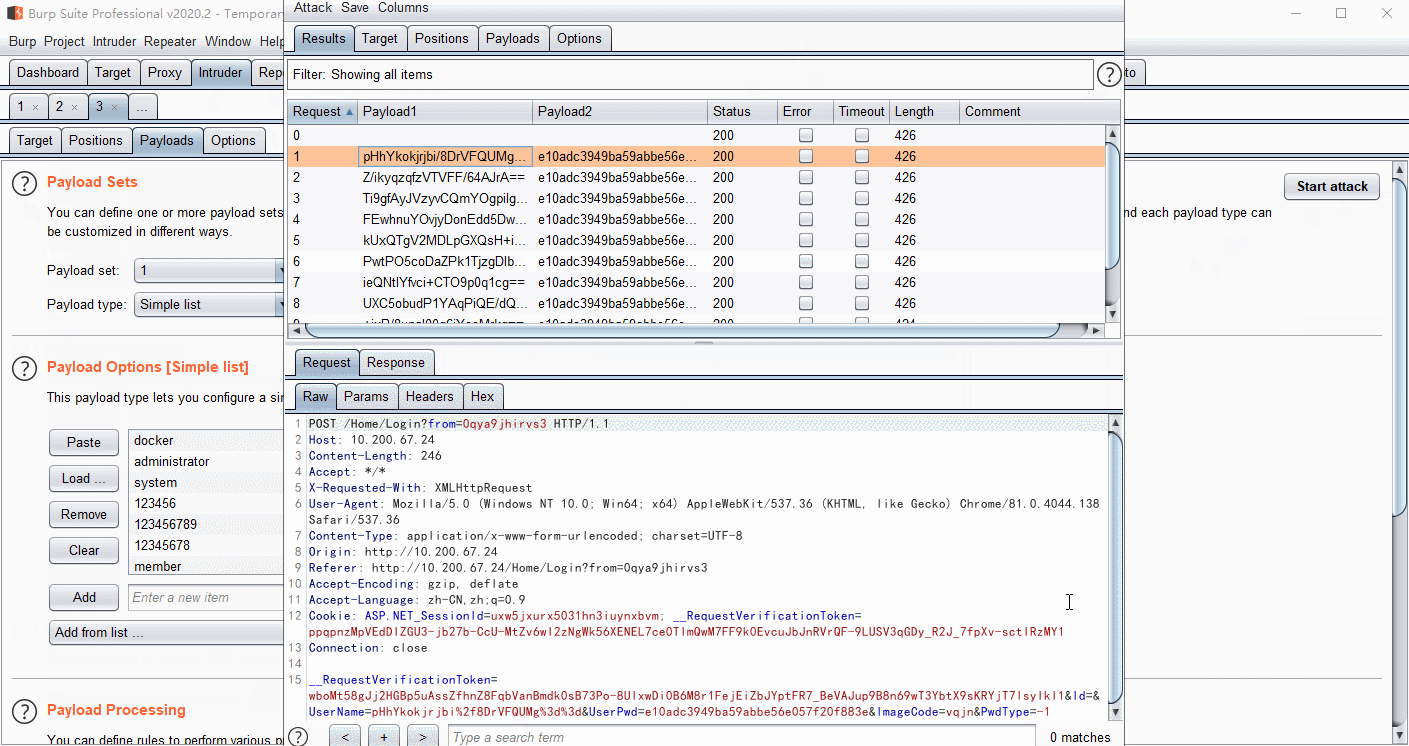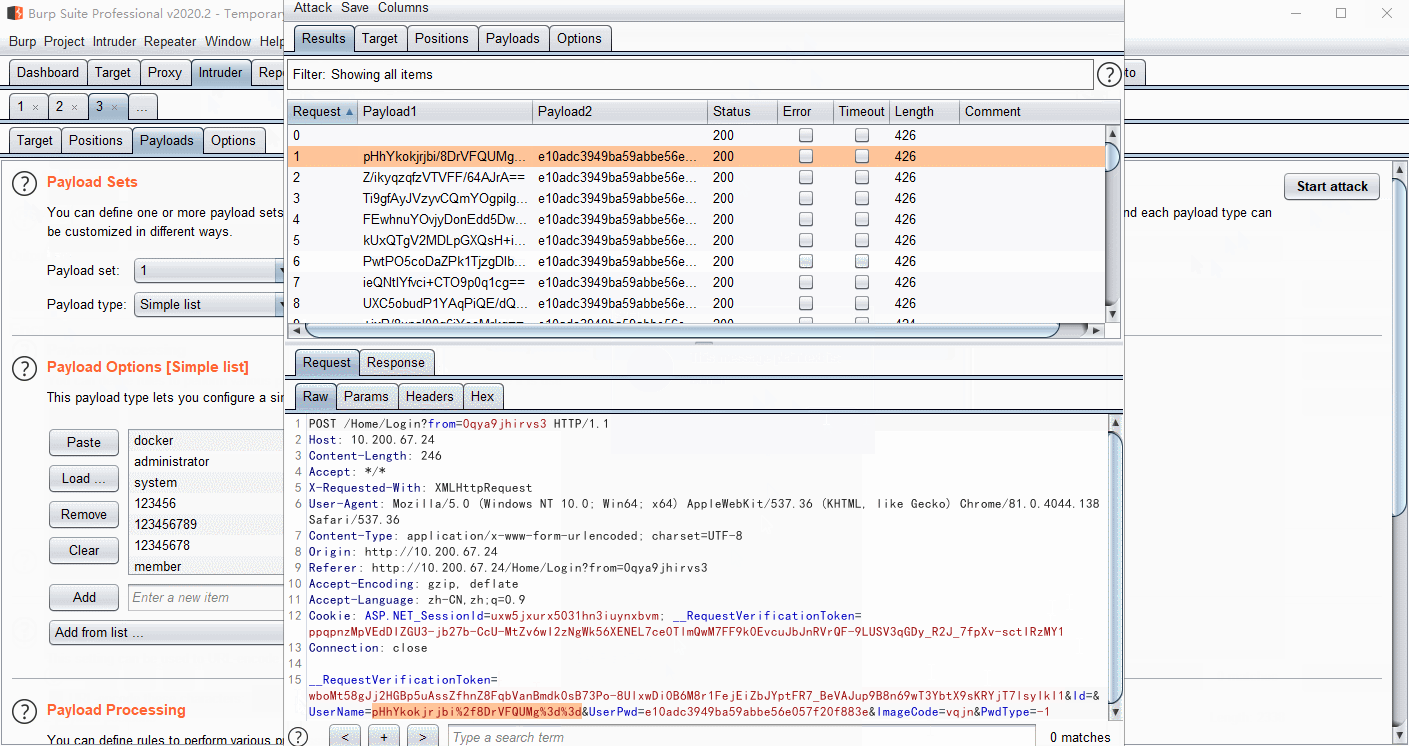
BurpCrypto
 whwlsfb/burpcrypto
BurpSuite plugin for encrypting payloads with AES, RSA, DES, or custom JS code, enabling automated decryption of front-end encrypted traffic during…
encryption-decryption-toolsfuzzingpayload-generation+1
1.7k
whwlsfb/burpcryptoBurpSuite plugin for encrypting payloads with AES, RSA, DES, or custom JS code, enabling automated decryption of front-end encrypted traffic during…
 yunemse48/403bypasser
Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
 adeyosemanputra/pygoat
intentionally vuln web Application Security in django
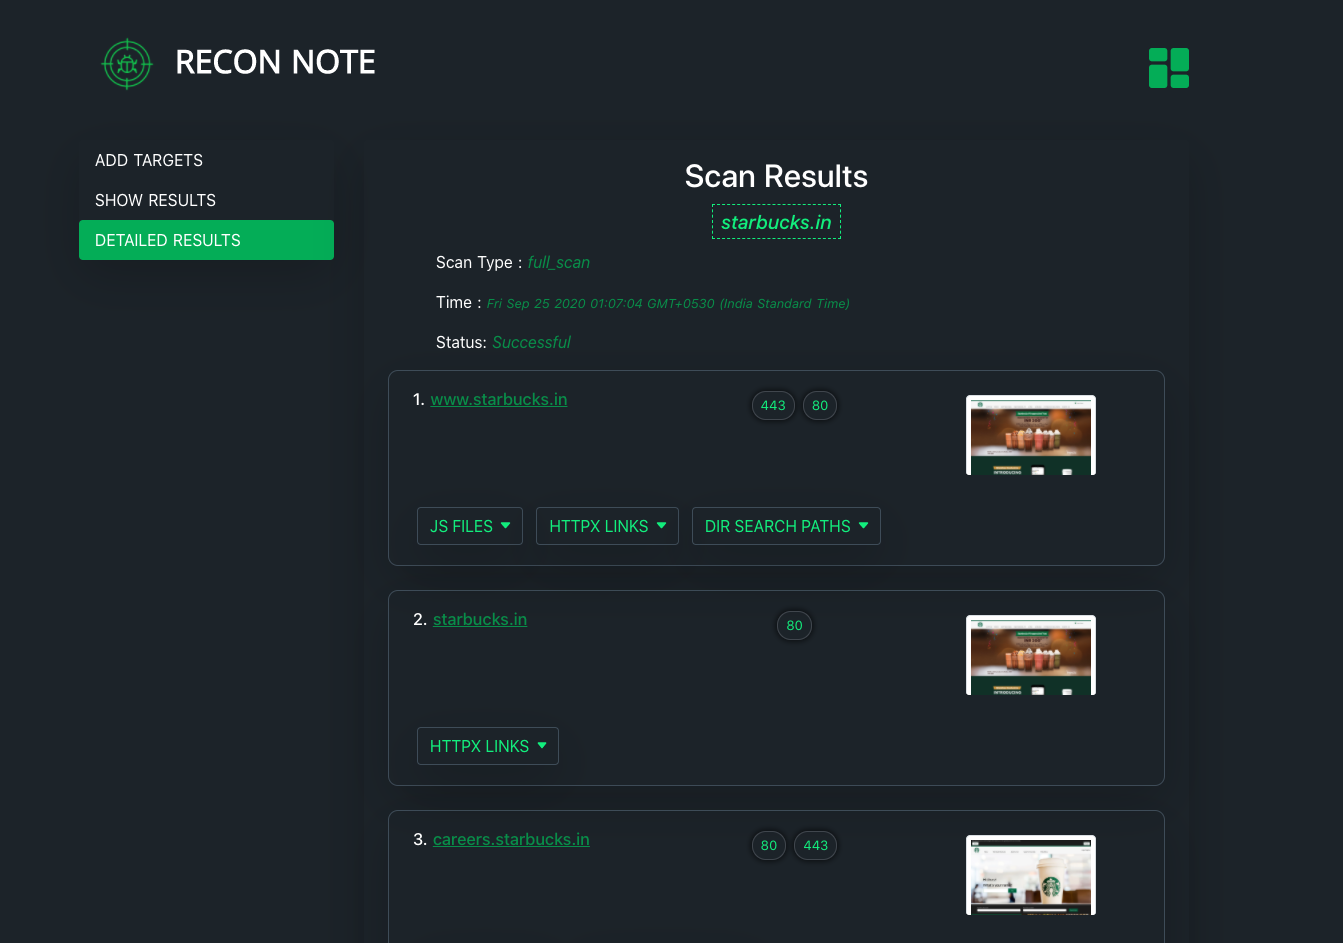 0xdekster/reconnote
Web Application Security Automation Framework which recons the target for various assets to maximize the attack surface for security professionals &…
 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts
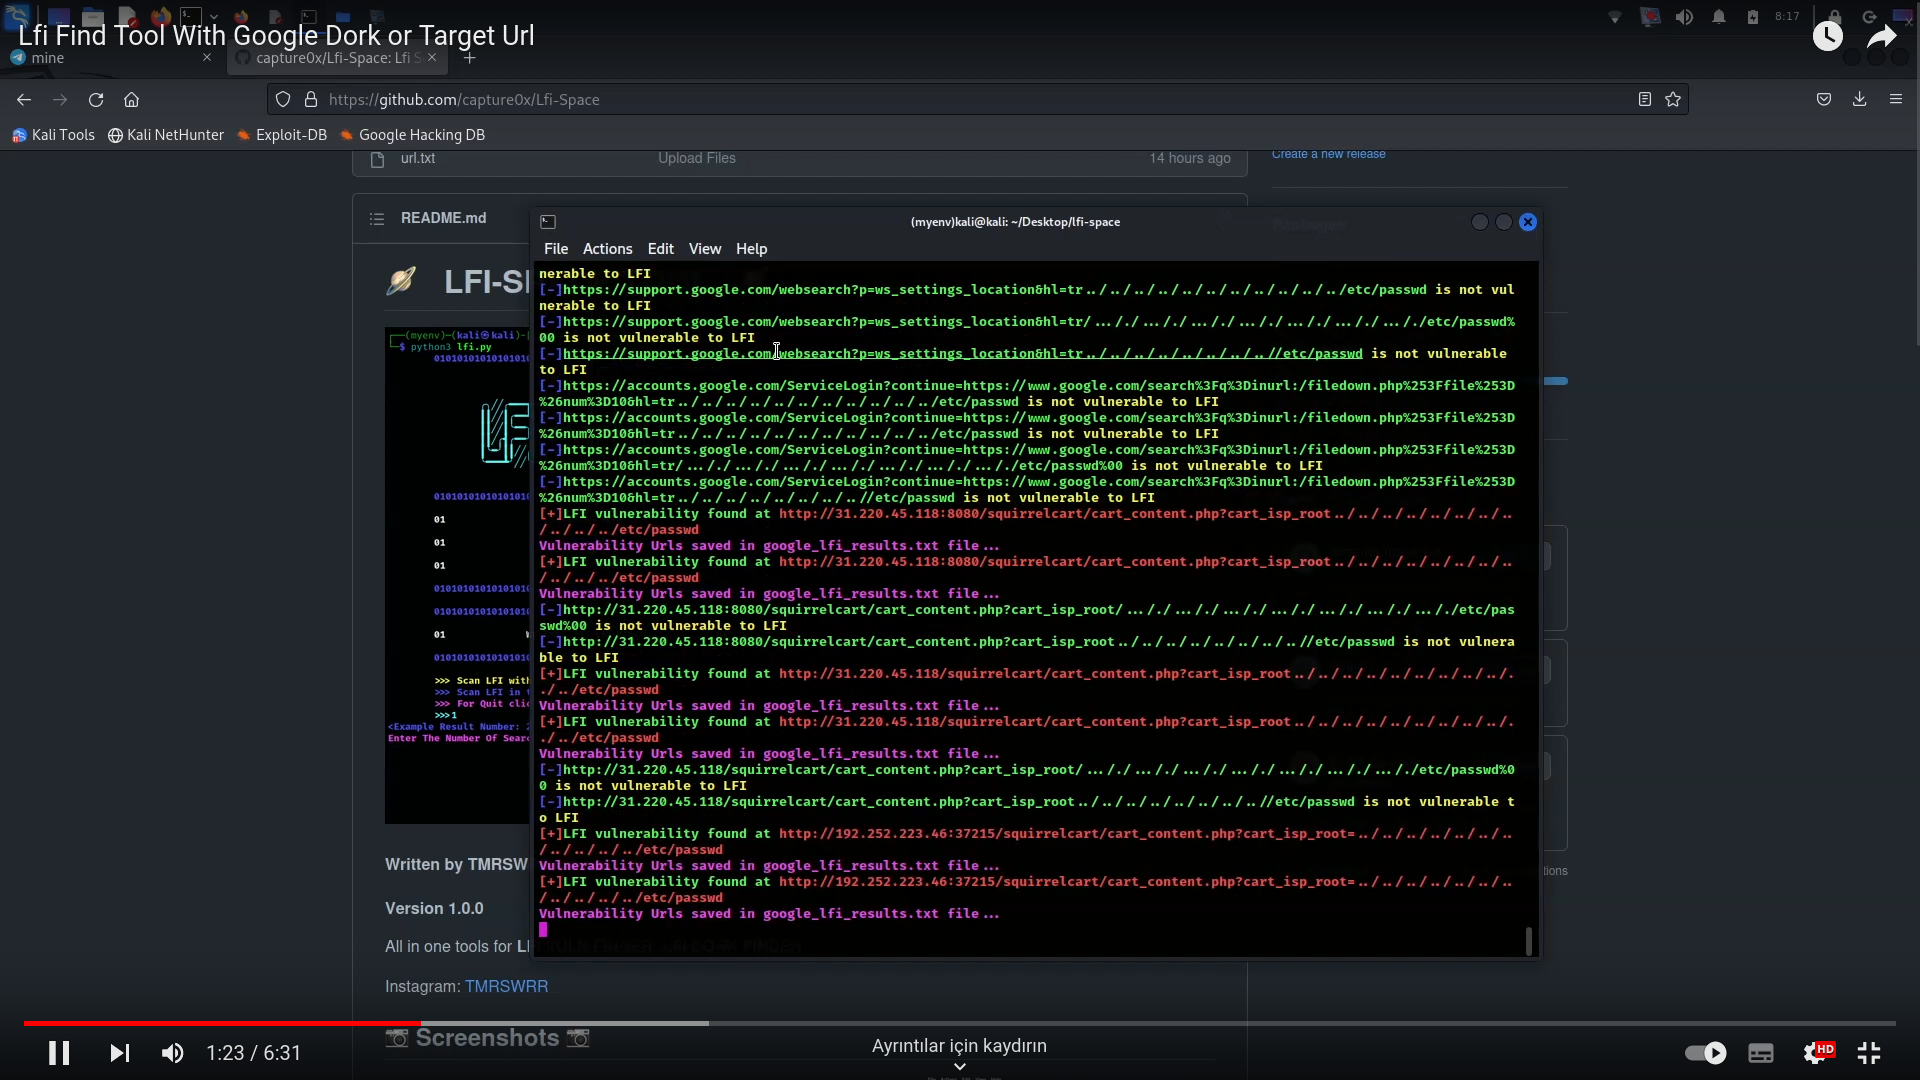 capture0x/lfi-space
Automated Local File Inclusion (LFI) vulnerability scanner with Google Dork search and targeted URL scan modes for web application security testing.
 owasp/owaspwebgoatphp
A deliberately vulnerable web application for learning web application security.
 bwasp/bwasp
BoB Web Application Security Project
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
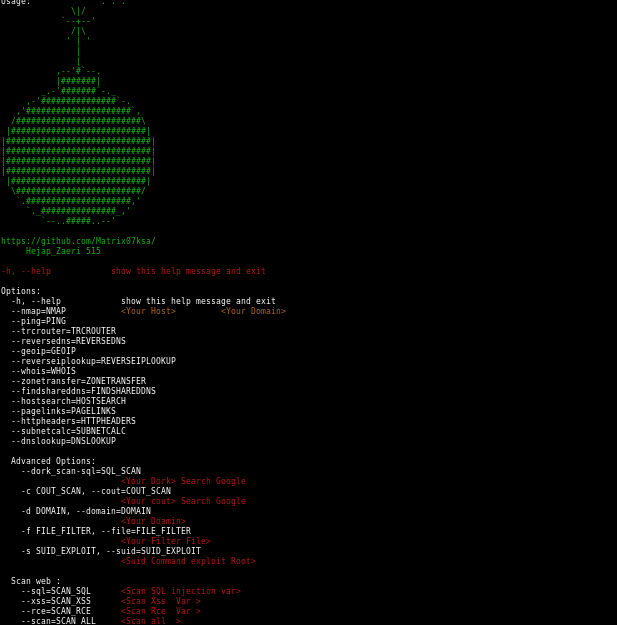 matrix07ksa/hackerinfo
Hackerinfo infromations Web Application Security
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 p0pr0ck5/lua-ffi-libinjection
LuaJIT FFI bindings for libinjection, providing SQL injection and XSS detection with context-specific APIs for web application security.
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
 nu11secur1ty/payload-lists
Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…
 alchemist3dot14/cve-2024-30270-poc
The script exploits Mailcow vulnerabilities via XSS and RCE, emphasizing the need for robust security measures and responsible usage to enhance web…
 mehedi-hasan-sami98/dvwa-zap-pentest
Web application security assessment of DVWA using OWASP ZAP — vulnerability scanning, RCE (CVE-2012-1823) analysis, and remediation report.