asf__cxf_CVE-2019-17573_3-2-11

Web services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, WS-Trust, and JAX-WS/JAX-RS APIs.

Web services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, WS-Trust, and JAX-WS/JAX-RS APIs.

Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.

Writeup/finding of CVE-2026-24061 within the Cyberhawks lab

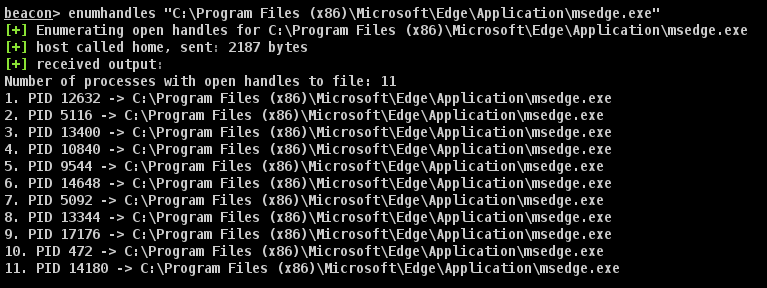
Cobalt Strike BOF for live Windows enumeration of open file handles, revealing which process has locked a target file on disk during…

AttackSurfaceMapper is a tool that aims to automate the reconnaissance process.

A tool to generate media files with malicious metadata

Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…

HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…

An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…

An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.

Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…

Automatic SQL injection and database takeover tool

Opensource IDE For Exploring and Testing API's (lightweight alternative to Postman/Insomnia)

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

Lightweight service virtualization/ API simulation / API mocking tool for developers and testers

Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a proof capsule you can replay yourself.

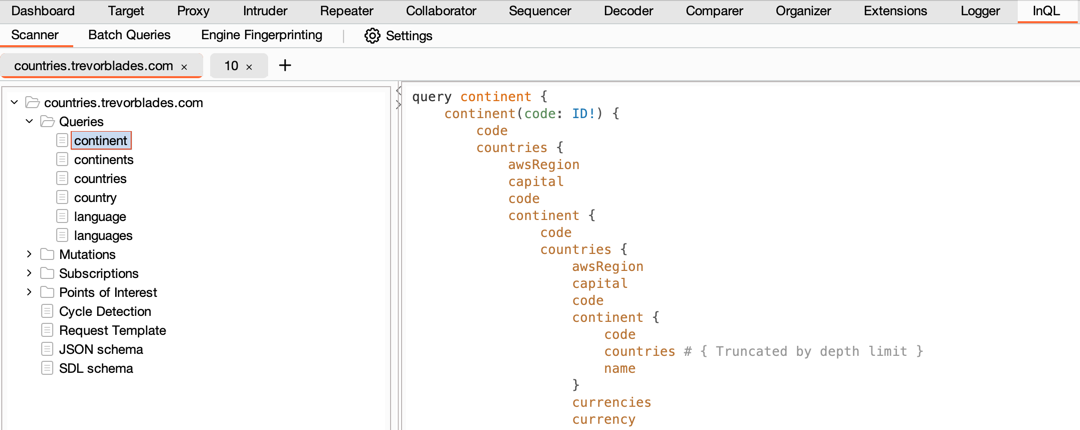
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…

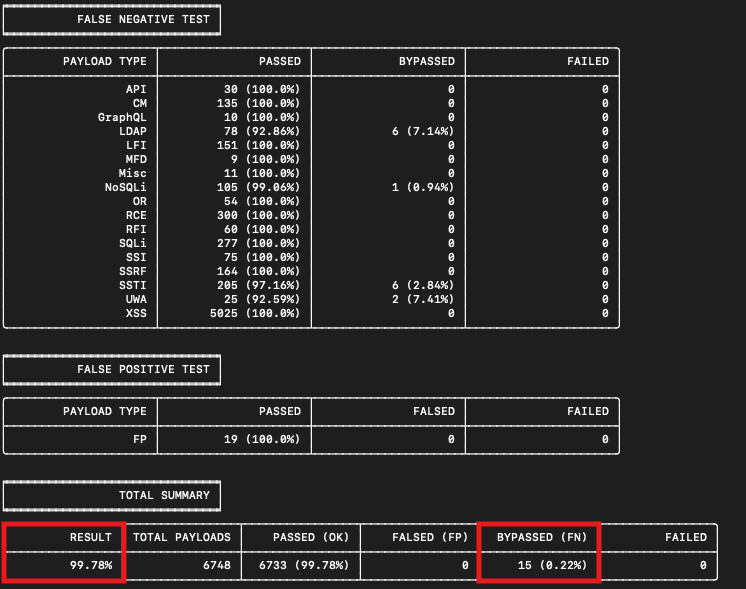
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…