
Bypass_AV
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
ids-ips-evasionpayload-developmentpayload-generation+2
108
hkl1x/bypass_avEvades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 didierstevens/falsepositives
Tools that trigger False Positive AV alerts
 dsnezhkov/elfpack
ELF binary section docking toolkit for stageless payload delivery, enabling in-field payload attachment, signature evasion, and static/dynamic…
 kira2040k/avbypass
golang script for bypass AV and work only in windows platform
 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 gmh5225/cs-memoryevasion
A Cobalt Strike memory evasion loader for redteamers
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
 leviathanfromdeepsea/iberyanbytes
PowerShell-based Active Directory enumeration tool for gathering network configuration, domain objects, user sessions, share permissions, and…
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 secretsquirrel/recomposer
Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.
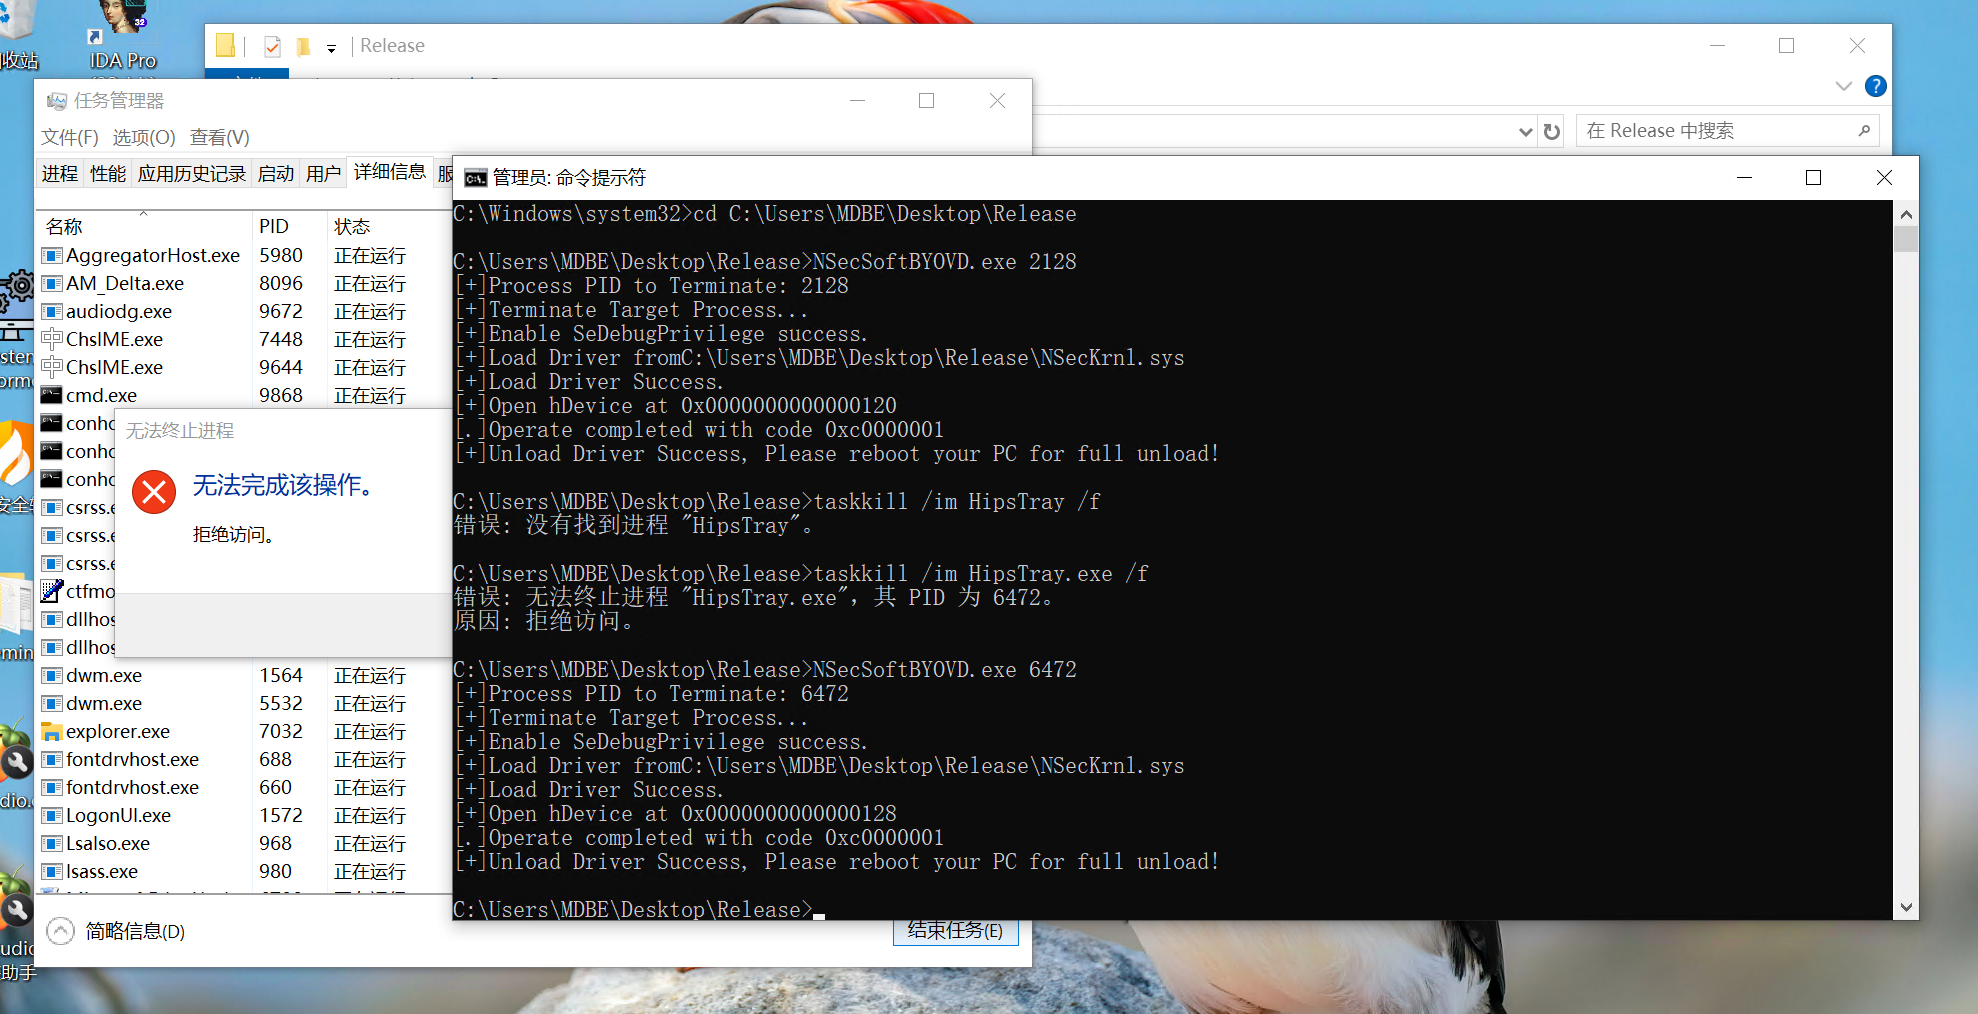
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
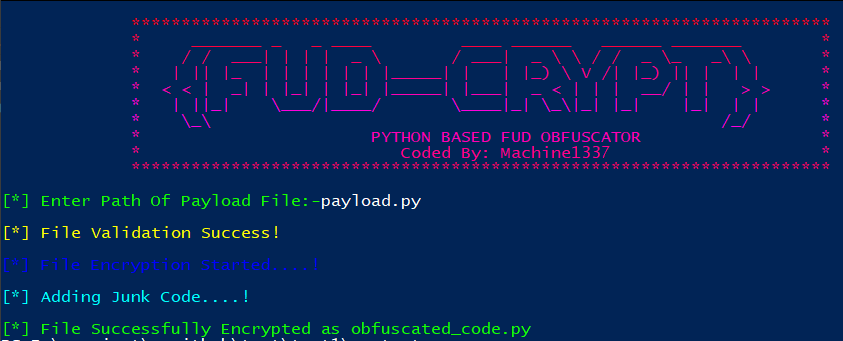 machine1337/fudcrypt
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.
 tennc/webshell
This is a webshell open source project
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors