

ios_triage
 realitynet/ios_triage
Bash script to extract data from a "chekcra1ned" iOS device
digital-forensicsforensicsios-security+1
realitynet/ios_triageBash script to extract data from a "chekcra1ned" iOS device
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 rlarabee/exploits
C-language exploit code collection focused on vulnerability research, proof-of-concept development, and offensive security testing.
 cbuijs/sdproxy
DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 sridhar-sec/evildroid
EvilDroid automates the exploitation of CVE-2024-0044, installing malicious payloads on a target device and extracting sensitive data. It features…
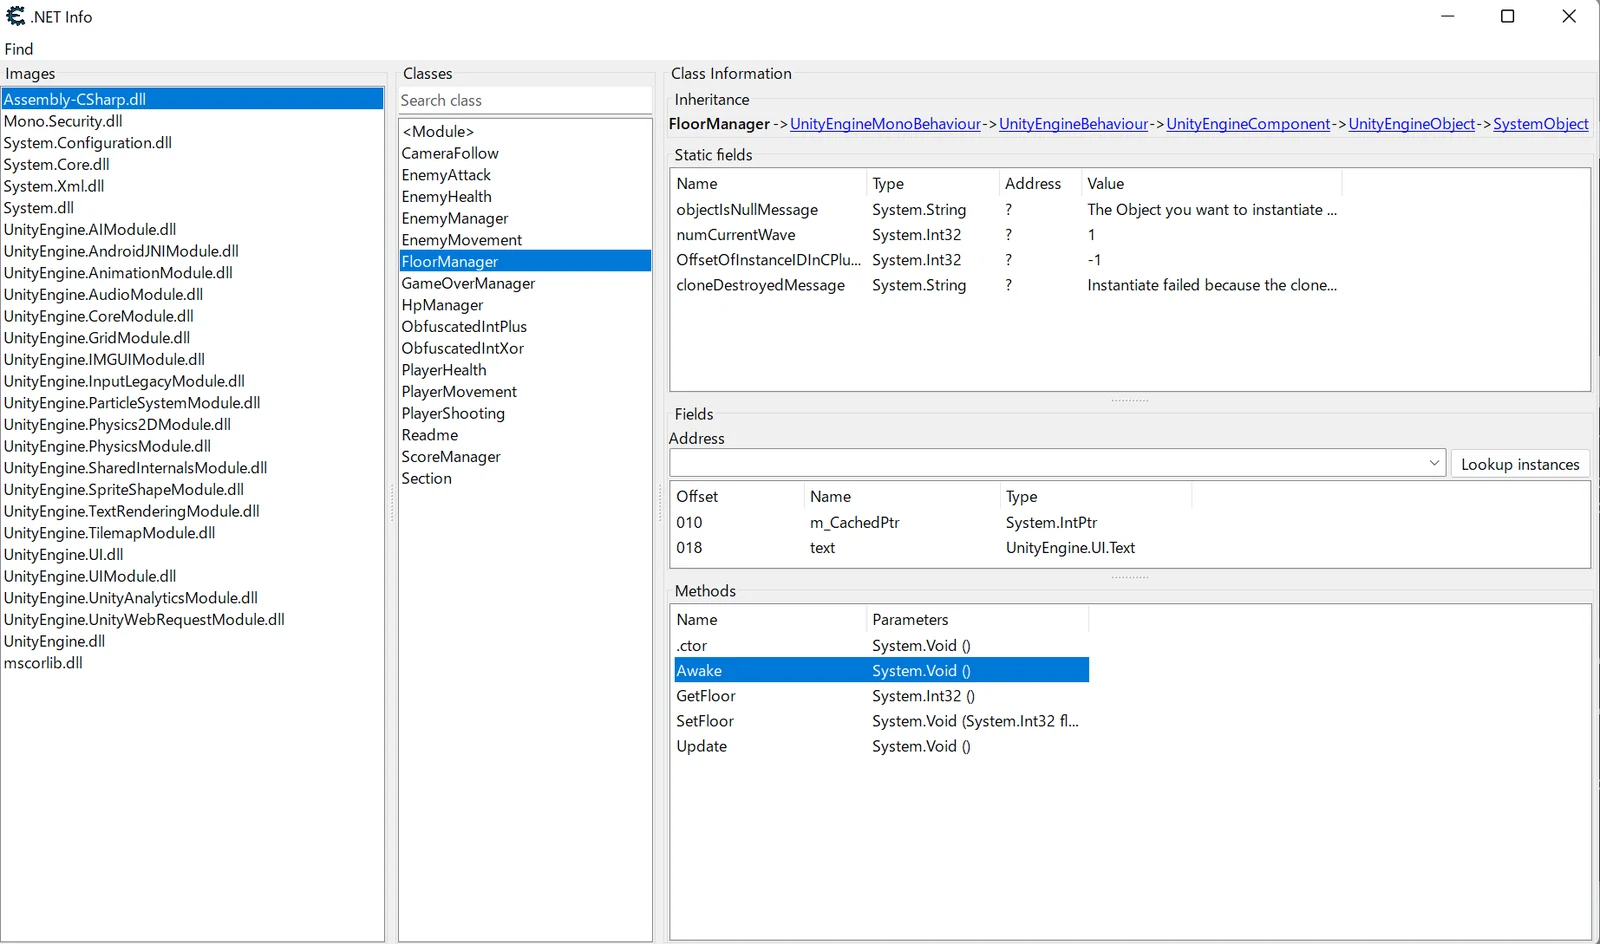 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 thomascannon/android-cve-2010-4804
Android Data Stealing Vulnerability
 crussella0129/tricorne
a Fedora remix focused on pentesting and purple hat tooling
 vnescape/zygote-cve-2024-31317
This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.
 feliam/cve-2014-4481
Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 0x43434343/cve-2019-0539
Focused exploit for CVE-2019-0539, a ChakraCore type confusion vulnerability, demonstrating arbitrary read/write access in the JavaScript engine.
 alixploit22/cve-2026-53587
Python proof-of-concept for CVE-2026-53587, providing a focused exploit path to reproduce the vulnerability and support validation and defensive…
 honestcorrupt/phonepe-sensitive-data-exposure-cve-2025-5154
CVE-2025-5154: Proof-of-concept for unencrypted local storage of authentication tokens, PII, and KYC data in the PhonePe Android app, enabling…