

vmp-lazy-unpack
 x86rc/vmp-lazy-unpack
Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…
binary-analysisbinary-exploitationdynamic-analysis-sandboxing+4
400
x86rc/vmp-lazy-unpackEmulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…
 capt-meelo/lazzzy
Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…
 tvdstaaij/telegram-history-dump
Backup Telegram chat logs with incremental support, multiple output formats (JSON, HTML, plaintext), and media download via telegram-cli remote…
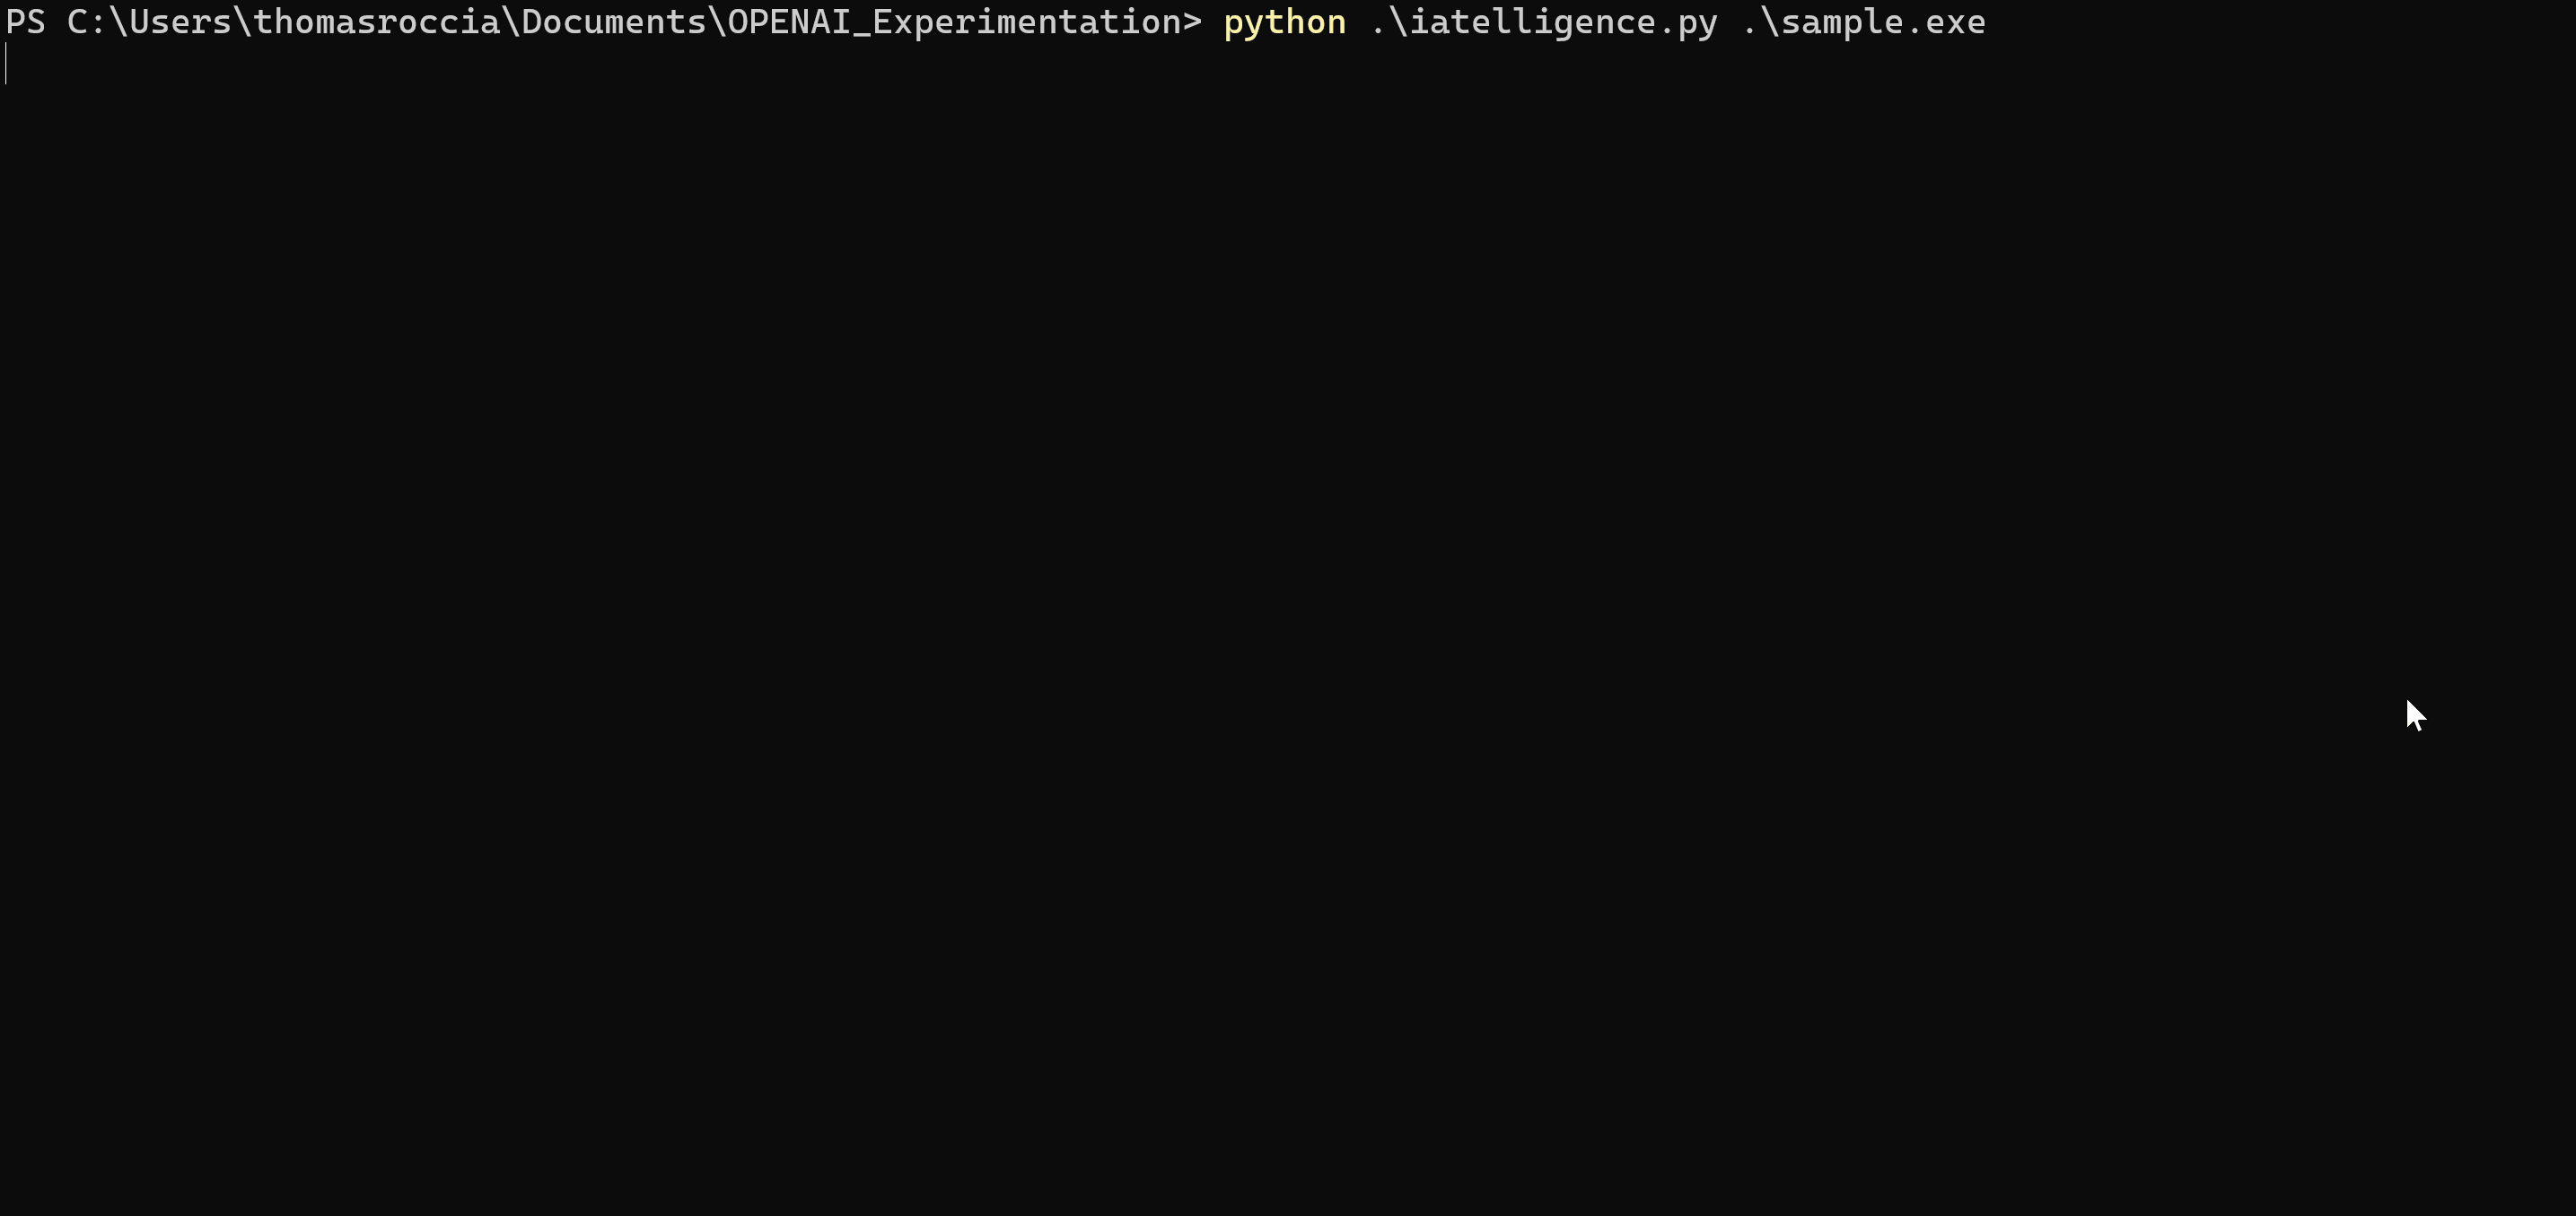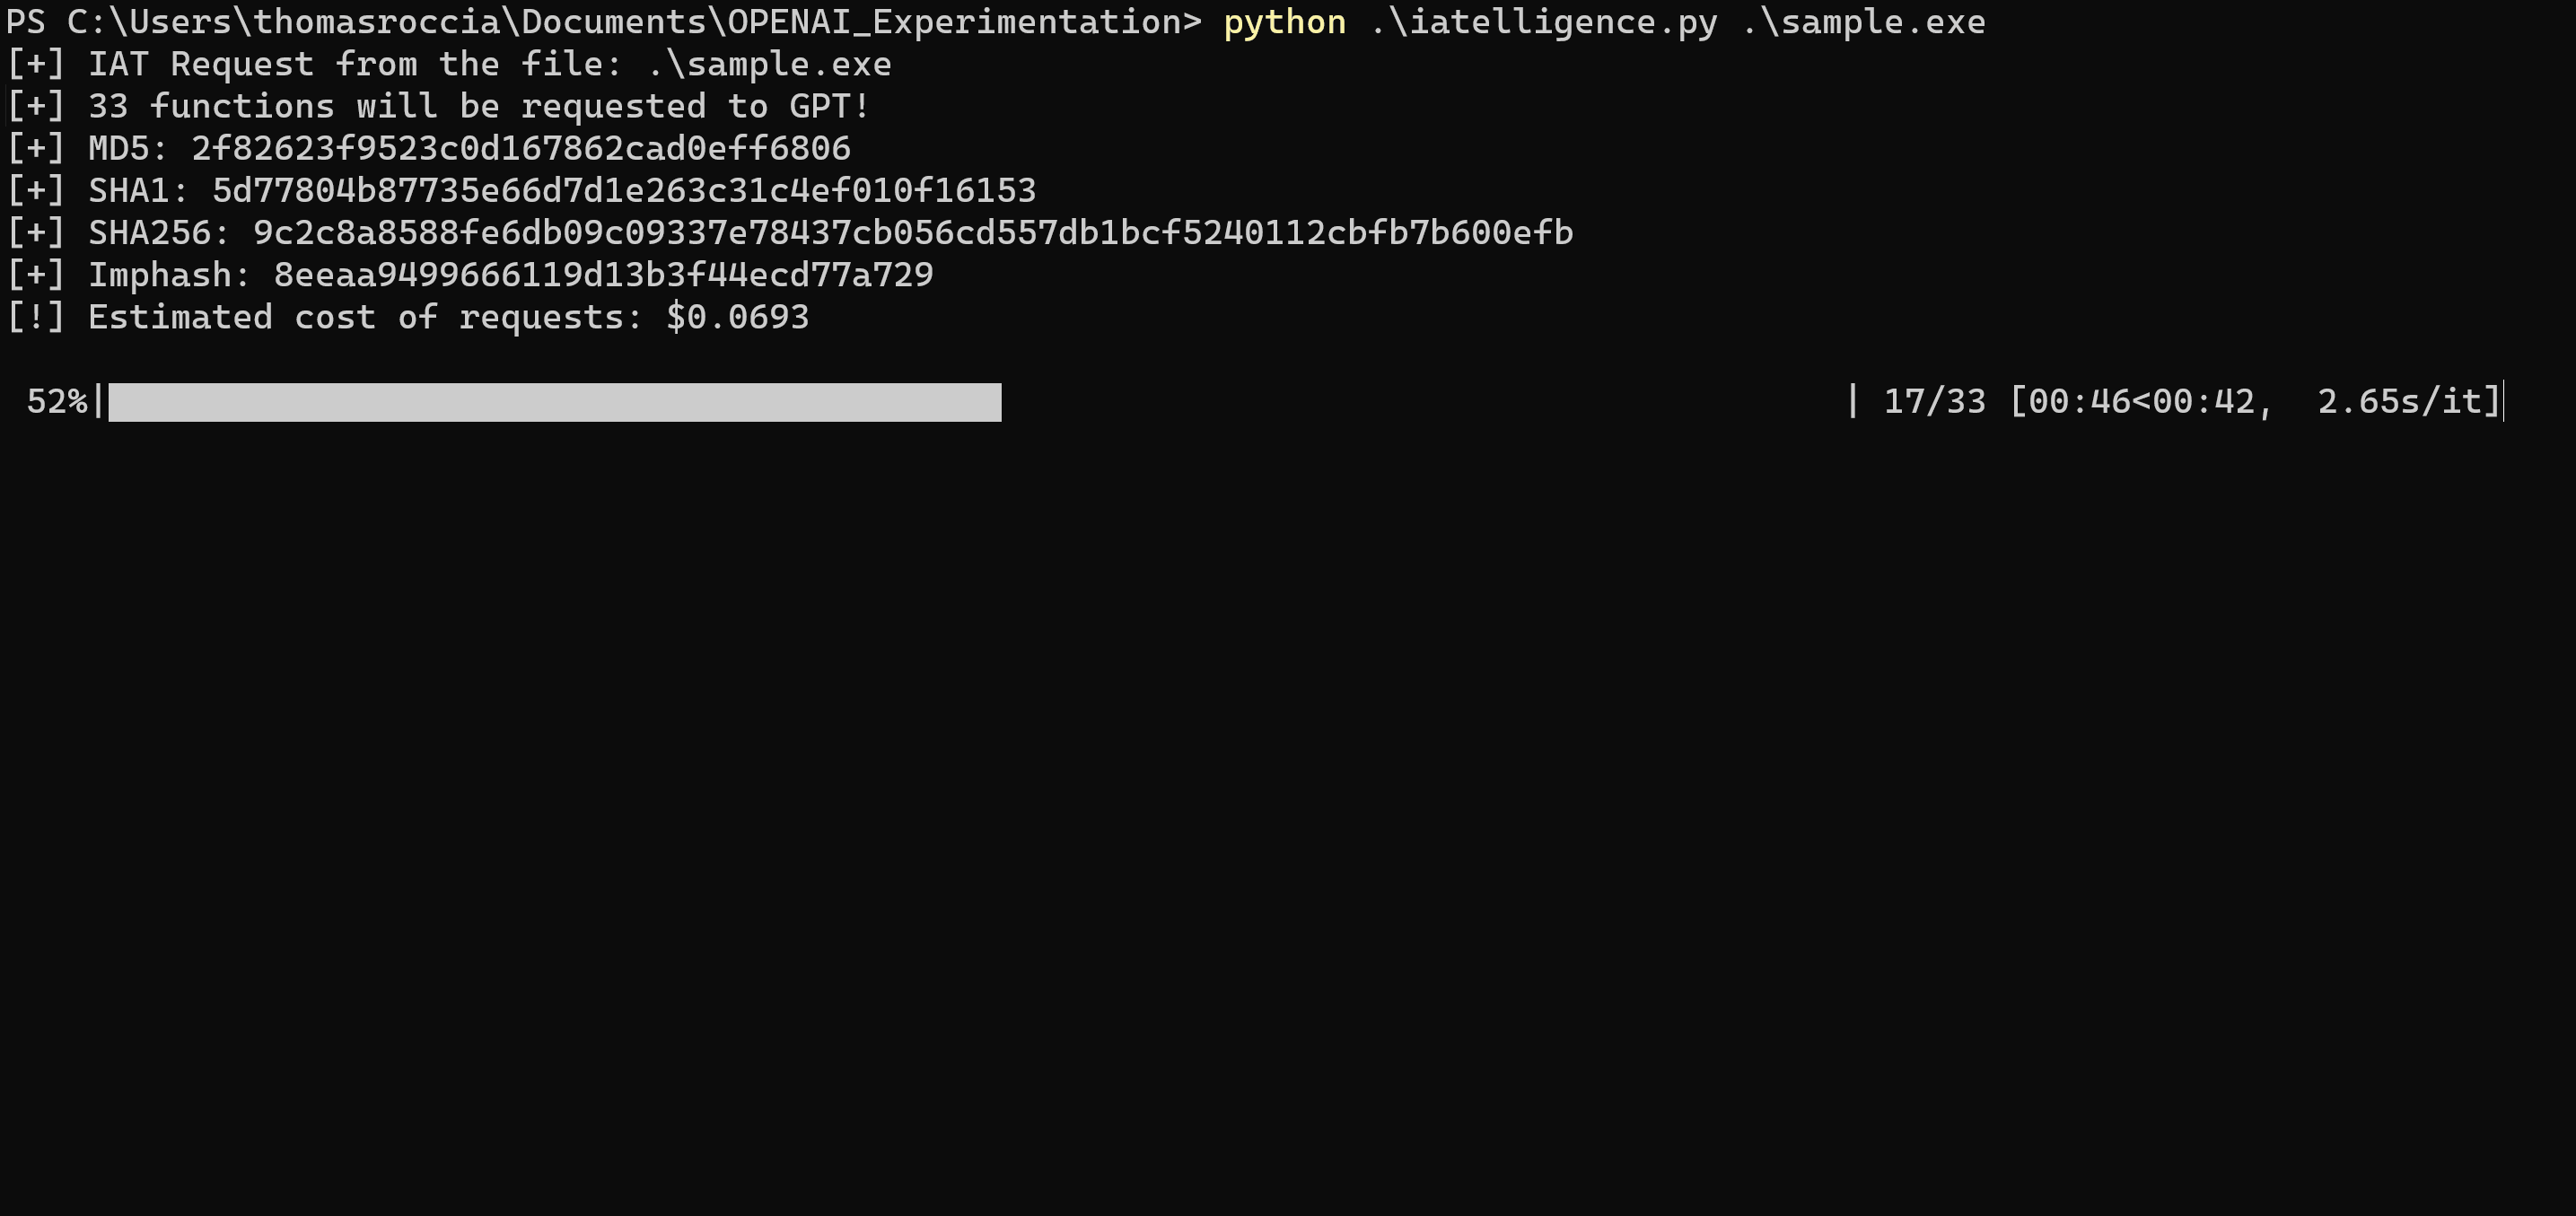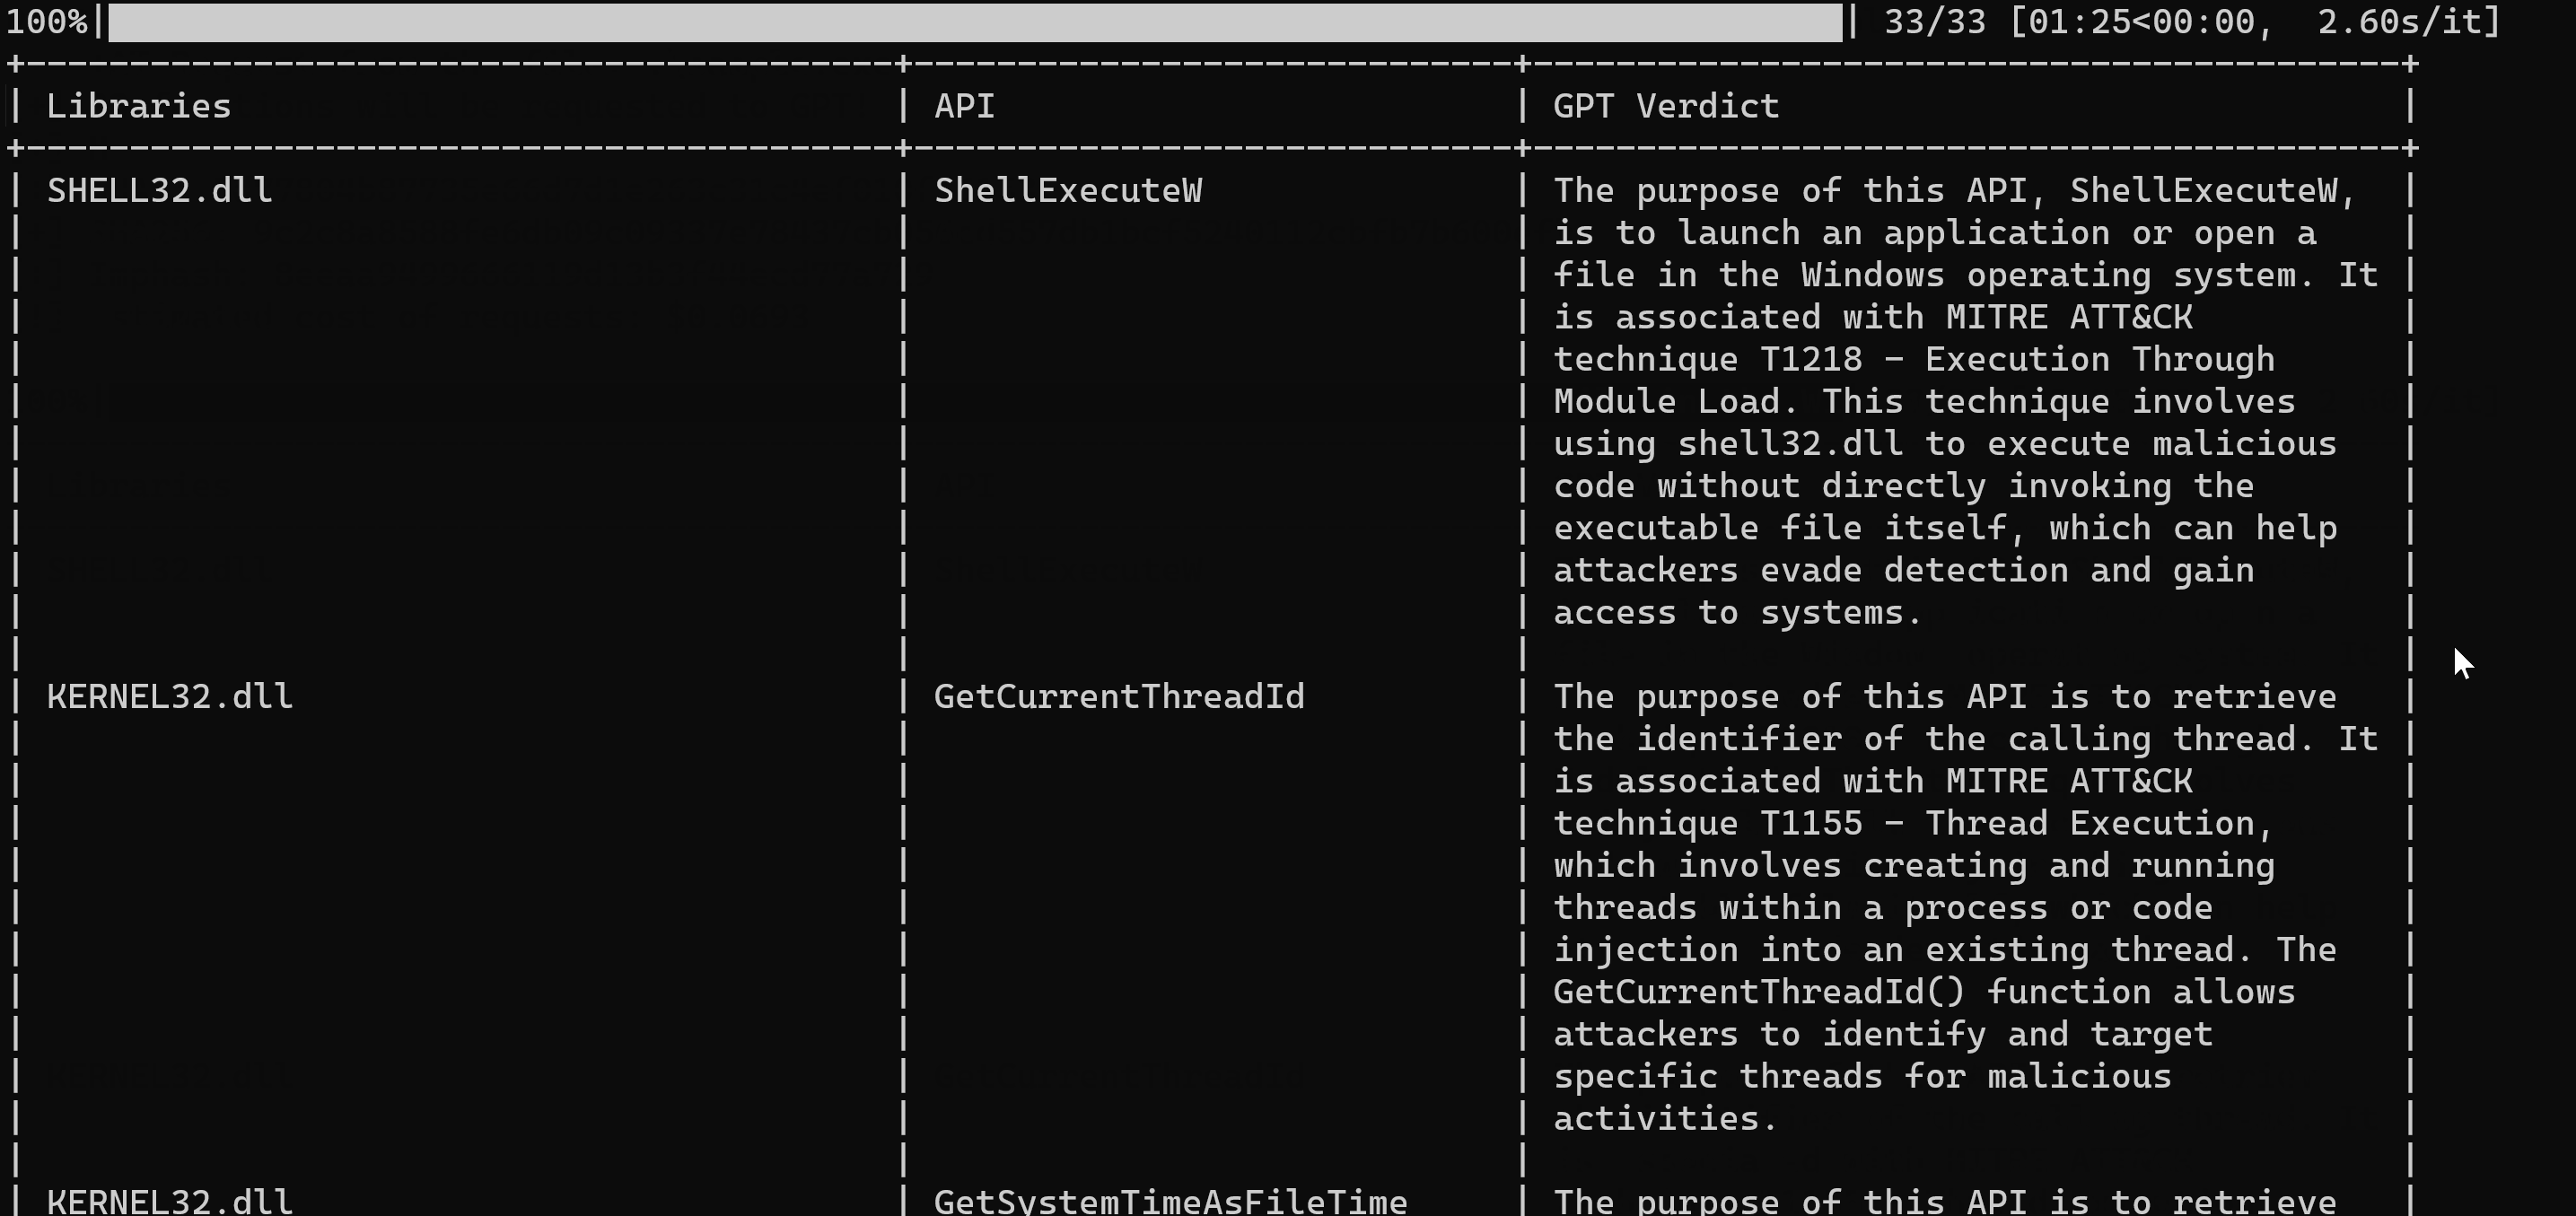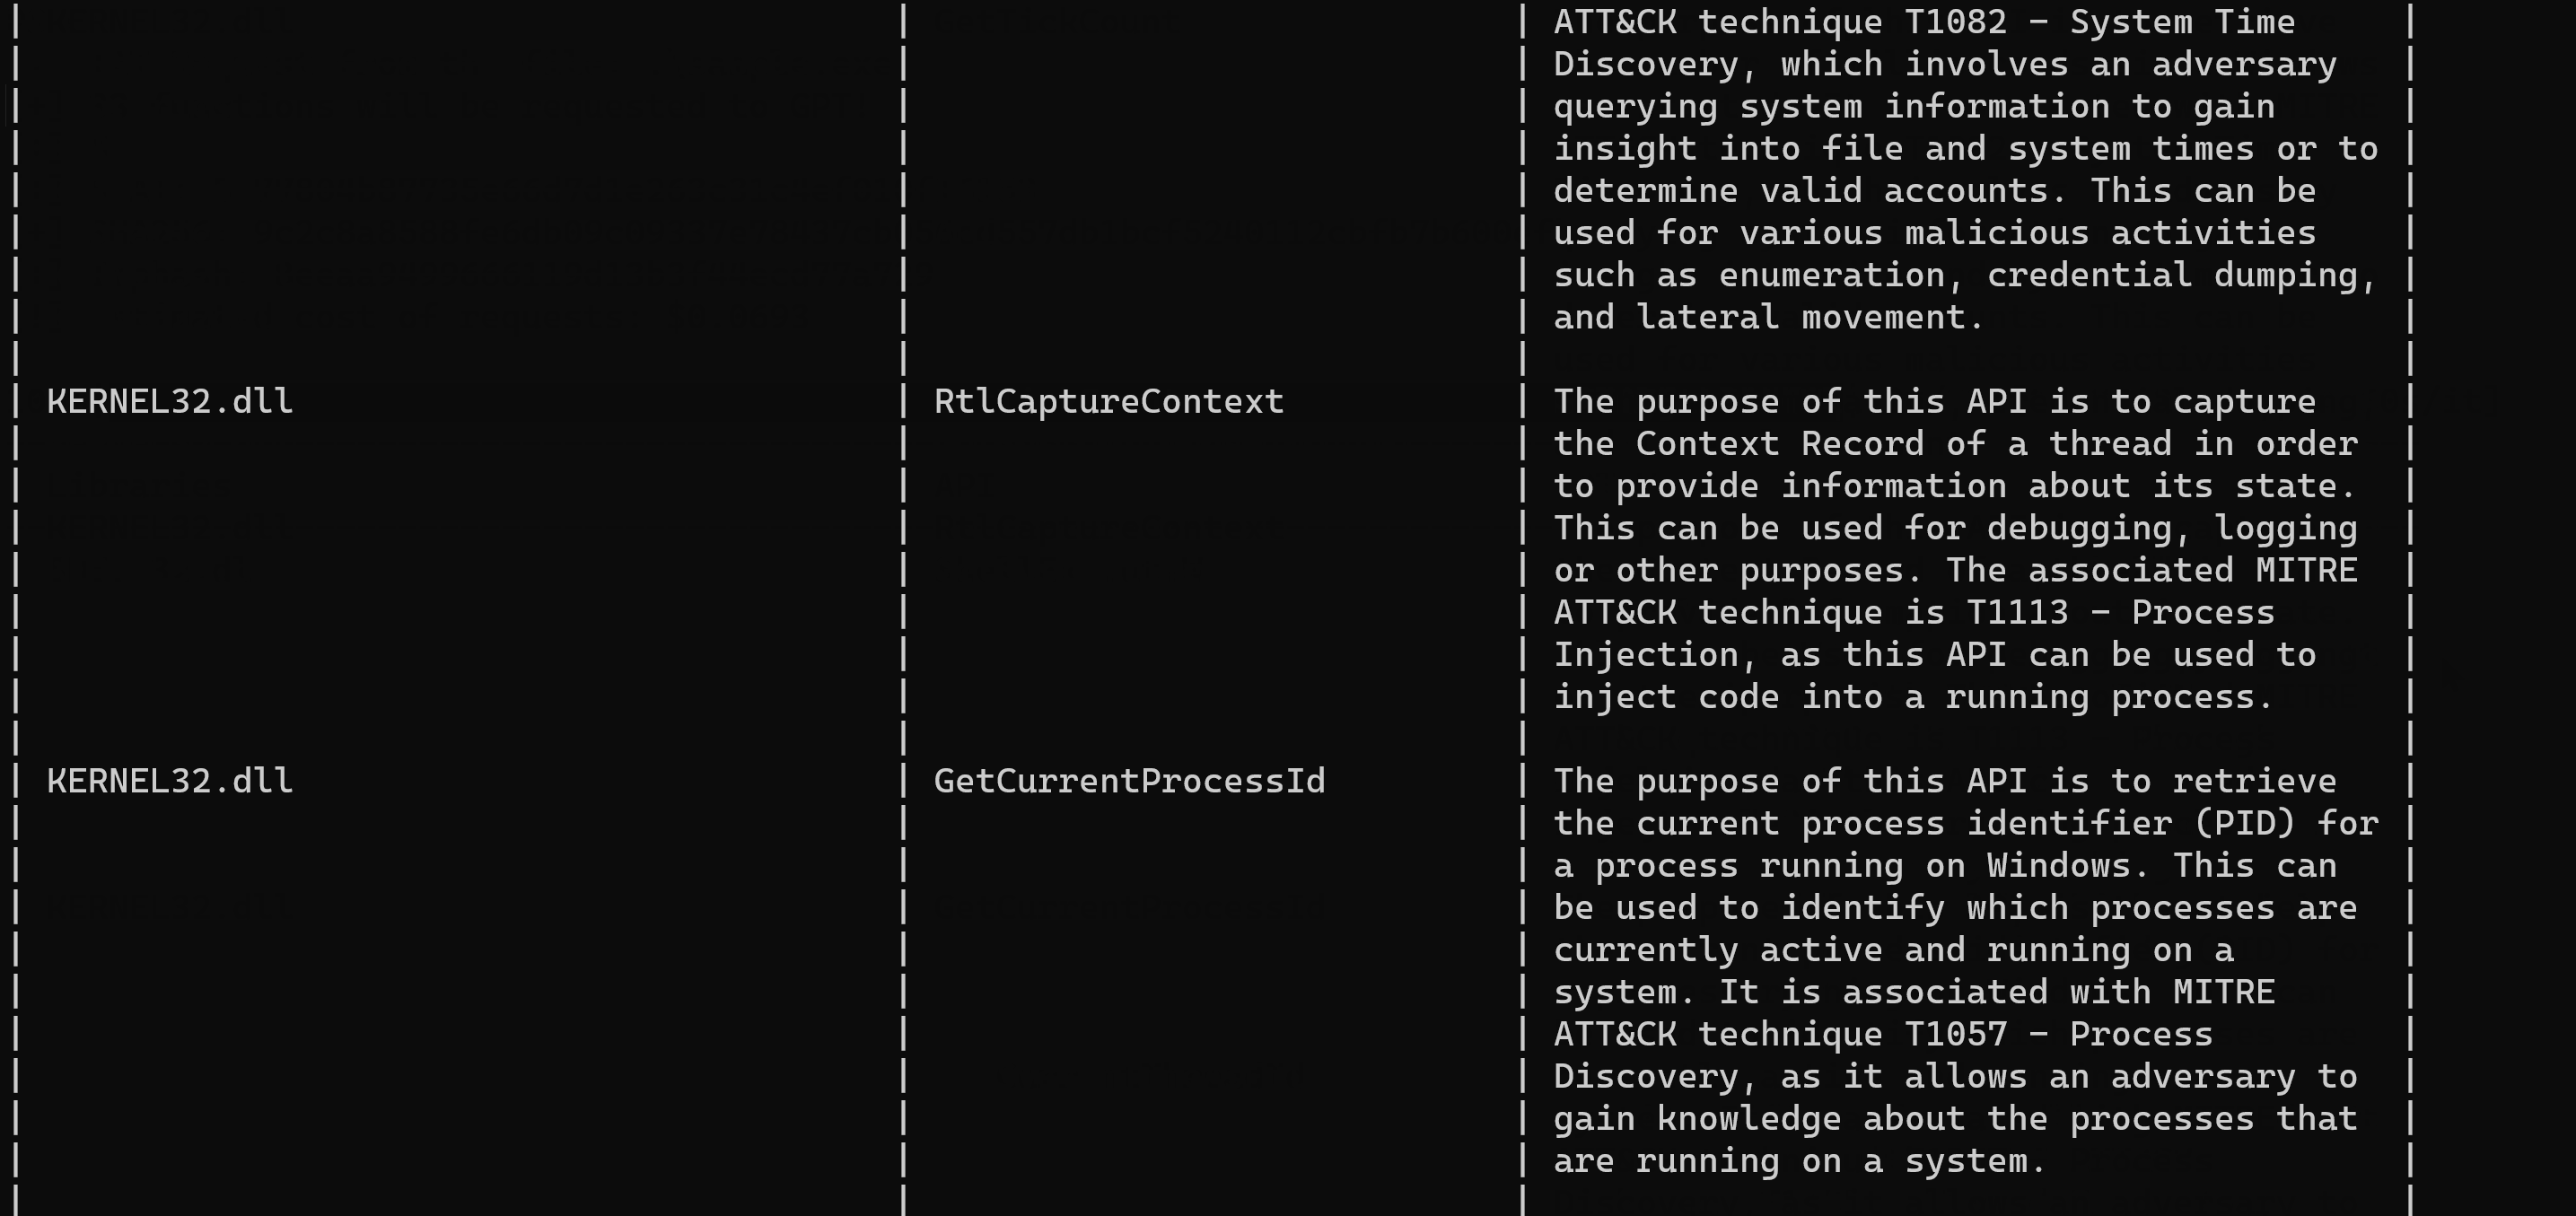 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
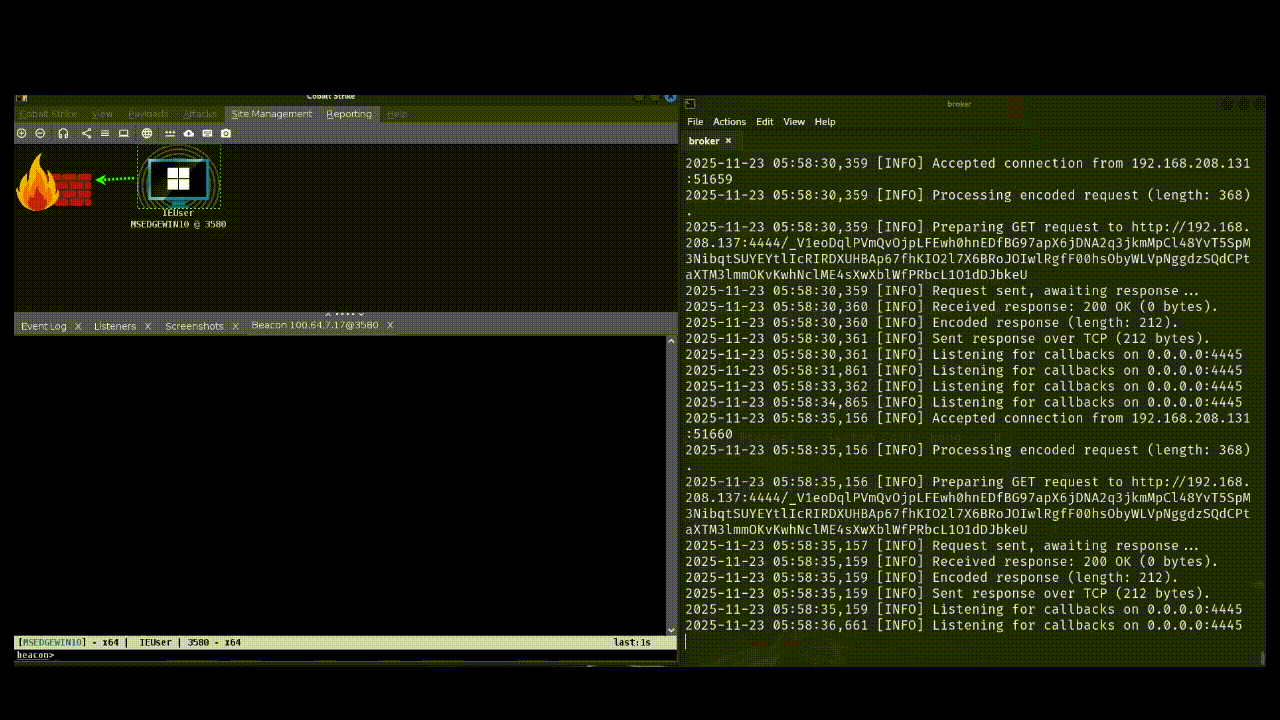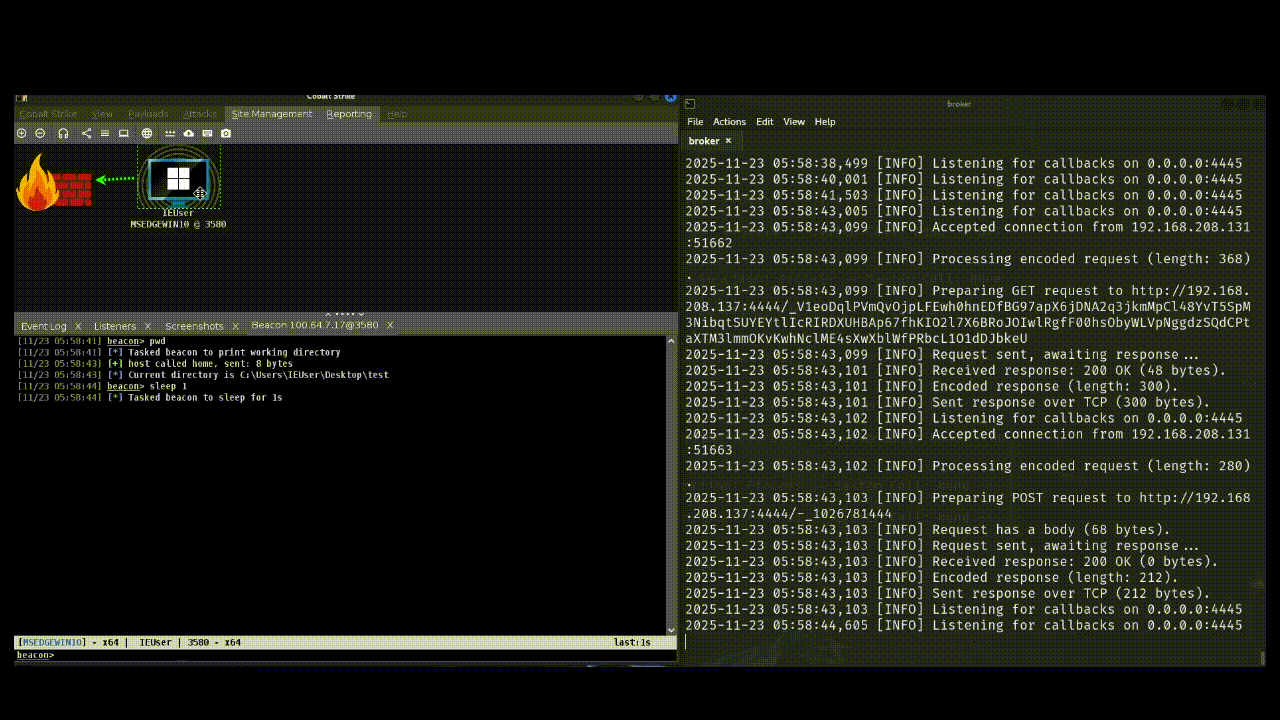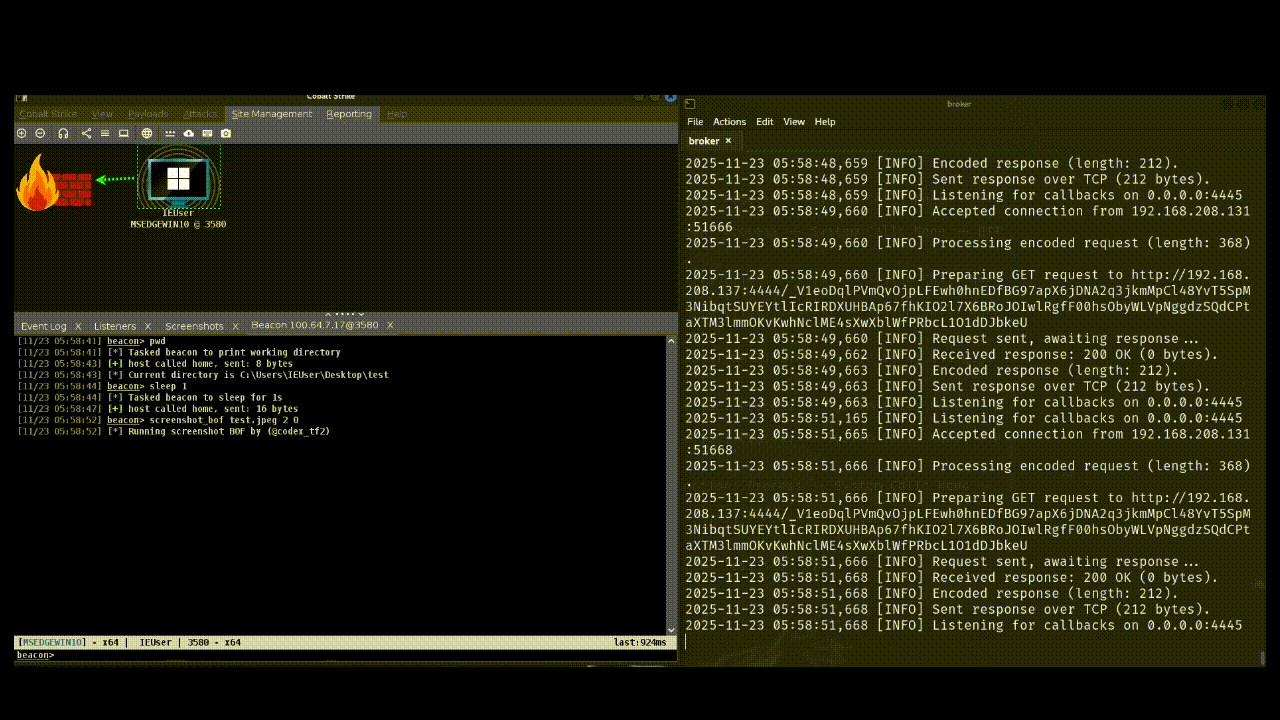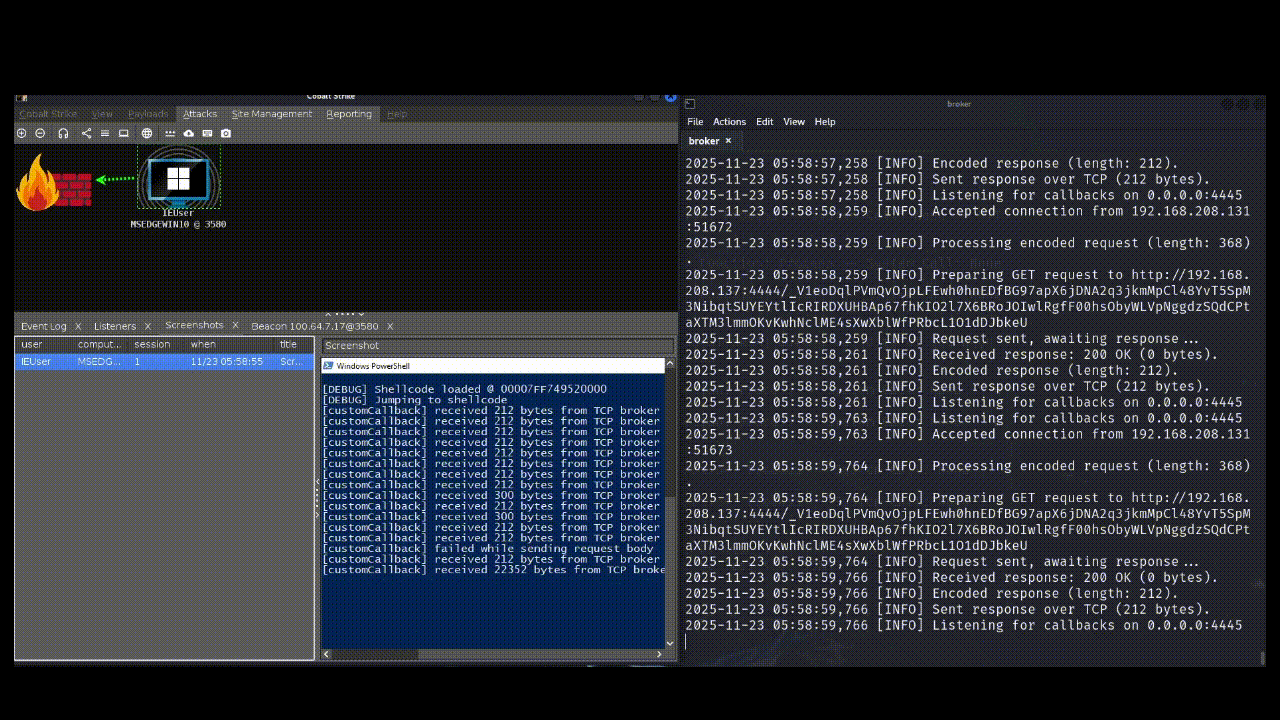 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 csenox/cve-2021-22911
Pre-Auth Blind NoSQL Injection leading to Remote Code Execution in Rocket Chat 3.12.1
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…
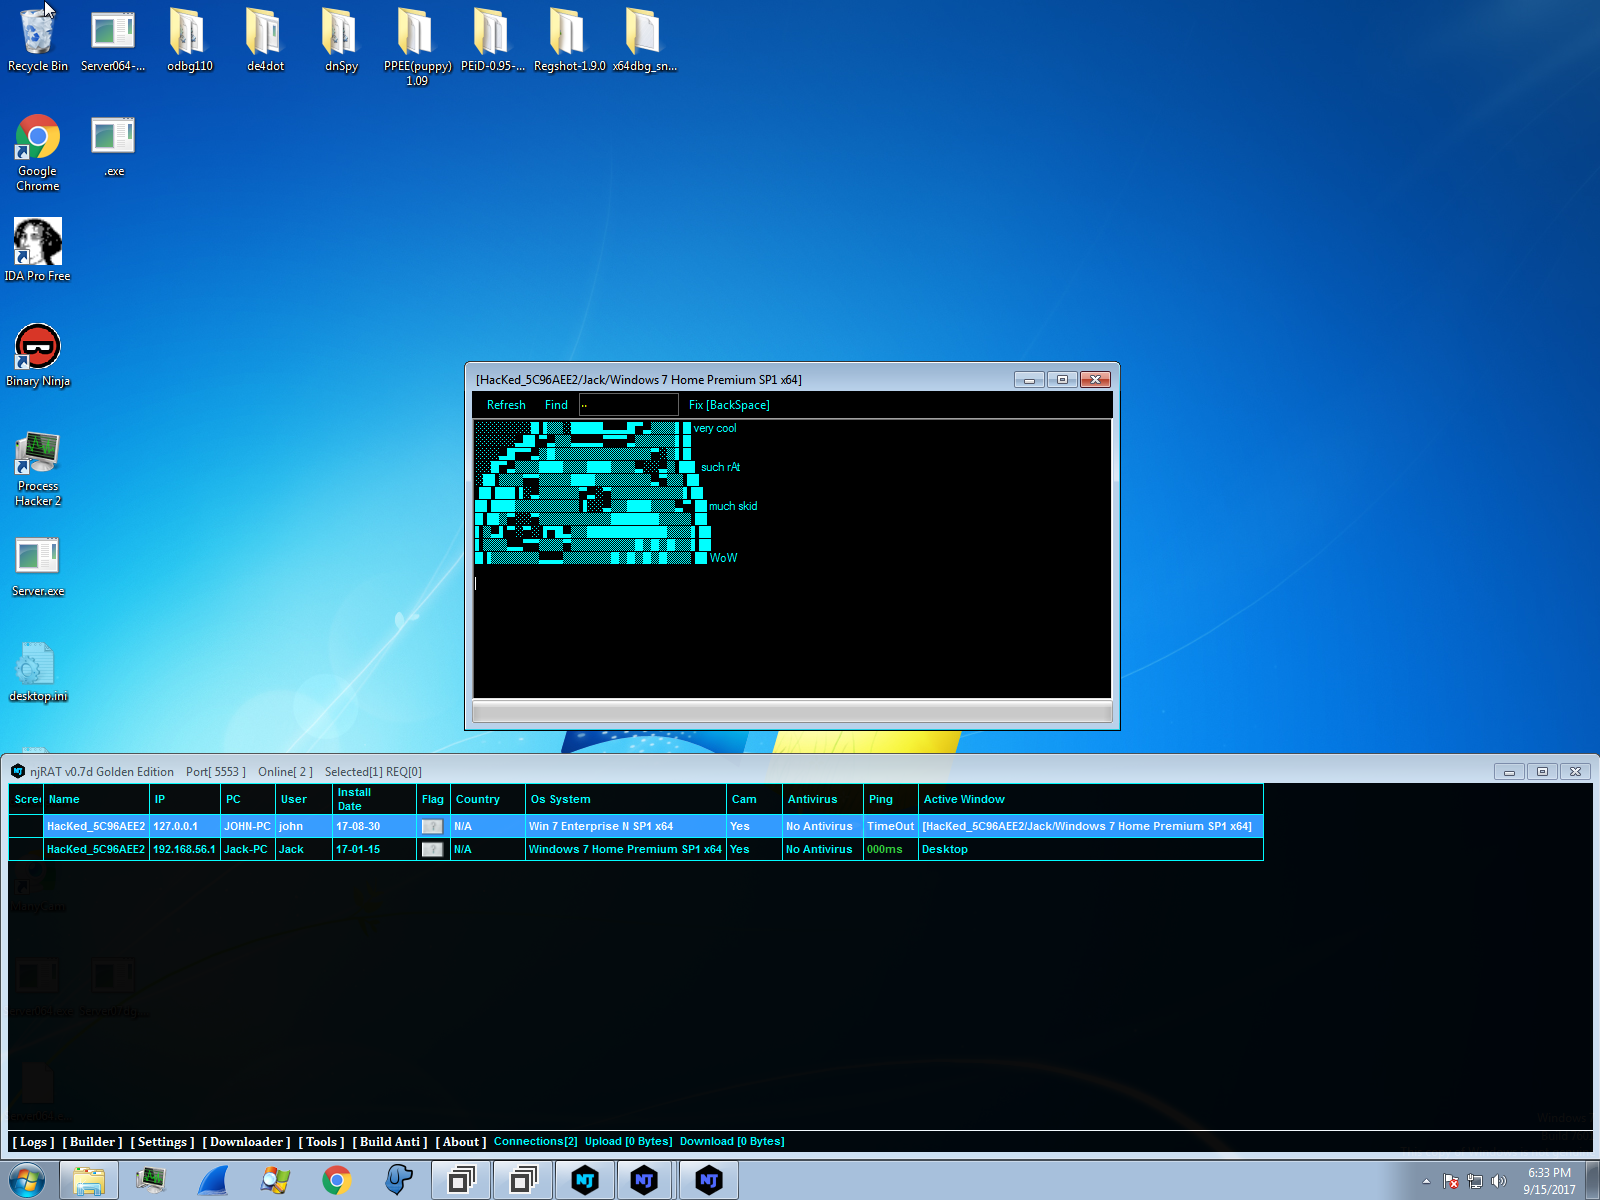 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 emirpolatt/cve-2022-31188
Proof-of-concept exploit for CVE-2022-31188, an SSRF vulnerability in OpenCV CVAT that allows authenticated users with Task Create permissions to…
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 ryehr/hitms_steganography
Embed multiple secret messages in LLM chat token choices using arithmetic/Discop steganographic coders, with bit-exact decoding and steganalysis…
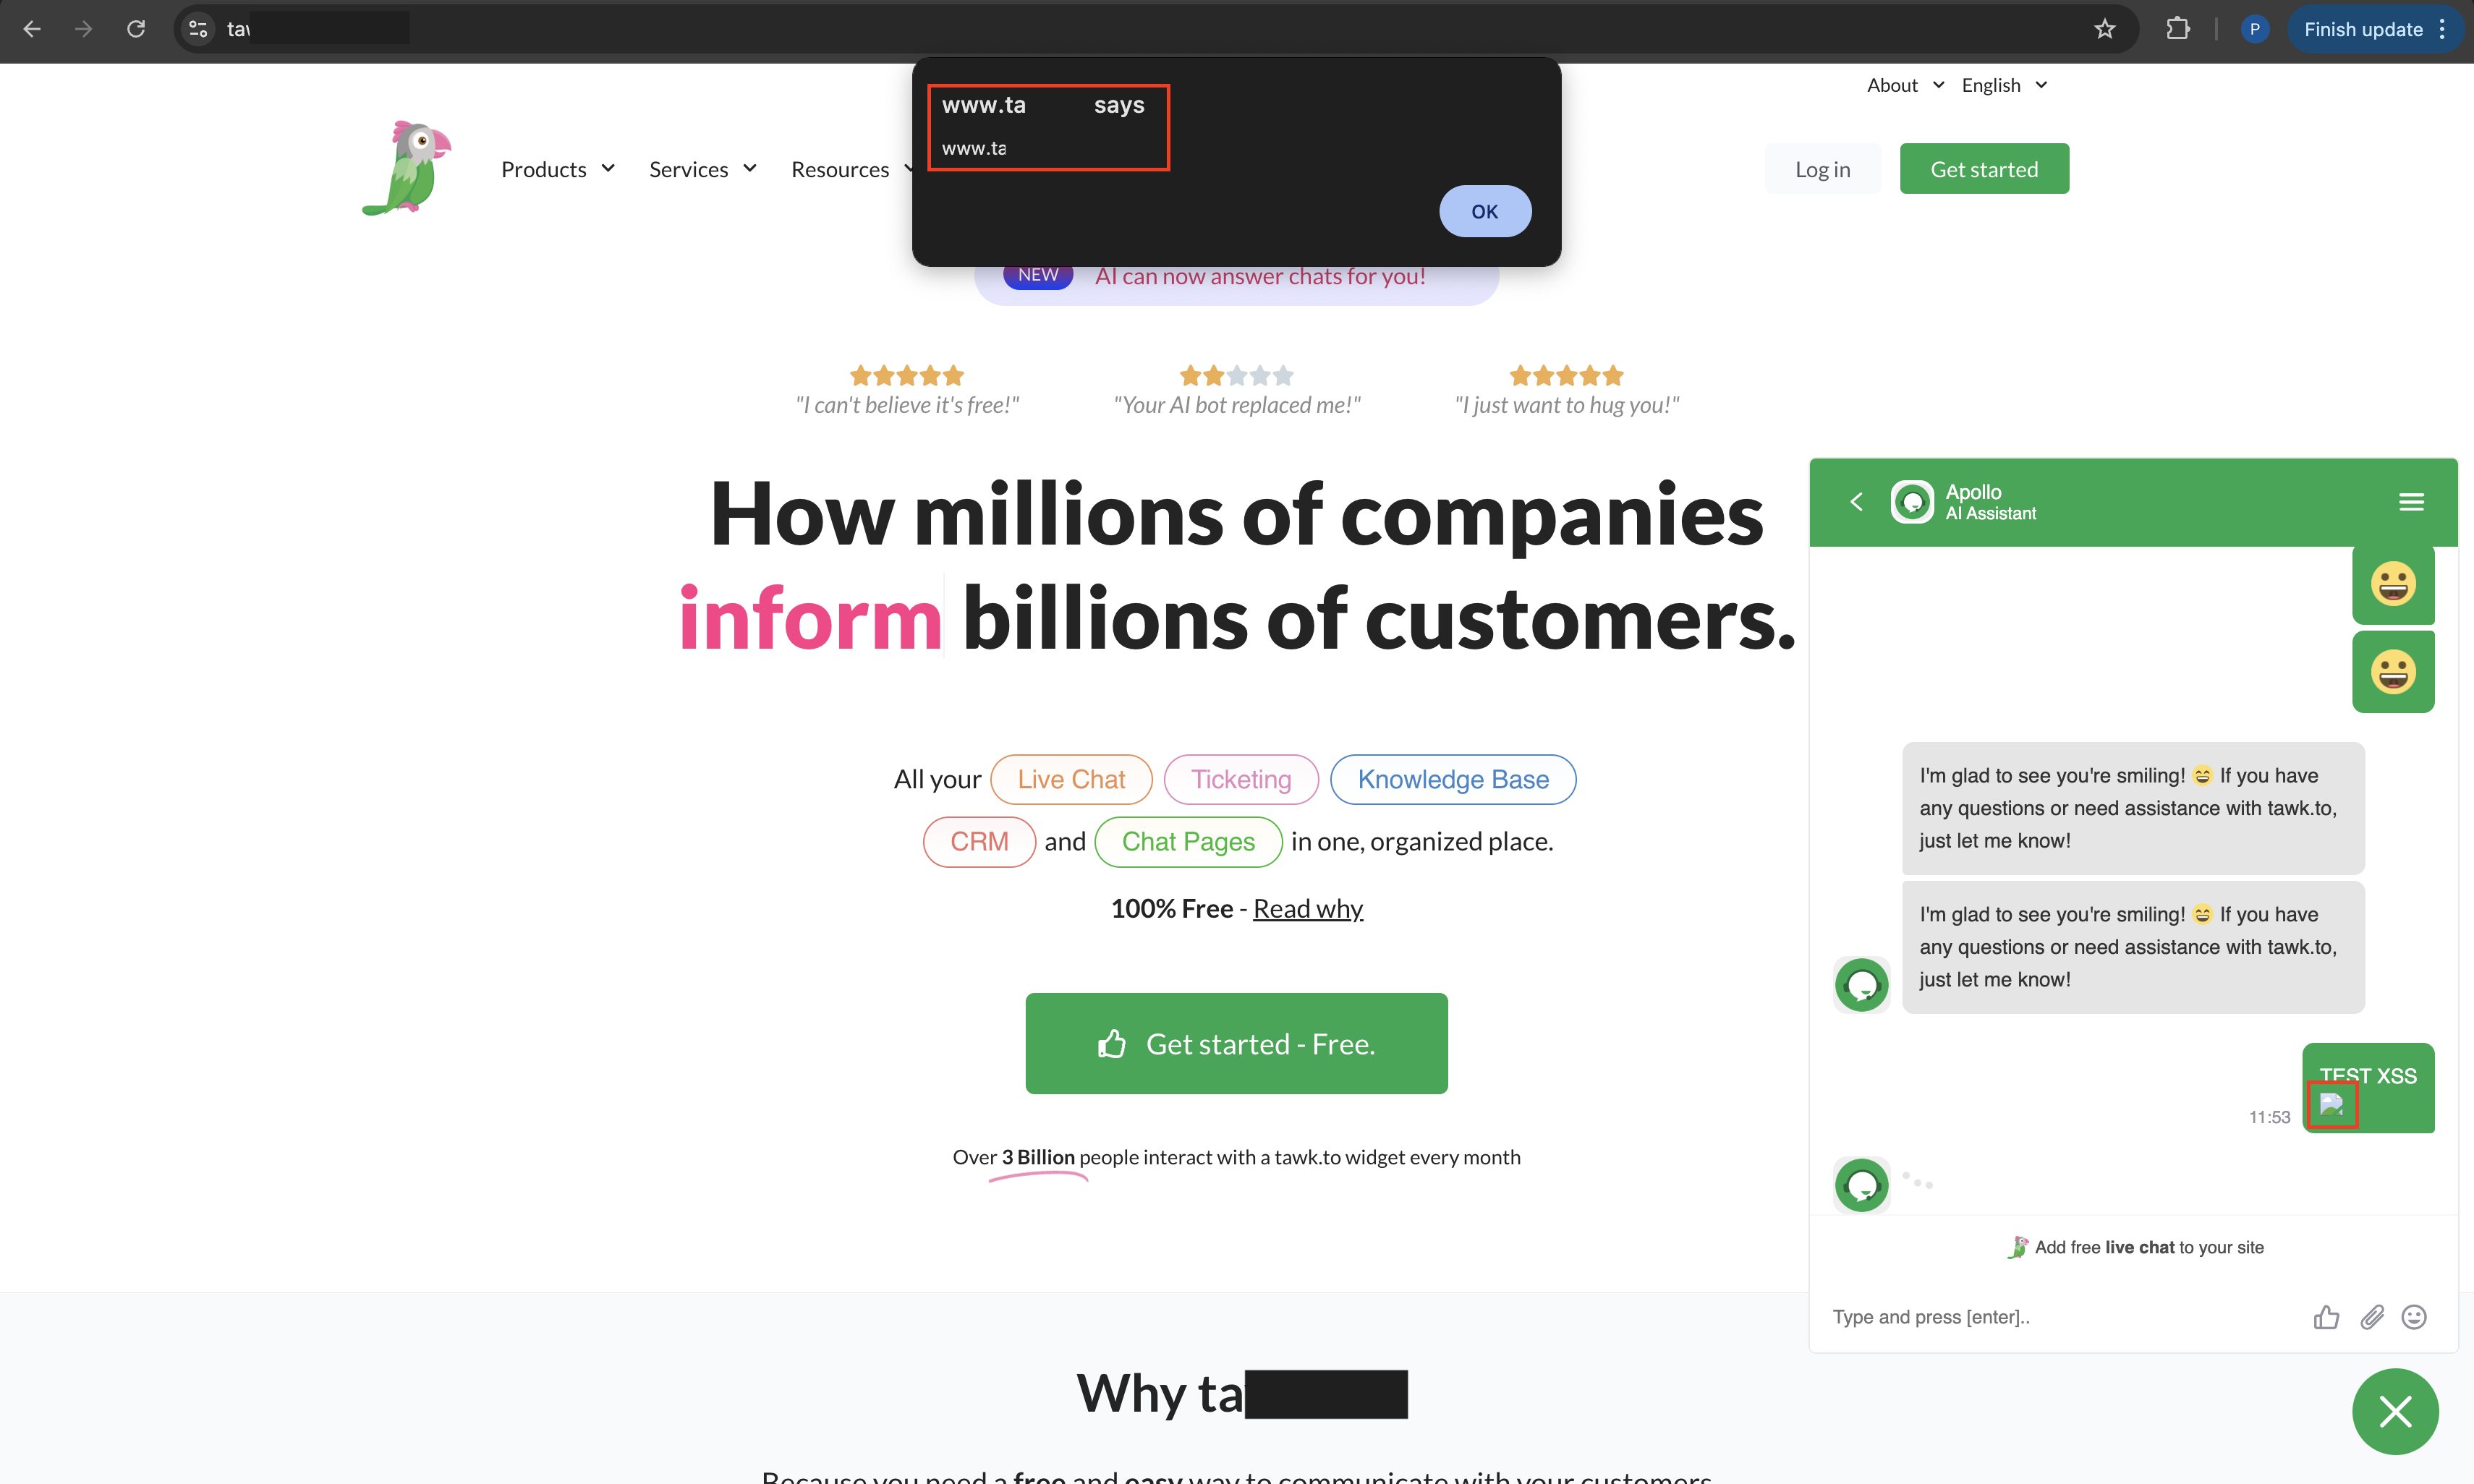 pracharapol/cve-2025-45960
Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in tawk.to Live Chat 1.6.1, demonstrating JavaScript injection via unsanitized…
 theopaid/cve-2026-66750-insufficient-access-controls-allow-for-unauthorized-file-downloads-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized File Downloads (Let's Chat)
 theopaid/cve-2026-66749-unchecked-room-lookup-leads-to-server-crash-let-s-chat-
Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)
 theopaid/cve-2026-66751-insufficient-access-controls-allow-for-unauthorized-room-deletion-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized Room Deletion (Let's Chat)
 rudsarkar/cve-2026-42228
Proof-of-concept exploit for CVE-2026-42228, an unauthenticated chat execution hijacking vulnerability in n8n, with automated scanning and attack…
 nullbyte8080/cve-2026-36228
Proof-of-concept for CVE-2026-36228 demonstrating a denial-of-service vulnerability in Easy Chat Server 3.1 via oversized mtowho parameter. Dry-run…
 secsys-fdu/cve-2025-51865
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Ai2's playground chat, allowing attackers to brute-force predictable message…