
DirtyClone
 gl1tch0x1/dirtyclone
Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
binary-exploitationcryptographyexploitation+3
2
gl1tch0x1/dirtycloneProof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
 ozcanpng/cve-2025-57819-freepbx-rce2root
Full-chain CVE-2025-57819 PoC for FreePBX 15, 16, and 17: unauthenticated SQLi to RCE and root takeover.
 davidcarliez/cve-2019-9702_symantec_encryption_desktop_lpe_poc
Local Privilege Escalation PoC to pop a SYSTEM shell for CVE-2019-9702 in Symantec Encryption Desktop.
 homjxi0e/cve-2017-0108
Proof-of-concept exploit for CVE-2017-0108, a remote code execution vulnerability in Microsoft Windows Graphics Component, triggered via crafted…
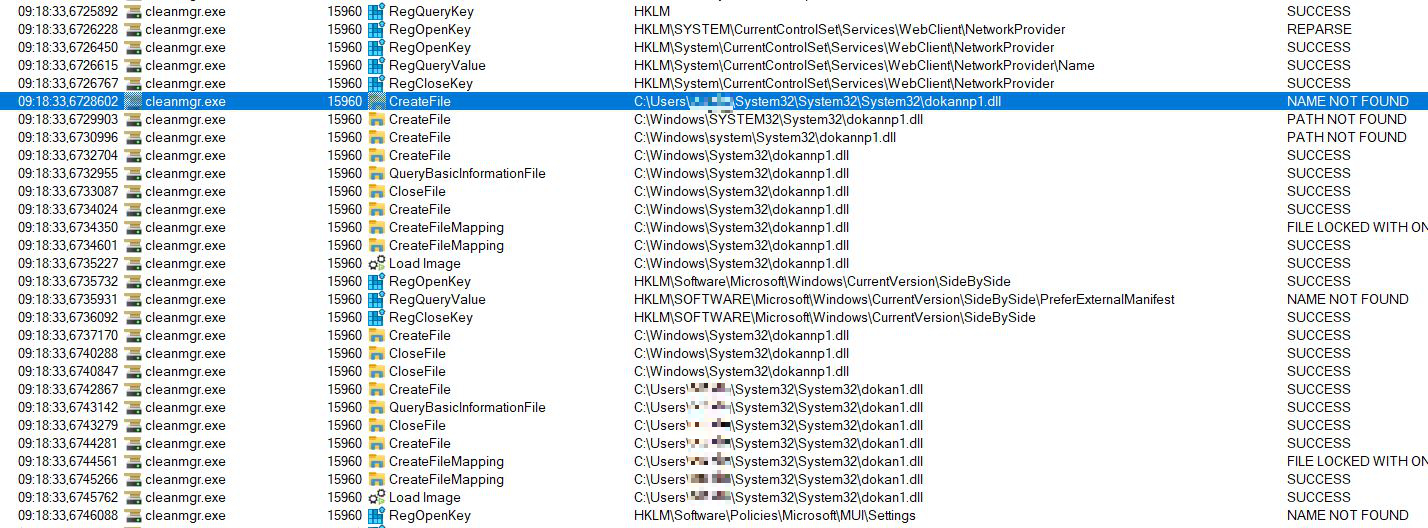 dmitri131313/cve-2025-21420-poc
We found a way to DLL sideload with cleanmgr.exe
 trevocastles/cve-2026-31431-copy-fail
Exploit PoC for CVE-2026-31431 that uses AF_ALG and splice() to overwrite Linux page cache and patch /usr/bin/su in memory, escalating unprivileged…
 hackspeak/cve-2026-60004
Gitea diffpatch RCE (CVE-2026-60004) PoC - repo-write to RCE as Gitea service account
 joshuavanderpoll/cve-2026-44262
Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.
 oilseller2001/poc-for-cve-2025-9074
Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.
 josemlwdf/cve-2019-13272
This is a Python 3 version of this exploit. Hope it works!!!

 nu11secur1ty/0
Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…
 its1zero/cve-2025-57819-exploit
Python exploit for CVE-2025-57819 targeting FreePBX via unauthenticated SQL injection to achieve remote code execution with automatic reverse shell…
 0xdak/cve-2025-32463_exploit
Local privilege escalation exploit for sudo 1.9.14-1.9.17 that abuses CVE-2025-32463 chroot handling, planting a malicious NSS library constructor to…
 itzheartzz/mass-cve-2024-27956
Proof-of-concept exploit for CVE-2024-27956 SQL injection in ValvePress Automatic plugin. Creates admin users in WordPress to achieve remote code…
 epsteina16/docker-escape-miner
Code sample for using exploit CVE-2019-5736 to mine bitcoin with no association to original container or user.
 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
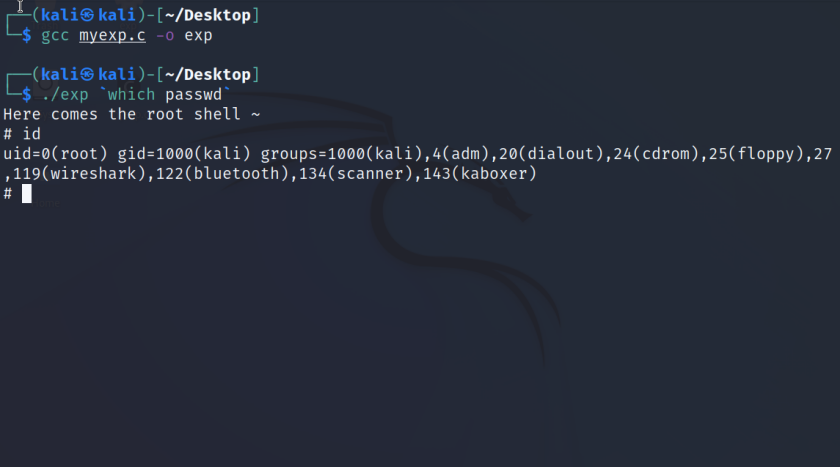 rabomen/dirty-pipe
exp of CVE-2022-0847
 killtr0/cve-2021-1675-printnightmare
PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation via Print Spooler, with custom DLL payload injection and…