CVE-2019-9053
Python 3 implementation of a time-based blind SQL injection exploit targeting CVE-2019-9053 in CMS Made Simple 2.2.8, with wordlist-based enumeration.

Python 3 implementation of a time-based blind SQL injection exploit targeting CVE-2019-9053 in CMS Made Simple 2.2.8, with wordlist-based enumeration.

Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.

Simple exploit

Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…

Python exploit for CVE-2019-9053 targeting SQL injection in CMS Made Simple, enabling automated time-based blind injection and credential extraction.

Proof-of-concept exploit for SQL injection in Simple Content Management System PHP, demonstrating UNION-based data extraction via the id parameter in…

Exploit for CVE-2026-7459 targeting Simple History plugin missing authorization vulnerability, enabling unauthenticated account takeover in WordPress…

Google Dork-based scanner for detecting CVE-2019-9053 SQL injection in CMS Made Simple < 2.2.10. Designed for security auditing and patch…

Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…

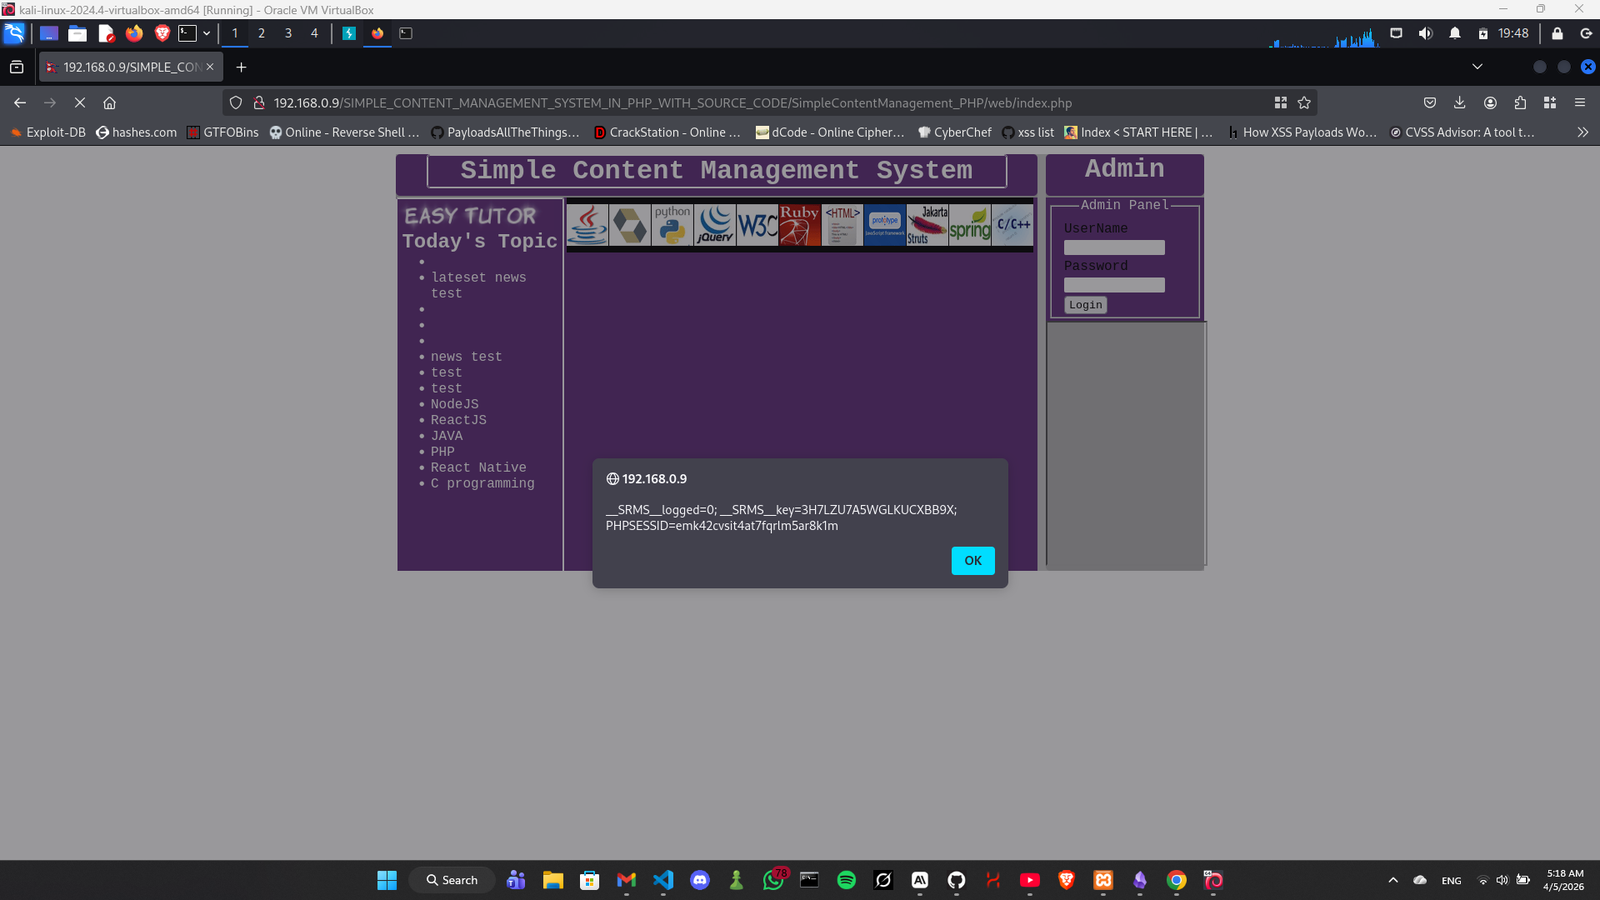
Proof-of-concept for a stored XSS vulnerability in Simple Content Management System PHP, demonstrating session cookie theft via unsanitized News…

CMS Made Simple CVE-2019-9053 Exploit (Python 3)

I created simple react2shell CVE-2025-55182 python exploit

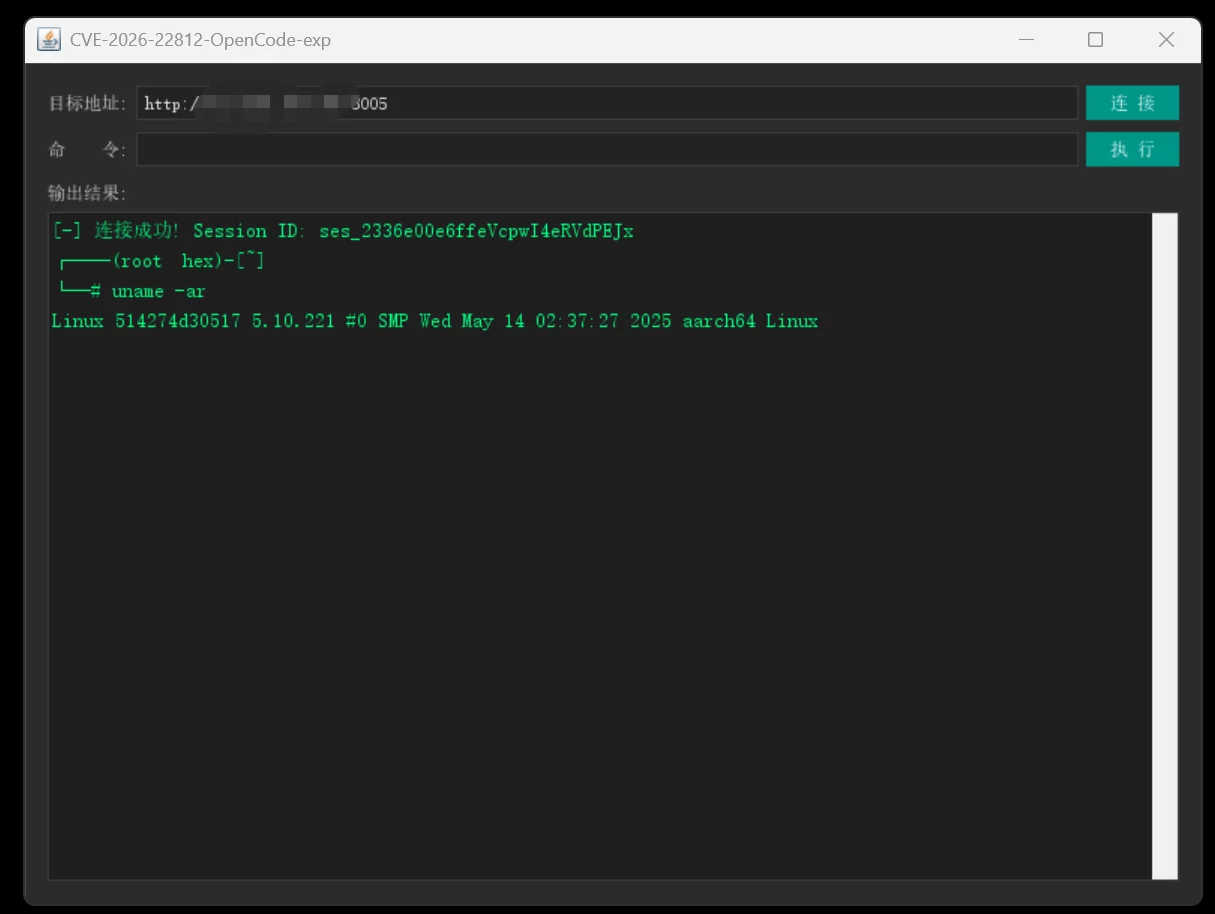
Java-based proof-of-concept exploit for CVE-2026-22812, a remote code execution vulnerability in OpenCode, demonstrating exploitation with a simple…

Python exploit script for CVE-2019-9053 targeting CMS Simple. Automates vulnerability exploitation and information gathering for penetration testing…

Check a target IP for CVE-2023-20198 vulnerability in Cisco IOS XE web UI. Simple Python script for rapid exploitation verification.

Here is a simple but effective exploit for CVE-2025-29927.

Simple shell script for the exploit

Proof-of-concept exploit for CVE-2019-11358, a prototype pollution vulnerability in jQuery's extend method (versions <3.4.0). Demonstrates the attack…