
CcmMessagingBackdoor
 synacktiv/ccmmessagingbackdoor
Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.
command-and-controlpayload-developmentpersistence-mechanisms+3
19
synacktiv/ccmmessagingbackdoorProof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.
 momika233/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, demonstrating command injection in Palo Alto PAN-OS with a Python-based backdoor, persistence via…
 c411e/cve-2024-53691
CVE-2024-53691
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 shubham0d/cve-2020-1048
POC exploit code for CVE-2020-1048(PrintDemon)
 geffner/cve-2020-8289
Proof-of-concept exploit for CVE-2020-8289 demonstrating remote code execution as SYSTEM/root via Backblaze backup client's SSL verification bypass…
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
 kirinse/cve-2023-42115
Python-based exploit and reverse shell payload generator for CVE-2023-42115, featuring scan and exploit modes with cross-platform payload creation.
 ally-petitt/cve-2024-48990-exploit
My exploit for CVE-2024-48990. Full details of how I made this are on my blog.
 drapl0n/pwnkit
USB Rubber Ducky payload that exploits CVE-2021-4034 to escalate privileges and spawn a root shell on Unix-like systems in under 10 seconds.
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
 777erp/cve-2026-49176_bof
CVE-2026-49176 WalletService LPE — standalone PoC + Cobalt Strike BOF (SYSTEM command on interactive session)
 sinsinology/cve-2022-26503
Proof-of-concept exploit for CVE-2022-26503, a local privilege escalation vulnerability in Veeam Agent for Windows via .NET deserialization, enabling…
 0p5cur/cve-2025-32462-poc
🔓 Local privilege escalation PoC for CVE-2025-32462 (sudo -h bypass) – gain root via misconfigured sudoers
 richard-tang/sscms-pluginshell
CVE-2022-28118
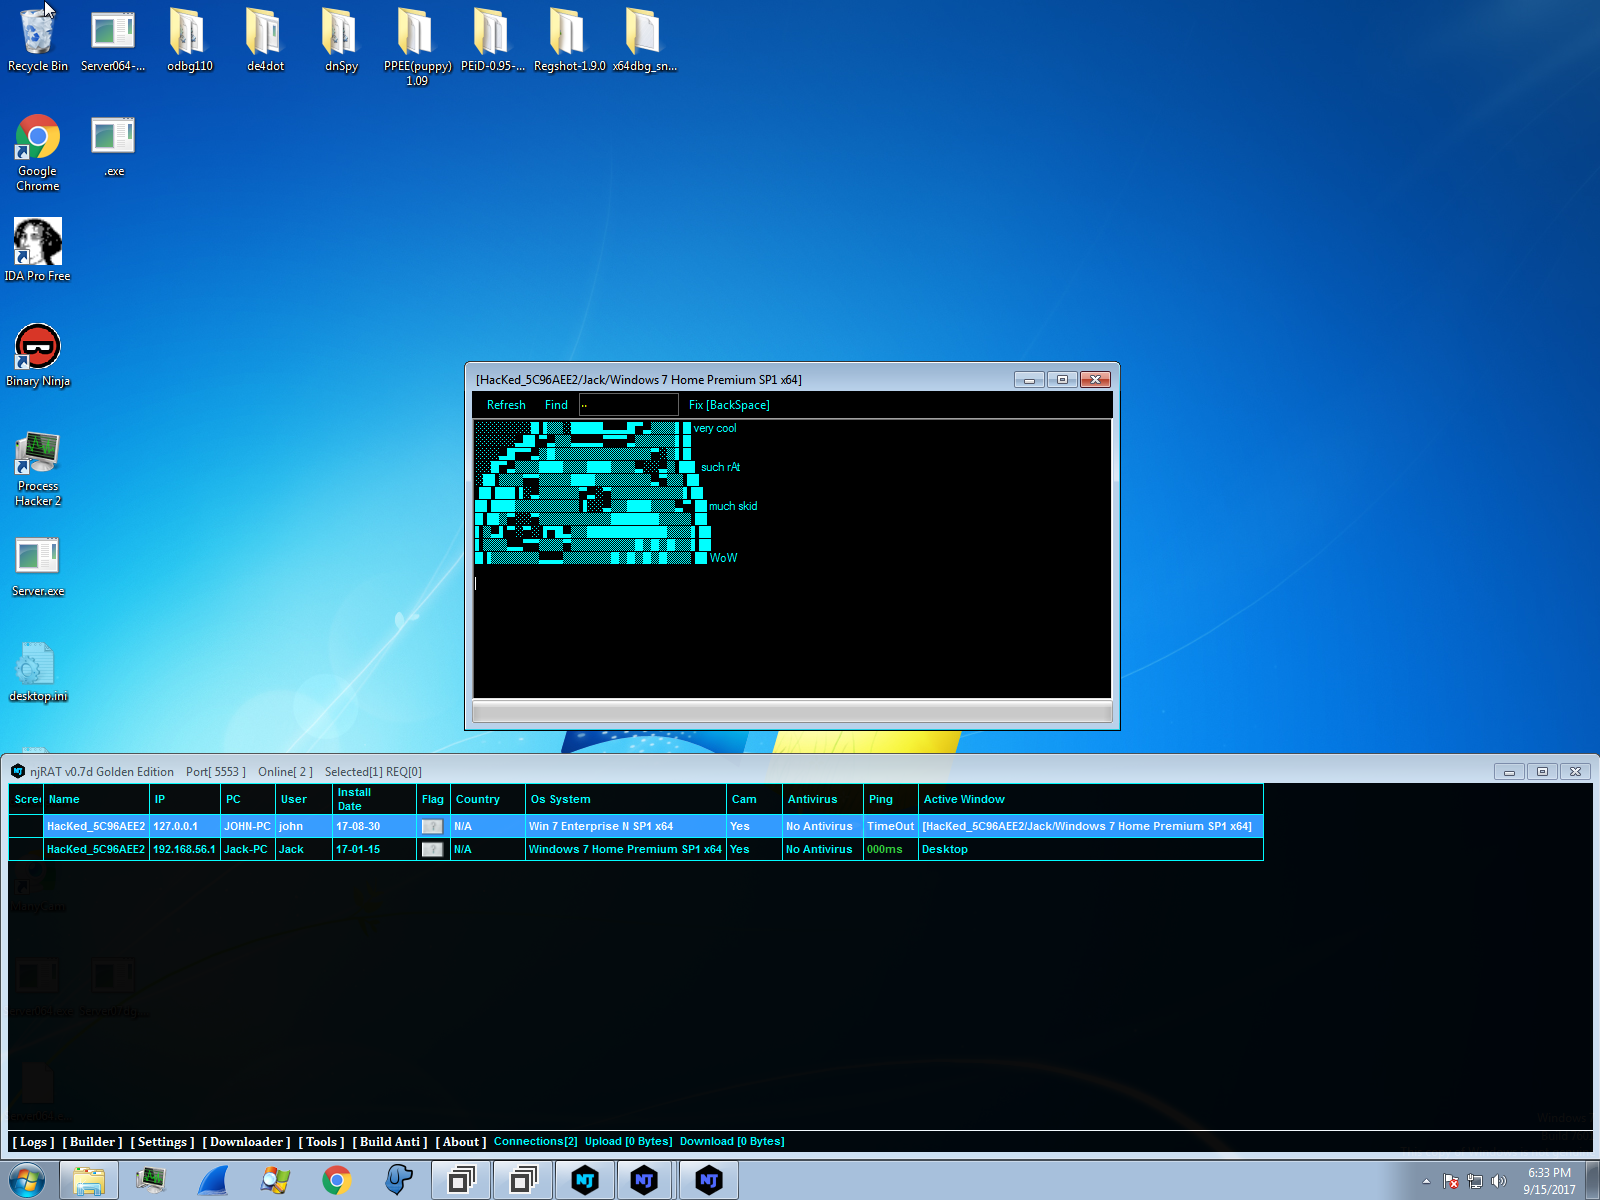 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 xboxoneresearch/cve-2023-21768-dotnet
C# / .NET version of CVE-2023-21768