CVE-2024-38077-MadLicense-exploit

Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
binary-exploitationeducationexploitation+6
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…

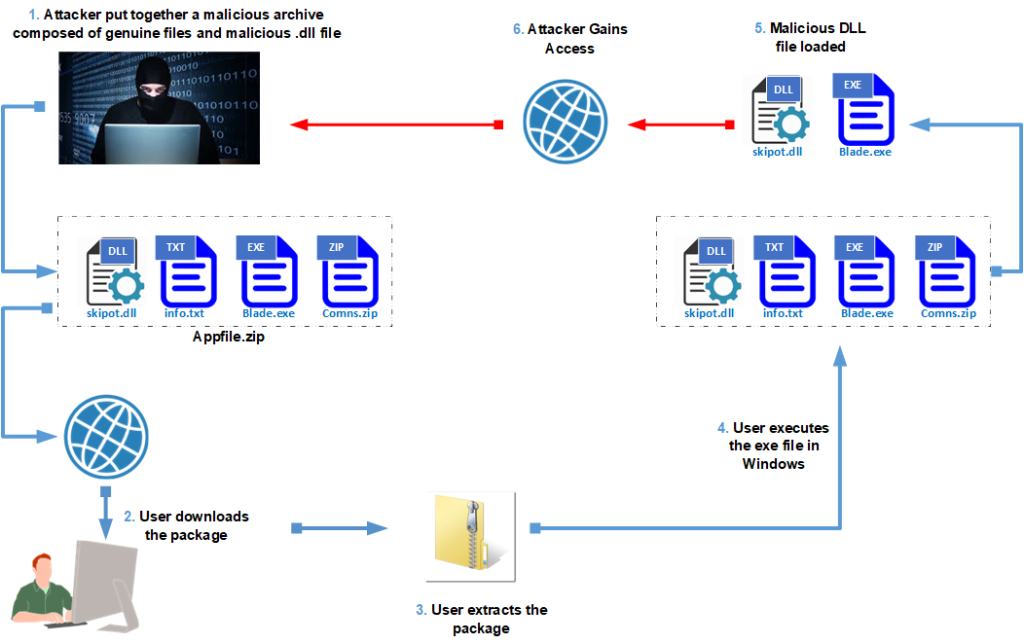
DLL Injection and CVE-2010-3124

Microsoft signed ActiveDirectory PowerShell module

Injects x64 managed DLLs into GUI processes via SetWindowsHook, with a modular C# payload runner and LSASS dump POC for red-team/offensive Windows…

Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection