

PrologWinDbg
 dumpanalysis/prologwindbg
Use Prolog to analyze memory dumps and stopped live processes in WinDbg.
binary-analysisdebuggersdigital-forensics+4
10
dumpanalysis/prologwindbgUse Prolog to analyze memory dumps and stopped live processes in WinDbg.
 nazeeh111/capsulith
Run preserved ARM64 code in Node or a browser; inspect decoded image pixels and initialized memory.
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
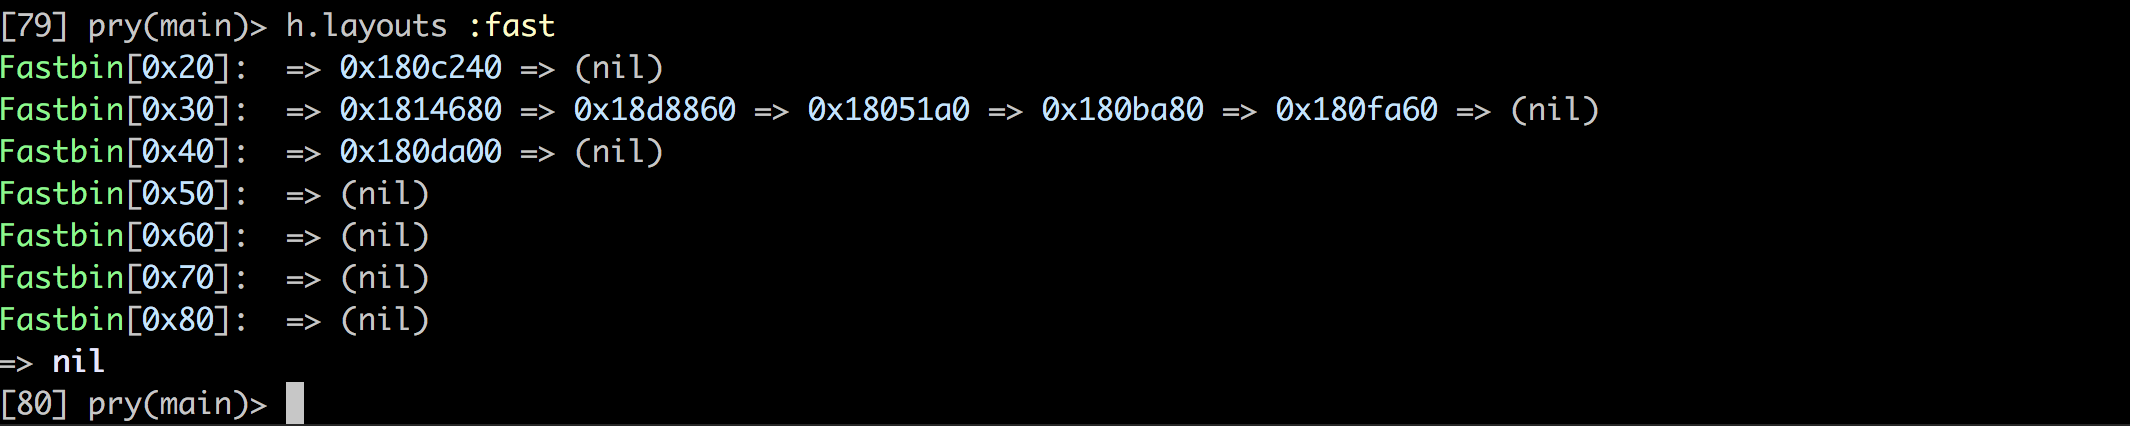 david942j/heapinfo
An interactive memory info for pwning / exploiting