
fastgpt-sandbox-audit
 qianlijaingshan/fastgpt-sandbox-audit
FastGPT Python sandbox escape chain audit tool (CVE-2026-32128 related, v4.14.8 inspect chain)
ai-securitycontainer-escapedynamic-analysis-sandboxing+4
1
qianlijaingshan/fastgpt-sandbox-auditFastGPT Python sandbox escape chain audit tool (CVE-2026-32128 related, v4.14.8 inspect chain)
 squ1shification/pngboomer-cve-2026-77622
Sliver HTTP(S) C2 PNG bomb DoS exploit — GHSA-663m-7x7m-g4fw (CVE-2026-77622)
 0xmrma/cve-2026-5061
Consul Template validated where a symlink pointed during template evaluation, but its later dependency fetch read the original path. Retargeting the…
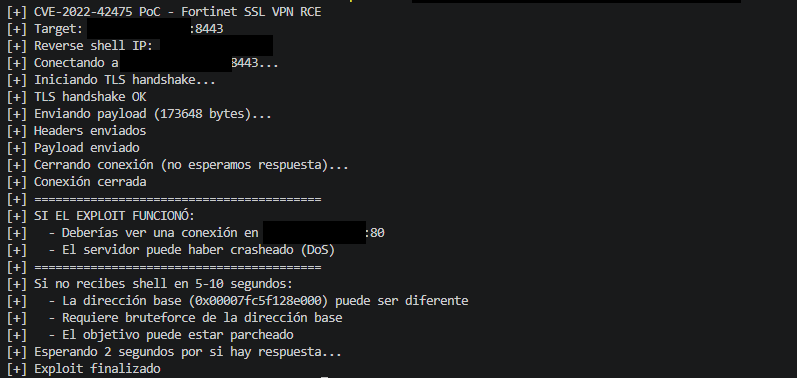 ull0a/cve-2022-42475-poc
Proof of Concept (PoC) for research and controlled laboratory validation of CVE-2022-42475, a critical heap-based buffer overflow vulnerability…
 covepseng/cve-2026-49352-poc
Exploitability PoC for CVE-2026-49352 (9router Hardcoded JWT Secret Authentication Bypass)
 biitts/cve-2026-56782-gorse-auth-bypass
CVE-2026-56782 — Gorse <0.5.10 unauthenticated DB dump/restore (admin_api_key fail-open). Lab + PoC, verified e2e.
 davidmgaviria/cve2_jenkins_rce
A proof of concept cross-site WebSocket hijacking exploit for CVE-2024-23898 — a vulnerability affecting Jenkins versions 2.217-2.441. For…
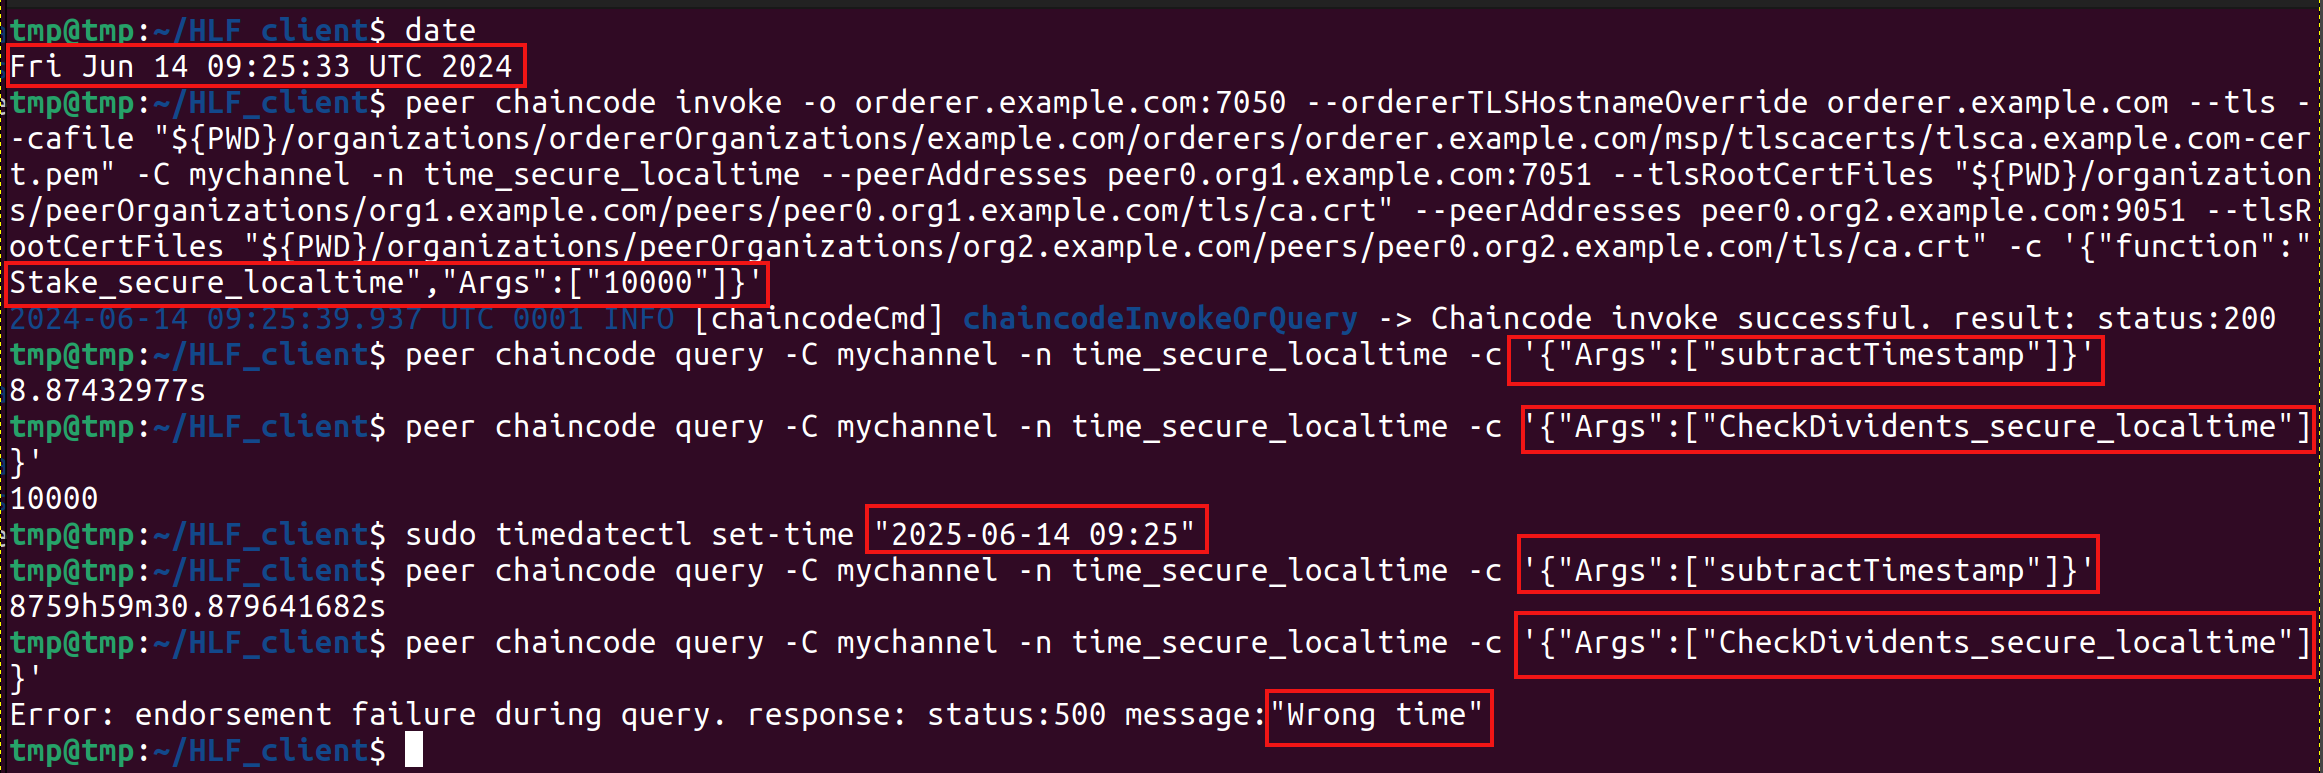 shanker-sec/hlf_txtime_spoofing
PoC covering the problem of transaction time manipulation (CVE-2024-45244) in the Hyperledger Fabric blockchain.
 plunder707/attestos
Bazzite plus a TPM boot attestation layer. Work in progress: builds unverified, UKI mechanism unresolved. Spec: github.com/plunder707/attested-gaming
 iqx6889/cve-2026-52813-gogs-rce
CVE-2026-52813 (Gogs Path Traversal → Git Hooks RCE) defensive writeup: root-cause & patch analysis, Sigma/SIEM detection rules, IOCs, non-intrusive…
 revyhub/cve-2026-43284---dirtyfrag-analysis-thm-
TryHackMe Dirty Frag (CVE-2026-43284) — Linux LPE writeup
 pvharmo2/gha-lab-2f775f277c
Authorized lab reproduction of CVE-2025-47928 (spotipy-dev/spotipy pull_request_target secrets exfiltration) — snapshot at vulnerable commit 4f5759d
 milloni/cve-2019-5736-exp
Exploit for the CVE-2019-5736 runc vulnerability
 vdisec/cve-2019-19871-auditguide
Audit Guide for the Citrix ADC Vulnerability CVE-2019-19871. Collected from multiple sources and threat assessments. Will be updated as new methods…
 chusiang/cve-2016-3714.ansible.role
Fix ImageMagick Command Injection (CVE-2016-3714) with Ansible.
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.
 gustavorobertux/gotigate
Go-based exploit for CVE-2022-40684 targeting Fortinet FortiGate devices. Automates authentication bypass to gain administrative access via the web…
 devengpk/cve-2022-1388
Exploit and mass-check script for CVE-2022-1388 targeting F5 BIG-IP iControl REST unauthenticated remote command execution. Supports single host,…