
Auto_EAP
 tylous/auto_eap
Automated Brute-Force Login Attacks Against EAP Networks.
password-attackspenetration-testingwi-fi-auditing+1
tylous/auto_eapAutomated Brute-Force Login Attacks Against EAP Networks.
 impostorkeanu/bruteloops
Protocol agnostic online password guessing API.
 agienka/blindy
Simple script to automate brutforcing blind sql injection vulnerabilities
 embee-research/yara-detection-rules
Yara Rules for Modern Malware
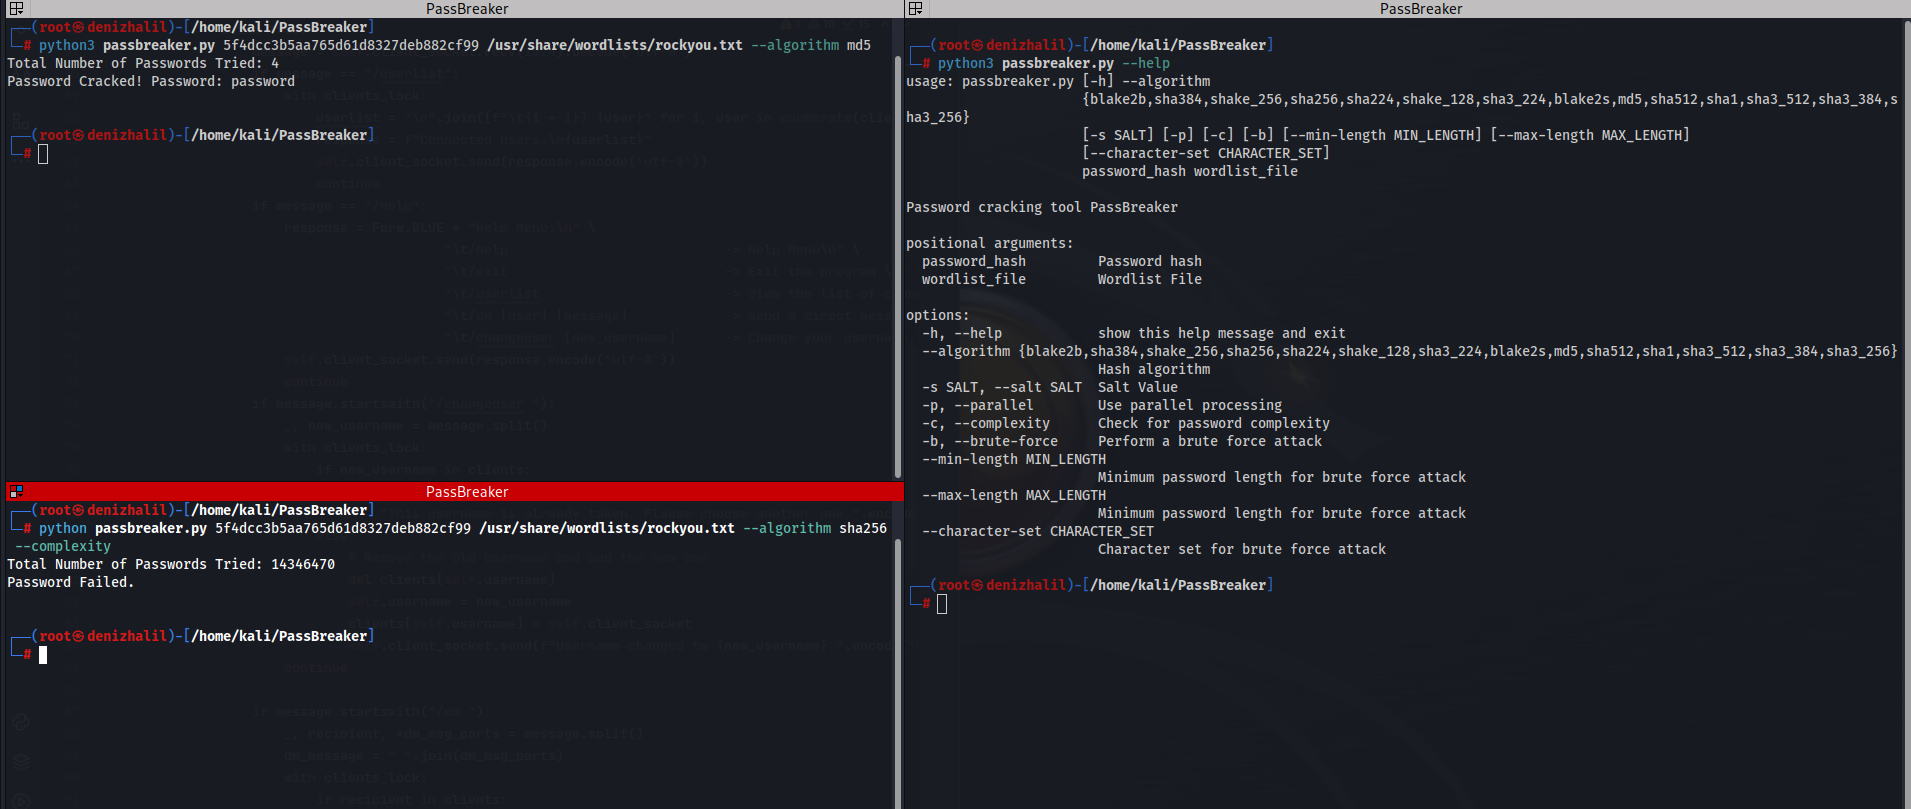 halildeniz/passbreaker
Python-based password cracker supporting wordlist and brute-force attacks with multiple hash algorithms, salt, parallel processing, and password…
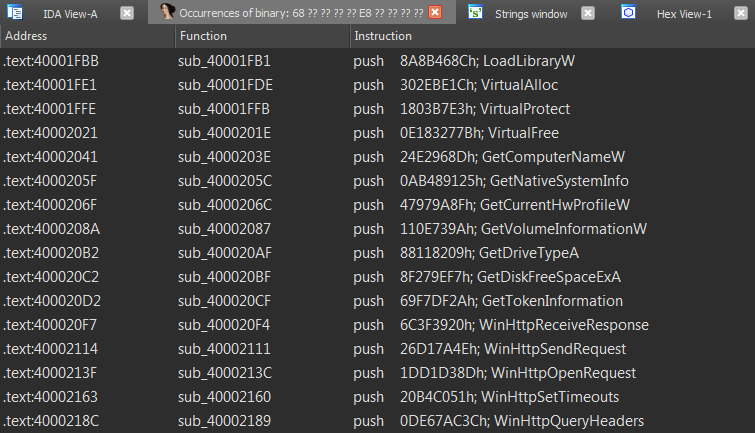 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 synacktiv/radmin3-password-cracker
Radmin Server 3 credentials dumper/cracker
 mavlevin/d-link-cve-2021-27342-exploit
Exploit for CVE-2021-27342 vulnerability (telnet authentication brute-force protection bypass)
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
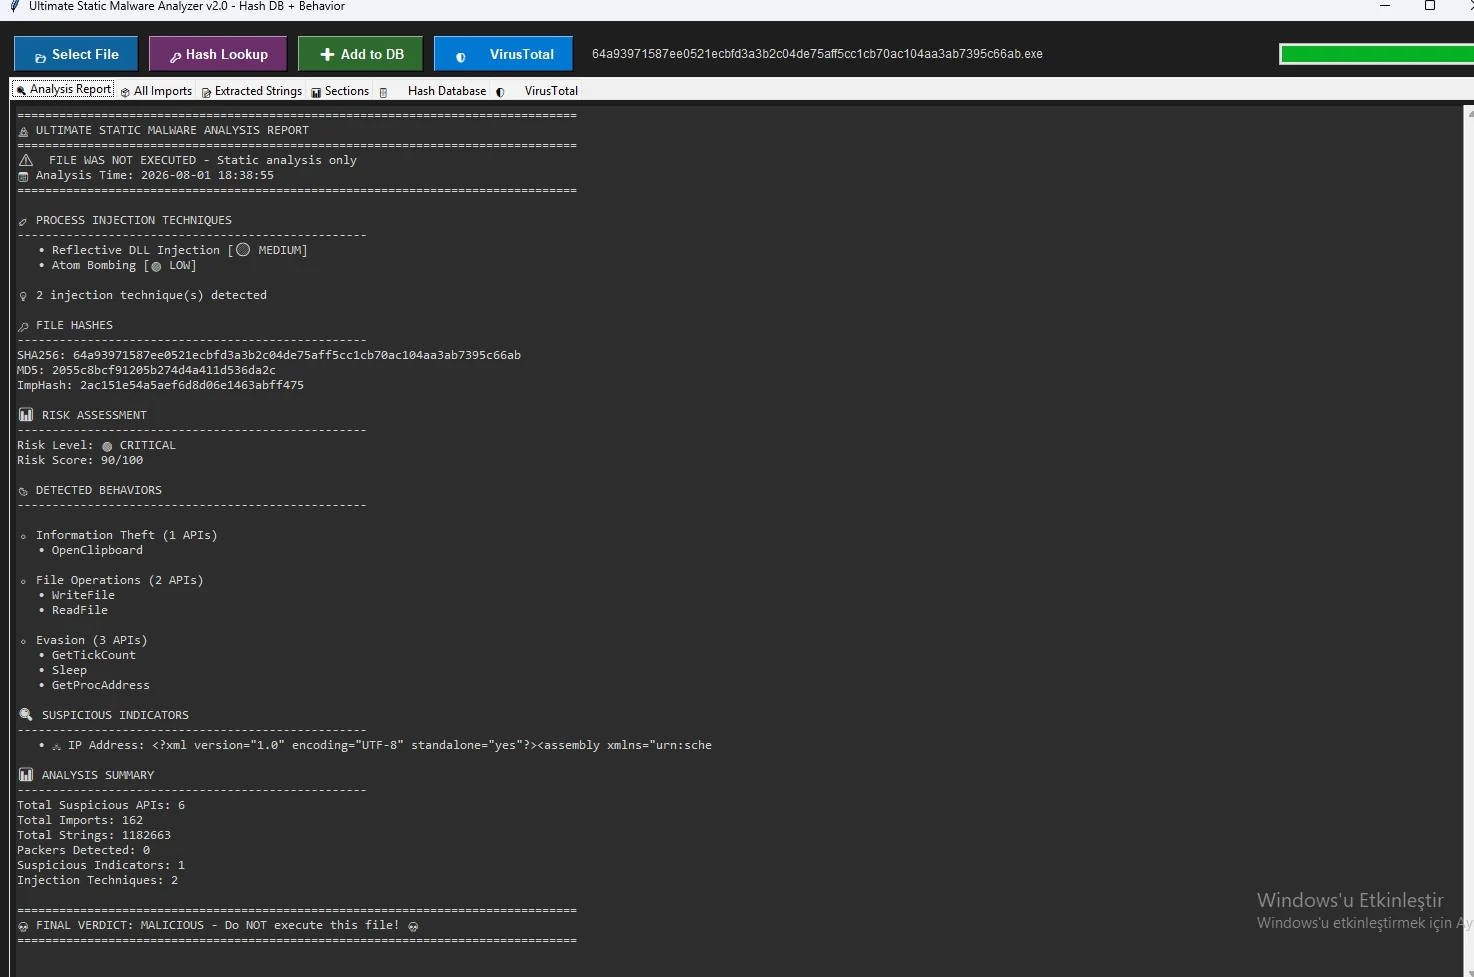 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
 pervinzahidli/cve-2026-77771
Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
 pingport80/cve-2019-17240
This is the exploit of CVE-2019-17240.
 coldfusionx/cve-2019-17240_bludit-bf-bypass
Bludit <= 3.9.2 - Authentication Bruteforce Mitigation Bypass Exploit/PoC
 pocpioneer/cve-2025-4094-poc
WordPress Plugin Digits < 8.4.6.1 - OTP Auth Bypass via Bruteforce (CVE-2025-4094)
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 itzmetanjim/cve-2026-8697
Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
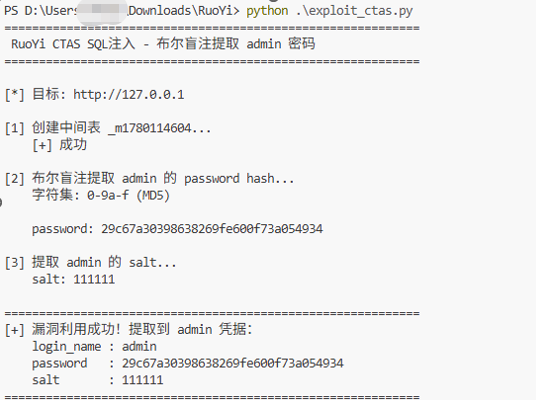 chinesespeople/cve-2026-52614
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3