

CheatSheetSeries
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
api-securityauthenticationcloud-security+6
33.2k
owasp/cheatsheetseriesThe OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 paragonie/awesome-appsec
A curated list of resources for learning about application security
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 six2dez/wahh_extras
The Web Application Hacker's Handbook - Extra Content
 owasp/vulnerable-web-application
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
 cy-clon3/awesome-ios-security
A curated list of awesome iOS application security resources.
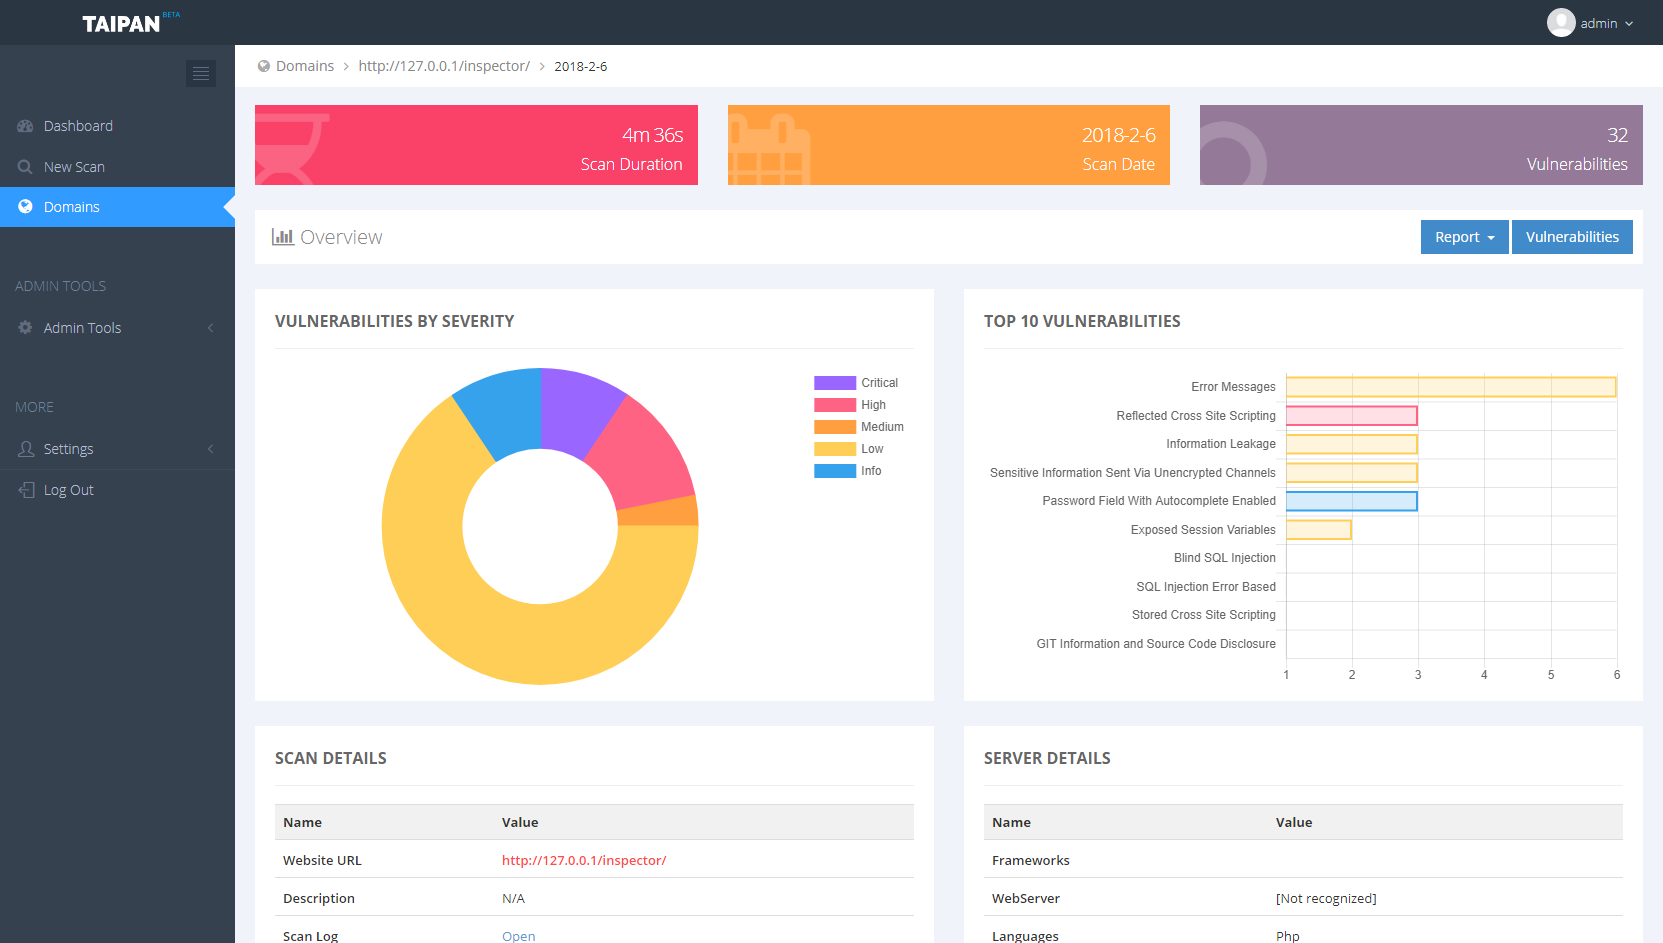 enkomio/taipan
Web application vulnerability scanner
 takito1812/web-hacking-playground
Web application with vulnerabilities found in real cases, both in pentests and in Bug Bounty programs.
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
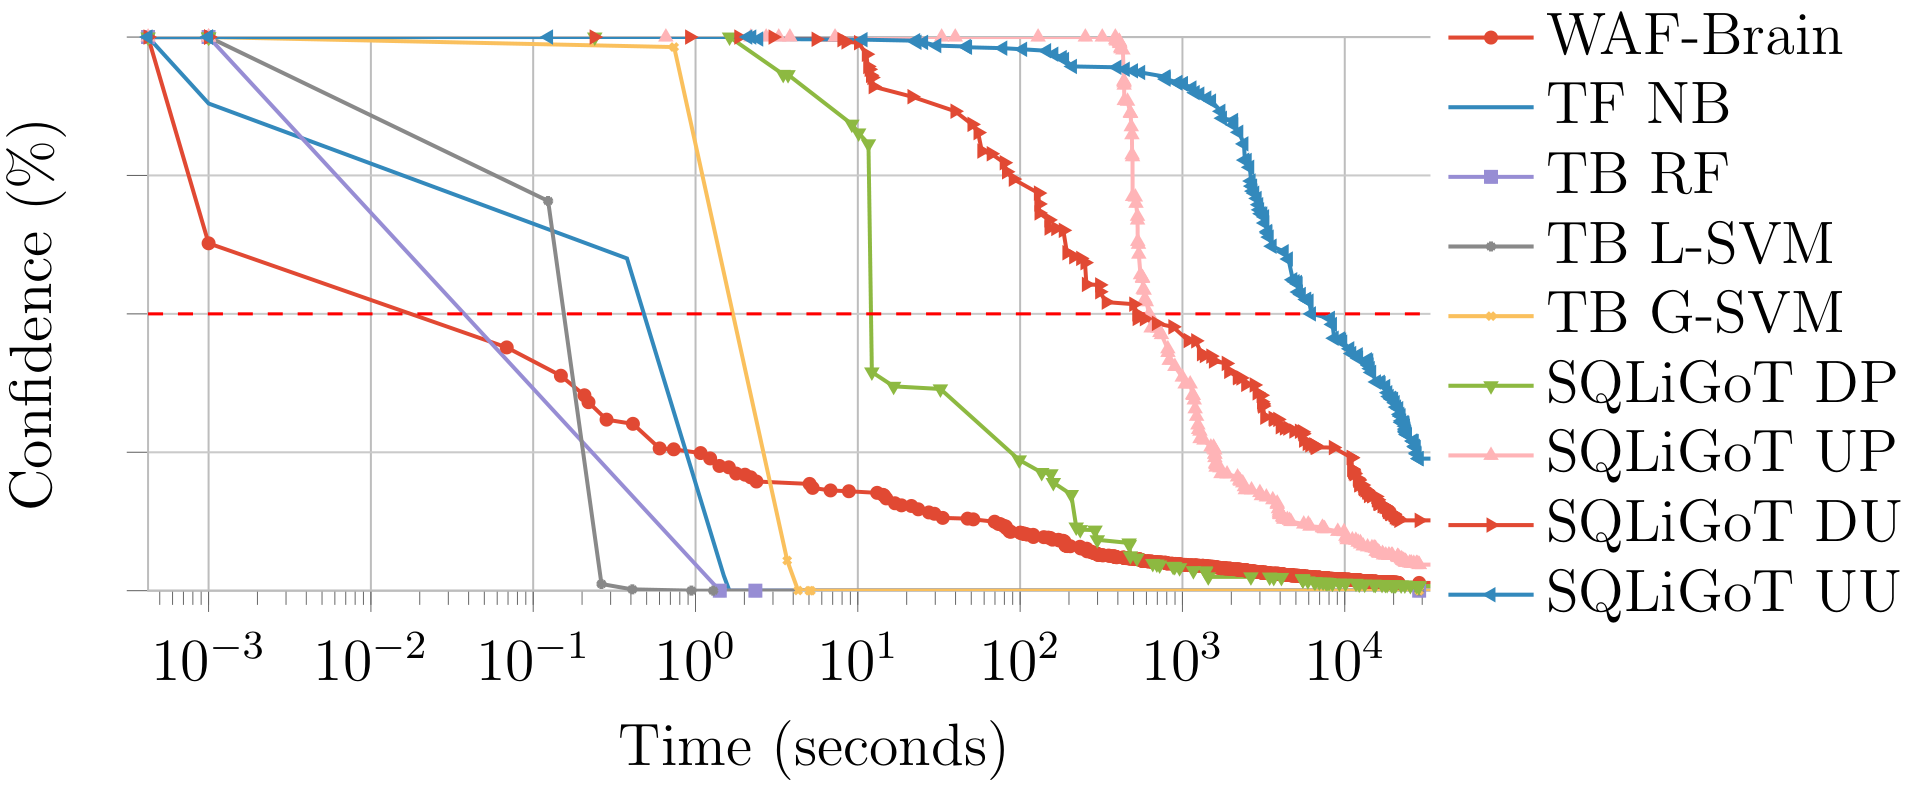 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
 stefan2200/aparoid
Static and dynamic Android application security analysis
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 owasp/asvs
Application Security Verification Standard