
suricata-vedas
 arpsyndicate/suricata-vedas
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for CVEs
exploit-frameworksintrusion-detectionmachine-learning+2
arpsyndicate/suricata-vedasVEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for CVEs
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 elihiho/security-operations-labs
Threat Modeling, IT-/OT-Segmentierung, Snort Detection und reproduzierbare Validierung eines Drupal-Detection-Profils.
 phucc29/cve-2025-55182
Proof-of-concept exploit demonstrating remote code execution via insecure deserialization in React Flight protocol (CVE-2025-55182). Includes Snort…
 tungduongnt/cve-2014-0160.
Docker-based lab environment for exploiting CVE-2014-0160 (Heartbleed) to leak sensitive memory from nginx web servers, with Snort IDS detection…
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
 trnguyen03/activemq-ids-ips-lab
IDS/IPS lab for detecting and preventing Apache ActiveMQ RCE (CVE-2023-46604) using GVM, Nmap, Snort, iptables, and UFW.
 snort3/snort3
Multi-threaded network intrusion detection and prevention system with rule-based detection, protocol-aware inspection, and pcap analysis for…
 22imer/cve-2014-0160
Dockerized training lab for exploiting Heartbleed (CVE-2014-0160) via TLS heartbeat to leak nginx memory, plus Snort rule to detect attacks.
 deepfence/packetstreamer
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐
 c3rb3ru5d3d53c/signatures
Community Detection Signature Build and Distribution Pipeline for YARA, Suricata, Snort and Sigma
 snorby/snorby
Ruby On Rails Application For Network Security Monitoring
 mandiant/heyserial
Programmatically create hunting rules for deserialization exploitation with multiple keywords, gadget chains, object types, encodings, and rule types
 mvlnetdev/cve-2021-31166-detection-rules
Different rules to detect if CVE-2021-31166 is being exploited
 kimobu/cve-2021-44228
CVE-2021-44228 investigation toolkit with Log4j RCE PoC, JNDIExploit payload runner, Snort detection rules, and PCAP analysis for red and blue team…
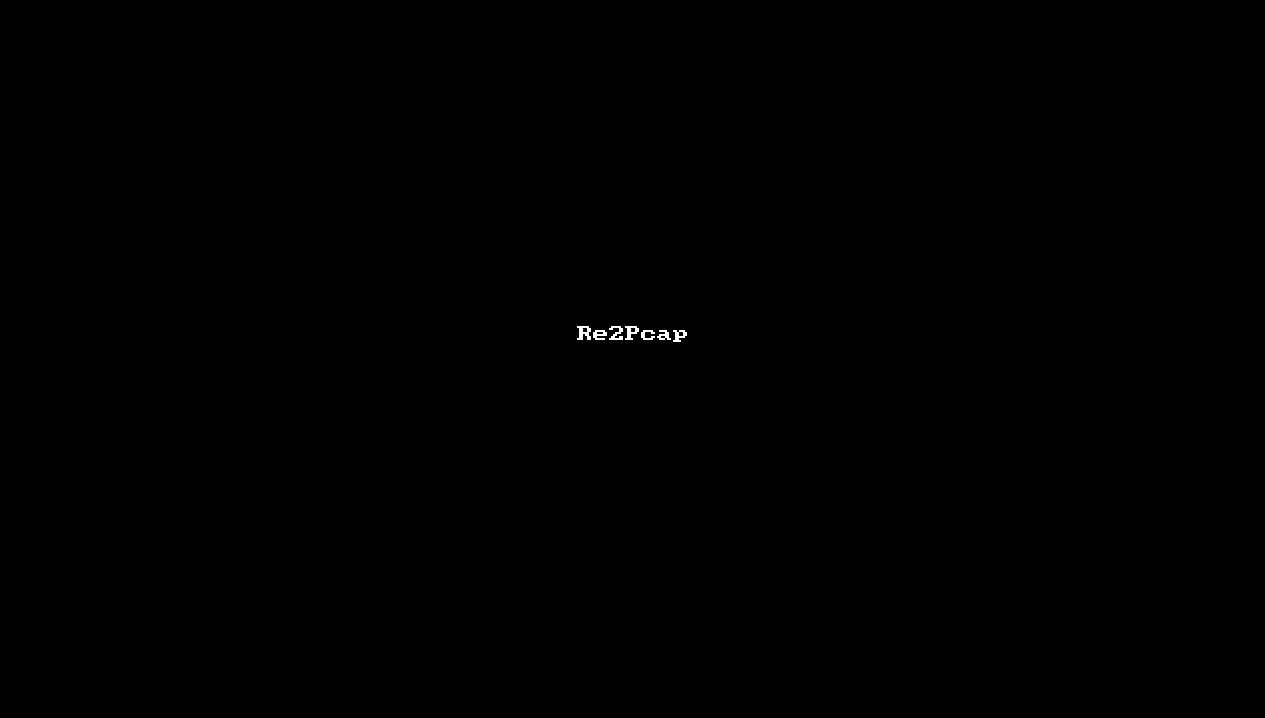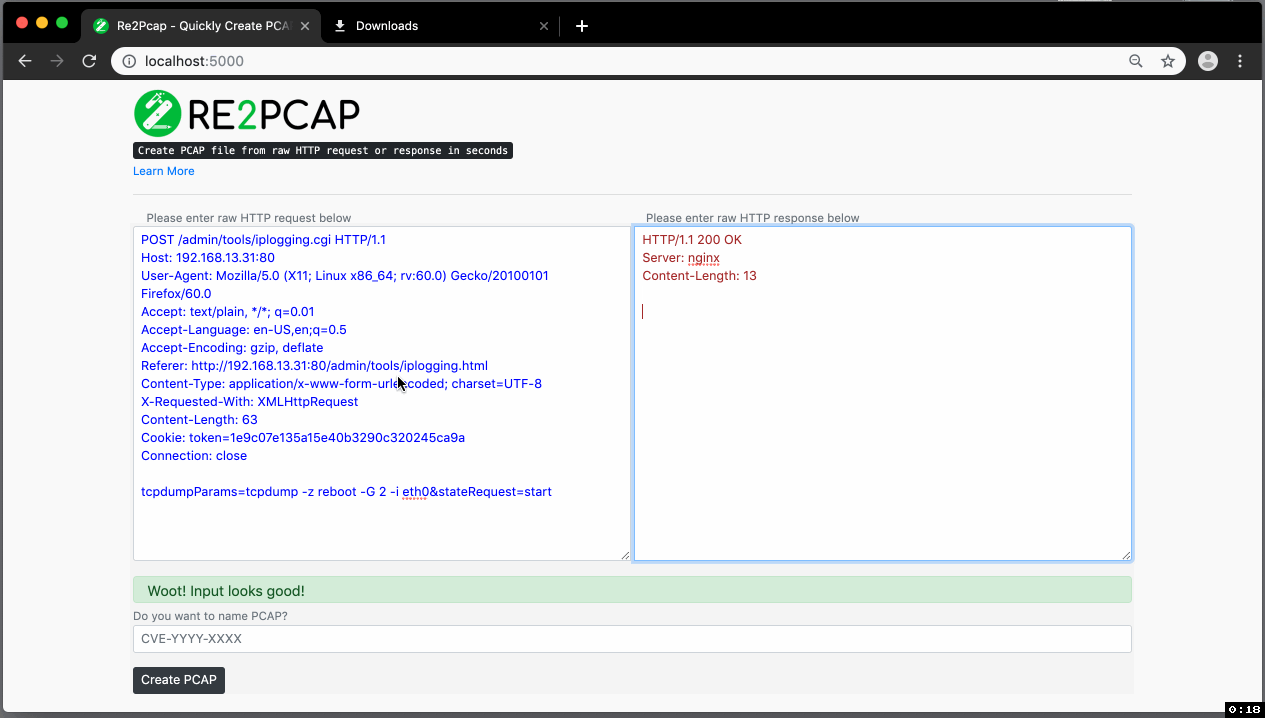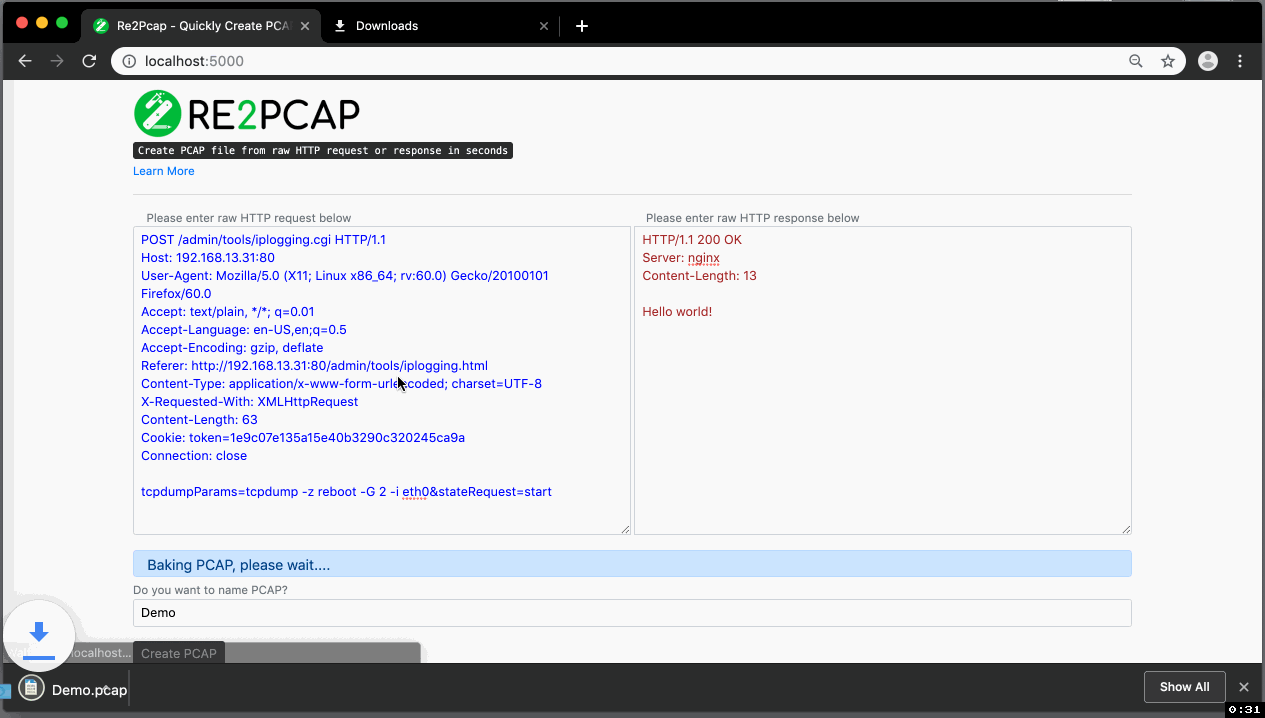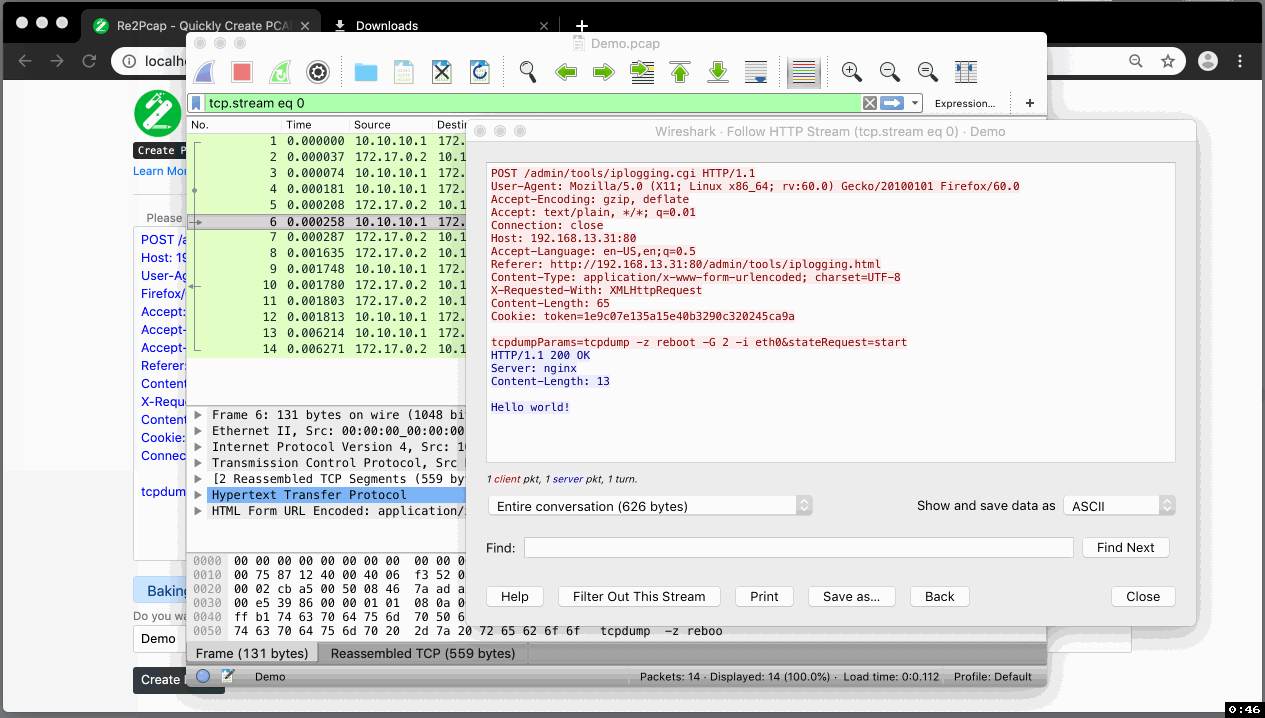 cisco-talos/re2pcap
Convert raw HTTP requests/responses into PCAP files for testing Snort IDS rules and network security analysis. Supports Docker deployment and…
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)