

jadx
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
android-securitybinary-analysisdebuggers+5
51.3k11h 37m ago
skylot/jadxCommand-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 nextdns/nextdns
Command-line DNS-over-HTTPS client and proxy for encrypted, tamper-resistant DNS resolution; works with any DoH provider and supports split-horizon…
 asciimoo/exrex
Irregular methods on regular expressions
 wkovacs64/pwned
CLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
 spamscanner/spamscanner
Spam Scanner is a Node.js anti-spam, email filtering, and phishing prevention tool and service. Built for @ladjs, @forwardemail, @cabinjs, @breejs,…
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
 cleasbycode/jdvrif
Steganography Tool for JPG Images
 vulncheck-oss/cli
VulnCheck's official command line tool
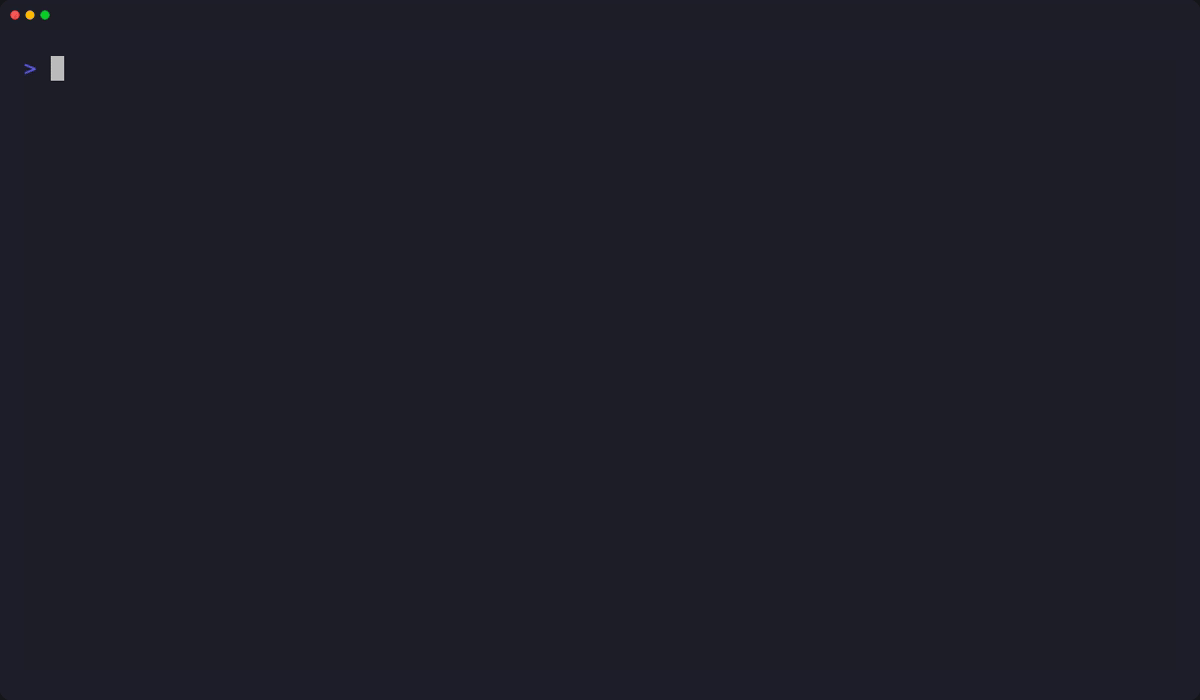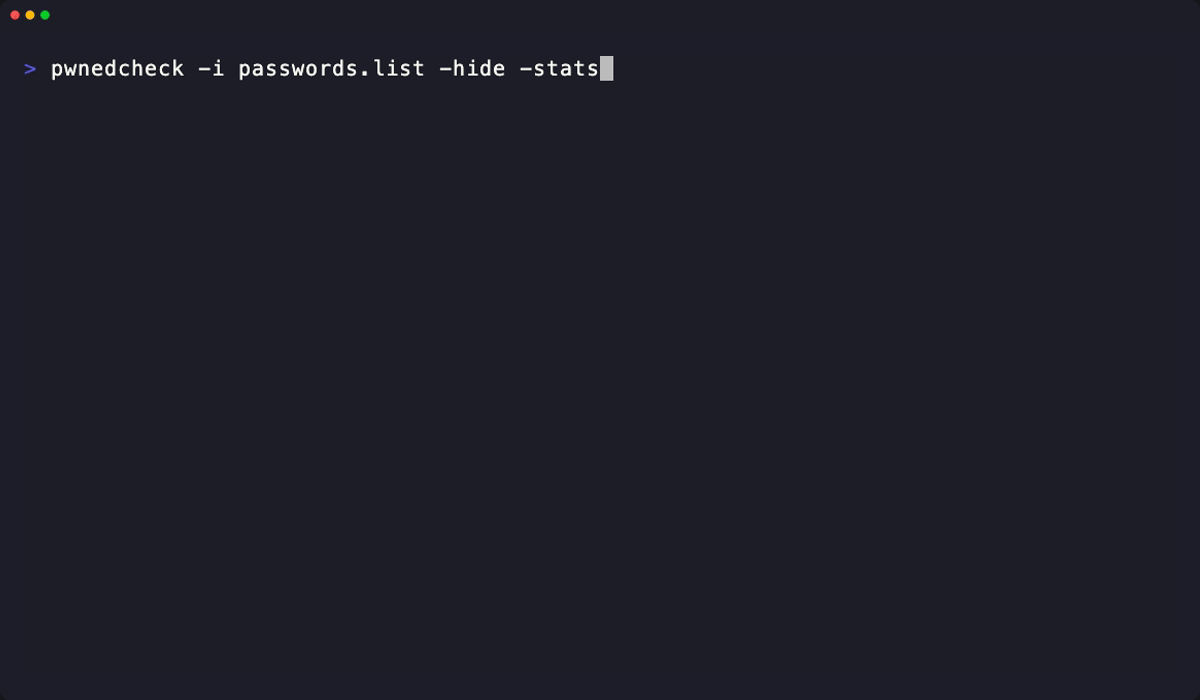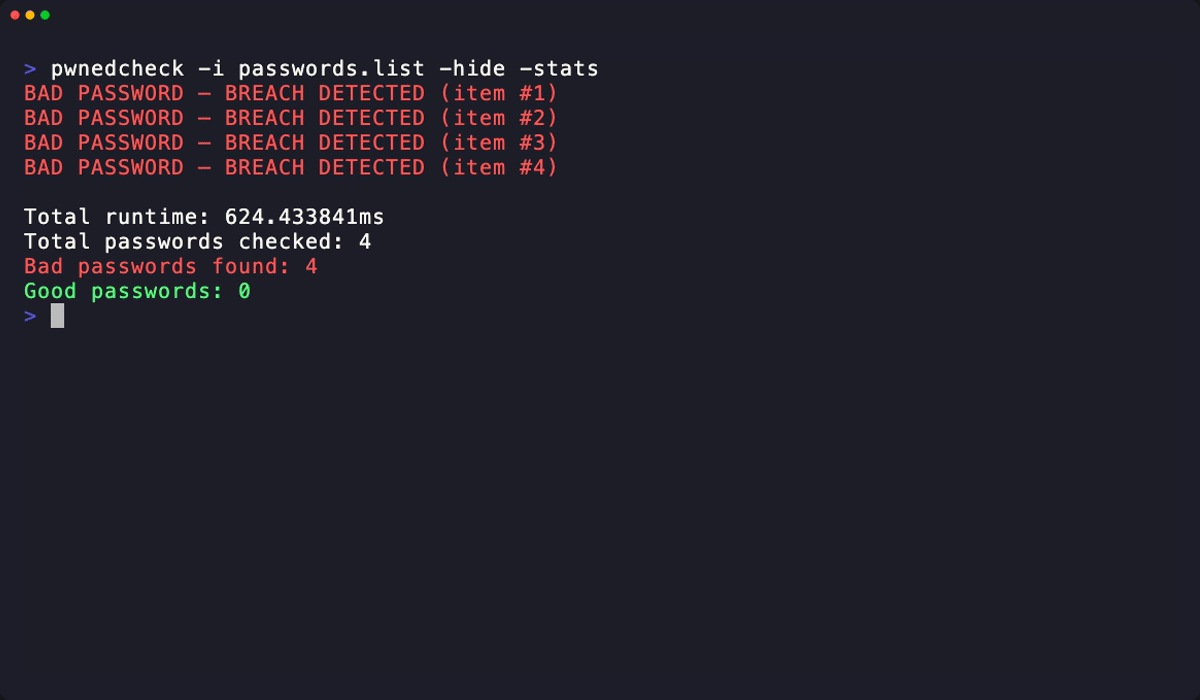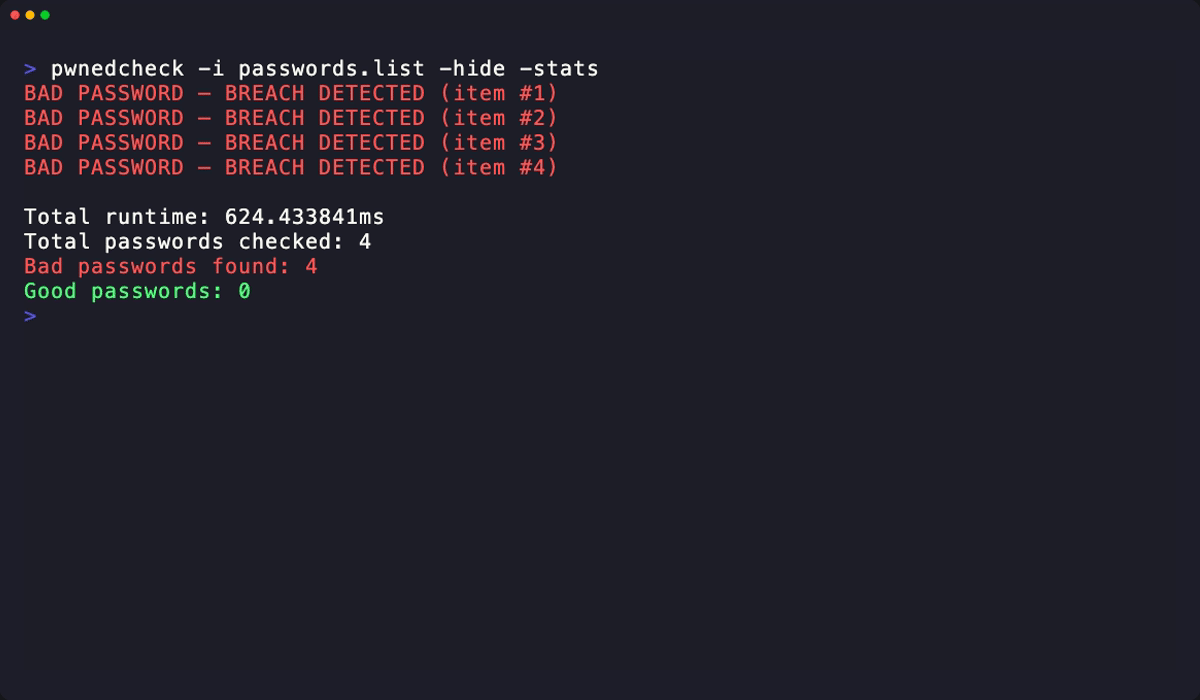 mohamedation/pwnedcheck
A command-line tool to check if passwords have been exposed in data breaches using the Have I Been Pwned (HIBP) API.
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
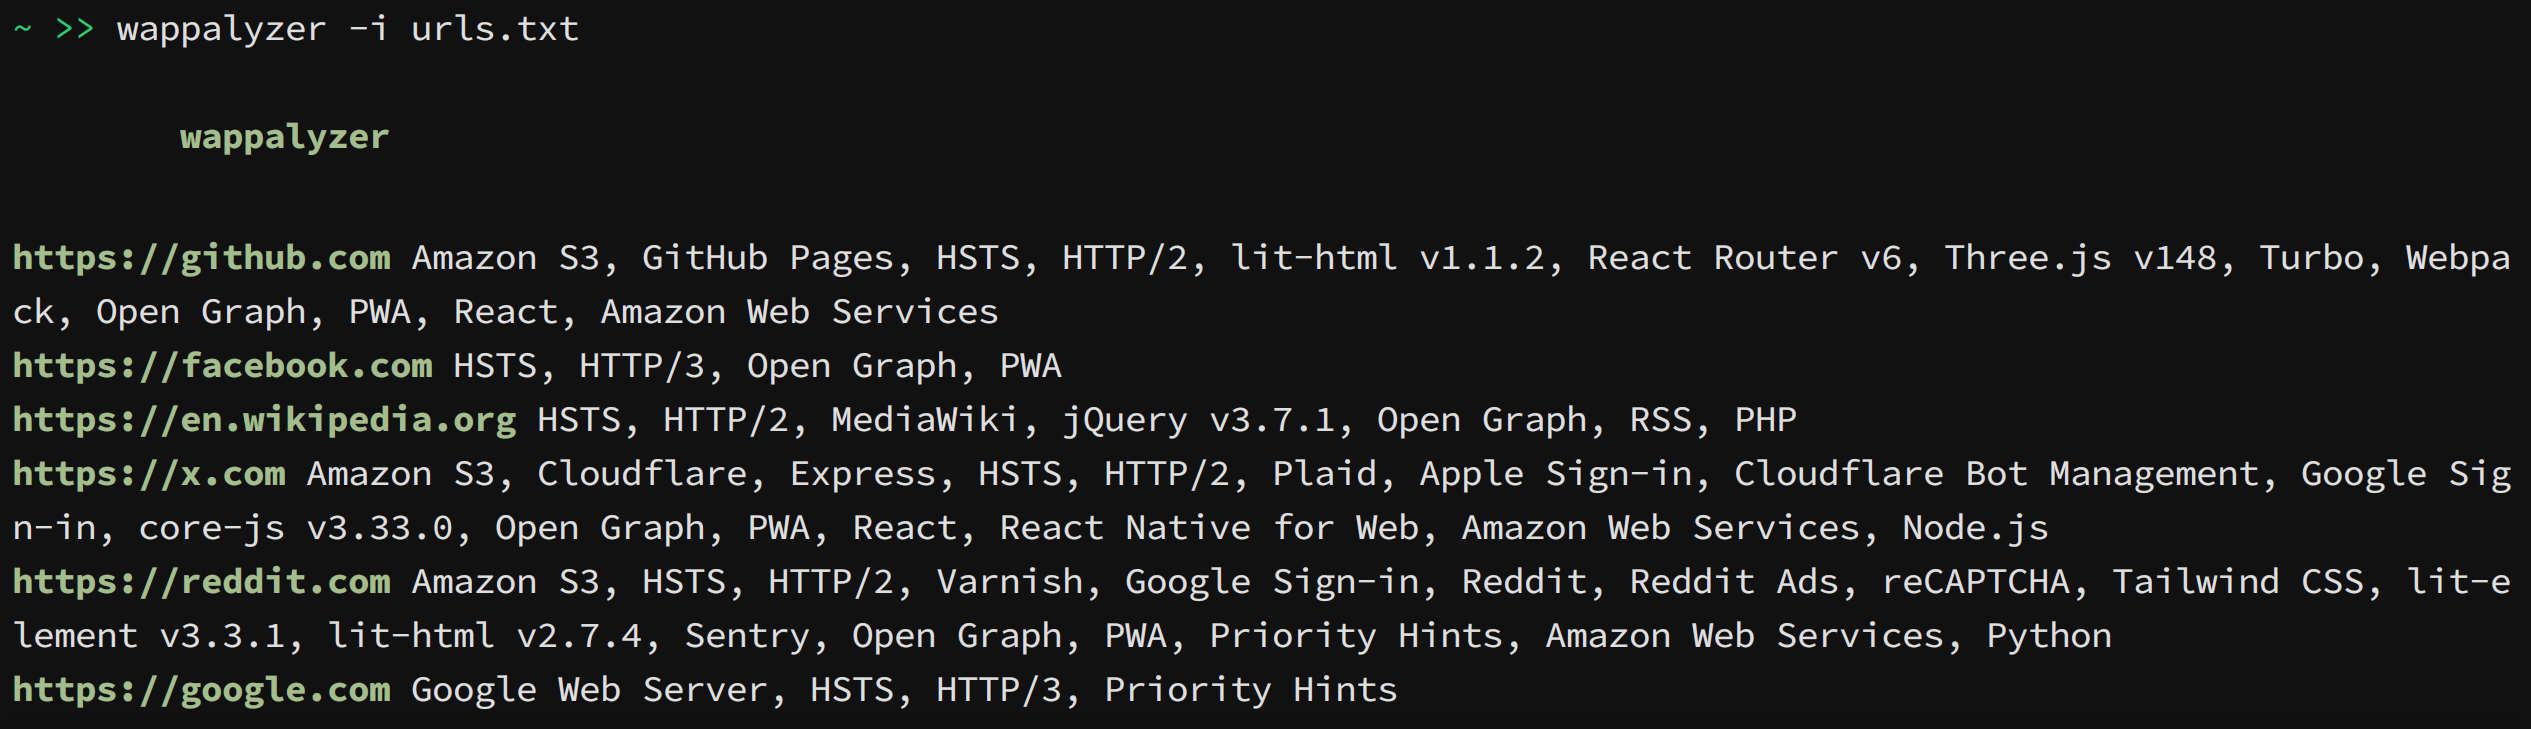 s0md3v/wappalyzer-next
detect technologies with wappalyzer alternative
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 sec-dan/wp2shell-scanner
Read-only CLI to check whether a WordPress site is exposed to WP2Shell (CVE-2026-63030 / CVE-2026-60137)
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
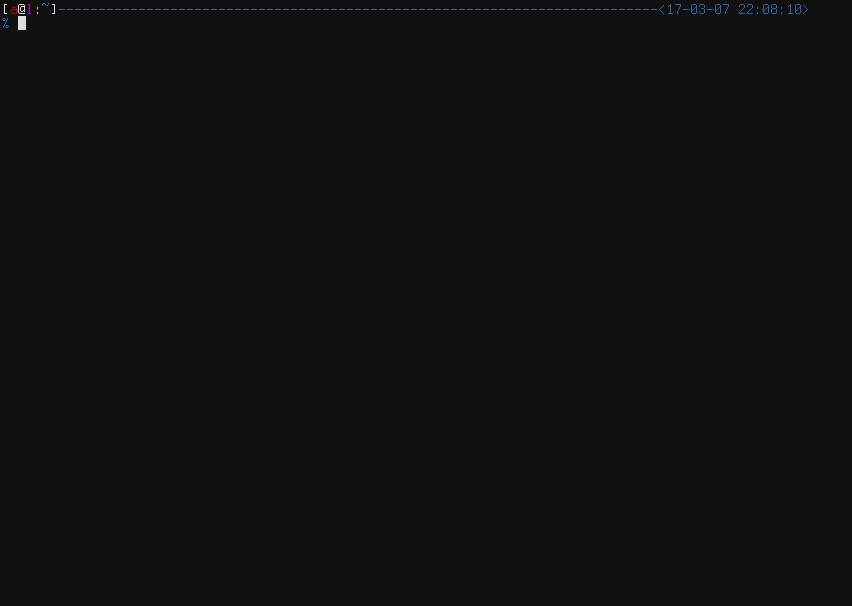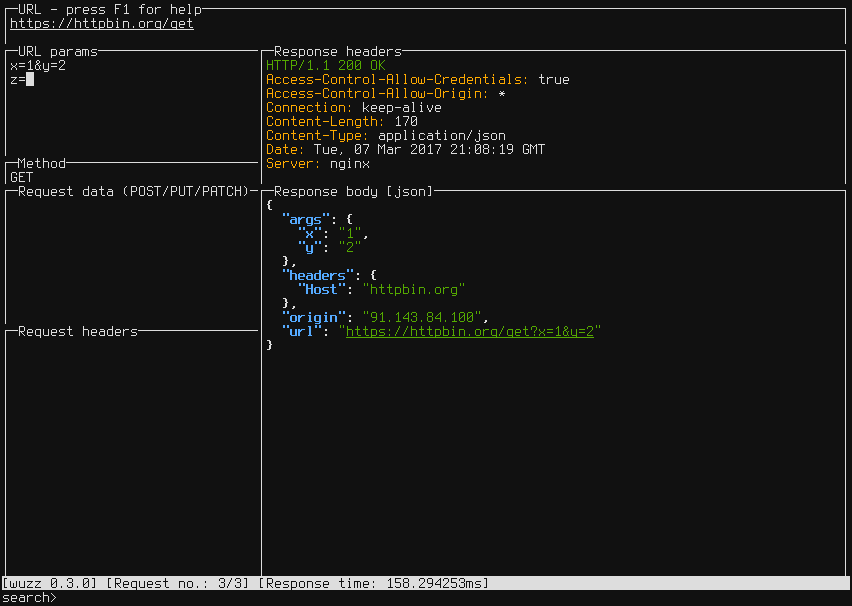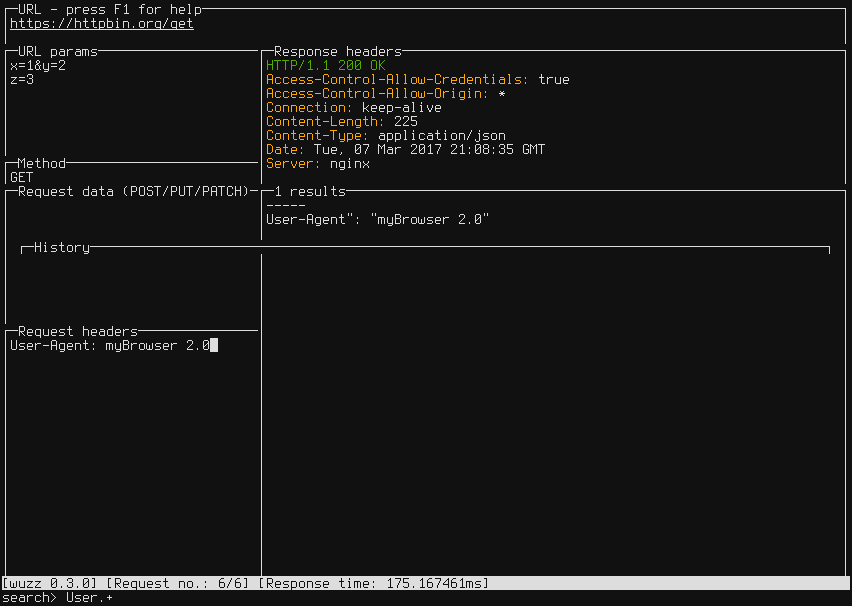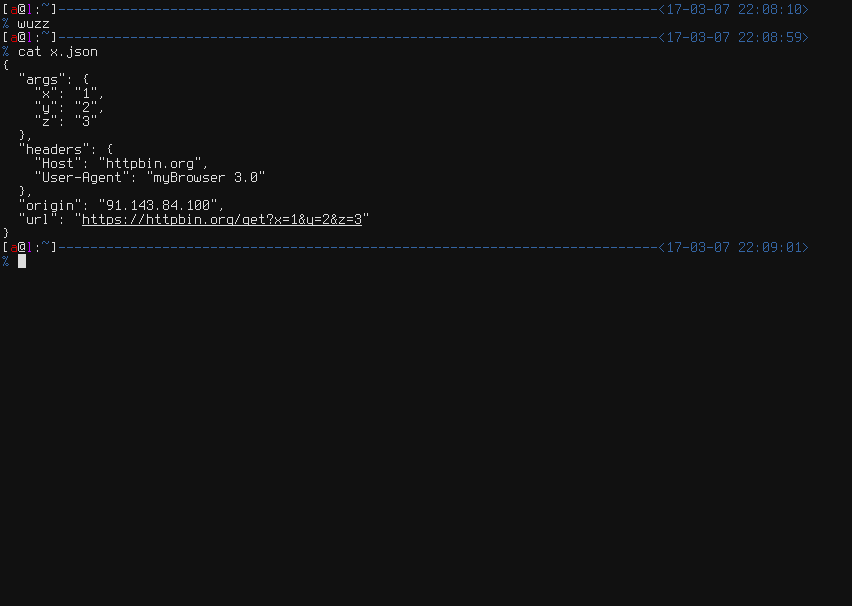 asciimoo/wuzz
Interactive cli tool for HTTP inspection
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78