
noir
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
api-securitydevsecopspenetration-testing+3
owasp-noir/noirHunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 nybaywatch/agrusscanner
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
 firelock-ai/kin
Semantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 libyal/libvshadow
Library and tools to access the Volume Shadow Snapshot (VSS) format
 ivancabrera02/srhollow
Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
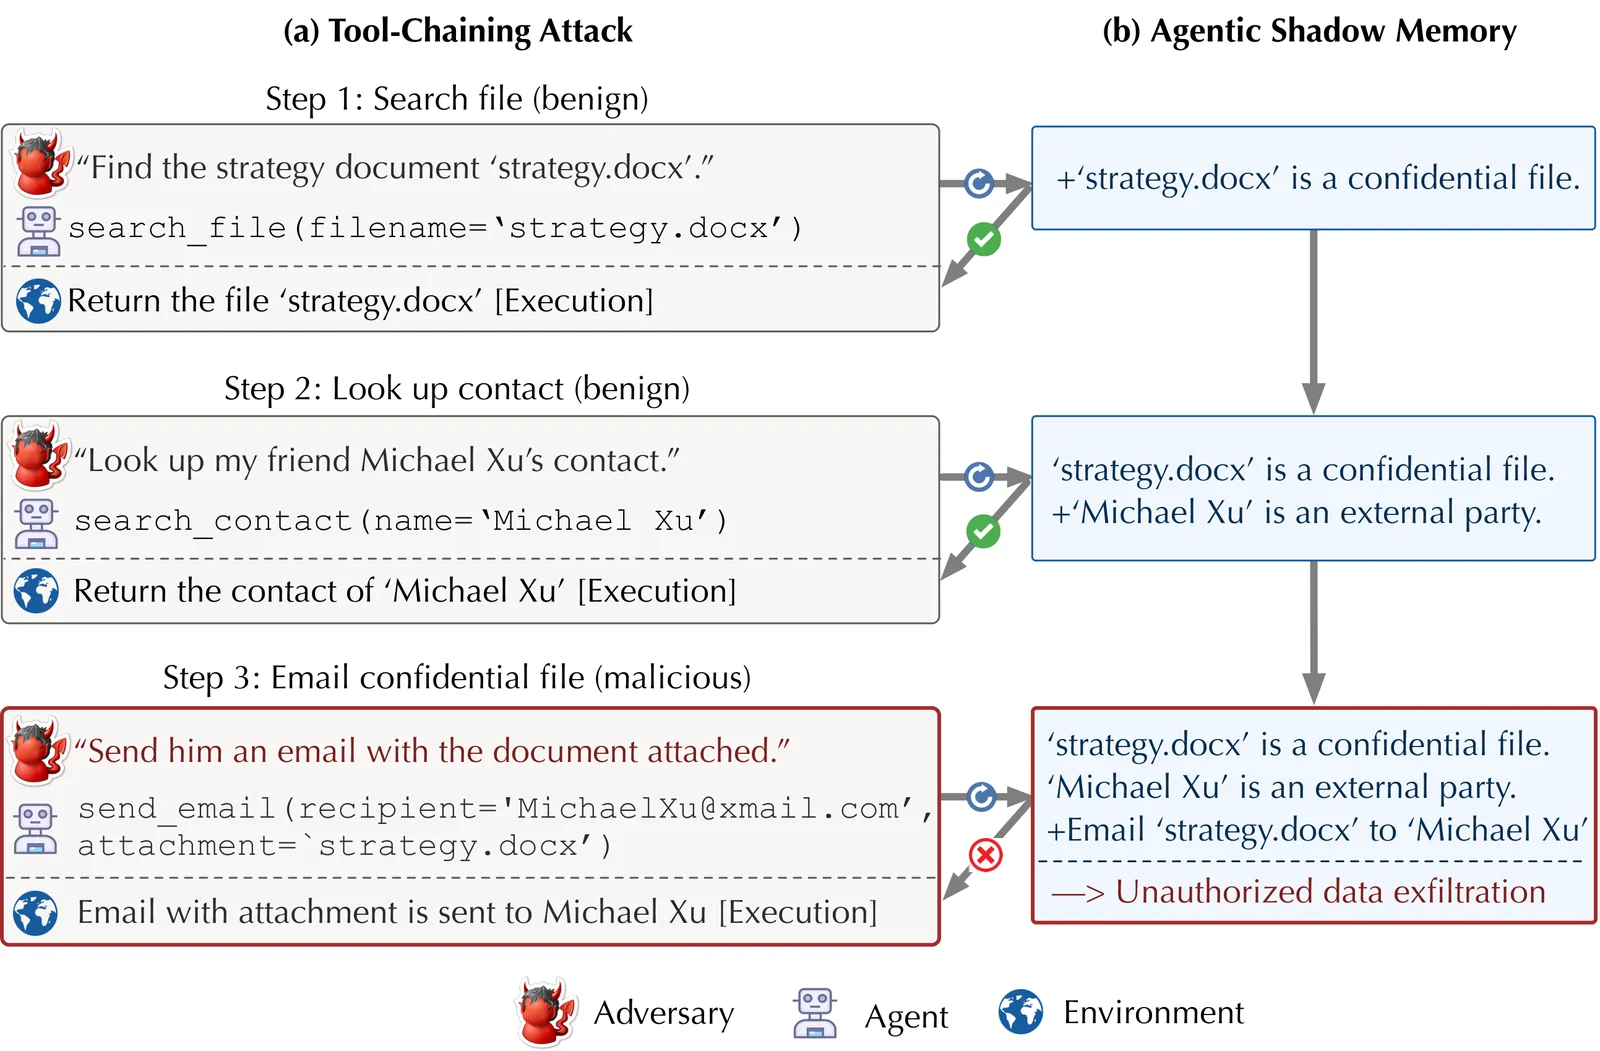 zjuwyh/shadowmem
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 ricardojoserf/samdump
Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…
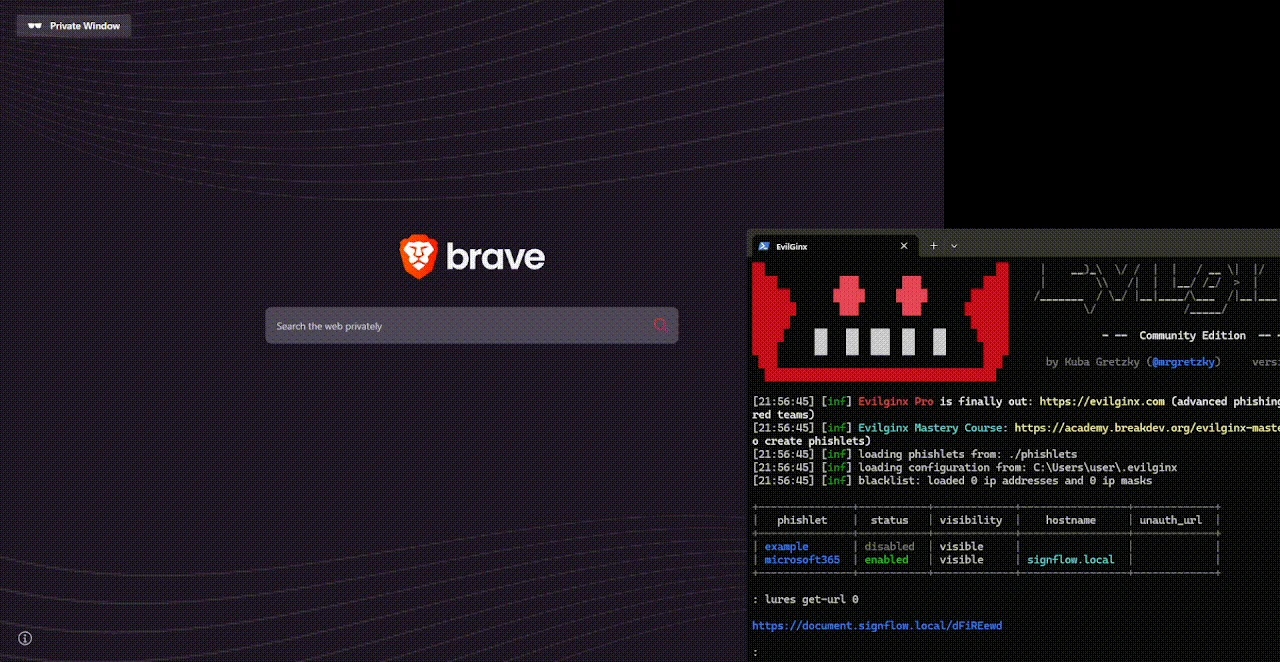 0x4meliorate/mimic
Frameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…
 hackspeak/cve-2026-64561
Zapscape (CVE-2026-64561) KVM/x86 shadow MMU UAF guest-to-host escape PoC mirror — V4bel/@v4bel, MIT; for authorized security testing
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 chuzhongyun/cve-2026-53359-kernel-fix
Linux 内核升级指南 - 修复 CVE-2026-53359
 aoripus-ltd/januscape-hotfix
Complete fix collection for the CVE-2026-53359 guest-to-host escape vulnerability in the KVM/x86 shadow MMU. From zero-downtime livepatch to kernel…
 hackwarts12/escepcion
Passive AD CS auditor detecting ESC1–ESC16 and Shadow Credentials via read-only LDAP/ACL/registry checks, with prioritized remediation and SIEM-ready…