
awesome-ai-security
 ottosulin/awesome-ai-security
A collection of awesome resources related AI security
adversarial-attackai-securitycurated-resources+6
1.5k
ottosulin/awesome-ai-securityA collection of awesome resources related AI security
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 owasp/www-community
OWASP Community Pages are a place where OWASP can accept community contributions for security-related content.
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 dependencytrack/dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 microsoft/agent-governance-toolkit
Policy enforcement, zero-trust identity, execution sandboxing, and audit logging for autonomous AI agents. Covers 10/10 OWASP Agentic Top 10 with…
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
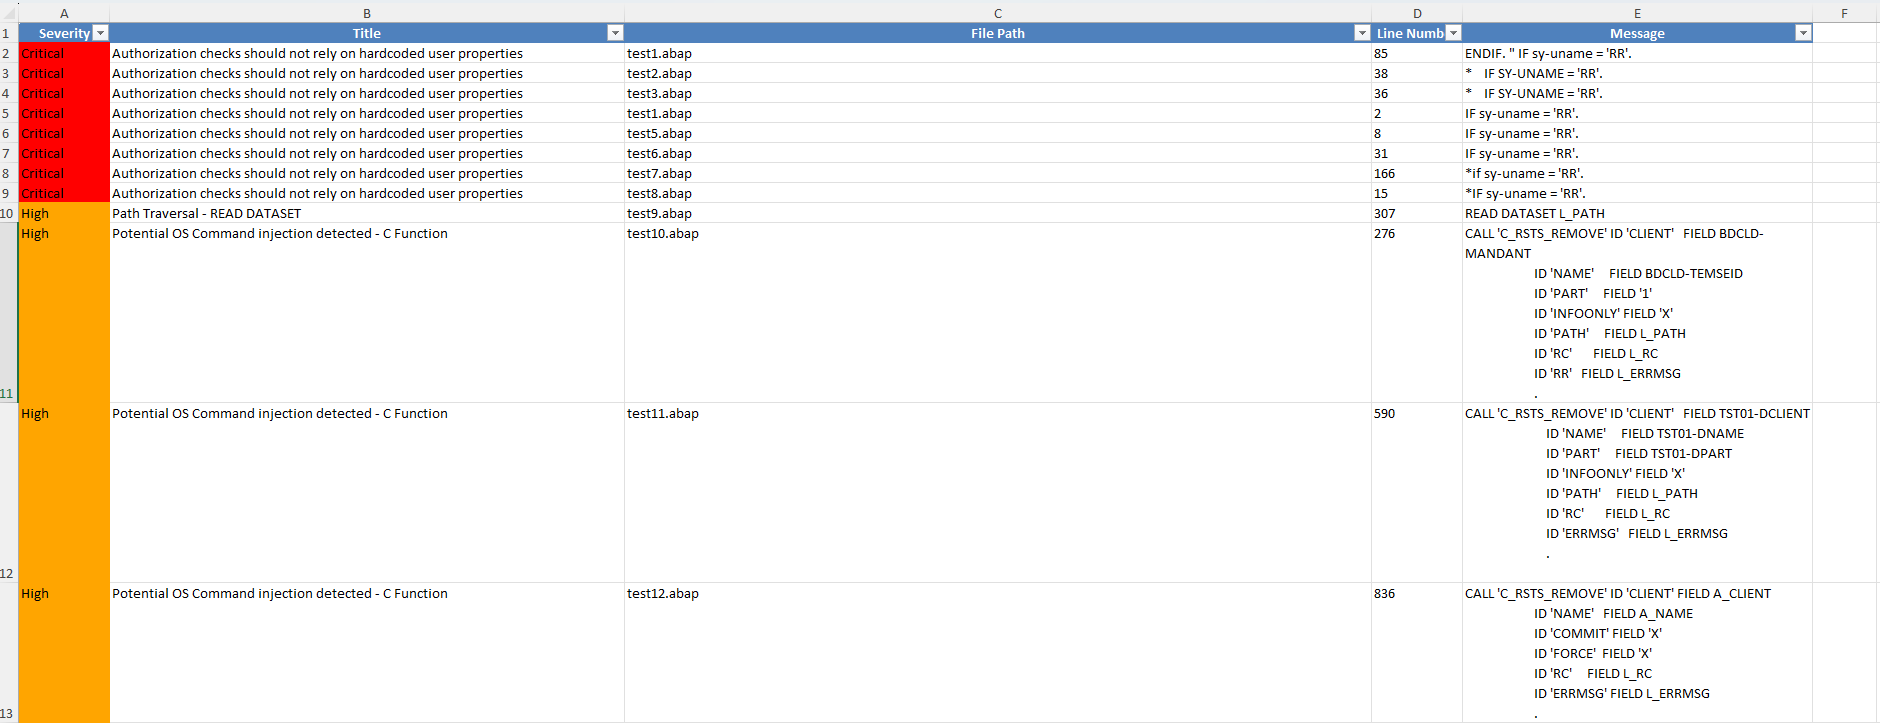
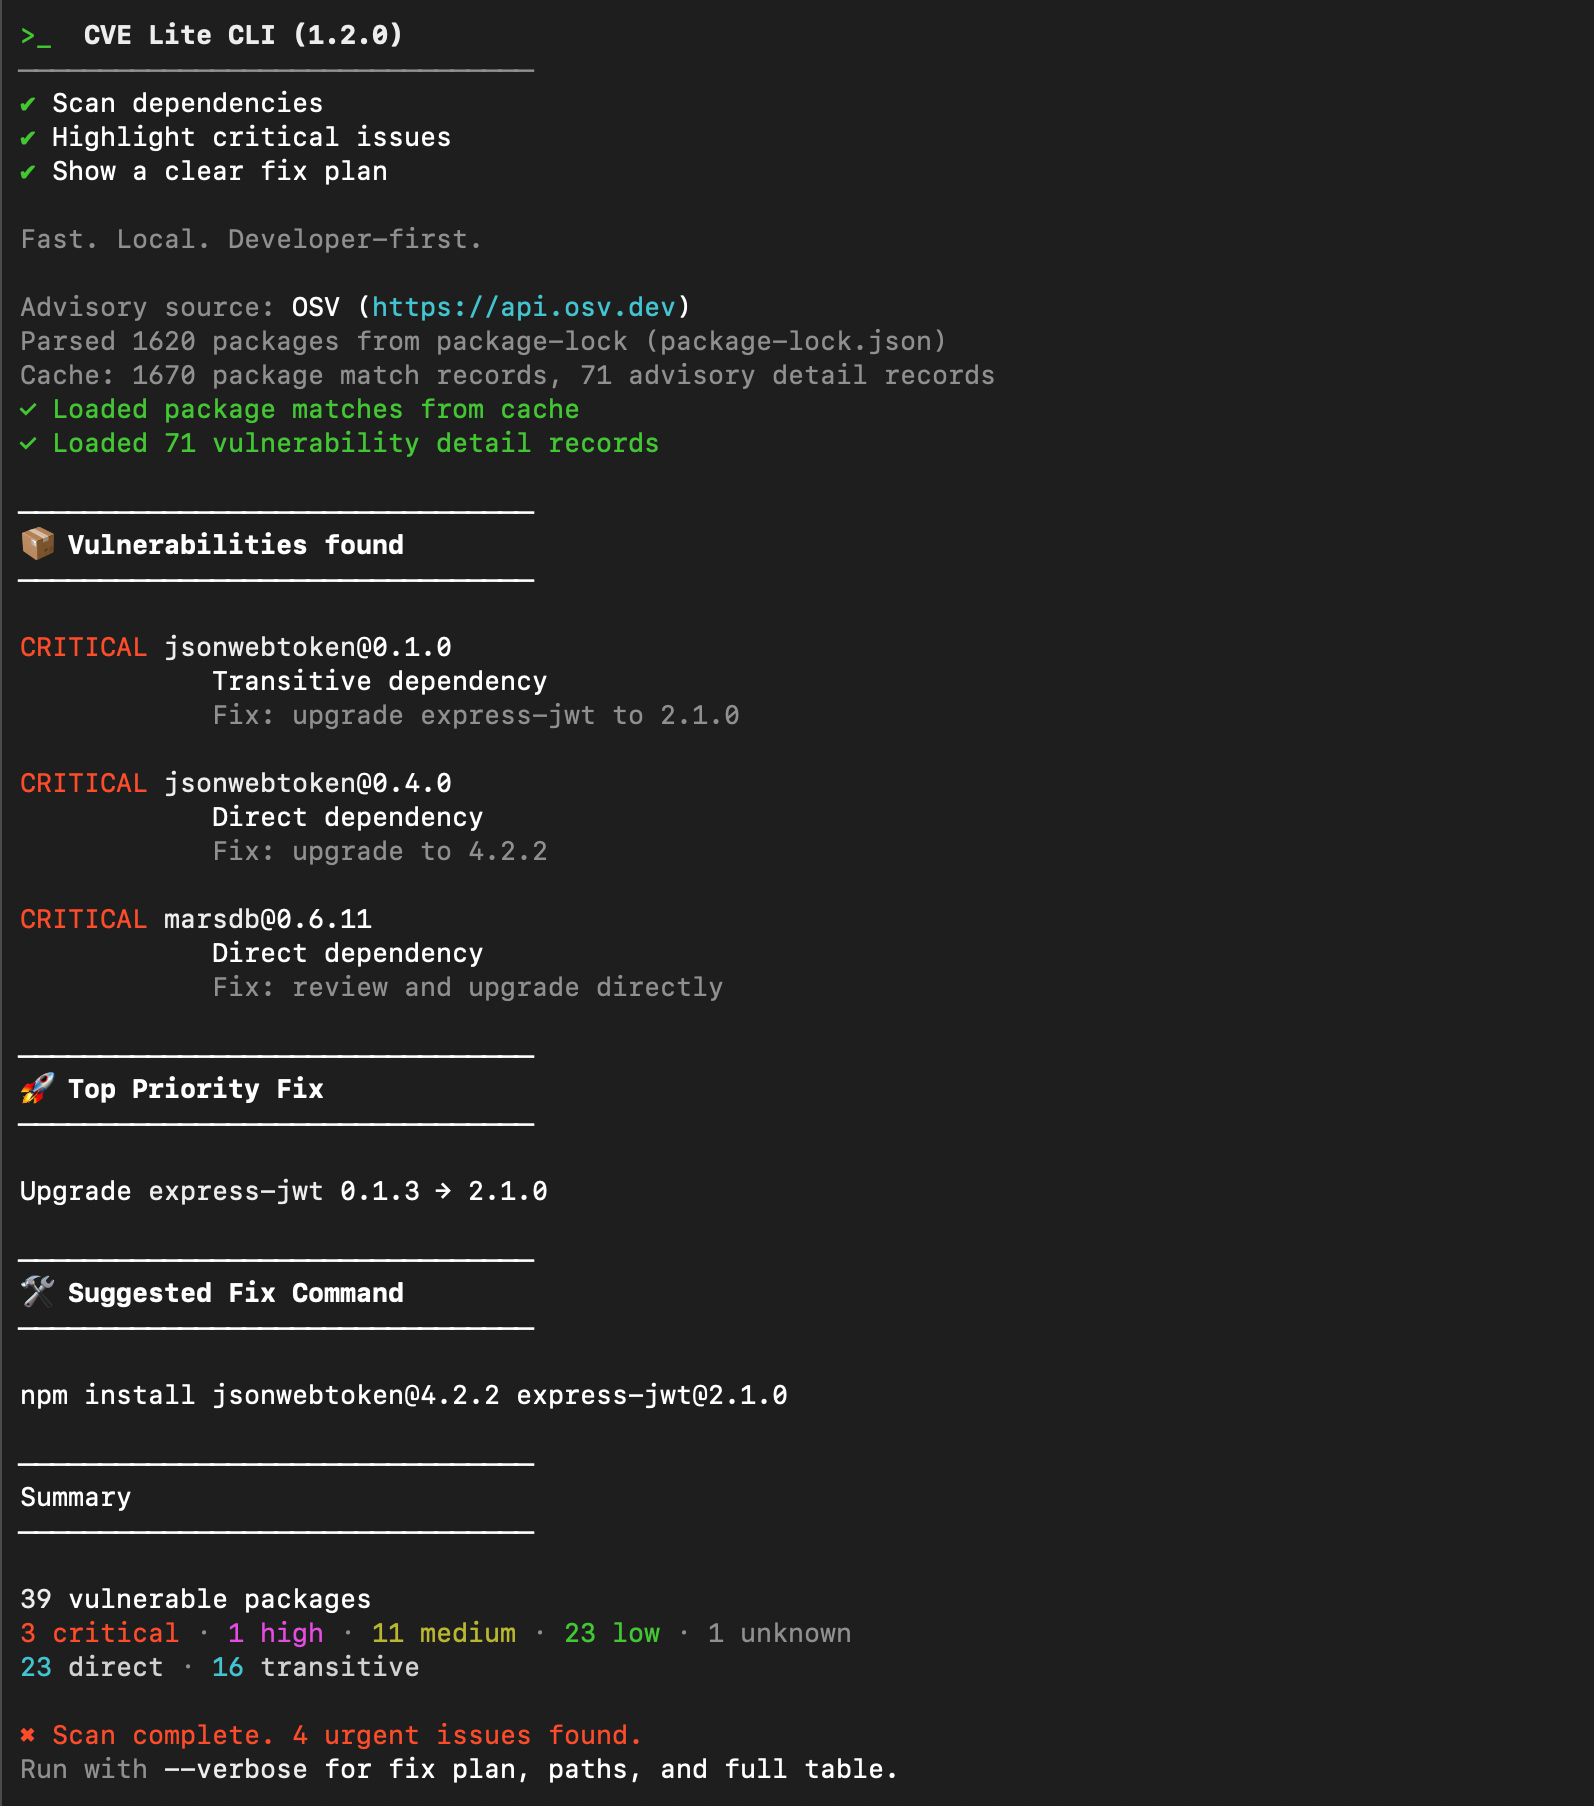 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.