Open-Source-Threat-Intel-Feeds

A curated collection of free and publicly available Open Source Threat Intelligence feeds, covering IP addresses, domains, URLs, file hashes, CVEs,…

A curated collection of free and publicly available Open Source Threat Intelligence feeds, covering IP addresses, domains, URLs, file hashes, CVEs,…

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…

Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…

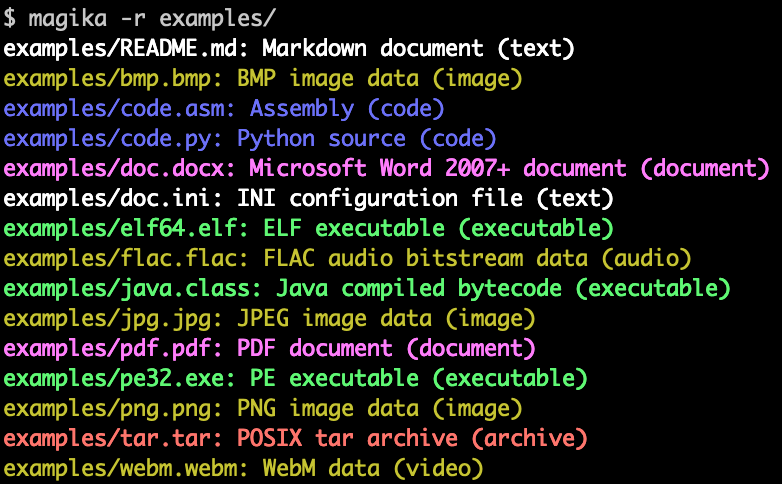
Fast and accurate AI powered file content types detection

This repository contains a list of new remediation scripts.

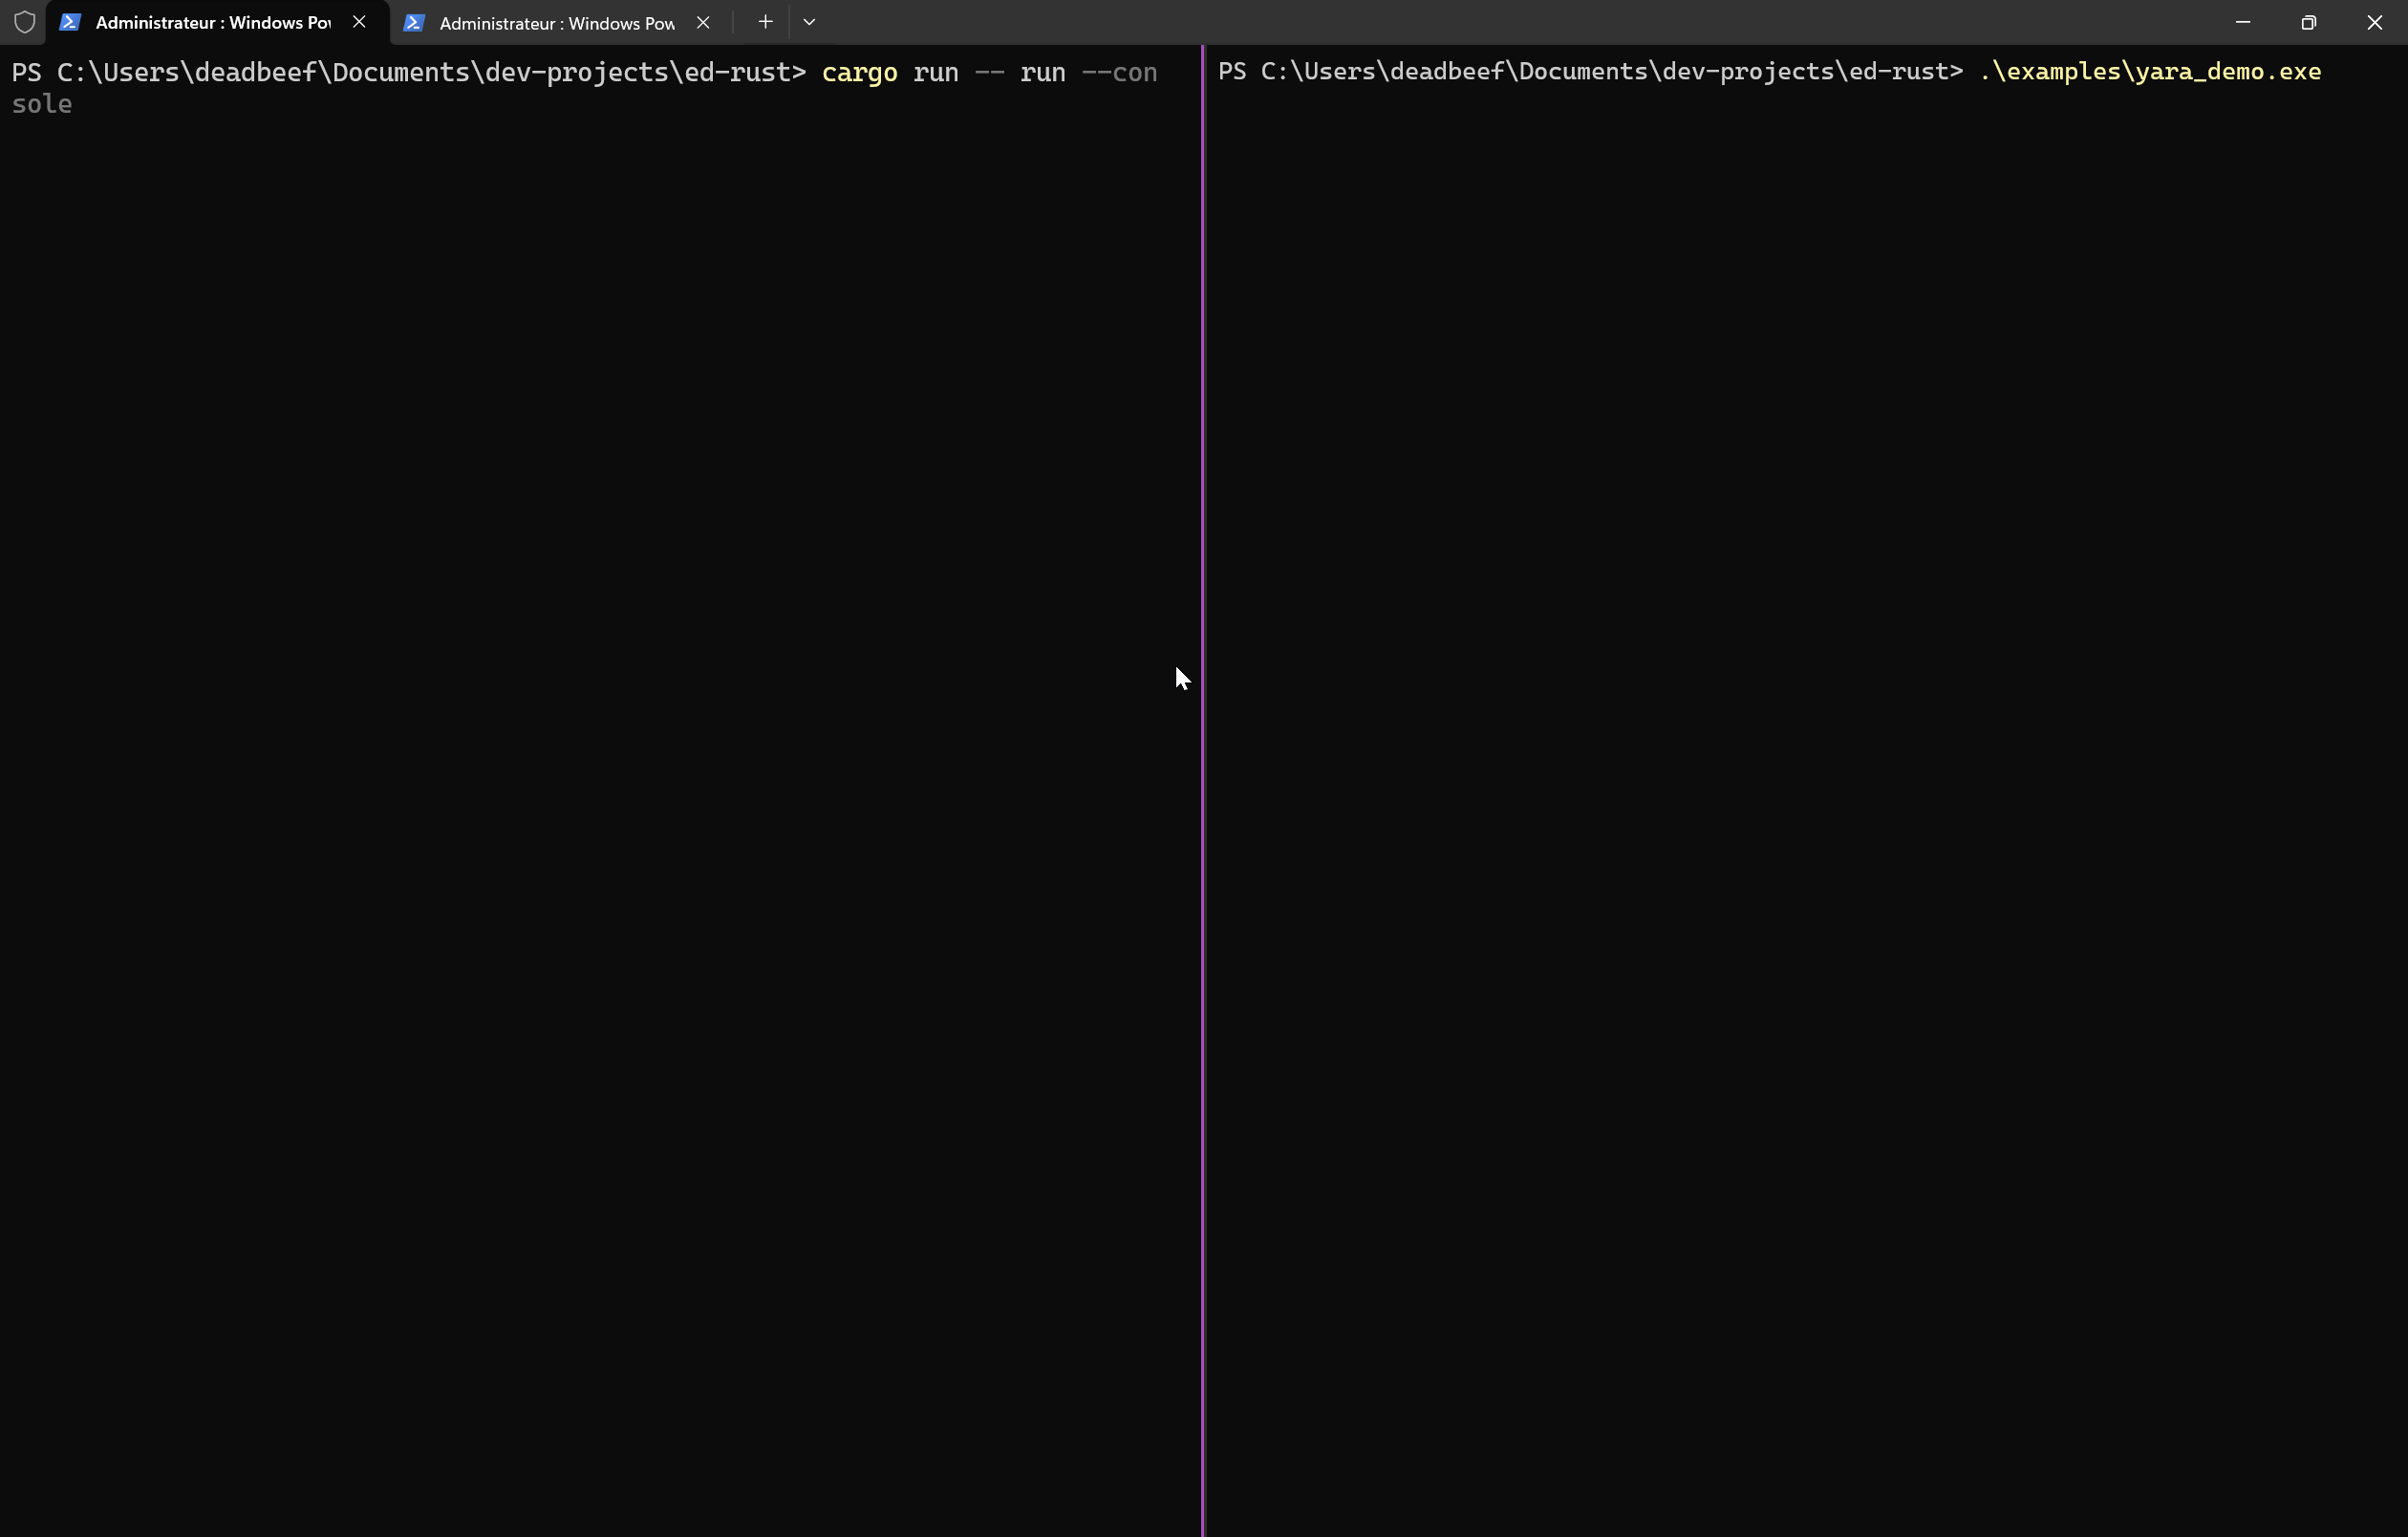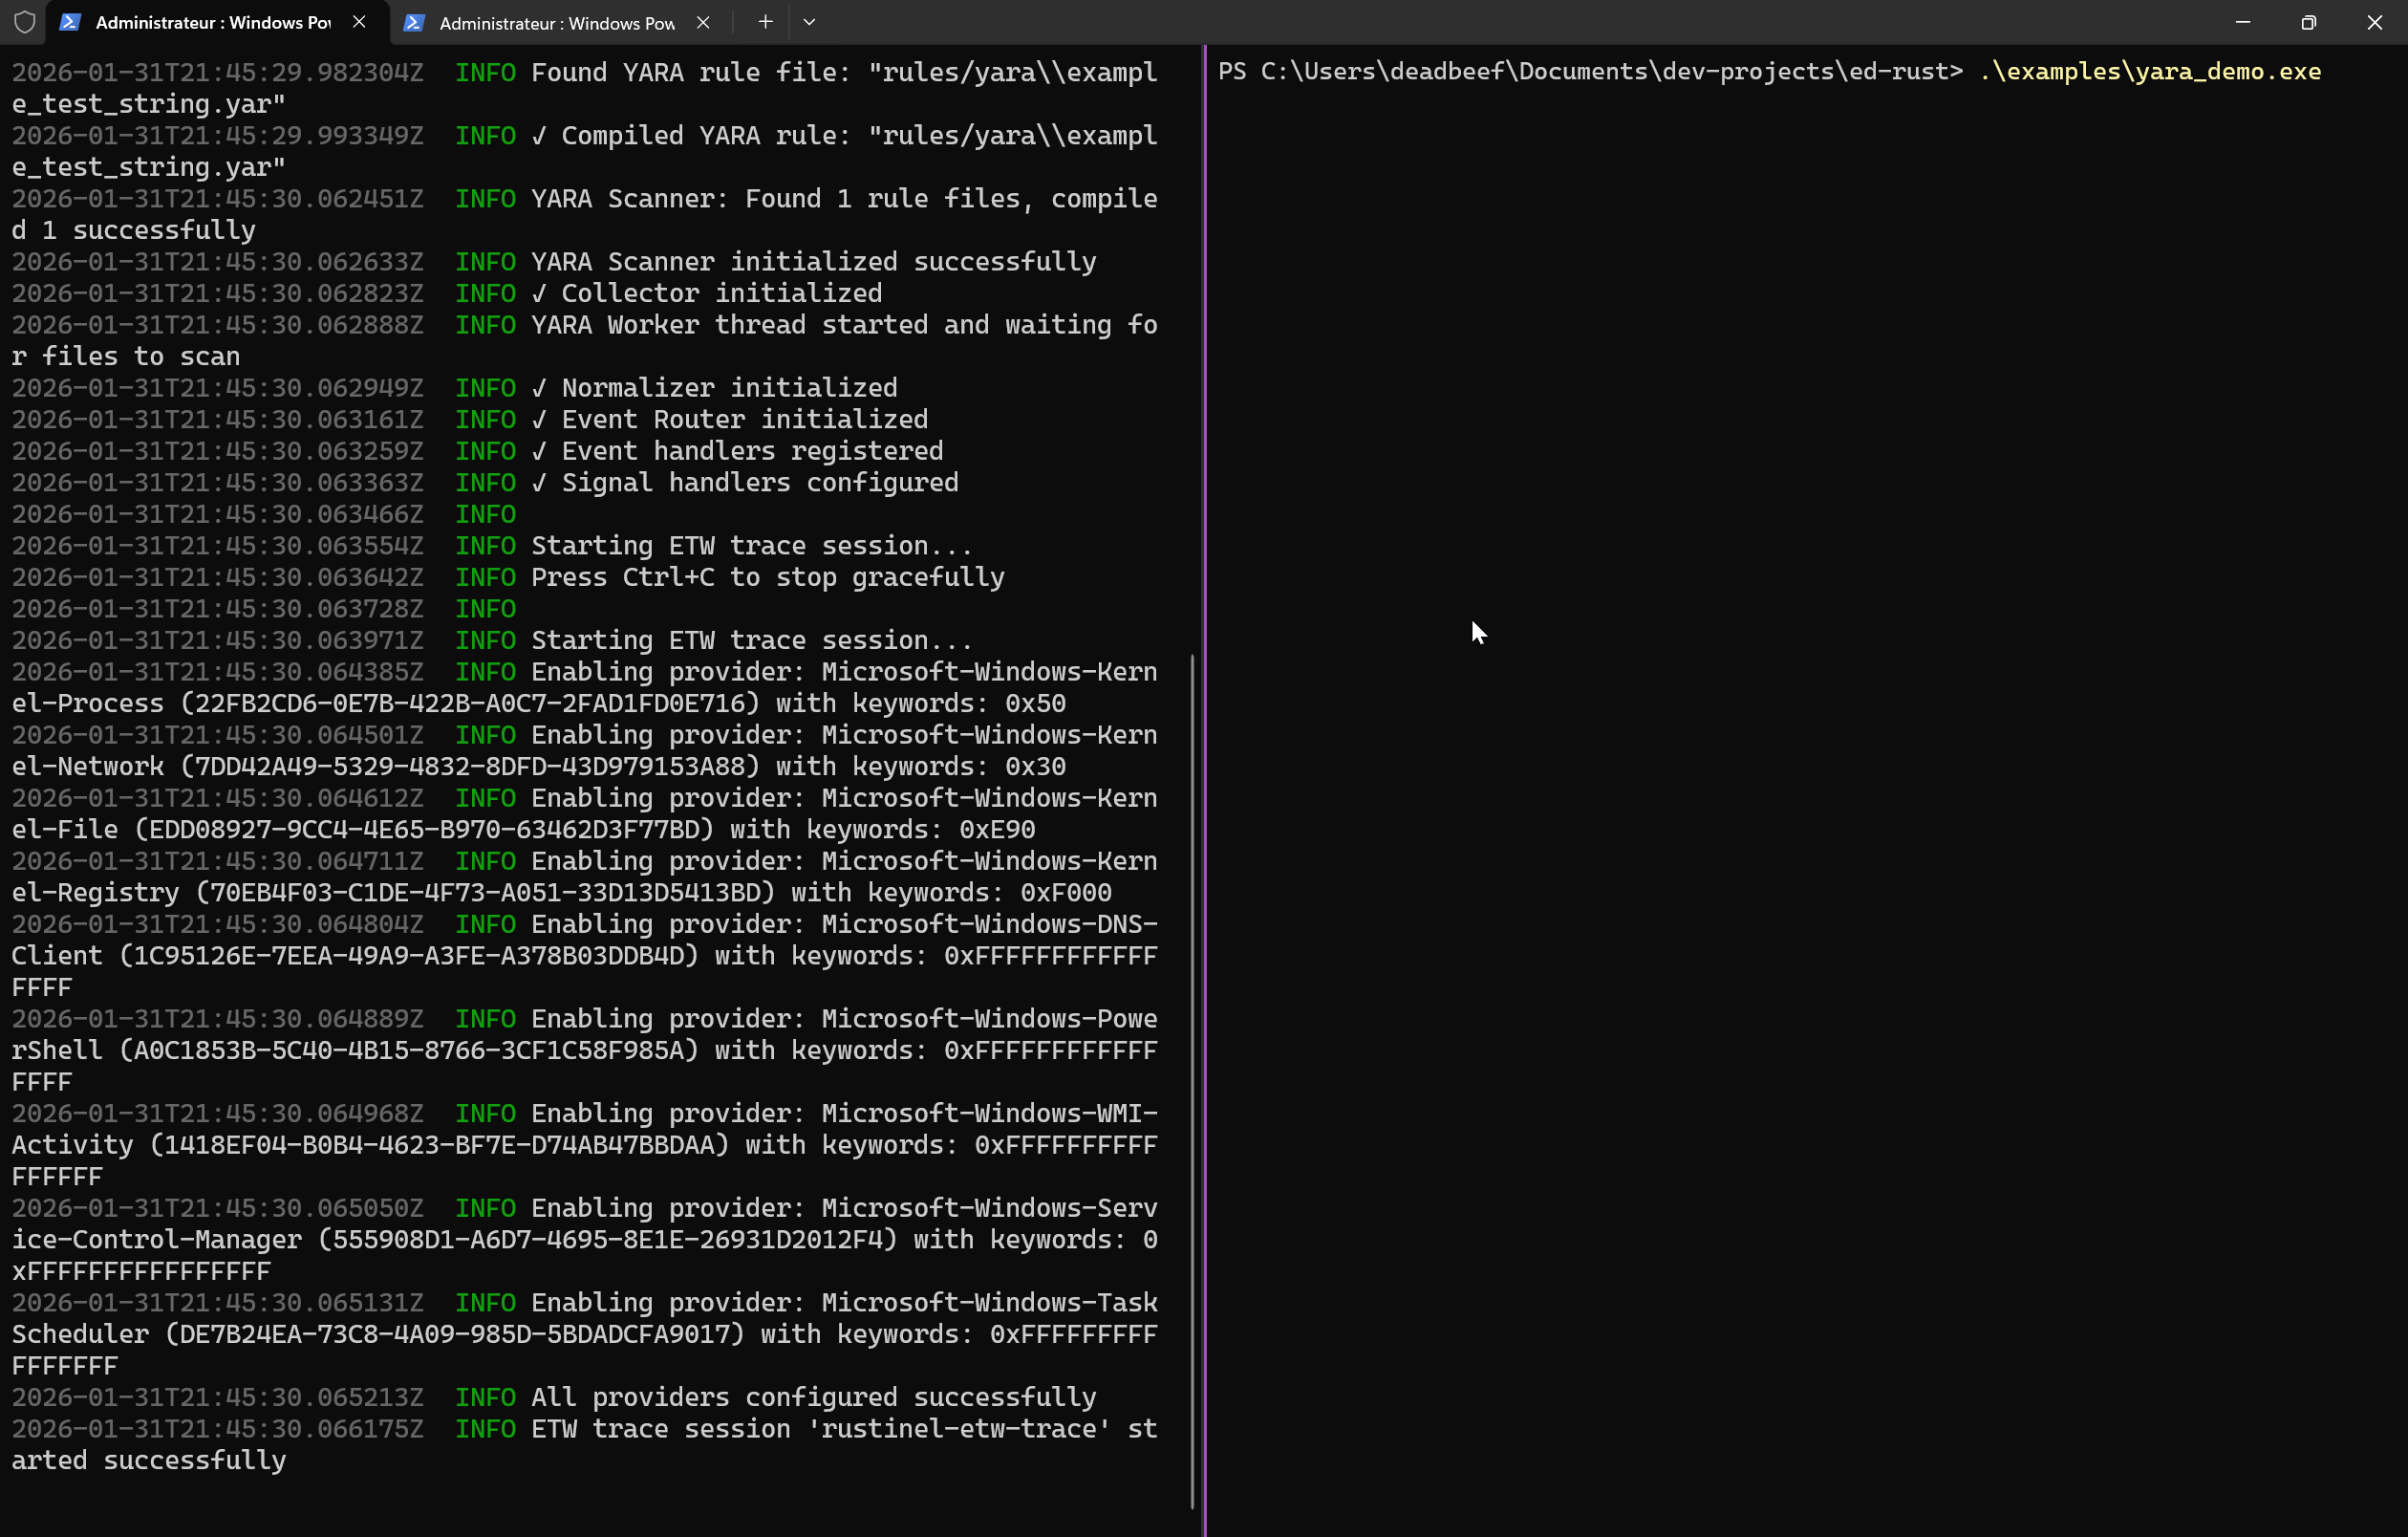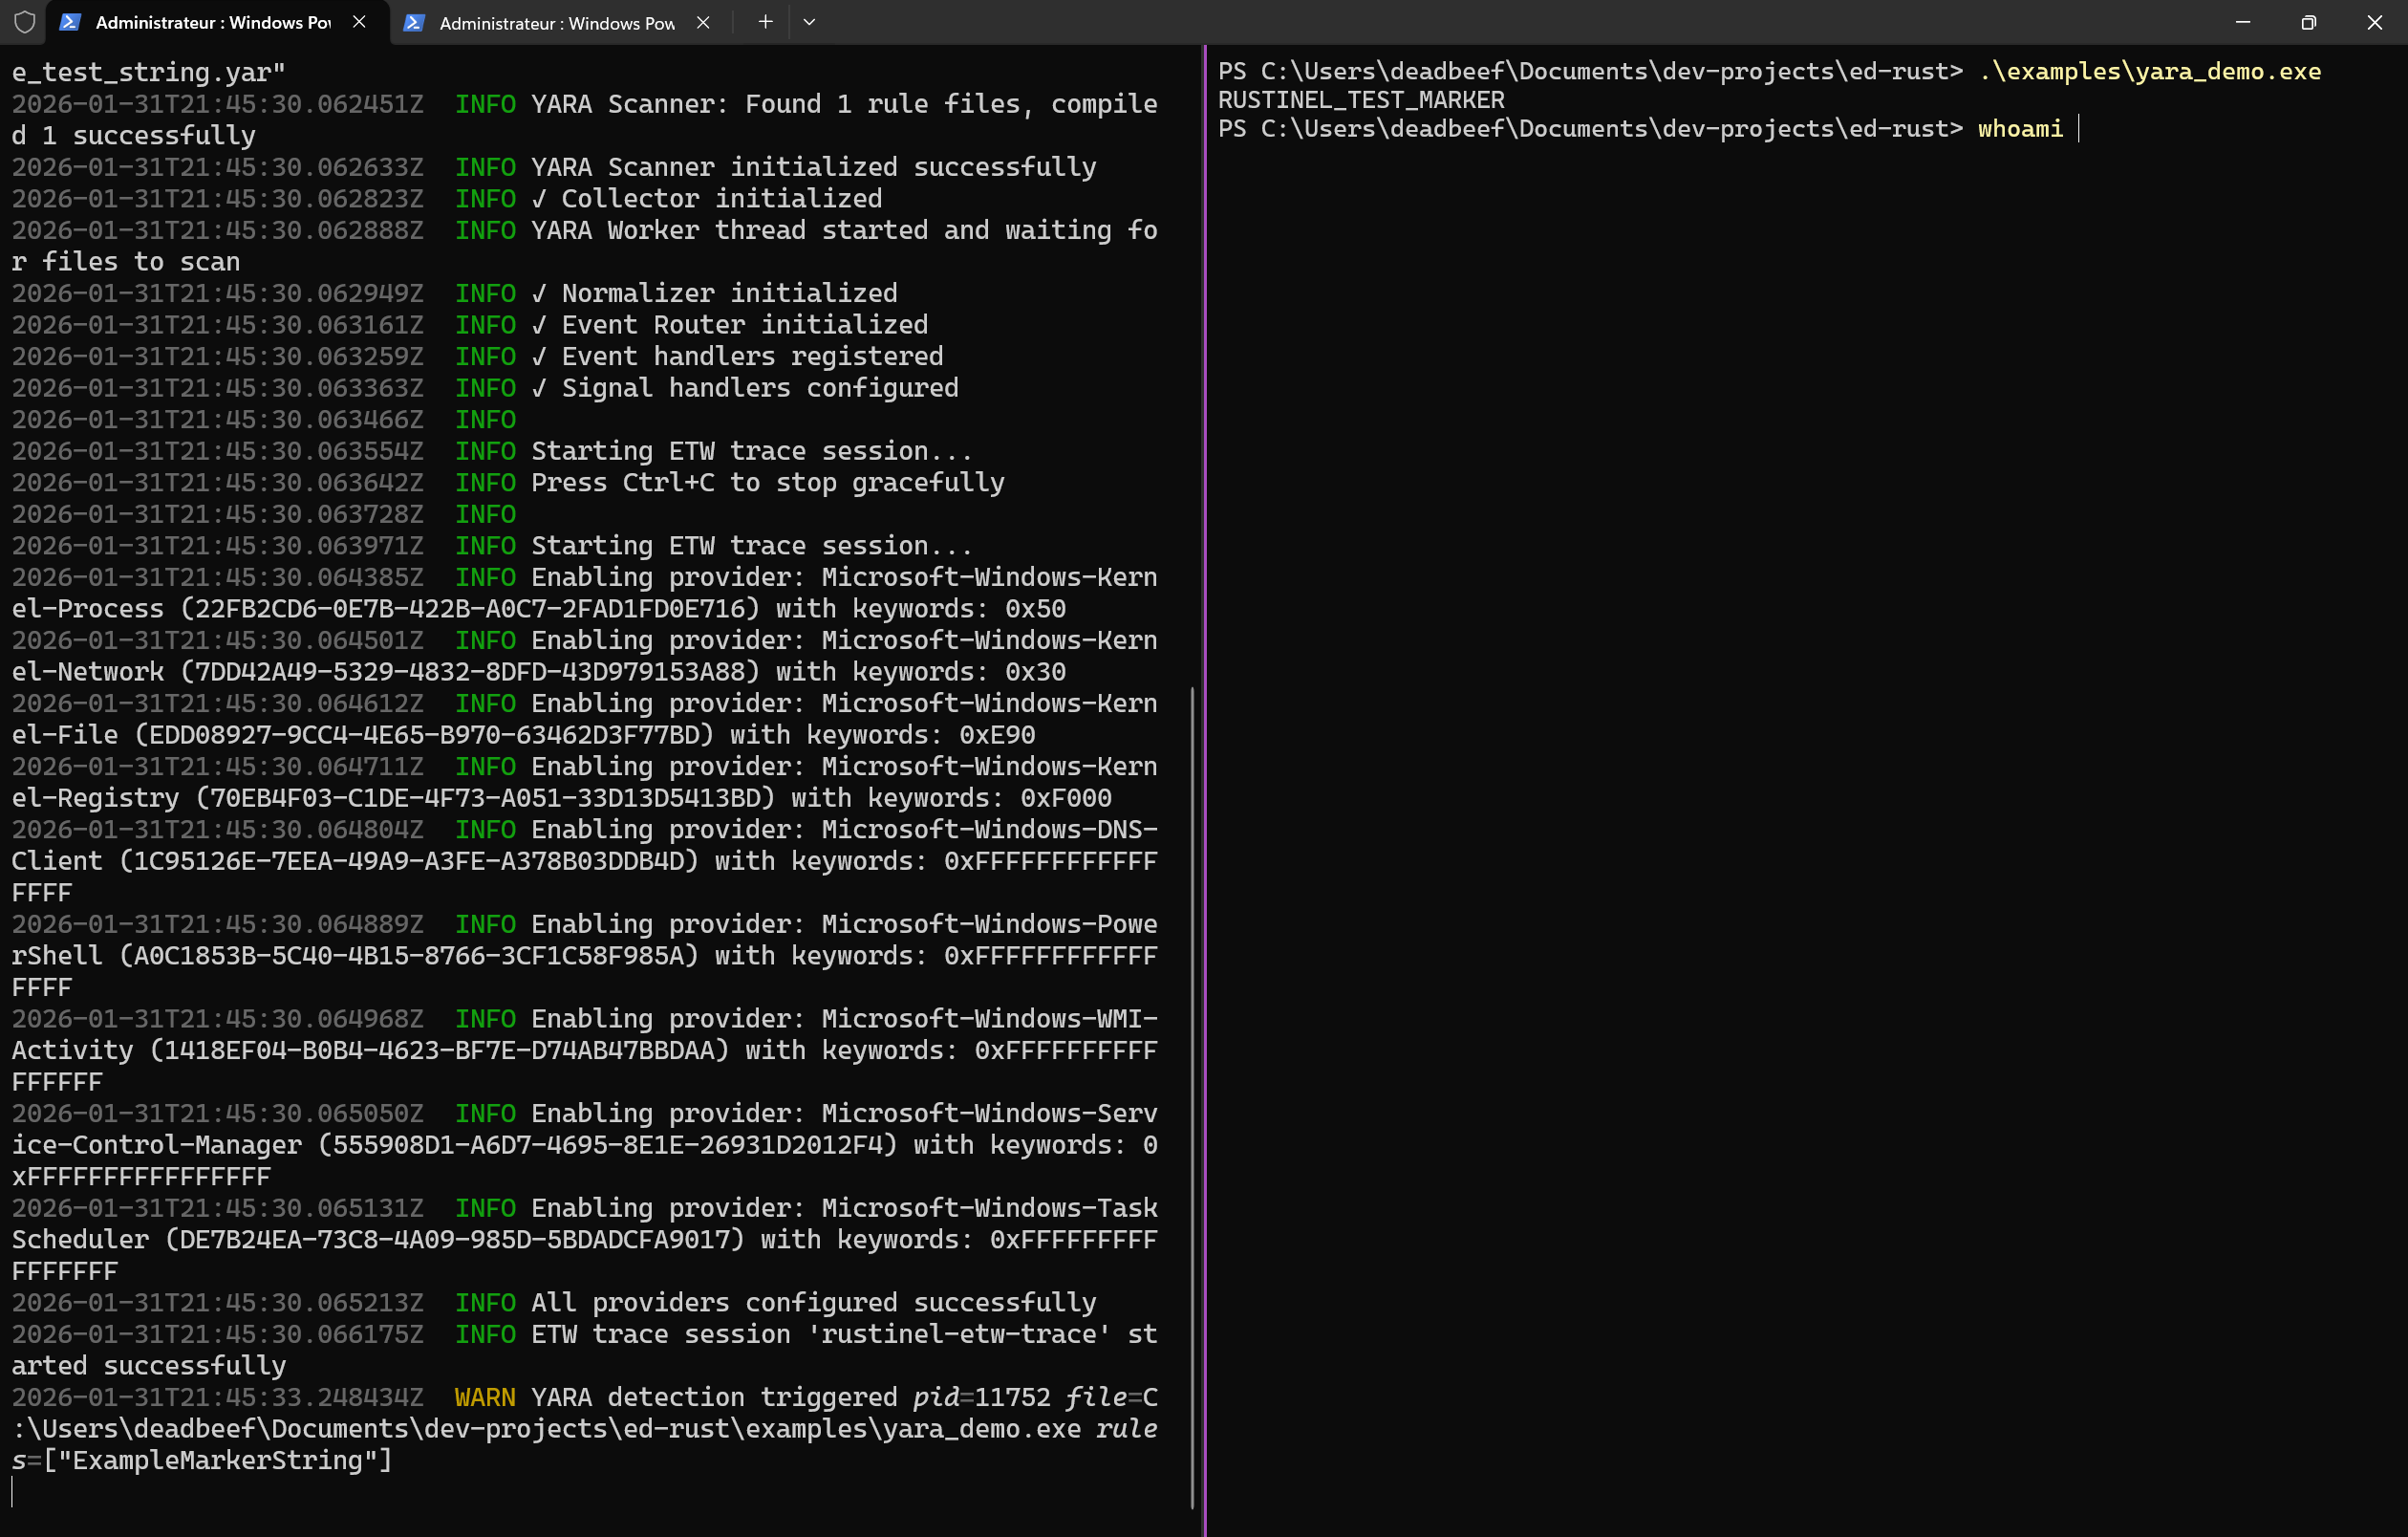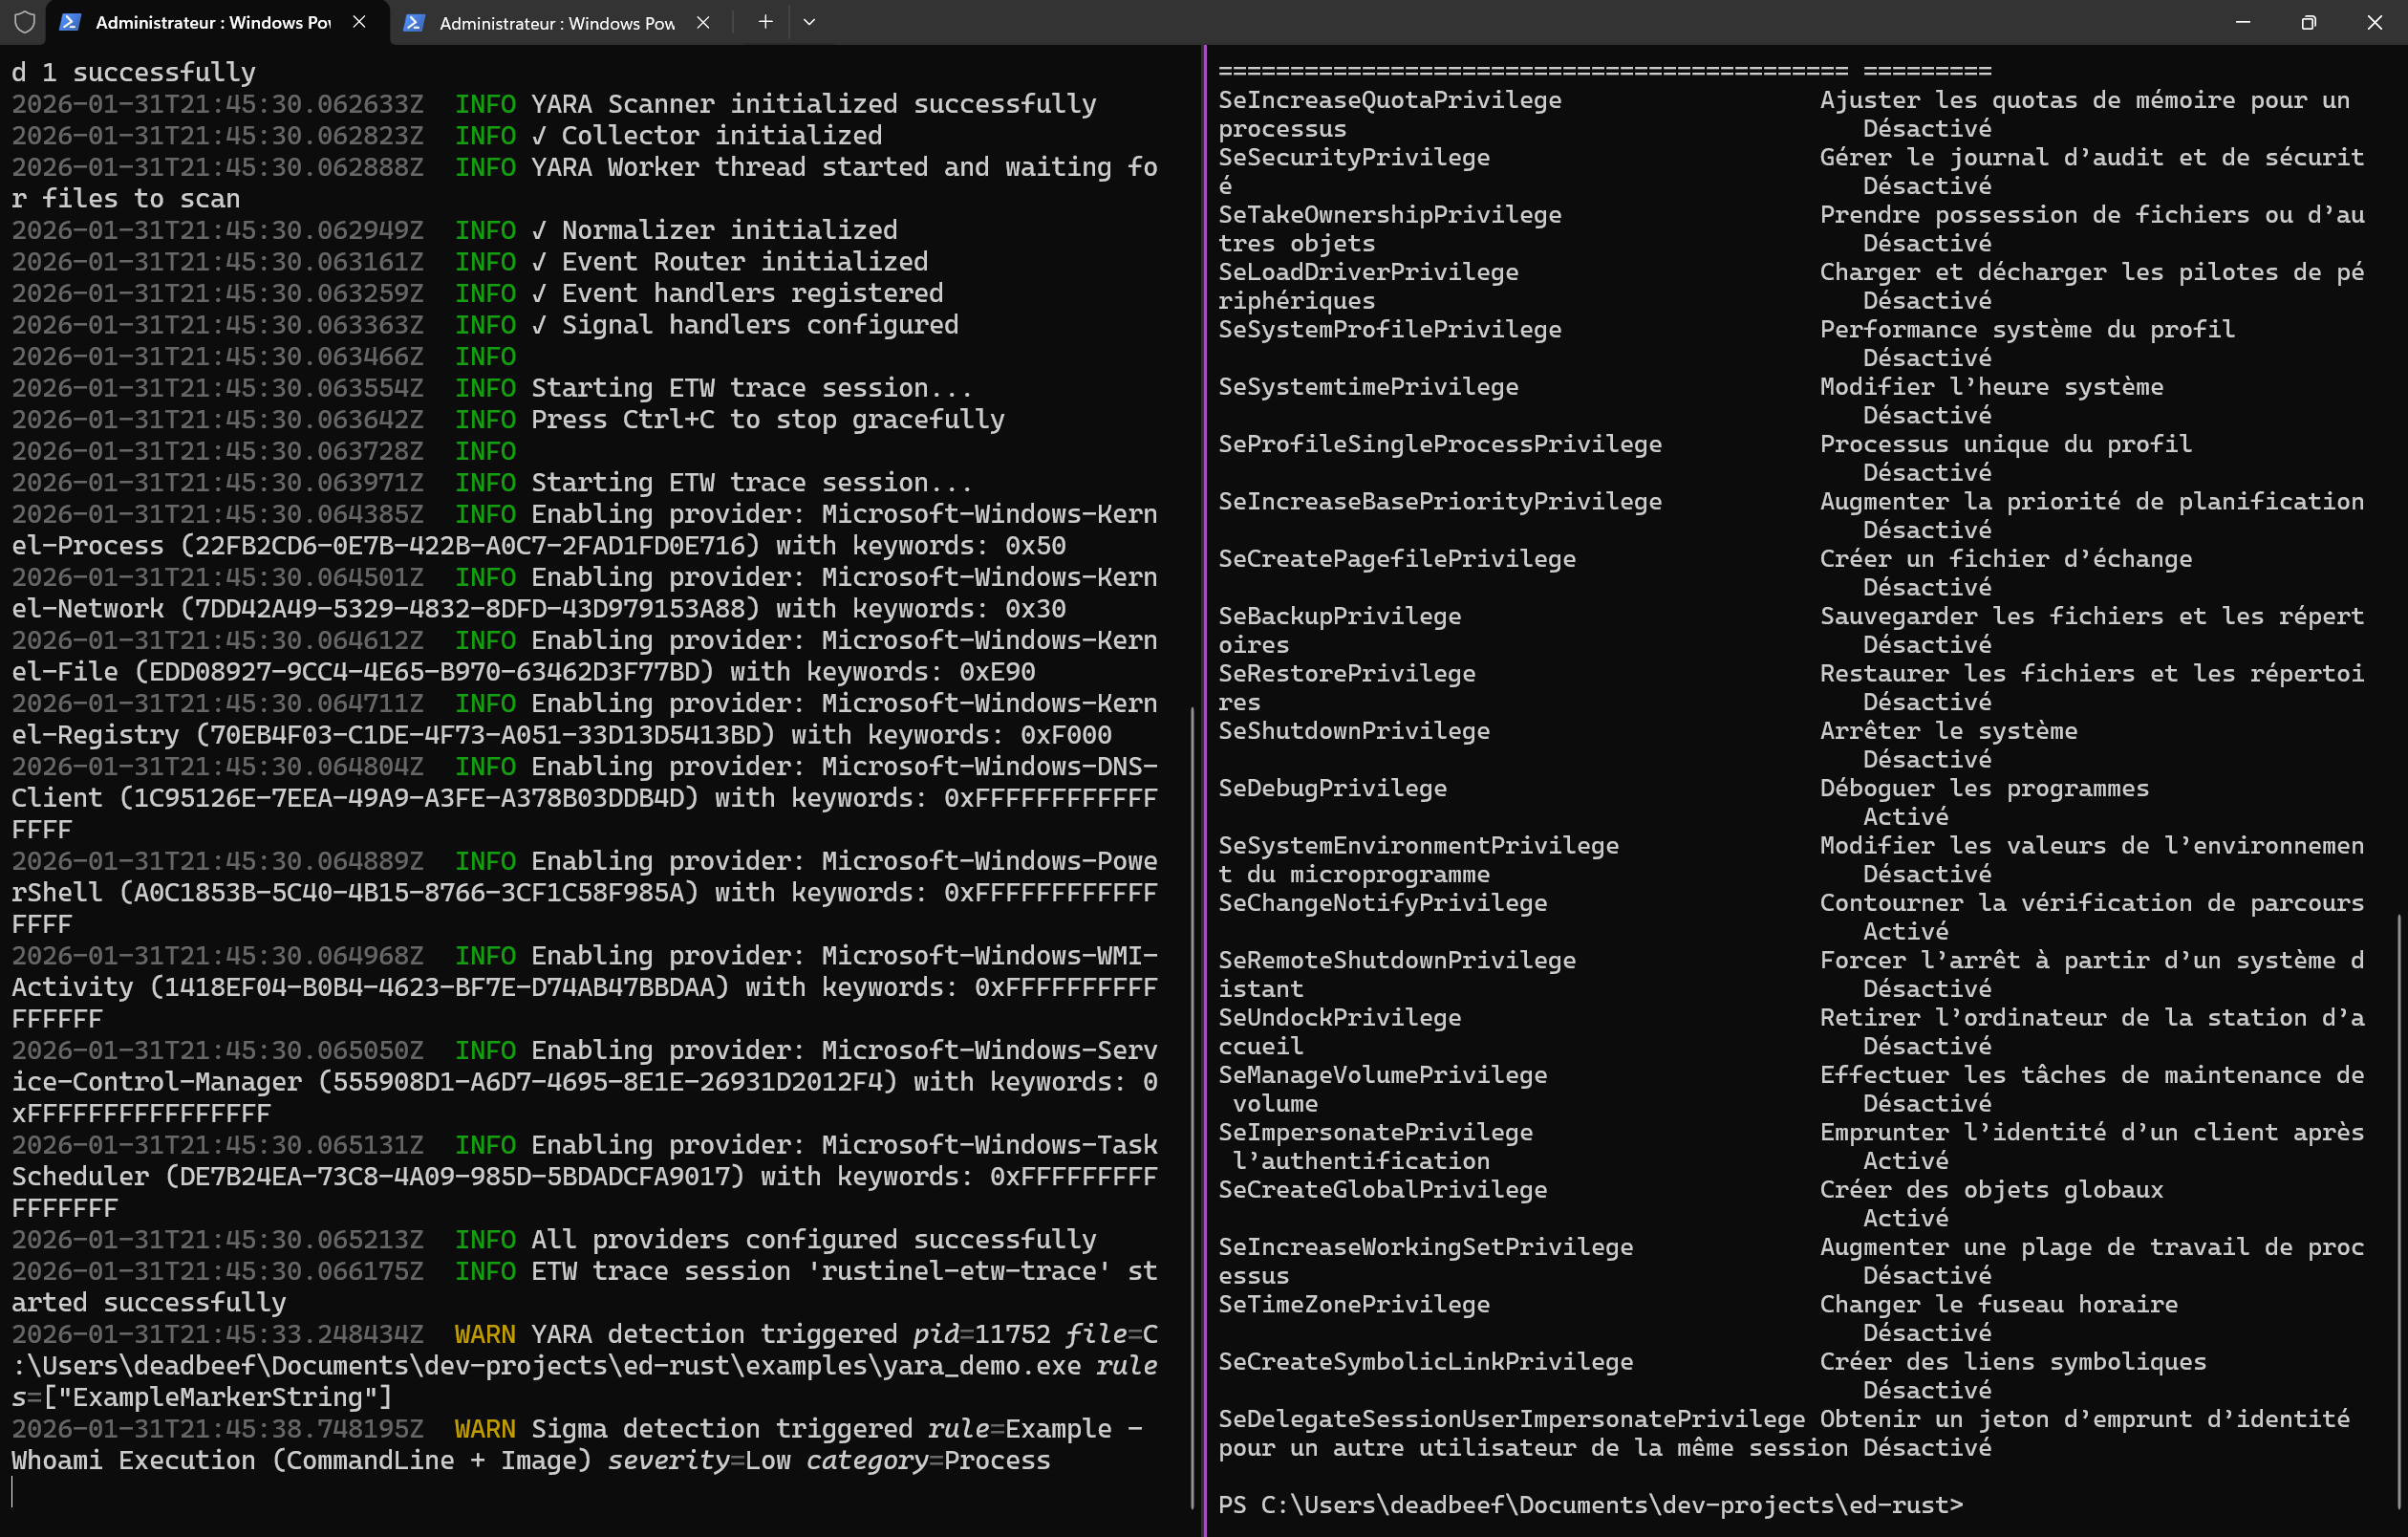
Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required.

IoCs and YARA rules from Threatray's Threat Research

A collection of initial access loaders to use inside enterprise hardened enviroments

A collection of samples and material related to process injection

A collection of android security related resources

Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/

Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…

Indicators of Compromise for malware documented in whitepapers.


Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…

Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…

Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…