

frida
 frida/frida
Main repo for hosting release binaries
android-securitybinary-analysiscode-analysis+9
frida/fridaMain repo for hosting release binaries
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 rednaga/apkid
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.

 momo5502/sogen
🪅 Windows & Linux userspace emulator
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
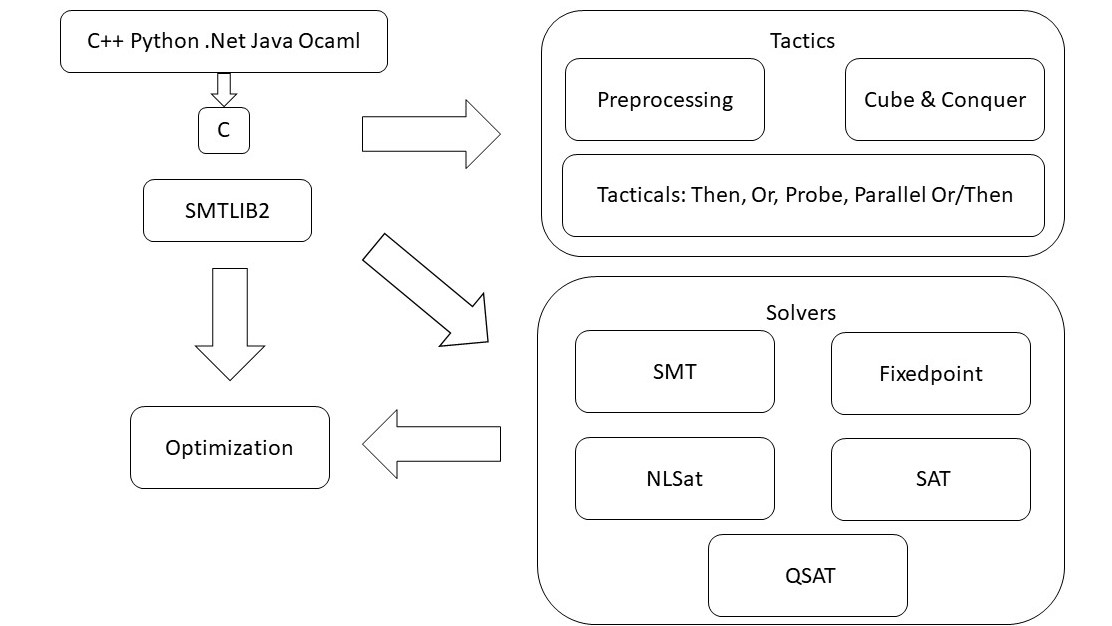 z3prover/z3
High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…

 r3n3r0/cve-2026-0006-step-2
Research package demonstrating a leak-assisted ROP chain in Android media.swcodec via the CVE-2026-0006 APV decoder heap overflow, with payload…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 ashishb/android-security-awesome
A collection of android security related resources