

evil-winrm-py
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
authenticationcommand-and-controllateral-movement+7
406
adityatelange/evil-winrm-pyExecute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 kienhosd/wp-file-manager-exploit-cve-2020-25213-with-zerologon
Exploit Windows server 2019 vulnerable to Zerologon with Garble, Chisel, wp-file-manager vulnerability (have video demo)
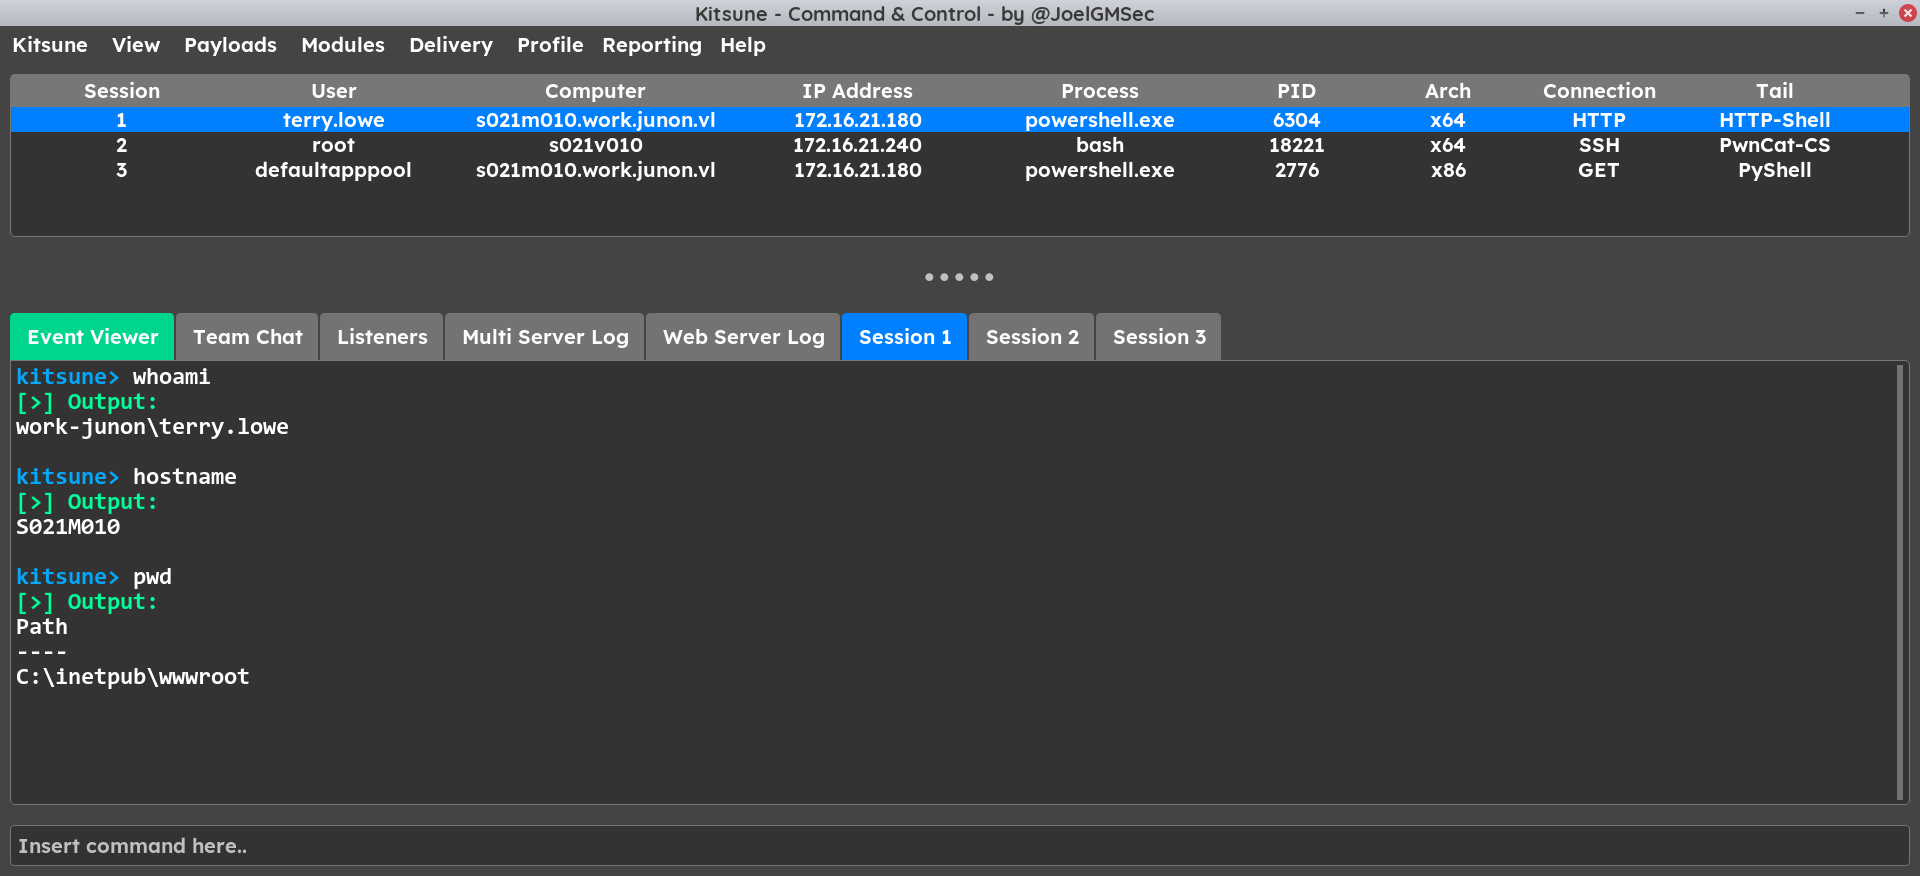 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.