
CVE-2025-29306_poc
 congdong007/cve-2025-29306_poc
Proof-of-concept exploit for CVE-2025-29306, a remote code execution vulnerability in FoxCMS v1.2.5 via the case display page. Includes a Python…
exploitationpenetration-testingremote-access-tool+2
congdong007/cve-2025-29306_pocProof-of-concept exploit for CVE-2025-29306, a remote code execution vulnerability in FoxCMS v1.2.5 via the case display page. Includes a Python…
 dedsecteam-blackhat/poleposph
Tools for scan CVE-2024-25600 - WordPress Bricks Builder Remote Code Execution (RCE)
 mattb709/cve-2025-34028-poc-commvault-rce
Proof-of-Concept (PoC) for CVE-2025-34028, a Remote Code Execution vulnerability in Commvault Command Center. This Python script scans single or…
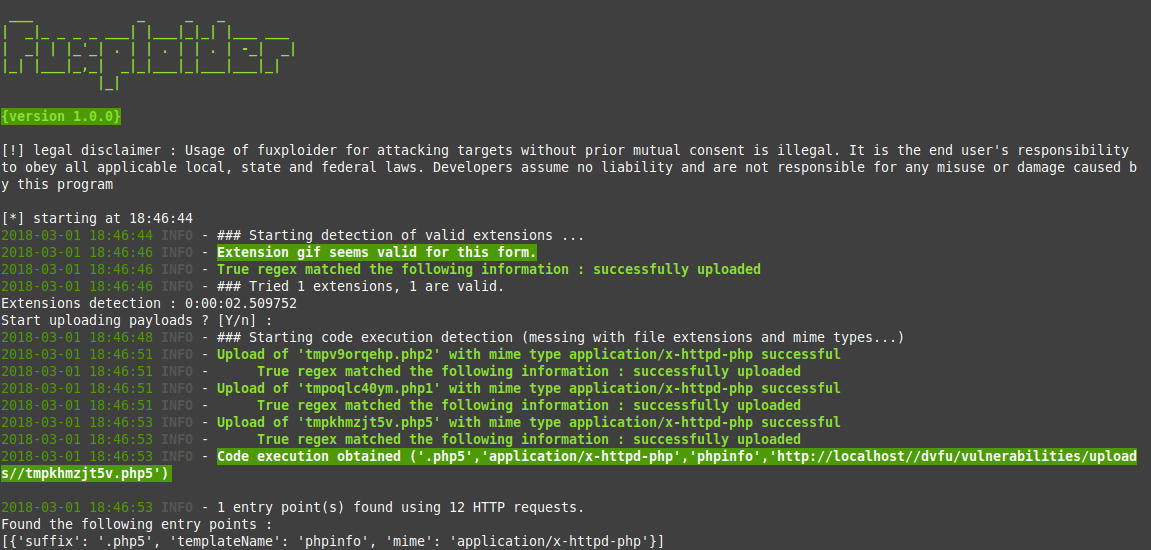 almandin/fuxploider
File upload vulnerability scanner and exploitation tool.
 srcx404/cve-2024-39719
Python exploit script for CVE-2024-39719, a file existence disclosure vulnerability in Ollama. Tests API endpoints to detect server file paths,…
 nairuzabulhul/nuclei-template-cve-2025-31324-check
sap-netweaver-cve-2025-31324-check
 anike-x/cve-2025-45250
Proof-of-concept exploit for CVE-2025-45250, an SSRF vulnerability in MrDoc's validate_url function, allowing authenticated attackers to make…
 randomrobbiebf/cve-2024-13800
Popup Plugin For WordPress - ConvertPlus <= 3.5.30 - Missing Authorization to Authenticated (Subscriber+) Limited Options Update
 srcx404/cve-2024-39722
Exploit tool for CVE-2024-39722, a model existence disclosure vulnerability in Ollama. Performs version checks, crawls official model library, and…
 jonathanstross/cve-2025-31324
A Python-based security scanner for identifying the CVE-2025-31324 vulnerability in SAP Visual Composer systems, and detecting known Indicators of…
 moften/cve-2021-23017
NGINX DNS Overflow Vulnerability Check - CVE-2021-23017 PoC
 xp3s/cve-2025-45250
CVE-2025-45250 POC
 gcatt-as/cve-2024-48590
Disclosure of a Server-Side Request Forgery (SSRF) vulnerability in Inflectra SpiraTeam 7.2.00, detailing the attack vector, impacts, and vendor…
 singetu0096/cve-2025-46731
Proof-of-concept exploit and technical report for CVE-2025-46731, providing vulnerability analysis and exploitation details for security testing and…
 esonhugh/ingressnightmare-cve-2025-1974-exps
IngressNightmare POC. world first non-blind remote execution exploitation with multi-advanced exploitation methods. allow on disk exploitation.…
 moften/cve-2014-6271
Shellshock Vulnerability Scanner
 graysignal/cve-2025-3248
Exploit scanner detecting unauthenticated code injection in Langflow's /api/v1/validate/code endpoint and executing arbitrary code for authorized…
 sexyshoelessgodofwar/cve-2025-47256
Stack overflow in LibXMP