Exploit-For-CVE-2026-18963

Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…

Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…


Proof-of-concept exploit for CVE-2026-18963, an authentication bypass in Keycloak's forgot-password flow, allowing password reset without proper…

Firmware Analysis and Comparison Tool

Patch: Template injection RCE (Atlassian Confluence)

Patch: Privilege escalation via web UI (Cisco IOS XE)

Go CLI that inventories HTTPS endpoints negotiating HTTP/2 via ALPN to identify systems requiring CVE-2023-44487 mitigation review. Non-exploitative,…

The vulnerable application that will teach you how to hack WebSockets

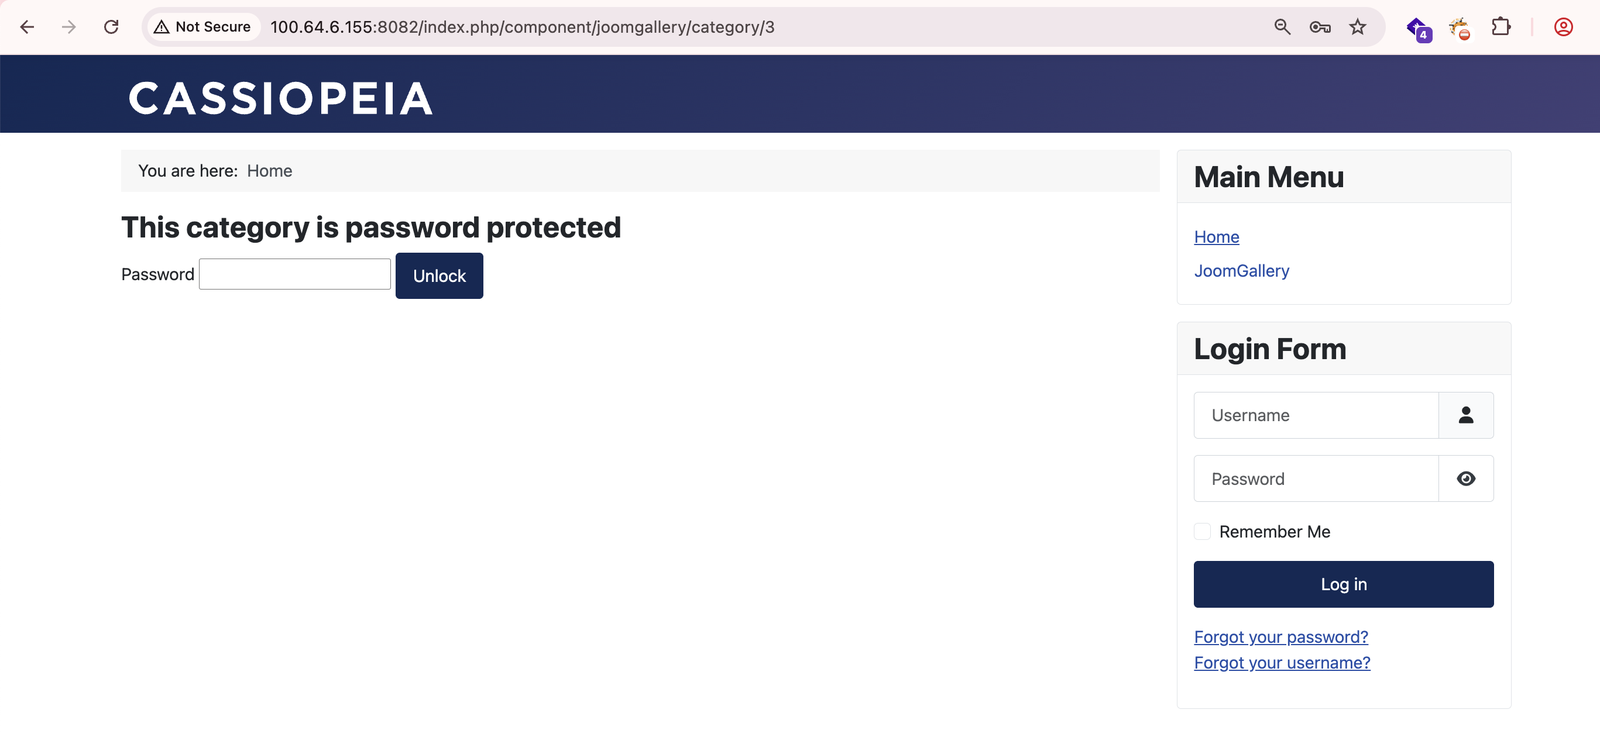
Password-Protected Category Bypass via JSON Format in JoomGallery

This python script exploit the vulnerable marimo /terminal/ws endpoint and returns a interactive shell.

Exploit Title: Unauthenticated SQL Injection on CMS Made Simple <= 2.2.9

Proof-of-concept exploit for UniFi OS CVE-2026-34910 auth bypass enabling command injection/RCE, and CVE-2026-34909 path traversal for arbitrary file…

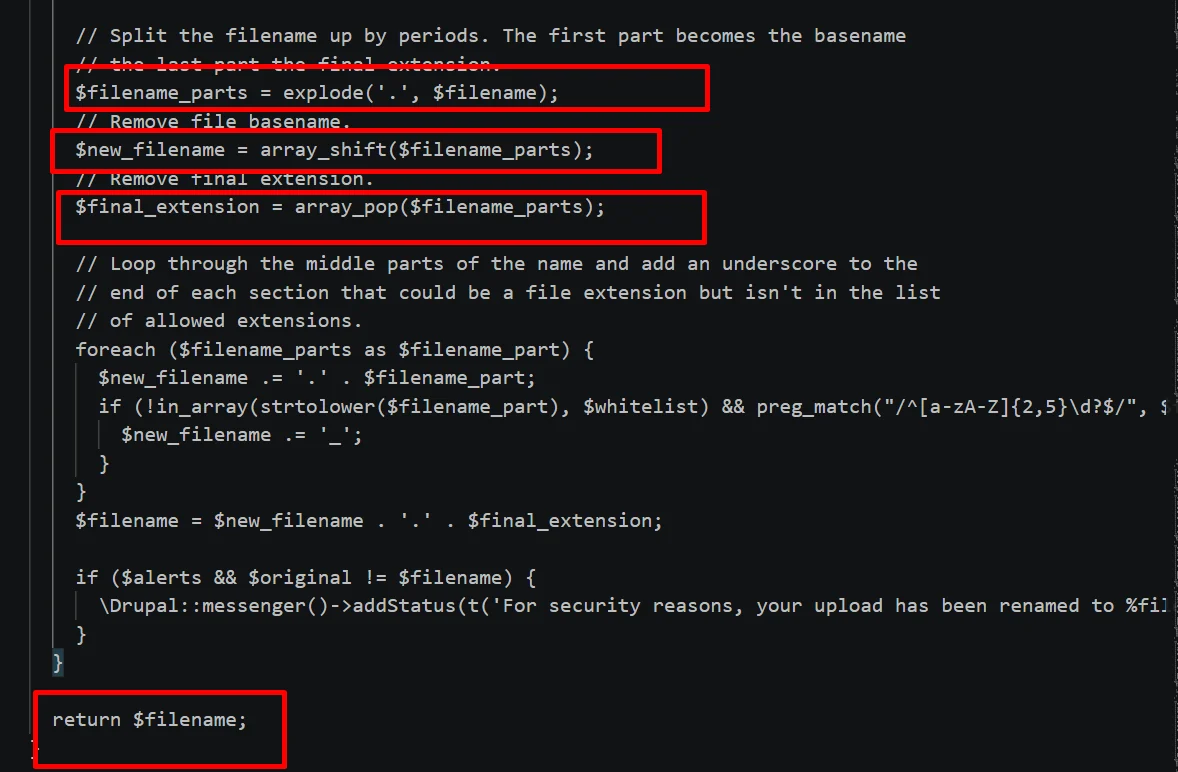
Detailed analysis and proof-of-concept for CVE-2020-13671, a Drupal core remote code execution vulnerability via file upload, including root cause,…

Minimal proof-of-concept for Spring Framework UrlHandlerFilter open redirect (CVE-2026-47883), demonstrating crafted double-slash requests produce…

Stored XSS in J2Commerce Guest Checkout via Cookie Filter Bypass

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

PoC for J2Store CVE-2026-67358–67362 (J2Commerce security advisory Aug 2026)

🛡️ Open-source and cloud-native Web Application Firewall (WAF)