
MsfMania
 lepotekil/msfmania
Python AV Evasion Tools
binary-analysiseducationencryption-decryption-tools+9
51711 months ago
lepotekil/msfmaniaPython AV Evasion Tools
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 oilseller2001/poc-for-cve-2025-9074
Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.
 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
 nika0x38/cve-2007-2447
A standalone Rust implementation of the CVE-2007-2447 exploit targeting Samba smbd 3.0.20-Debian.
 radoi-teodor/cve-2023-21768-dse-bypass
Windows kernel exploit for CVE-2023-21768 that bypasses Driver Signature Enforcement (DSE) to load unsigned drivers, enabling local privilege…
 pentestfunctions/best-cve-2025-8088
Winrar CVE exploitation before 7.13 using multiple ADS streams on a single file (Custom PDF implementation)
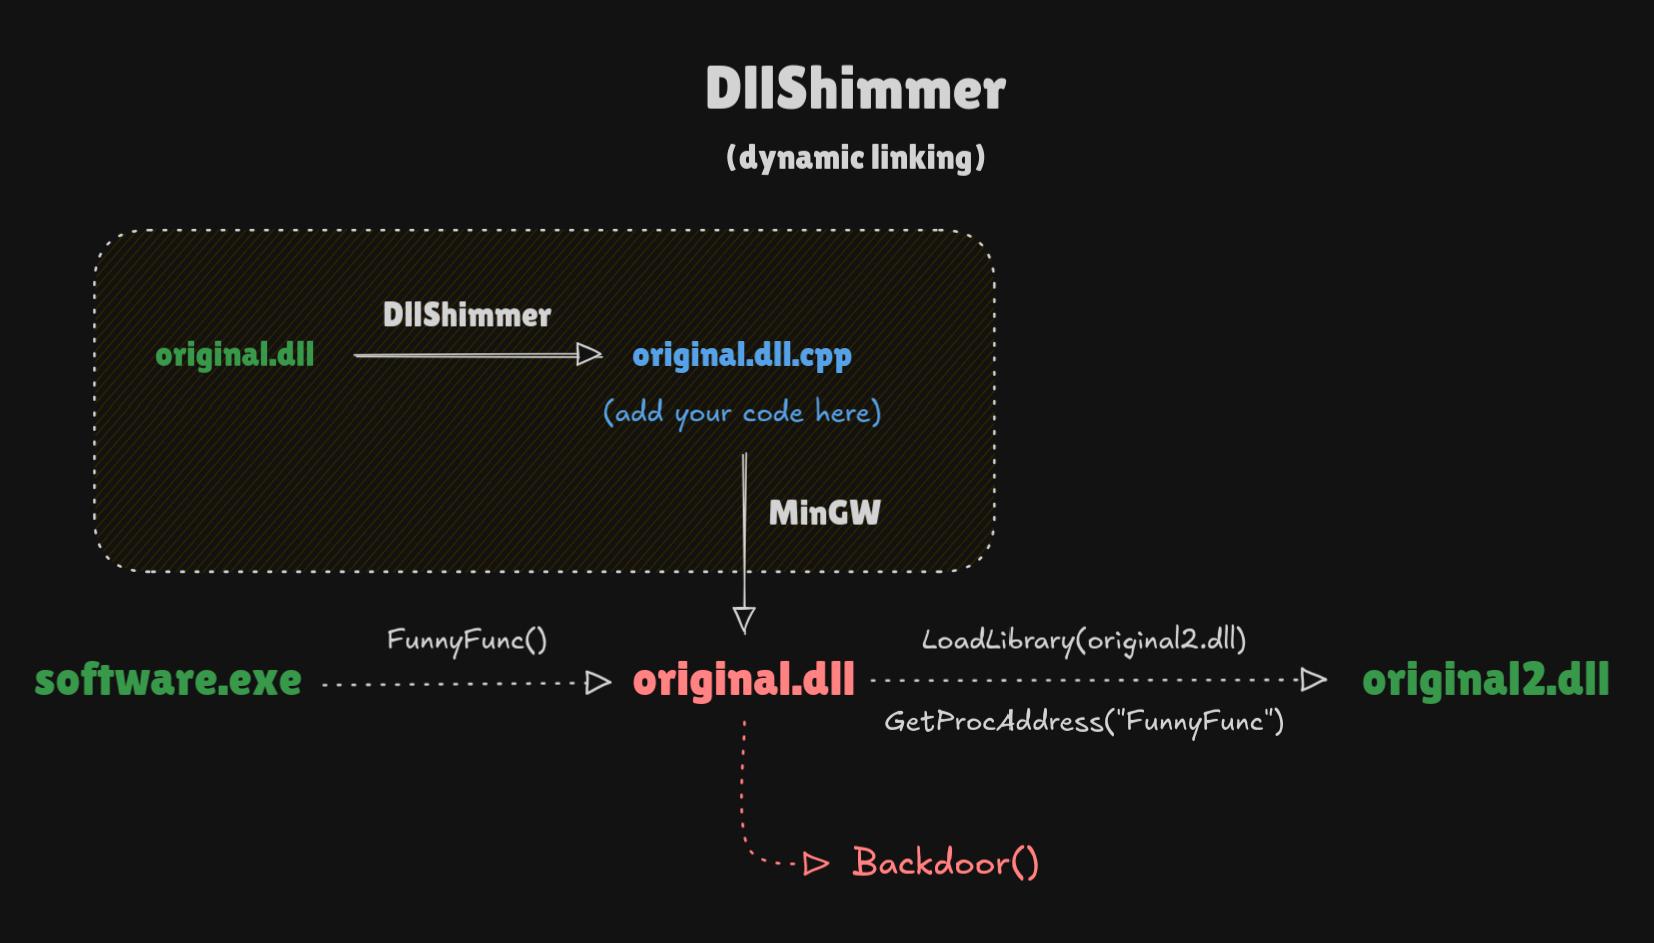 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 pexlexity/winrar-cve-2025-8088-path-traversal-poc
Proof-of-Concept for CVE-2025-8088 vulnerability in WinRAR (path traversal via ADS)
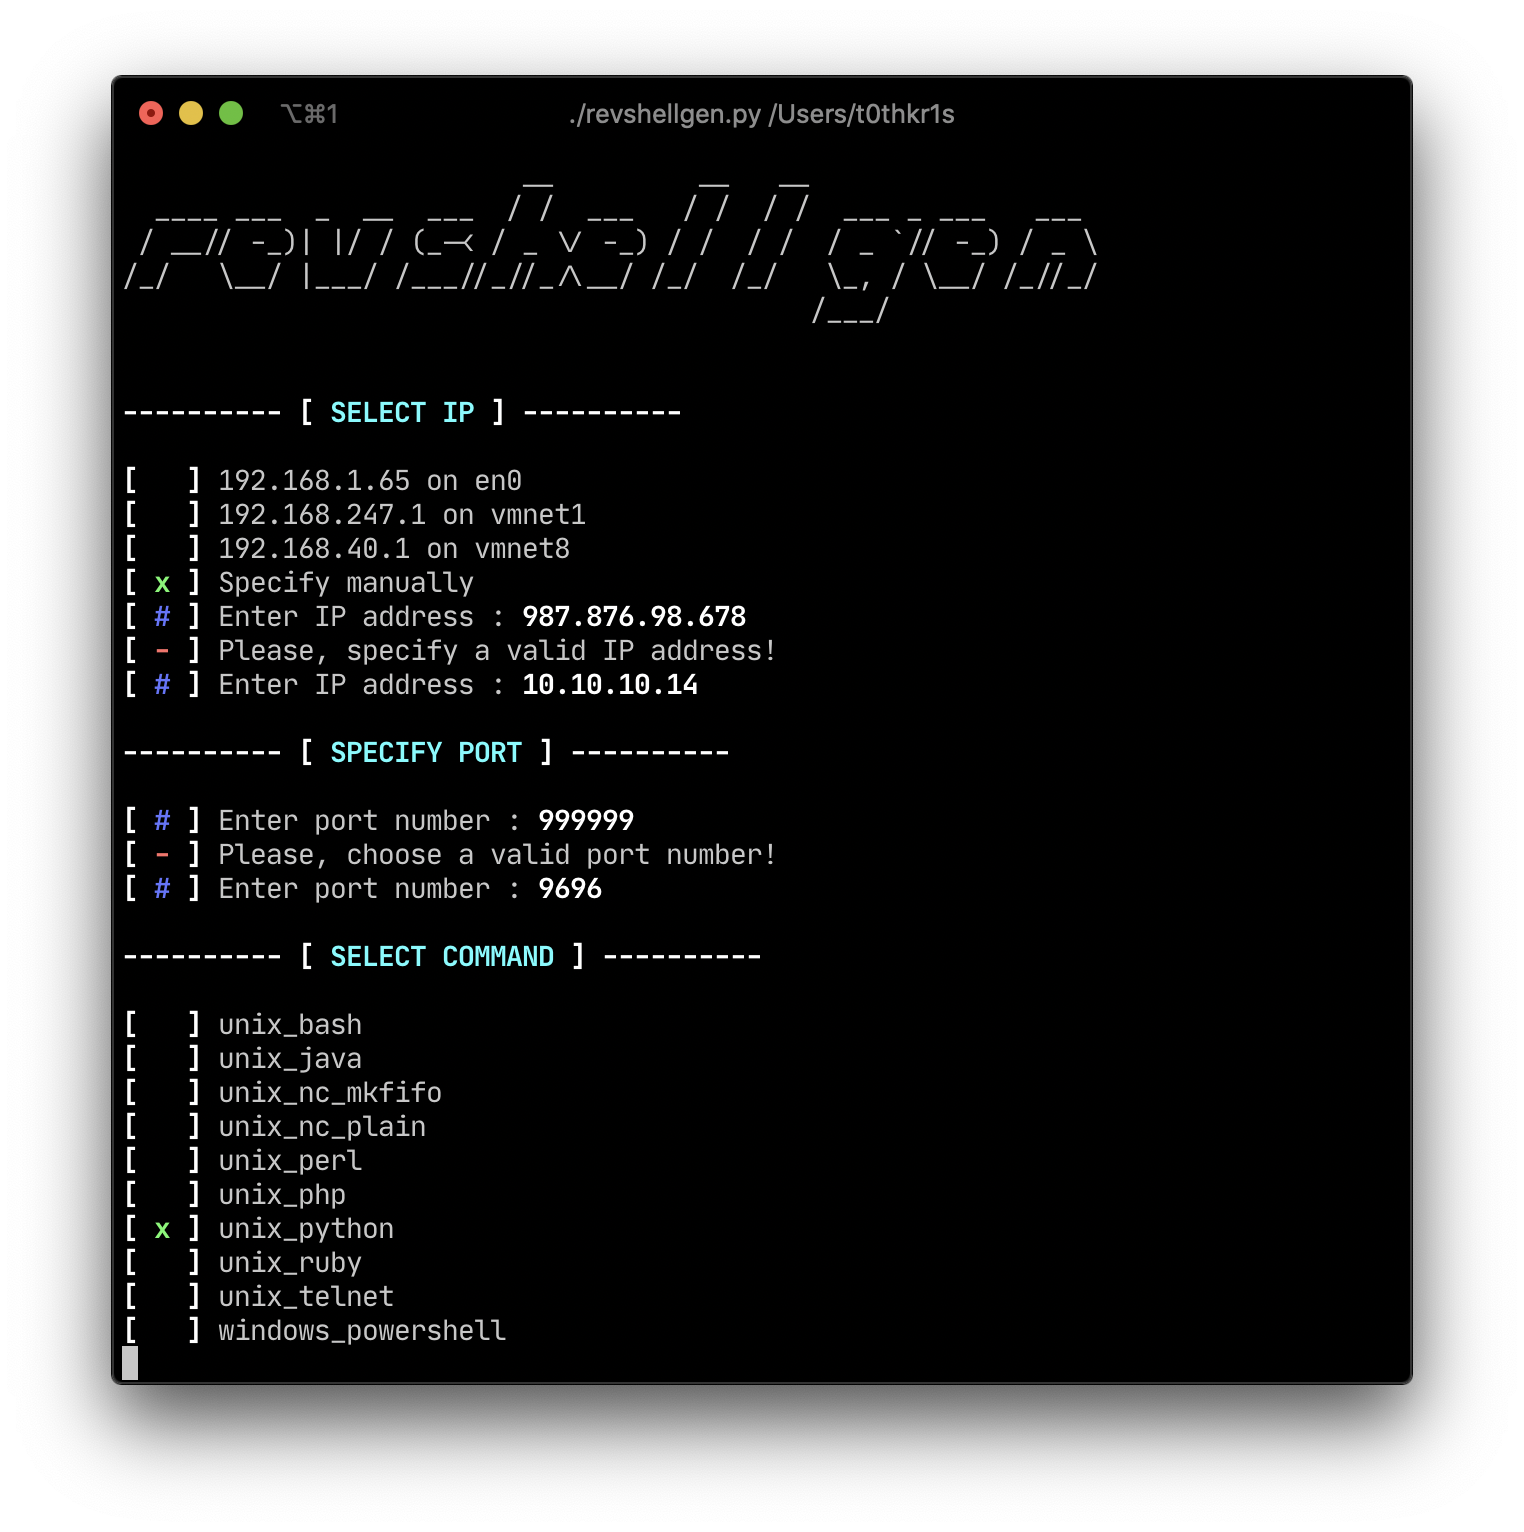 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 cyglegit/cve-2025-24813
Automated exploitation toolkit for CVE-2025-24813 targeting Apache Tomcat insecure session deserialization. Features multi-target scanning, gadget…
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 josemlwdf/cve-2019-13272
This is a Python 3 version of this exploit. Hope it works!!!
 je5442804/wptaskscheduler_cve-2024-49039
WPTaskScheduler RPC Persistence & CVE-2024-49039 via Task Scheduler
 exploits-forsale/collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 synacktiv/ccmmessagingbackdoor
Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.