
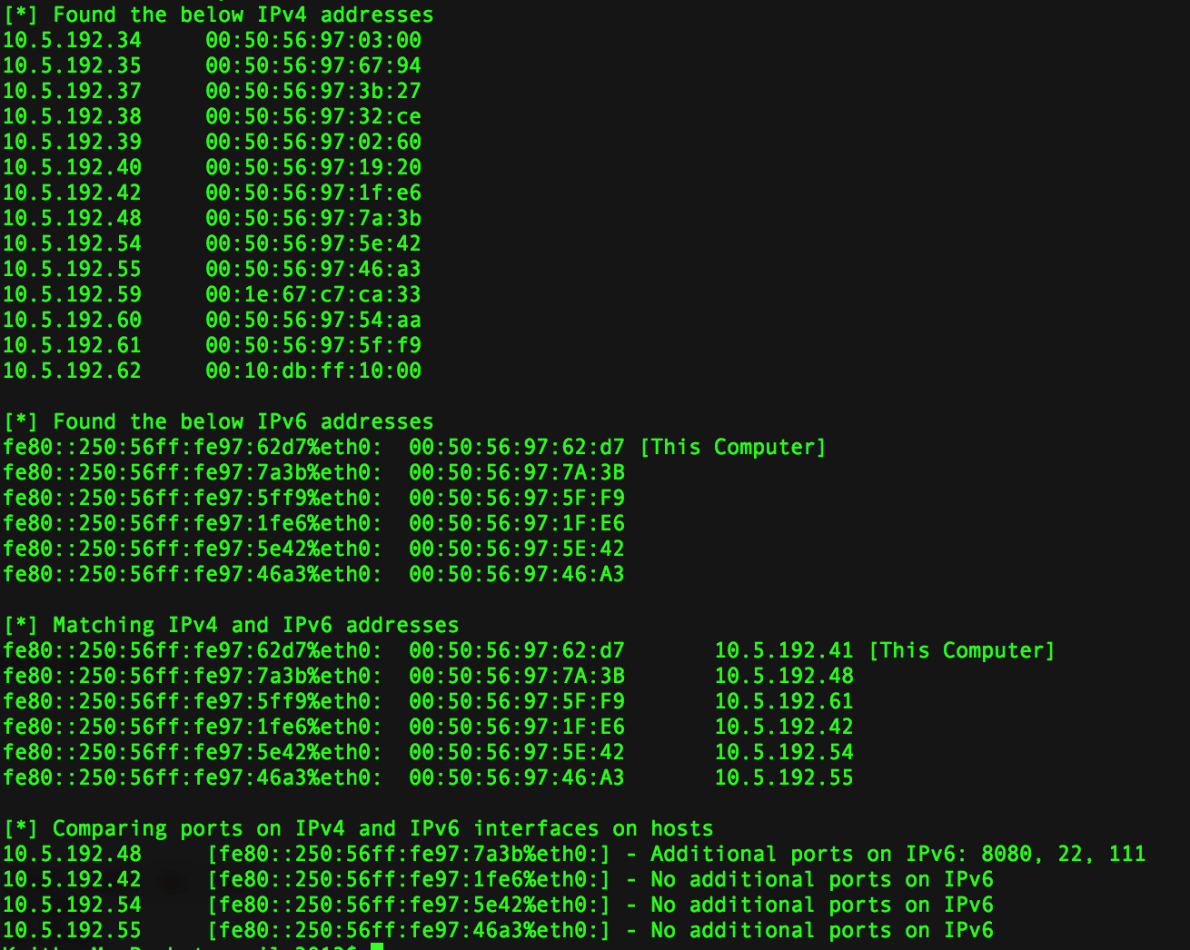
ipv4Bypass
 milo2012/ipv4bypass
Using IPv6 to Bypass Security
ids-ips-evasionnetwork-securitypenetration-testing+2
93
milo2012/ipv4bypassUsing IPv6 to Bypass Security
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
 hagrid29/cve-2024-40586-windows-coerced-authentication-in-forticlient
Exploit for CVE-2024-40586: coerces Windows hosts to authenticate via a vulnerable FortiClient named pipe, enabling privilege escalation to SYSTEM or…
 rteccybersec/raitrigger
Local SYSTEM auth trigger for relaying
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)
 starscow/cve-2025-33073
PoC Exploit for the NTLM reflection SMB flaw.
 u53rw4r3/remotekeystrokes
A script to automate keystrokes through a graphical desktop program.
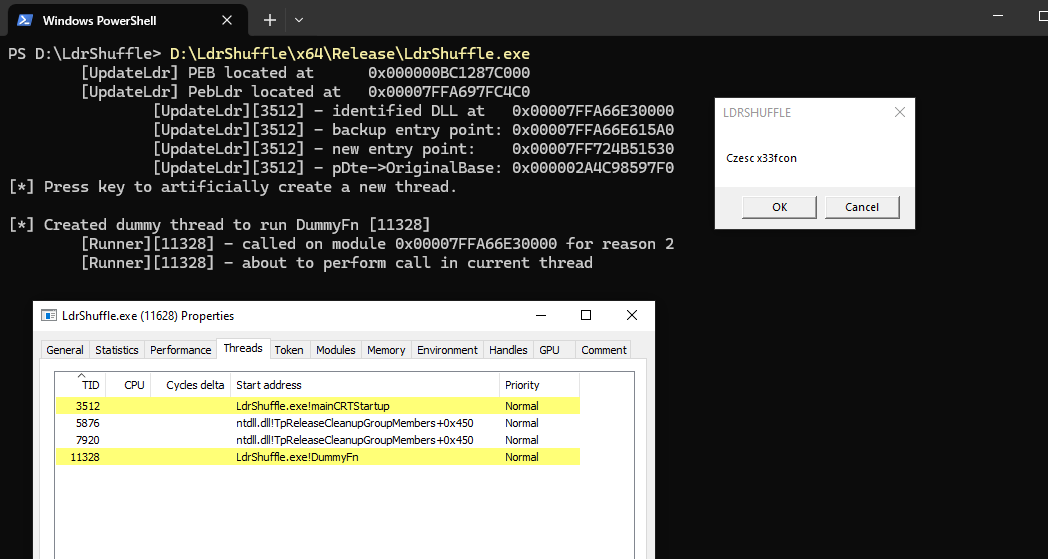 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 hxlxmj/cve-2025-26264
CVE-2025-26264 - GeoVision GV-ASWeb with the version 6.1.2.0 or less, contains a Remote Code Execution (RCE) vulnerability within its Notification…
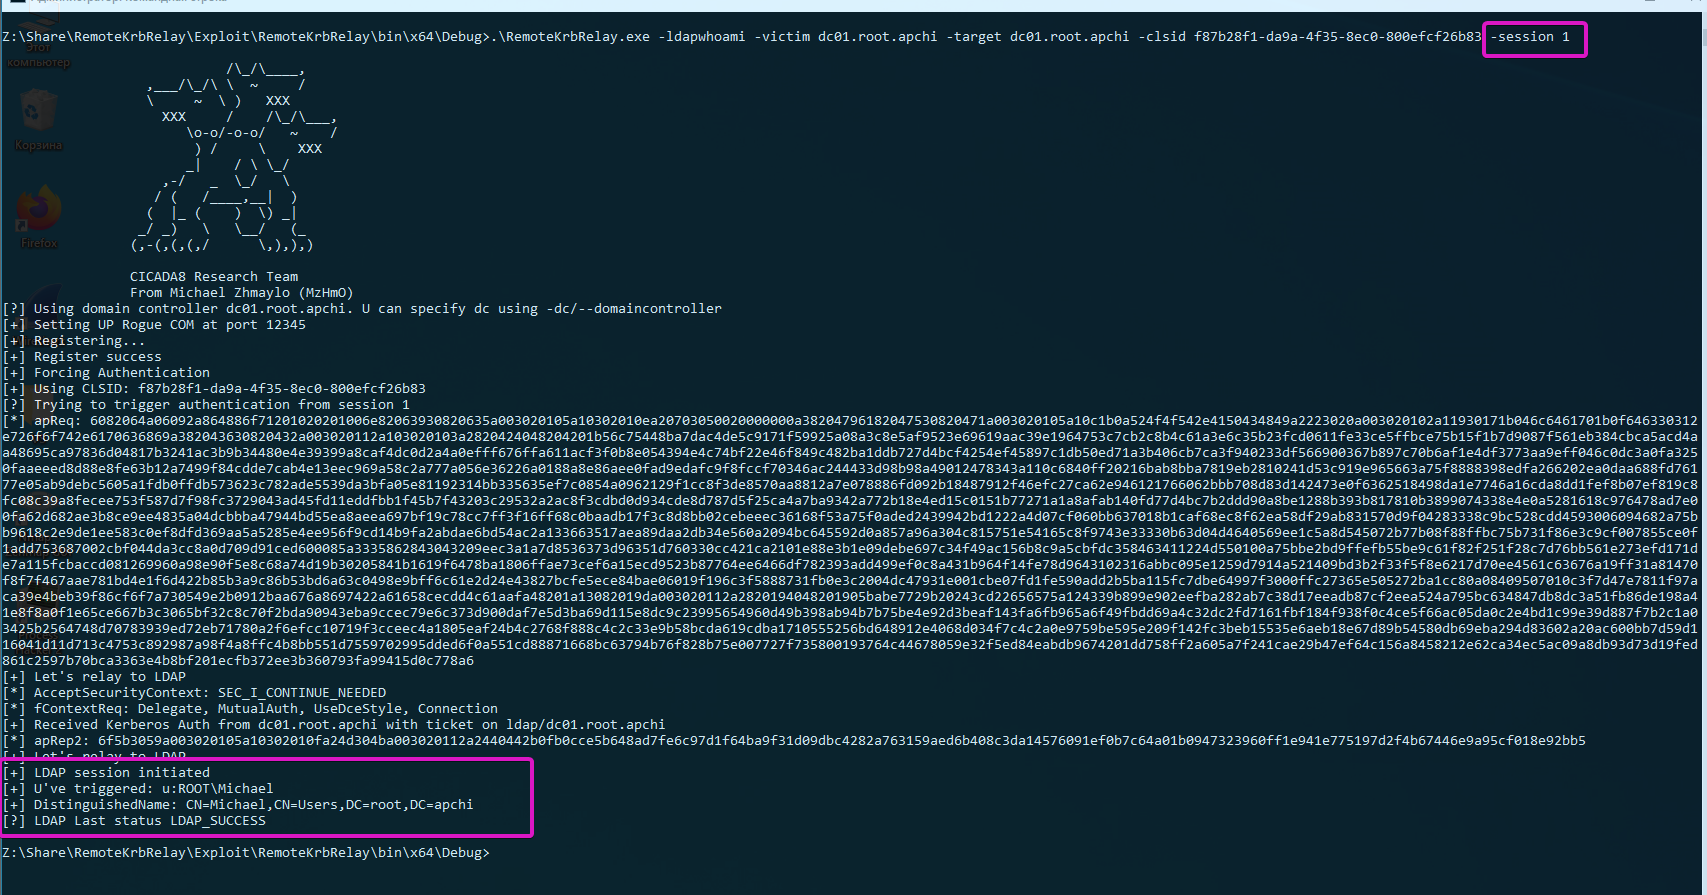 cicada8-research/remotekrbrelay
Remote Kerberos Relay made easy! Advanced Kerberos Relay Framework
 zimedev/certipy-merged
Tool for Active Directory Certificate Services enumeration and abuse
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
 gunzf0x/cve-2020-0665
Proof of Concept for CVE-2020-0665, a.k.a. SID Filter Bypass.
 mbadanoiu/cve-2020-13941
CVE-2020-13941: Abusing UNC Paths in Windows Environments in Apache Solr