
CVE-2025-24813
 alpereny-cs/cve-2025-24813
Create lab for CVE-2025-24813
container-securityeducationexploitation+4
alpereny-cs/cve-2025-24813Create lab for CVE-2025-24813
 performant-labs/cve-2024-22262
Proof-of-concept exploit for CVE-2024-22262 in Spring applications, with a Dev Container environment for hands-on vulnerability exploration and…
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
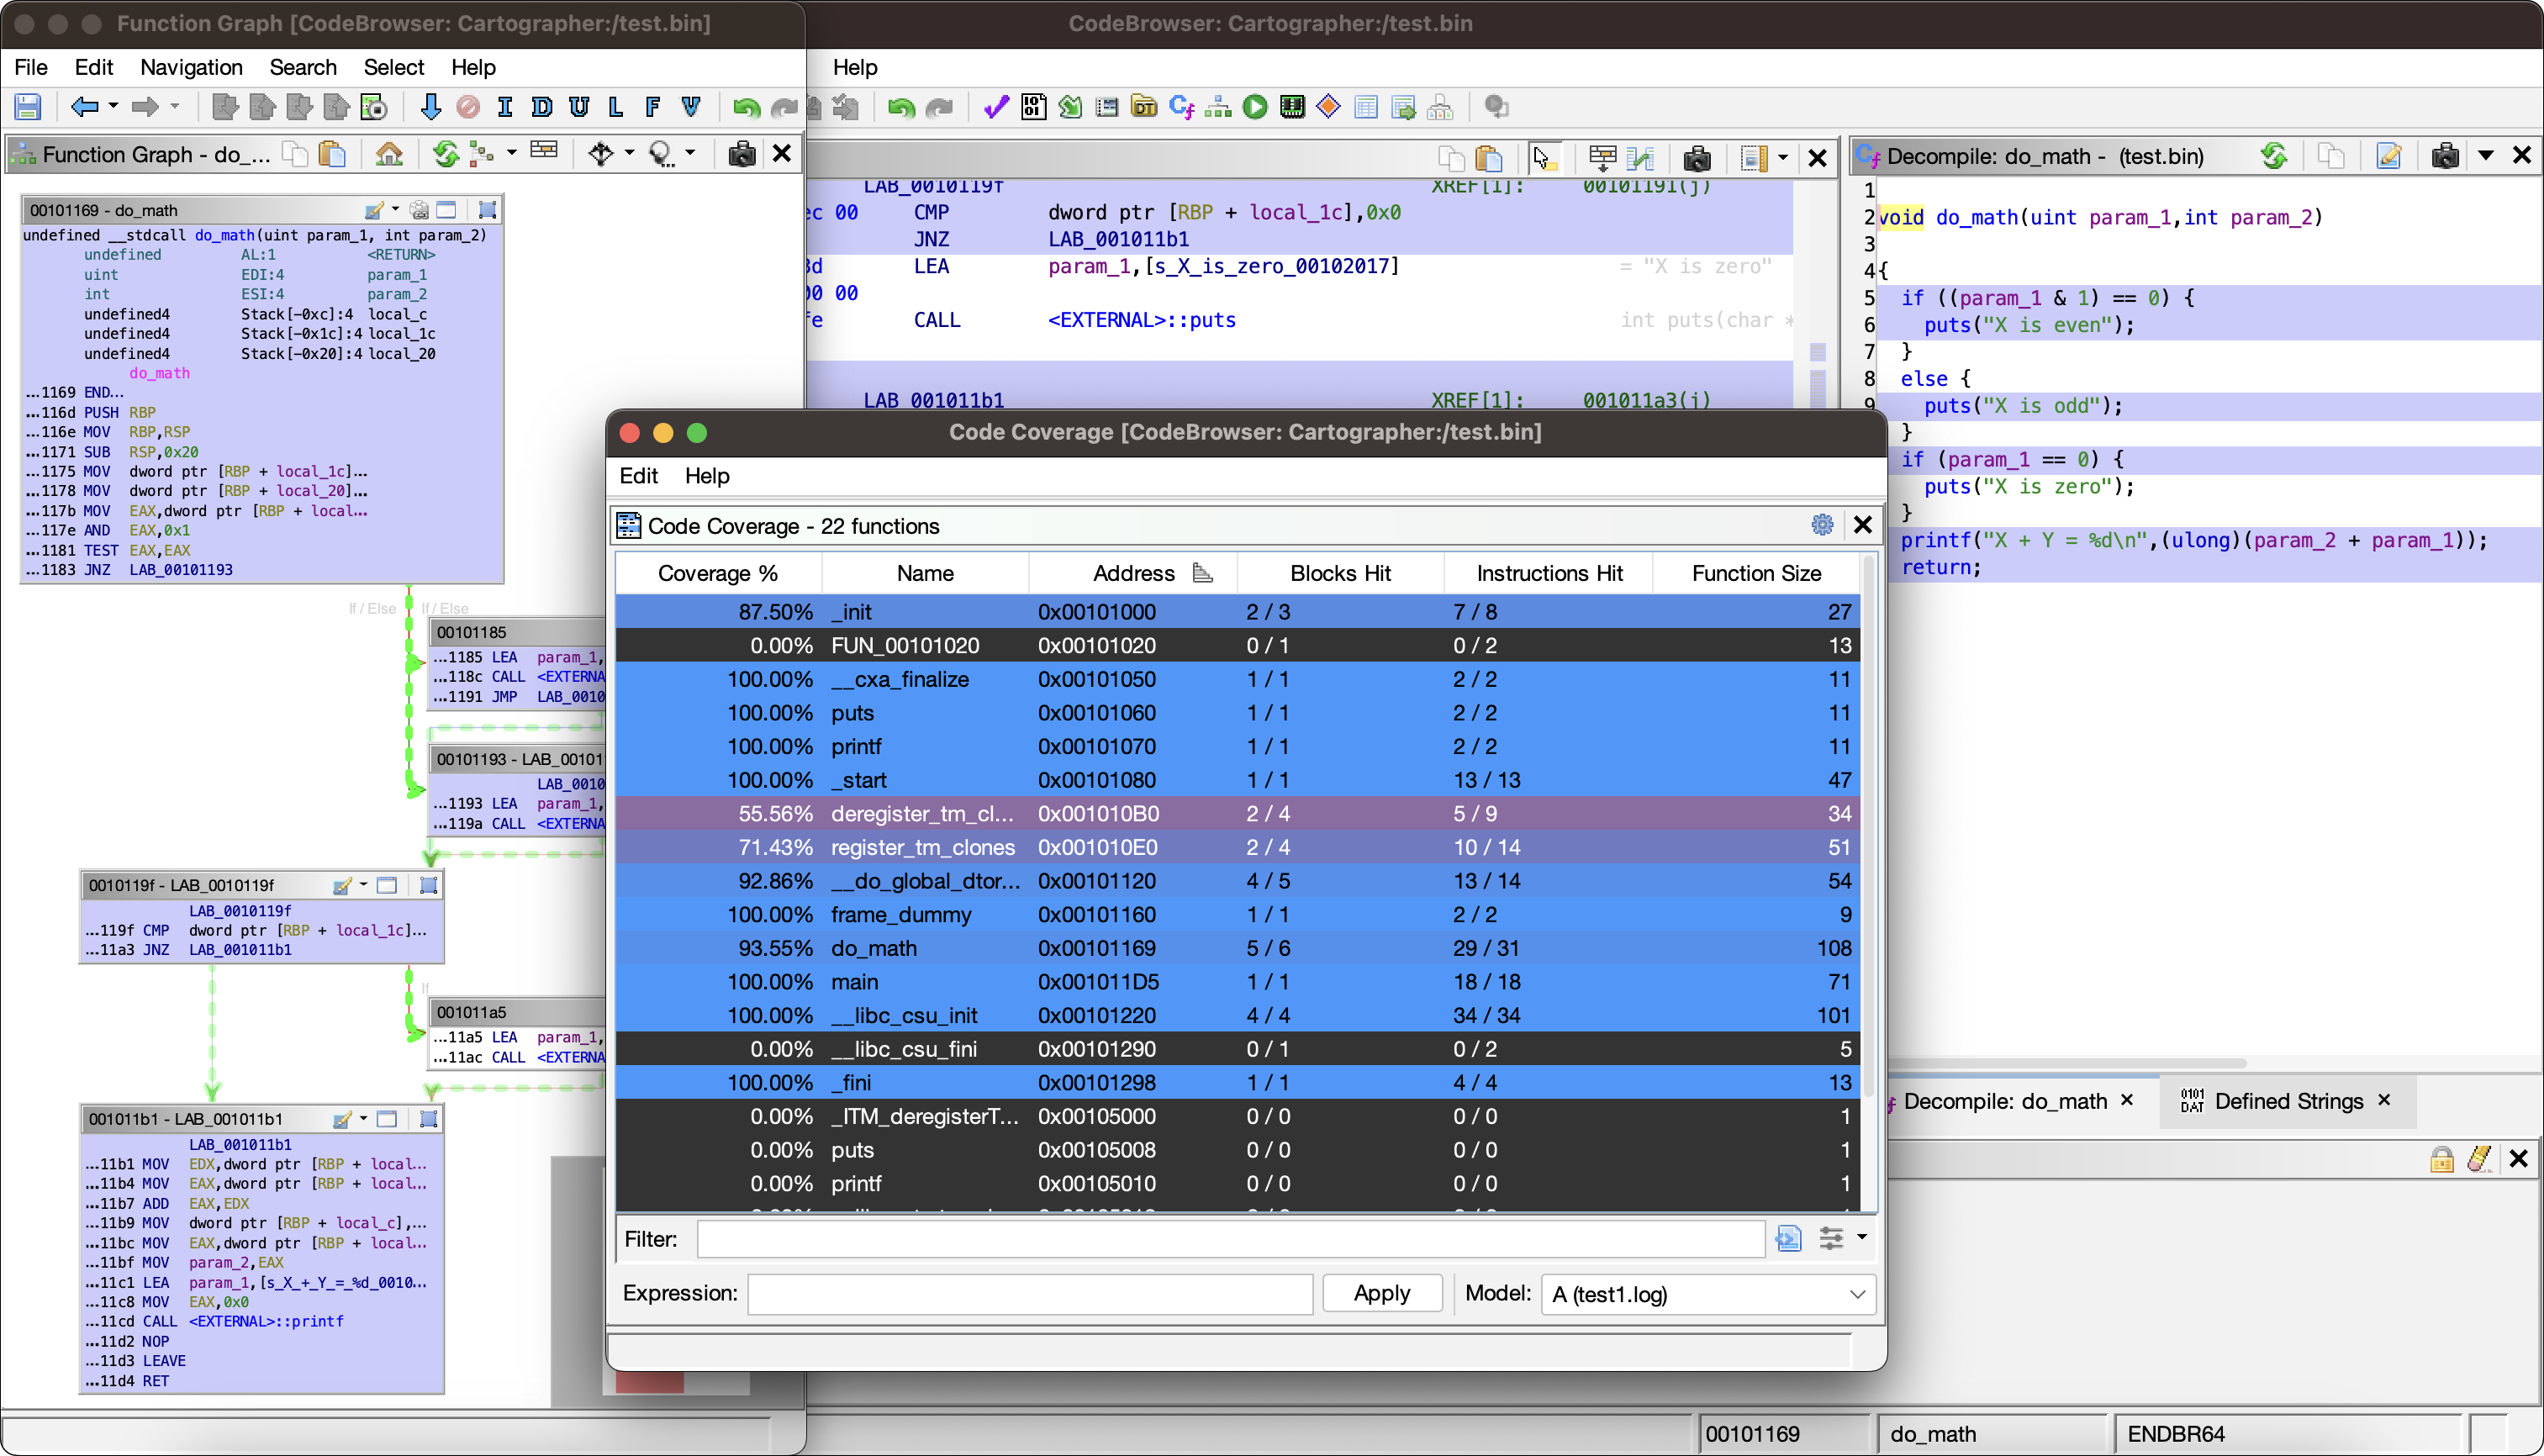 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 wshinkle/cve-2023-2982
Python exploit script for CVE-2023-2982, packaged in a Docker container for automated deployment and testing against vulnerable targets.
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 hackarada/cve-2015-3306
Dockerized exploit environment for CVE-2015-3306 (ProFTPD copy_file_range) with FTP and HTTP services for penetration testing and vulnerability…
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 0x3c3e/slides
CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU
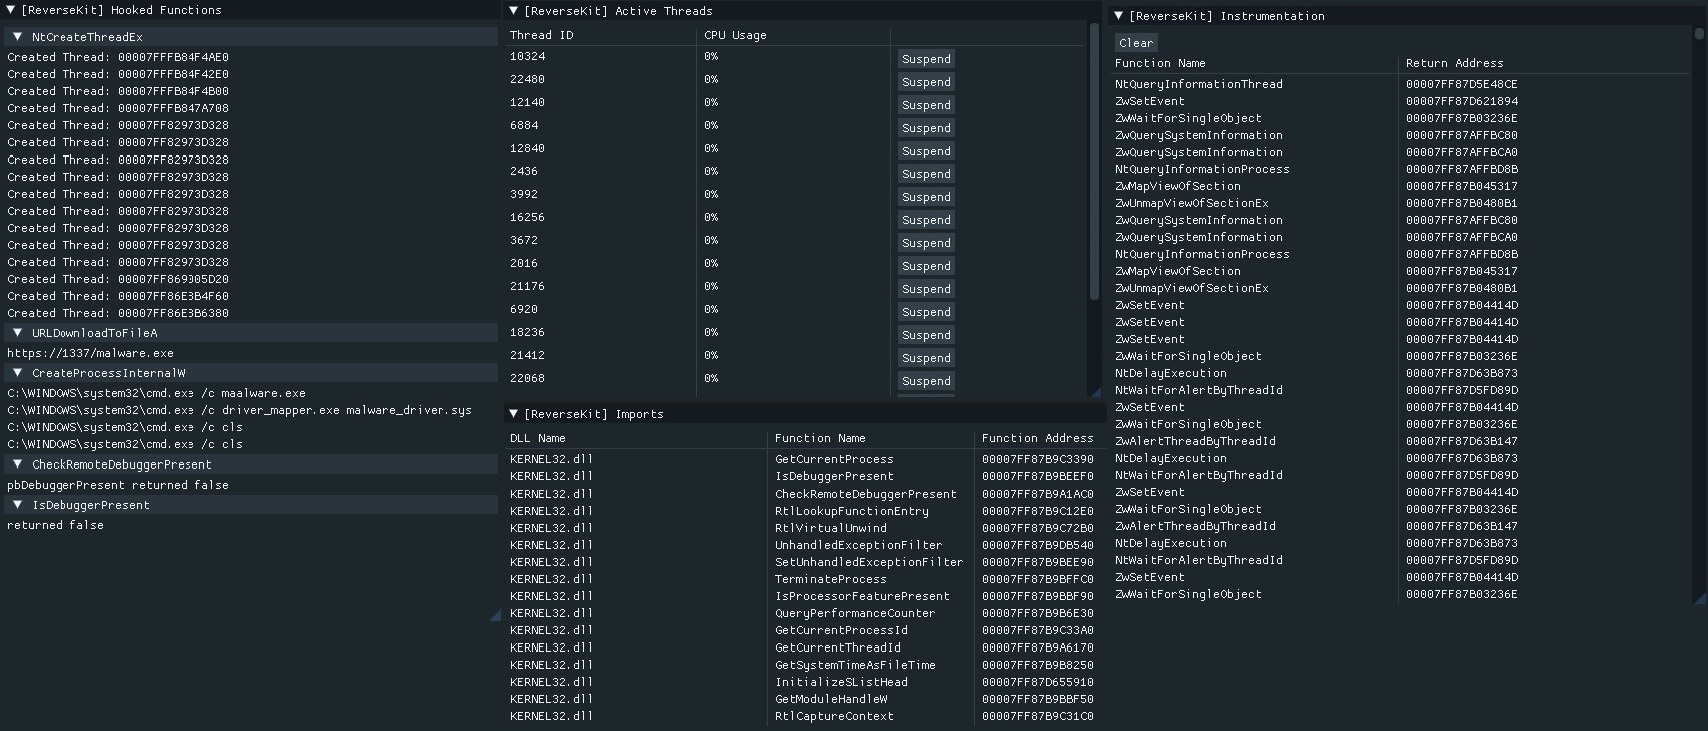 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 kuttappu123/cve-2023-30212-lab
Hands-on lab environment for exploiting CVE-2023-30212, a stored XSS vulnerability in OURPHP ≤7.2.0, using Docker containers for safe penetration…
 reachabilityorg/cve-2022-42889-text4shell-docker
Dockerized vulnerable Java application demonstrating CVE-2022-42889 (Text4Shell) remote code execution via Apache Commons Text string lookups, for…
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 devengpk/cve-2022-22965
Dockerized Spring4Shell (CVE-2022-22965) proof-of-concept with Python exploit script and webshell deployment for educational vulnerability testing.
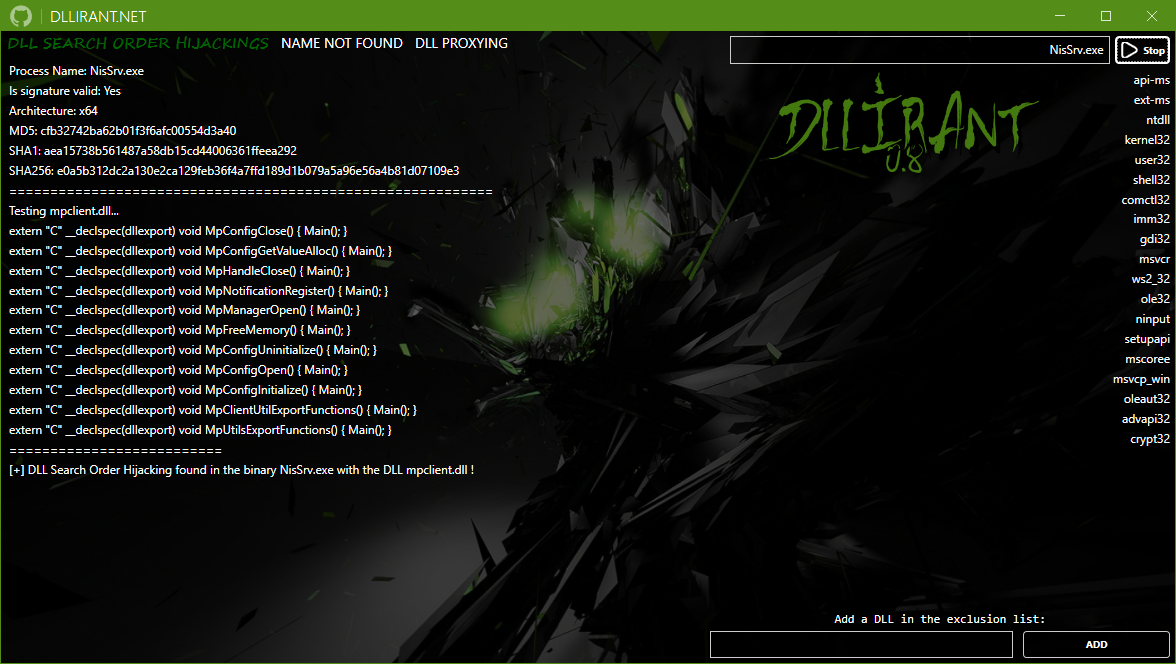 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
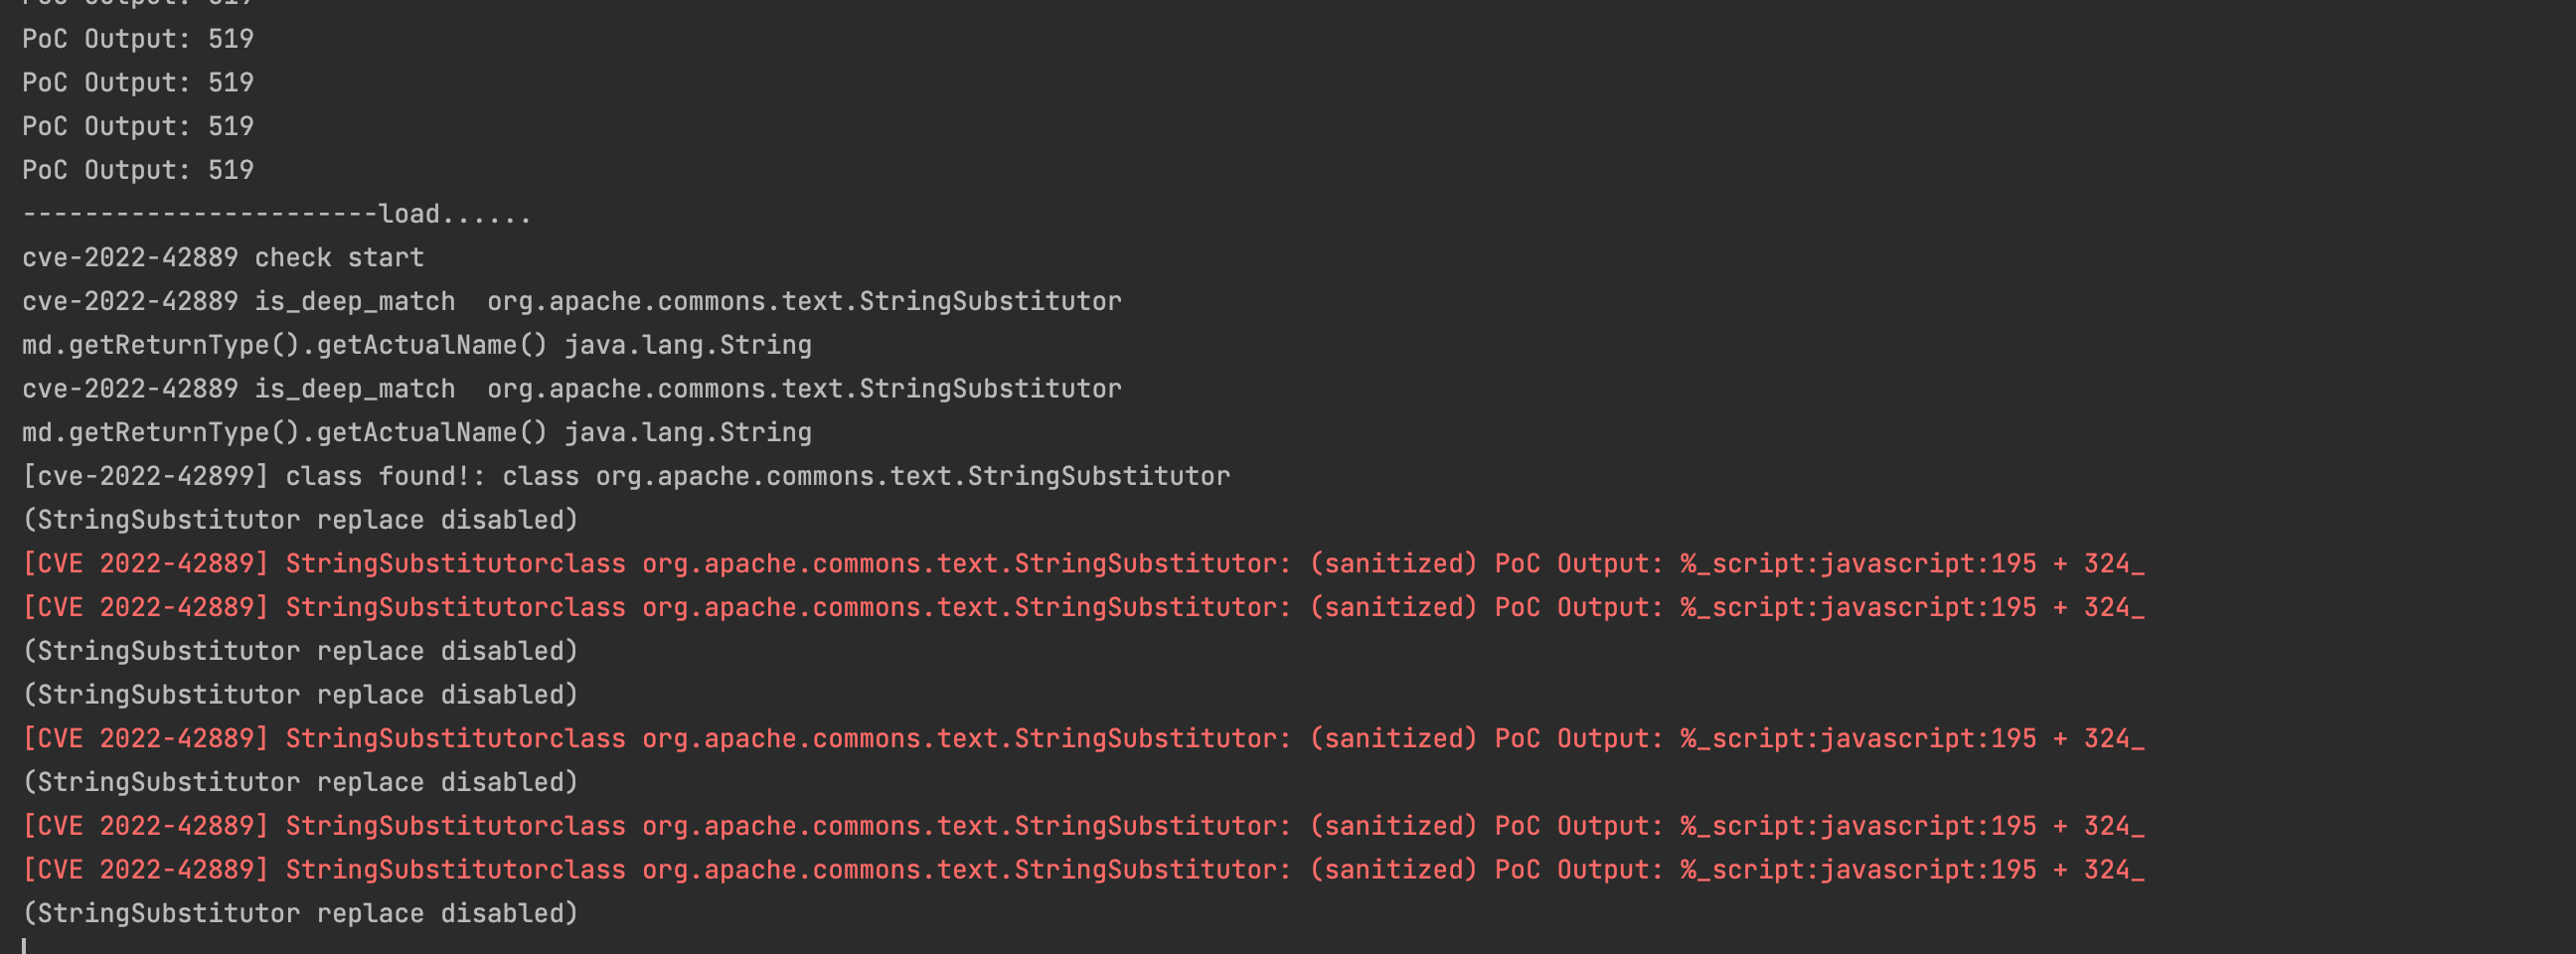 uk0/cve-2022-42889-intercept
通过 jvm 启动参数 以及 jps pid进行拦截非法参数
 karthikuj/cve-2022-42889-text4shell-docker
Dockerized proof-of-concept for CVE-2022-42889 (Text4Shell) with script, DNS, and URL lookup-based RCE payloads for security testing and education.
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)