 s_r_e_e_r_a_j/ziprarhunter
ZipRarHunter is a powerful command-line ethical hacking tool designed to crack passwords of ZIP and RAR archive files using a wordlist.
 s_r_e_e_r_a_j/ftpbuster
FTPBuster is a powerful command-line brute-forcing tool designed to brute-force FTP, SFTP, and explicit FTPS servers by performing dictionary-based…
 s_r_e_e_r_a_j/sshbuster
SSHBuster is a powerful command-line SSH brute-forcing tool designed for ethical hacking and penetration testing. It performs dictionary-based…

 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
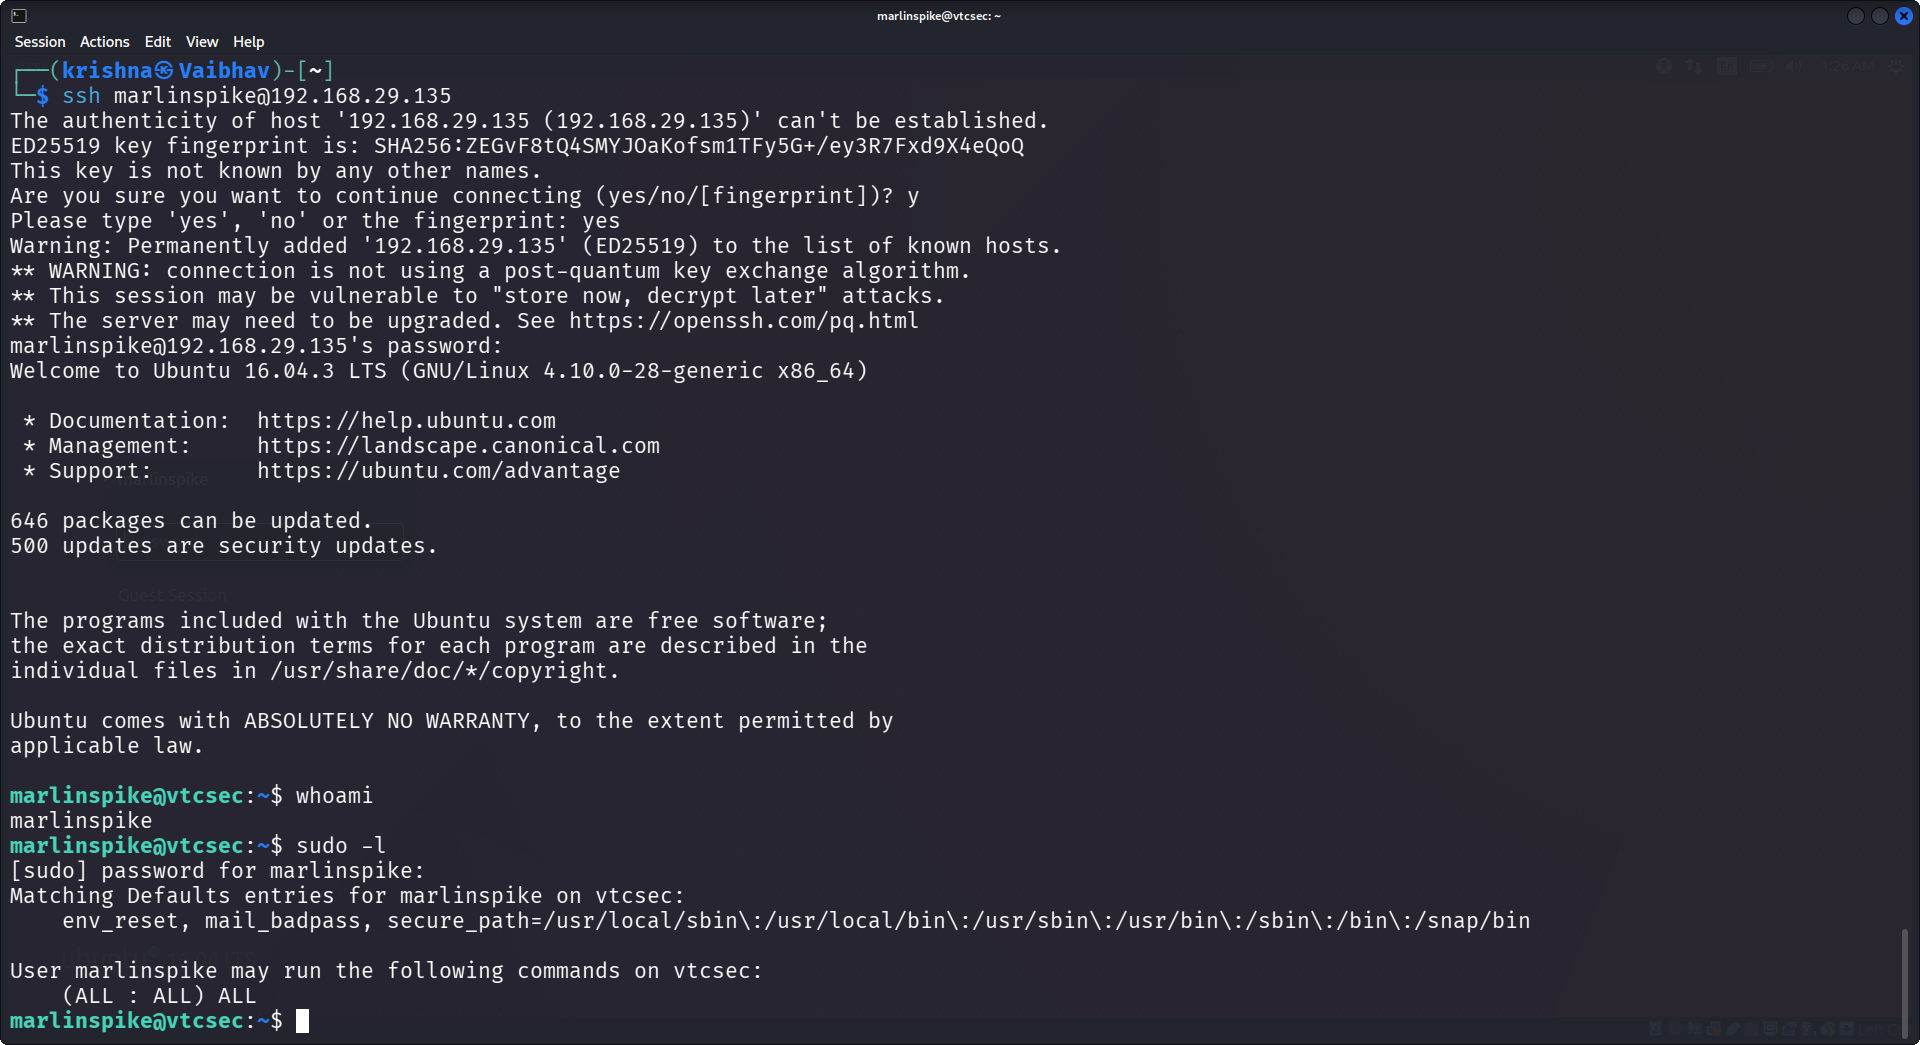 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 emrekybs/pikachu-smtp
Simple python script for brute force attack to smtp users
 squiblydoo/certreport
A tool to support the reporting of Authenticode Certificates by reducing the effort on individuals to report.
 n0isegat3/regpwnbrc4bof
Brute Ratel C4 BOF that exploits a registry symlink race condition in Windows Accessibility ATConfig to escalate privileges to SYSTEM by writing…
 guelfoweb/knockpy
Knock Subdomain Scan
 ishaklaz/hash-eye
**HashEye** is a powerful Python CLI tool for instantly detecting and analyzing hash types. It provides detailed information about hash formats,…
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
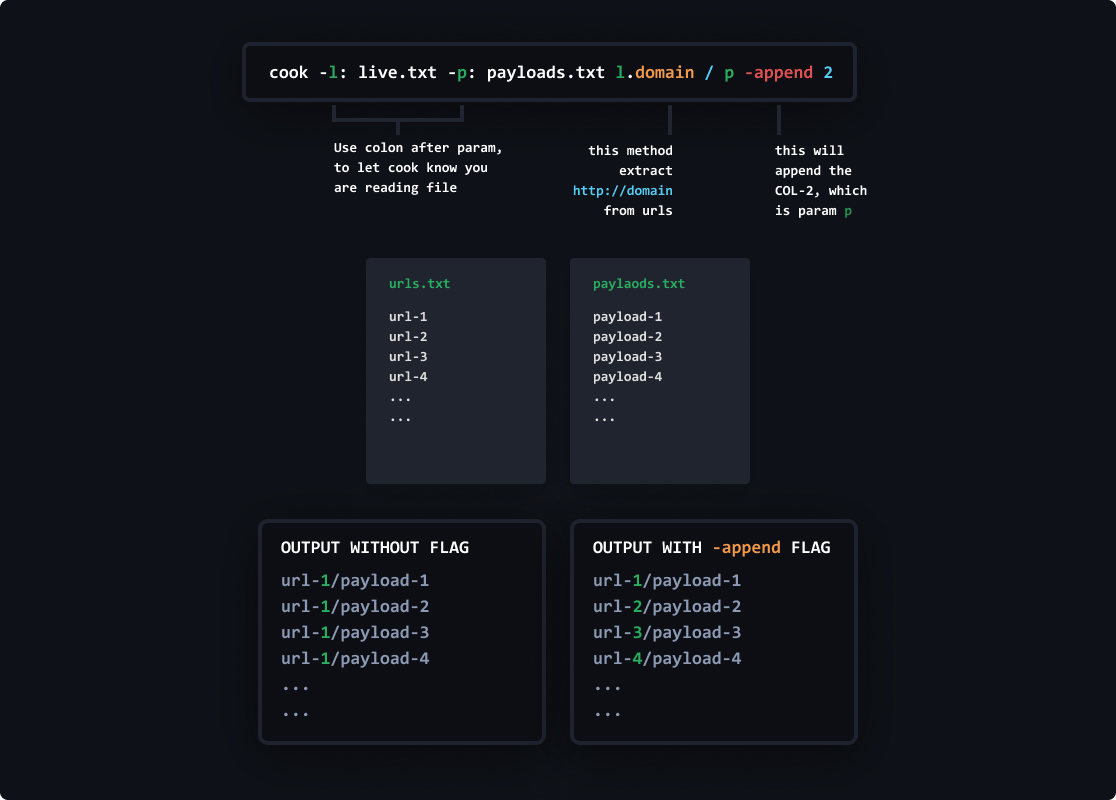 glitchedgitz/cook
A wordlist framework to fullfill your kinks with your wordlists. For security researchers, bug bounty and hackers.
 jazzband/django-defender
A simple super fast django reusable app that blocks people from brute forcing login attempts
 tw1sm/spraycharles
Low and slow password spraying tool, designed to spray on an interval over a long period of time
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…