

lynis
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
configuration-auditingdatabase-securitydefensive-tools+5
16.3k
cisofy/lynisAgentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 arkenfox/user.js
Firefox hardening template that applies privacy and security settings to reduce tracking, fingerprinting, and telemetry while preserving core browser…
 sneakynachos/cve-2026-85046-who-put-the-silverback-guerilla-in-the-wasm
Proof-of-concept exploit for CVE-2026-85046 in Chrome 152.0.7977.75, demonstrating type confusion in sort() to achieve arbitrary code execution via a…
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 bombobombone/cve-2026-74239
Proof of concept and technical write-up for CVE-2026-74239, a path traversal vulnerability in XenForo style archive imports on Windows, allowing file…
 bombobombone/cve-2026-73315
Proof-of-concept and technical write-up for CVE-2026-73315, an SSRF in XenForo's PayPal REST webhook handler allowing blind server-side HTTP requests.
 bombobombone/cve-2026-73314
Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…
 bombobombone/cve-2026-73311
Proof-of-concept exploit demonstrating OAuth2 authorization code reuse in XenForo before 2.3.13, allowing token replay and multiple token families.
 bombobombone/cve-2026-73310
Proof of concept and technical write-up for CVE-2026-73310, an OAuth2 authorization code redirect URI binding flaw in XenForo before 2.3.13,…
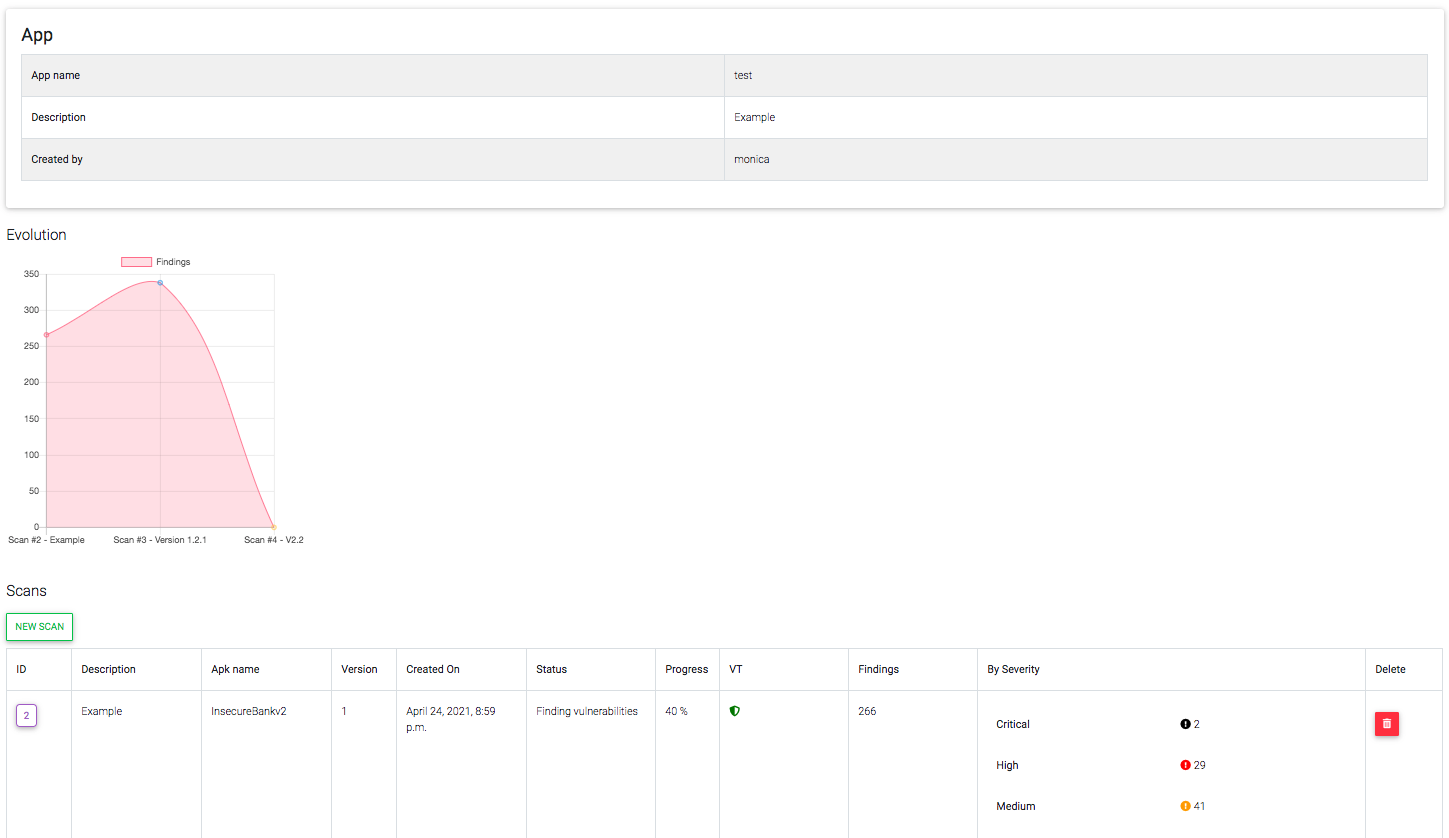 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 amis13/spip-cve-2024-23659-
SPIP (CVE-2024-23659) script with native python3 dependencies
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 linan-oo/cve-2026-52307
Proof-of-concept for CVE-2026-52307, an authenticated stored XSS in 1CMS v5.6 Column Management, with reproduction steps and impact analysis.