
Grafana-Final-Scanner
 zierax/grafana-final-scanner
Grafana scanner with all public CVEs that I collected in one script to make grafana testing easier
configuration-auditinginformation-gatheringvulnerability-analysis+3
244
zierax/grafana-final-scannerGrafana scanner with all public CVEs that I collected in one script to make grafana testing easier
 testardou/cve-2026-65540
Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
 maximilianomeyer/cve-2026-33017
Proof-of-concept implementation for CVE-2026-33017, demonstrating the vulnerability for authorized security testing and research.
 jp.louvel/ncstatuscheck
Monitoring centralisé pour instances Nextcloud multiples
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 hakaioffsec/cve-2026-63642
Proof-of-concept exploit scripts for CVE-2026-63642 and CVE-2026-63643, SSRF vulnerabilities in MagicMirror²'s Calendar module allowing…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 ivanesk315/cve-2026-42613
PHP proof-of-concept for CVE-2026-42613, demonstrating exploitation of the referenced vulnerability.
 ivanesk315/cve-2026-13181-telerik
Proof-of-concept exploit for CVE-2026-13181 affecting Telerik web components, demonstrating remote code execution via crafted requests.
 coroner/cryptolyzer
Multi-protocol cryptographic analyzer auditing TLS, SSL, SSH, IKE, DNSSEC, and HTTP security headers. Detects 400+ cipher suites, generates JA3/HASSH…
 soskalai/cve-2026-77578
Python proof-of-concept exploiting CVE-2026-77578, an authenticated path traversal in Xibo CMS that reads arbitrary local files via crafted XML…
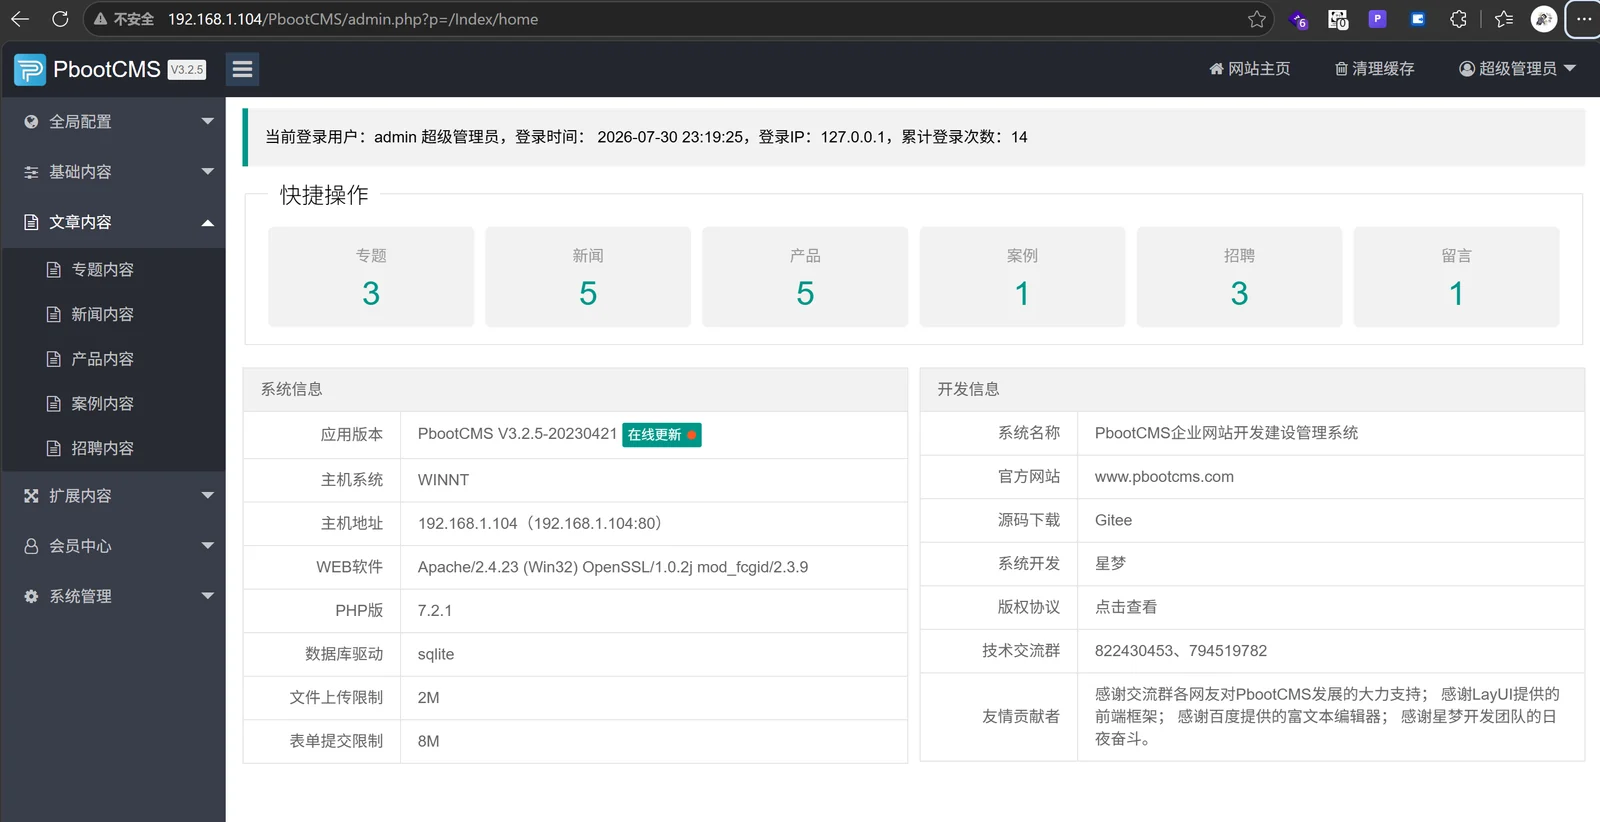 jhli07/cve-2026-79387-pbootcms-sql-injection
Proof-of-concept for CVE-2026-79387, an authenticated SQL injection in PbootCMS user management allowing arbitrary field updates and account takeover.
 owasp/threat-dragon
An open source threat modeling tool from OWASP
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 4ybrick/cve-2026-79303
Proof-of-concept for CVE-2026-79303, a critical boolean-blind SQL injection in Kaiten affecting order_by and order_direction parameters, with…