
c-copy-fail
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
binary-exploitationexploitationexploit-frameworks+3
1
openpixelsystems/c-copy-failC-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 mr-bv/copy-fail-cve-2026-31431-exploit-in-c
C exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability in the AF_ALG AEAD path, using splice() to influence cached file…
 ikow/cve-2026-31431-live-code-corruption
CVE-2026-31431 (Copy Fail) novel exploit: live code corruption via page cache. Overwrites libc exit() code through MAP_PRIVATE page sharing — affects…
 guiimoraes/cve-2026-31431
Python implementation of a Linux kernel local privilege escalation exploit for CVE-2026-31431, leveraging xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW to…
 julichaan/cve-2026-31431-python-copyfail-poc
Python exploit for CVE-2026-31431, a Linux kernel privilege escalation via page cache corruption of setuid binaries, achieving root access.
 pvpaulo01/cve-2026-31431
Esse documento descreve o Exploit publico em python
 361way/cve-2026-31431
Exploit for CVE-2026-31431 that escalates privileges to root, with a detection mode and C implementation for portability.
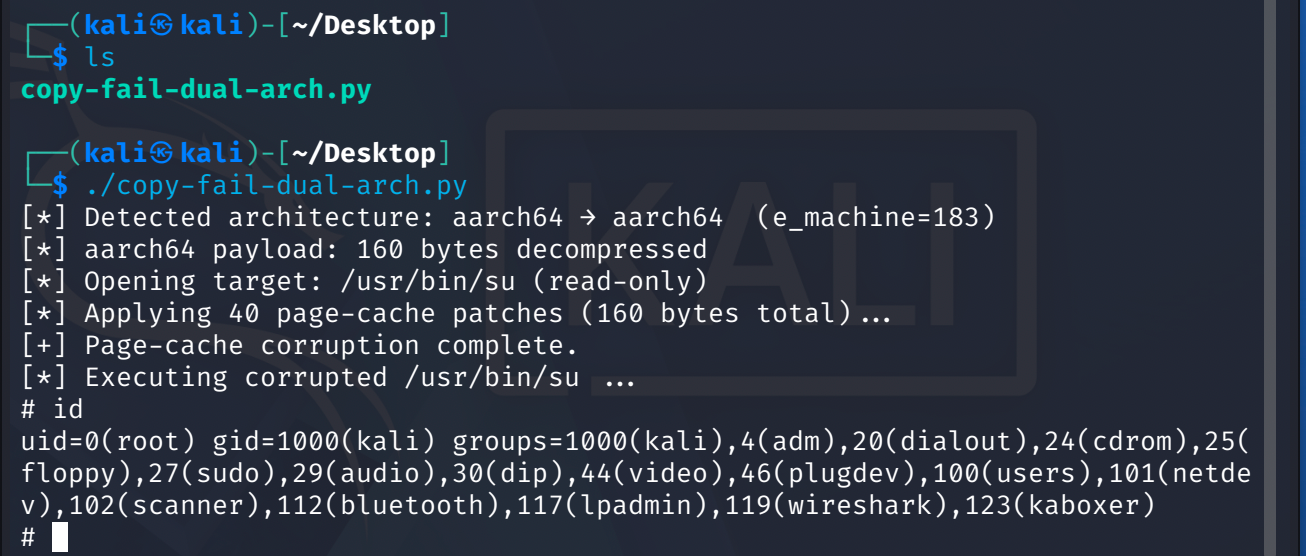 0xer0/cve-2026-31431-copy-fail-add-arm64
Python exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG and splice() to write to page cache, gaining root on arm64…
 starxsky/cve-2026-31431
Provides attack source code and sniffing tools for CVE-2026-31431, a kernel vulnerability, along with mitigation instructions including disabling the…
 iblamenear/cve-2026-31431-copy-fail---advanced-lpe-proof-of-concept---c-rewrite
Copy Fail (CVE-2026-31431) is a logic bug in the Linux kernel's authencesn cryptographic template. It lets an unprivileged local user trigger a…
 razvanduda/ghostshell
CVE-2026-31431 — Local Privilege Escalation via Linux Kernel Page Cache Corruption
 0xn7y/cve-2026-31431
Logic bug in the kernel's authencesn cryptographic template that escalate privilege
 adityabhatt3010/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, abusing AF_ALG AEAD socket handling to achieve root shell access on vulnerable Linux kernels.
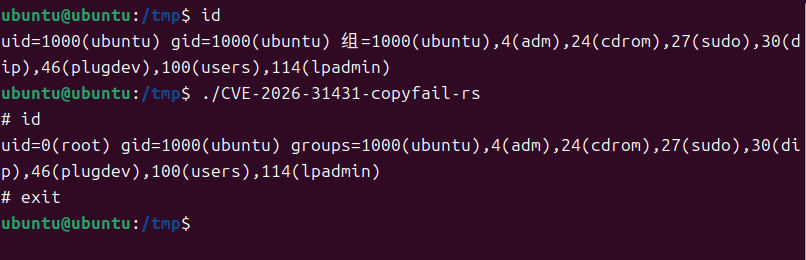 kanbaraakihito/cve-2026-31431-copyfail-rs
Pure Rust proof-of-concept for CVE-2026-31431, targeting Linux x86_64 kernels with AF_ALG AEAD support. Static musl build, no runtime dependencies,…
 rat5ak/cve-2026-31431-copyfail-static-elf--poc
Minimal 587-byte static ELF exploit for CVE-2026-31431, achieving local privilege escalation via AF_ALG splice page cache corruption. No libc or…
 ozergoker/cve-2026-31431-copy-fail
Exploit for CVE-2026-31431: a 732-byte Python script that exploits a straight-line logic flaw to gain root on all Linux distributions since 2017.
 threat9/routersploit
Exploitation Framework for Embedded Devices
 zhanghangorg/cve-2026-31431
Detector and proof-of-concept for a Linux kernel page-cache write vulnerability (CVE-2026-31431) in algif_aead, including a non-destructive scanner…