eternalblue-ms17-010-research

Controlled reproduction of CVE-2017-0144 (EternalBlue) in an isolated AWS EC2 lab — exploit analysis, Wireshark traffic capture, and MITRE ATT&CK…

Controlled reproduction of CVE-2017-0144 (EternalBlue) in an isolated AWS EC2 lab — exploit analysis, Wireshark traffic capture, and MITRE ATT&CK…

Remediation report for MegaQuagga Publishing validating the mitigation of CVE-2019-9978 through progressive defensive layering. Documents reverse…

Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.

A swiss-knife MCP server for analysing PCAP files

Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…

Qualitative TVRA for multi-VLAN enterprise lab scoring stored XSS and EternalBlue via CVSS v3.0 with ZAP, Nessus, and Wireshark evidence.

Multi-VM virtual network lab with GRE tunneling, nftables firewall, Active Directory, BIND9 DNS, and Docker services. Includes vulnerability…

It was developed to speed up the processes of SOC Analysts during analysis

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files

Python wrapper for tshark, allowing python packet parsing using wireshark dissectors

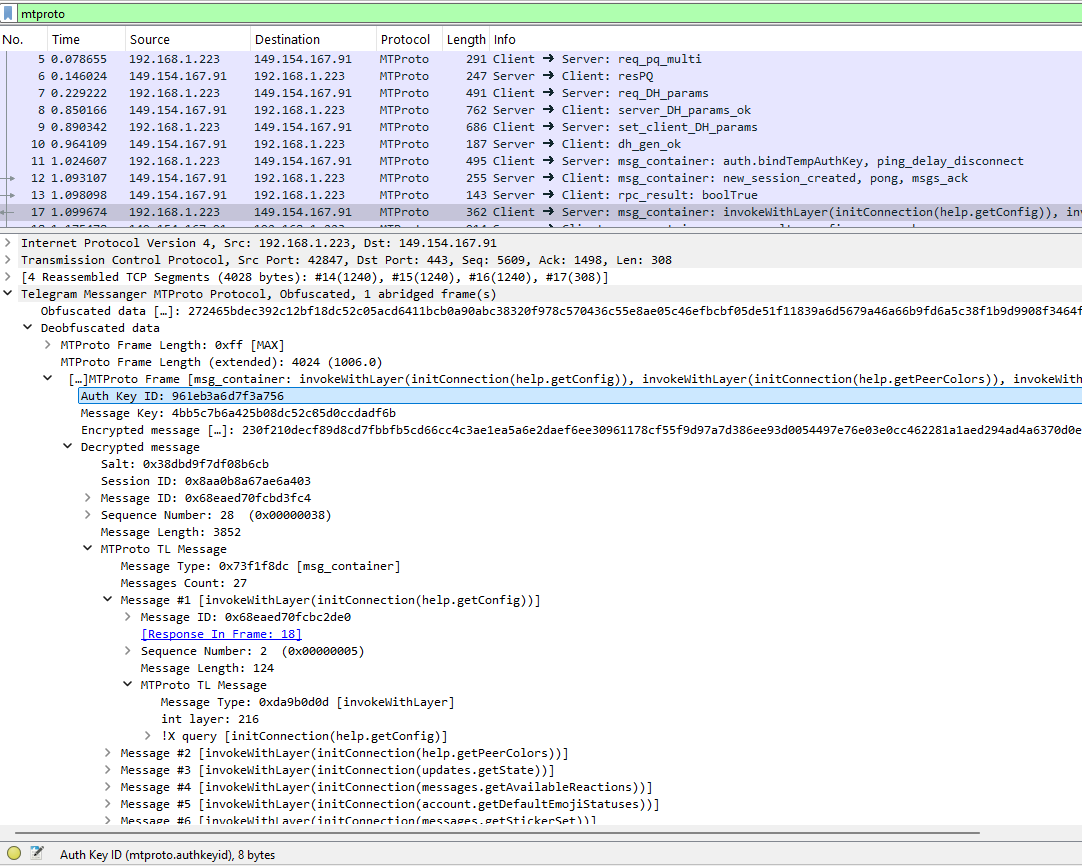
Wireshark plugin for dissecting the Telegram protocol

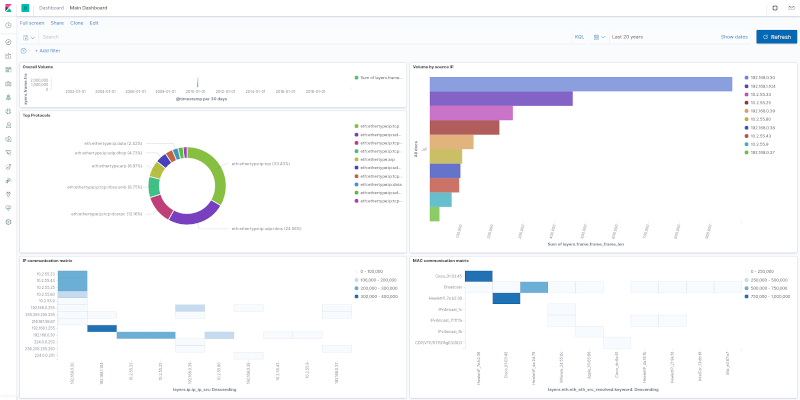
tshark + ELK analytics virtual machine

Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…

Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".

Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.

Wireshark RDP resources

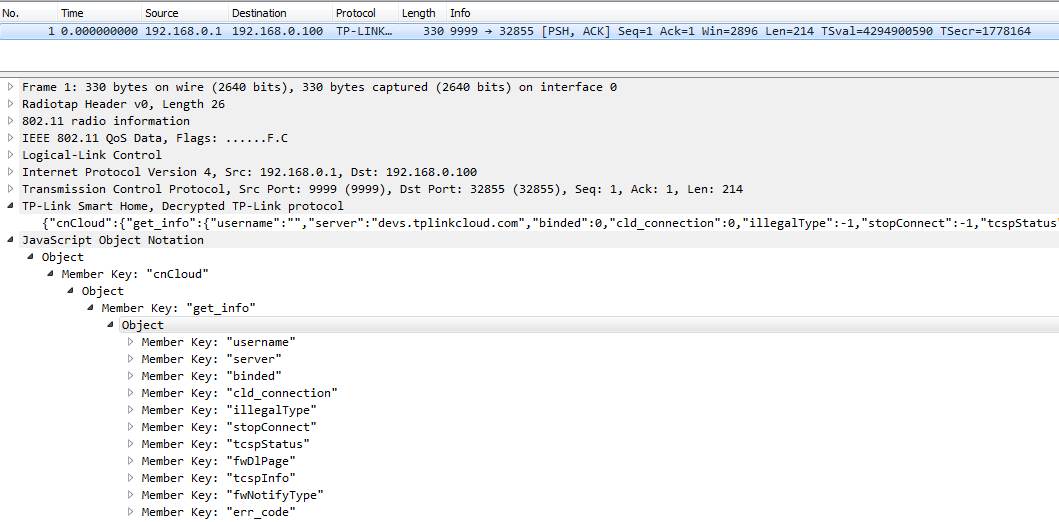
TP-Link WiFi SmartPlug Client and Wireshark Dissector

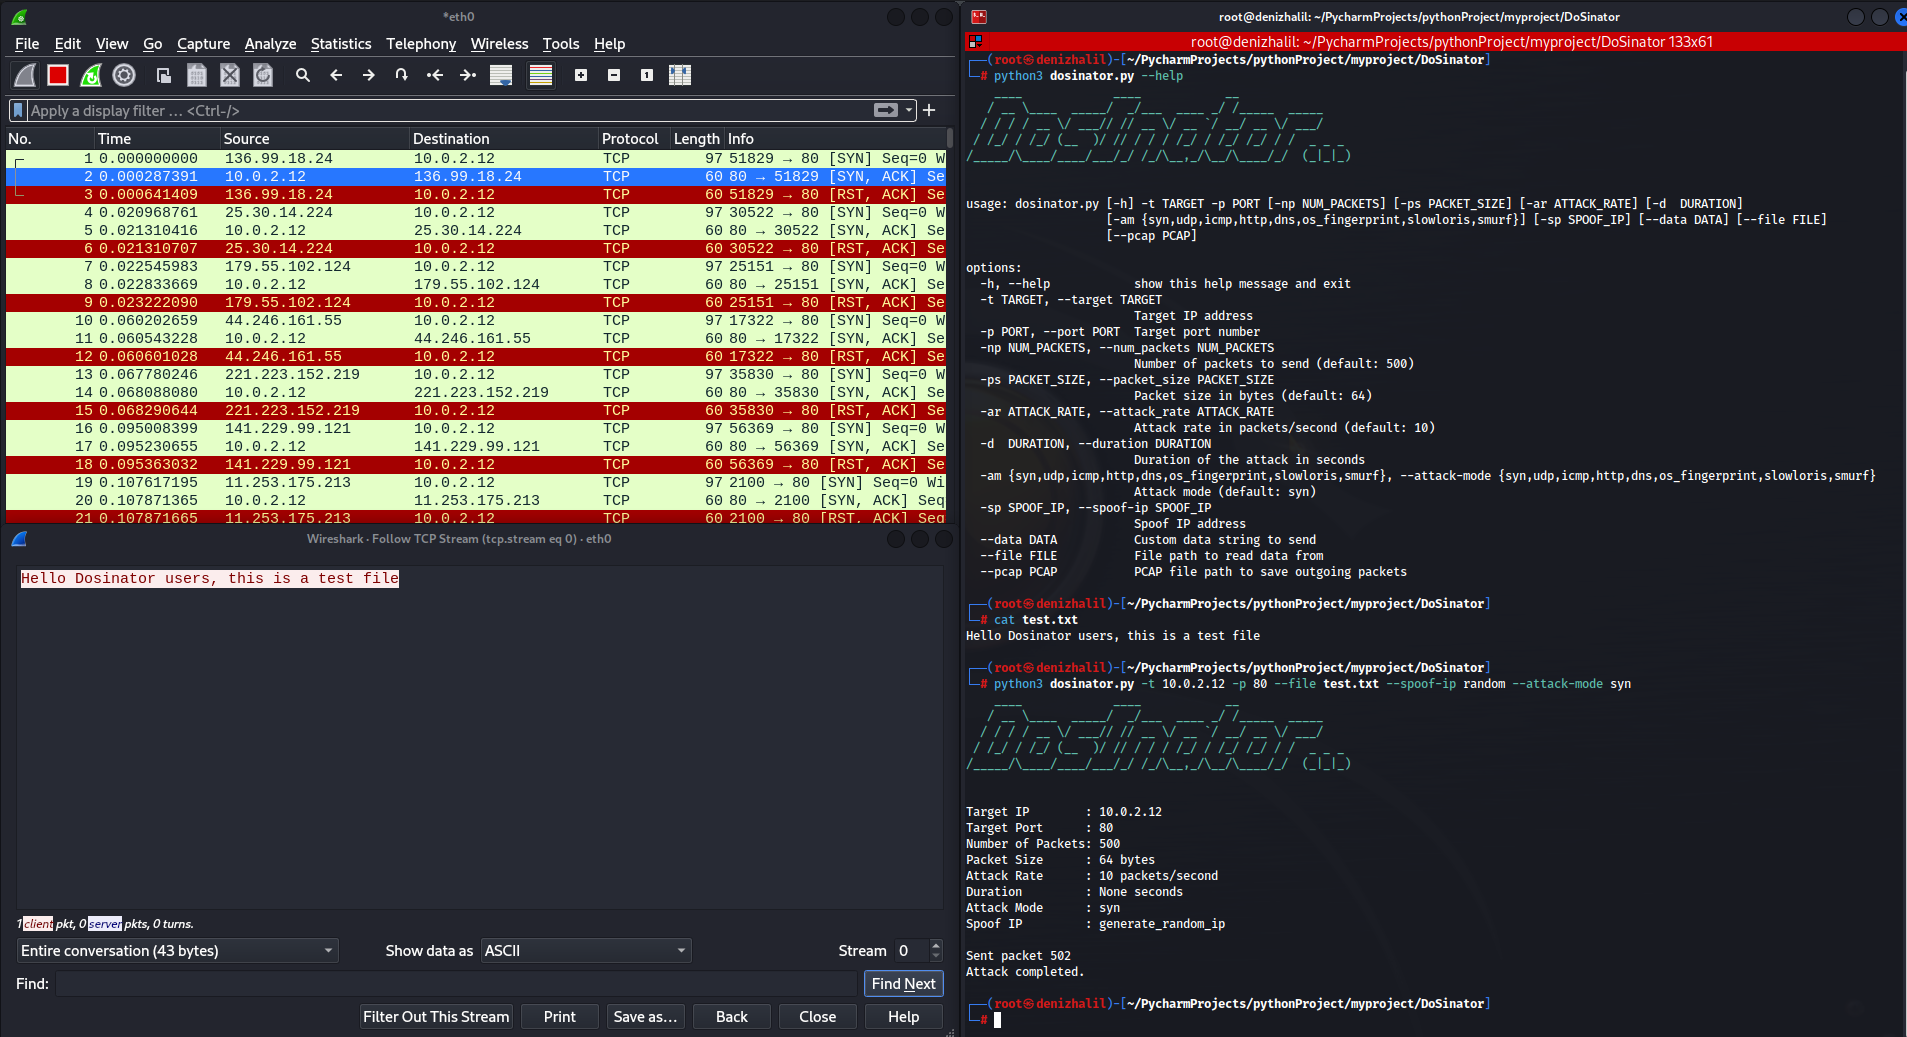
DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.