
Project-CVE-2026-33017
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
command-and-controlexploitationpayload-development+6
1
e4zyy/project-cve-2026-33017CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 katransefa/cve-2026-13714
Unauthenticated RCE exploit for Realtyna WPL < 5.3.0 that uploads a PHP webshell via hardcoded API key and executes arbitrary system commands.
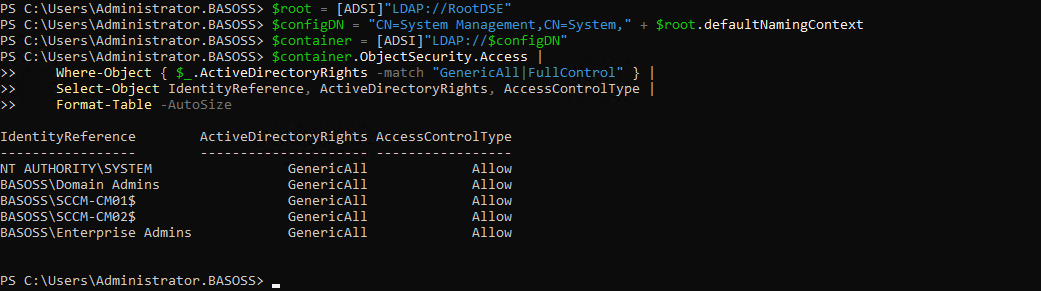 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
 1xpwn/cve-2025-32463
This CVE addresses a vulnerability in sudo versions 1.9.14 to 1.9.17, enabling unauthorized local privilege escalation to root access.
 gutierre0x80/cve-2026-59827
Technical analysis and proof of concept for CVE-2026-59827, a critical unsafe Java deserialization vulnerability in Metabase leading to remote code…
 ashrafdev/mysql-remote-root-code-execution
0ldSQL_MySQL_RCE_exploit.py (ver. 1.0) (CVE-2016-6662) MySQL Remote Root Code Execution / Privesc PoC Exploit For testing purposes only. Do no…
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
 jiahong-guan/log4j-shell-poc
A Proof-Of-Concept for the CVE-2021-44228 vulnerability.
 jendmaoul/xss2shell-cve-2026-64638
CVE-2026-64638 — WordPress Pre-Auth Reflected XSS → RCE via DOM Clobbering + Application Password Theft + REST API Plugin Activation. Dual-mode PoC…
 longwayhomie/polyengine
PolyEngine is an evasive PE packer designed for CTF challenges and low-level Windows security education. It focuses on bypassing EDR and AV…
 sam00/cve-2026-56158-.net-framework-rce-poc-exploit
Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 hackspeak/cve-2026-60004
Gitea diffpatch RCE (CVE-2026-60004) PoC - repo-write to RCE as Gitea service account
 0xdak/cve-2025-32463_exploit
Local privilege escalation exploit for sudo 1.9.14-1.9.17 that abuses CVE-2025-32463 chroot handling, planting a malicious NSS library constructor to…
 trevocastles/cve-2026-31431-copy-fail
Exploit PoC for CVE-2026-31431 that uses AF_ALG and splice() to overwrite Linux page cache and patch /usr/bin/su in memory, escalating unprivileged…
 777erp/cve-2026-49176_bof
CVE-2026-49176 WalletService LPE — standalone PoC + Cobalt Strike BOF (SYSTEM command on interactive session)
 codextf2/screenshotbof
An alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.