
stride-gpt
 mrwadams/stride-gpt
An AI-powered threat modeling tool that leverages OpenAI's GPT models to generate threat models for a given application based on the STRIDE…
ai-securityeducationpenetration-testing-frameworks+2
1.1k
mrwadams/stride-gptAn AI-powered threat modeling tool that leverages OpenAI's GPT models to generate threat models for a given application based on the STRIDE…
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 hamzamalik3461/cve-2026-20841
🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
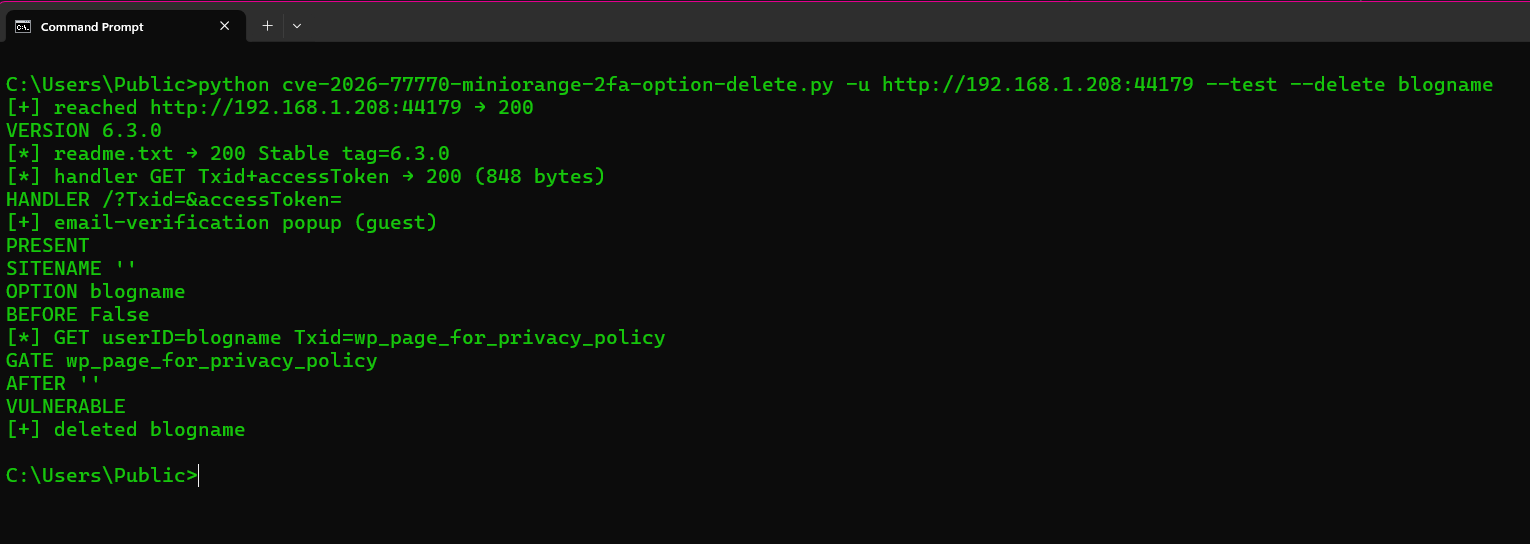 cflowsec/cve-2026-77770
Python PoC for CVE-2026-77770, an unauthenticated arbitrary WordPress option deletion flaw in the miniOrange 2FA plugin (<= 6.3.0) via the…
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 jp1337/easywall
Web interface for the nftables firewall on Linux, written in Go. The apply undoes itself after 120 seconds unless you confirm it — you cannot lock…
 dnsviz/dnsviz
Analyzes DNS delegation and DNSSEC security by probing resolvers and authoritative servers, then validating, diagnosing, and visualizing zone…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…

 roddhjav/apparmor.d
Comprehensive set of over 1500 AppArmor profiles to confine Linux system processes, desktops, and services, with support for multiple distributions…
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 wadesweaponshed/checkpoint-cve-webscanner
A web version of the bash scripts wrote for Check Point CVE-2026-50751 and CVE-2026-50752. This uses a local server to scan and make changes using…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.