

mitm
 0x0be/mitm
A simple yet effective python3 script to perform DNS spoofing via ARP poisoning
packet-sniffing-analysis
0x0be/mitmA simple yet effective python3 script to perform DNS spoofing via ARP poisoning
 paranoidninja/boomerang
Agent-server HTTP+TCP tunneling tool for exposing multiple internal services to external networks. Supports multi-level pivoting and SOCKS proxy…
 pkb1s/sharprelay
C# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…
 ridter/cve-2019-1040
CVE-2019-1040 with Exchange
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887
 al1ex/cve-2020-11652
Exploit for SaltStack CVEs (CVE-2020-11651/11652) enabling remote command execution on master/minions, file read/upload, and reverse shell.
 saharattackit/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) targeting Windows Netlogon to achieve privilege escalation and domain controller compromise.
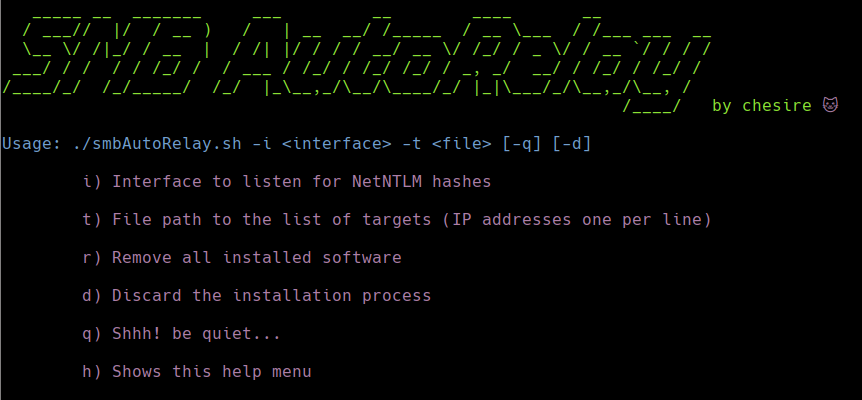 cheshireca7/smbautorelay
SMB Auto Relay provides the automation of SMB/NTLM Relay technique for pentesting and red teaming exercises in active directory environments.
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
 k8gege/pyladon
Ladon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…
 refi64/cve-2020-25265-25266
Proof-of-concept exploit demonstrating CVE-2020-25265 and CVE-2020-25266, using a crafted MP3 file to achieve arbitrary code execution via…
 b1ack0wl/cve-2020-1472
Exploit for CVE-2020-1472 (ZeroLogon) that resets the domain controller account password and enables DCSync for full domain compromise.
 sp00kyskelet0n/py-rdp-patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
 rasta-mouse/misctools
Miscellaneous Tools
 scorpioneslabs/dvs
D(COM) V(ulnerability) S(canner) AKA Devious swiss army knife - Lateral movement using DCOM Objects