
CVE-2020-16898
 advanced-threat-research/cve-2020-16898
CVE-2020-16898 (Bad Neighbor) Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
exploitationintrusion-detectionnetwork-security+1
209
advanced-threat-research/cve-2020-16898CVE-2020-16898 (Bad Neighbor) Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 djhohnstein/sharpchromium
.NET 4.0 CLR Project to retrieve Chromium data, such as cookies, history and saved logins.
 advanced-threat-research/cve-2020-16899
CVE-2020-16899 - Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
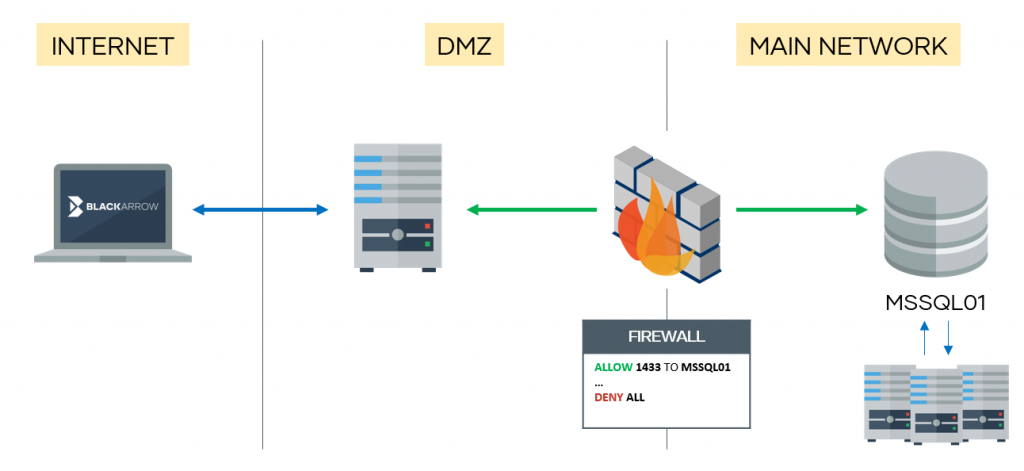 blackarrowsec/mssqlproxy
mssqlproxy is a toolkit aimed to perform lateral movement in restricted environments through a compromised Microsoft SQL Server via socket reuse
 corelight/sigred
Zeek package for detecting CVE-2020-1350 (SIGRed) Windows DNS server exploit attempts via large DNS SIG/KEY response analysis with configurable…
 citronneur/rdpy
Remote Desktop Protocol in Twisted Python
 cert-lv/cve-2020-0688
Scans networks for Microsoft Exchange servers vulnerable to CVE-2020-0688, using zmap for host discovery and TLS/version fingerprinting to identify…
 guokers/aioscan_cve-2020-0796
基于asyncio(协程)的CVE-2020-0796 速度还是十分可观的,方便运维师傅们对内网做下快速检测。
 dhoomralochana/scanners-for-cve-2020-0796-testing
Scanners List - Microsoft Windows SMBv3 Remote Code Execution Vulnerability (CVE-2020-0796)
 butrintkomoni/cve-2020-0796
Identifying and Mitigating the CVE-2020–0796 flaw in the fly
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
 robertdavidgraham/rdpscan
A quick scanner for the CVE-2019-0708 "BlueKeep" vulnerability.
 gh0st0ne/rdpscan-bluekeep
A quick scanner for the CVE-2019-0708 "BlueKeep" vulnerability.
 oneoy/bluekeep
CVE-2019-0708 bluekeep 漏洞检测
 syriusbughunt/cve-2019-0708
PoC about CVE-2019-0708 (RDP; Windows 7, Windows Server 2003, Windows Server 2008)
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability