

Yasso
 sairson/yasso
强大的内网渗透辅助工具集-让Yasso像风一样 支持rdp,ssh,redis,postgres,mongodb,mssql,mysql,winrm等服务爆破,快速的端口扫描,强大的web指纹识别,各种内置服务的一键利用(包括ssh完全交互式登陆,mssql提权,redis一键利用,mysql数据库…
exploitationlateral-movementpassword-attacks+5
1.6k
sairson/yasso强大的内网渗透辅助工具集-让Yasso像风一样 支持rdp,ssh,redis,postgres,mongodb,mssql,mysql,winrm等服务爆破,快速的端口扫描,强大的web指纹识别,各种内置服务的一键利用(包括ssh完全交互式登陆,mssql提权,redis一键利用,mysql数据库…
 antoniococo/malseclogon
A little tool to play with the Seclogon service
 comparedarray/printix-cve-2022-29551
A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…
 hackerxphantom/spoof_anymail
Most Powerful Send Fake Mail Using Any Mail I'd undetectable
 marcorosa/cnc-botnet-in-python
C&C Botnet written in Python with fabric
 jmousqueton/poc-cve-2022-30190
POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina
 juliourena/sharpnopsexec
Get file less command execution for lateral movement.
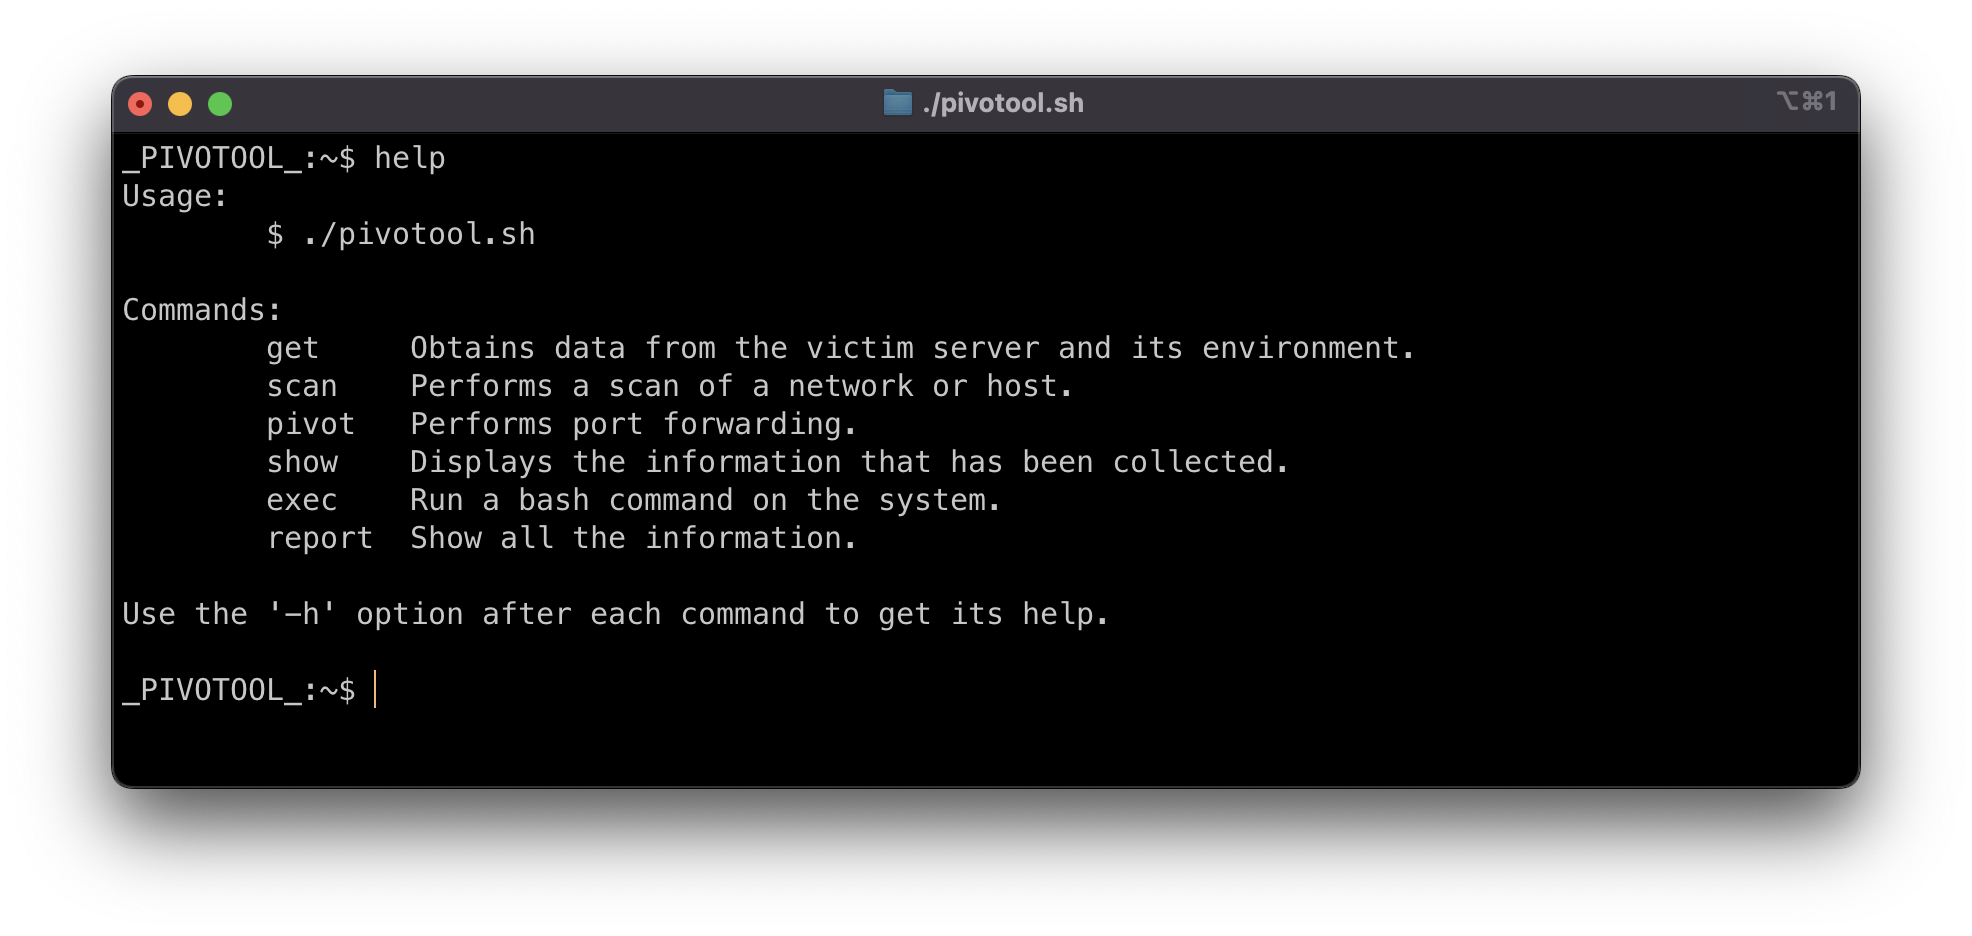 artusec/pivotool
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
 0xflagplz/ms-msdt-office-rce-follina
CVE-2022-30190 | MS-MSDT Follina One Click
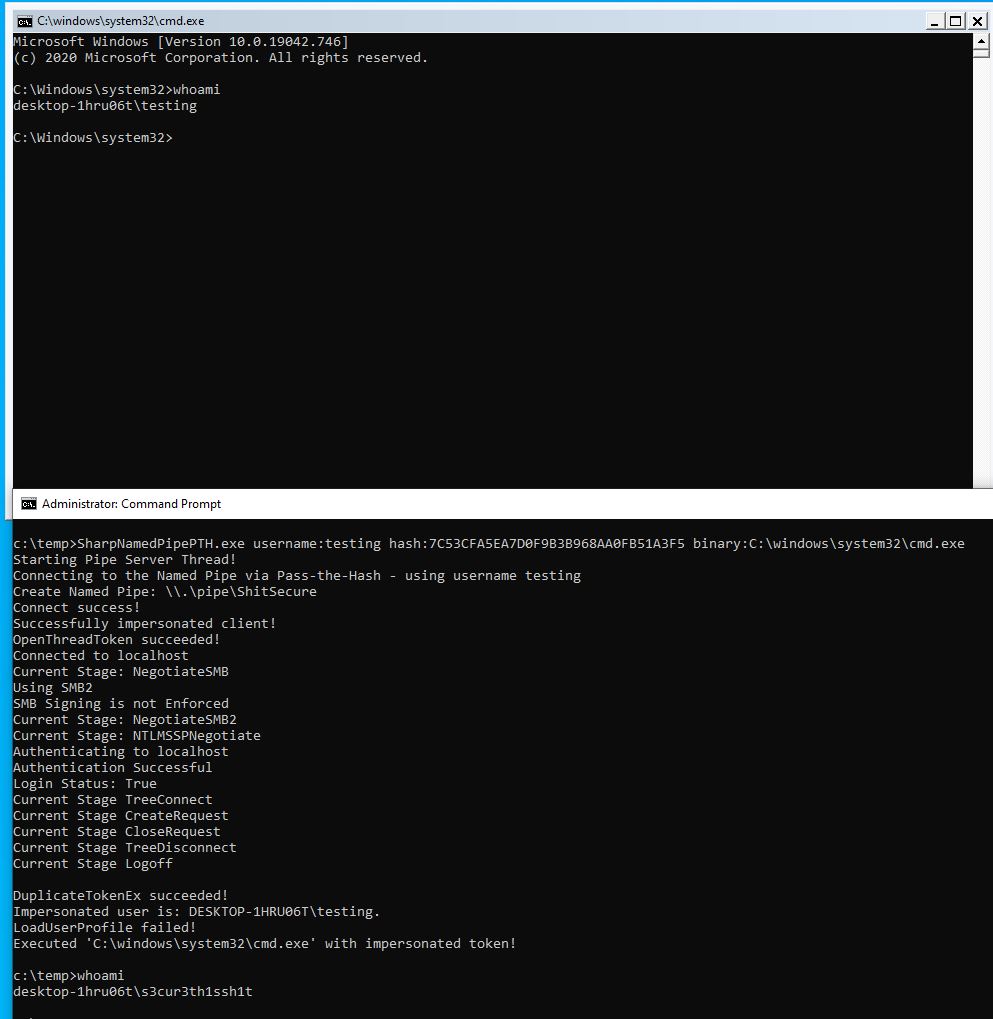 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 cube0x0/krbrelay
Kerberos relay framework for Windows environments enabling authentication relay, privilege escalation, and lateral movement via LDAP, SMB, HTTP, and…
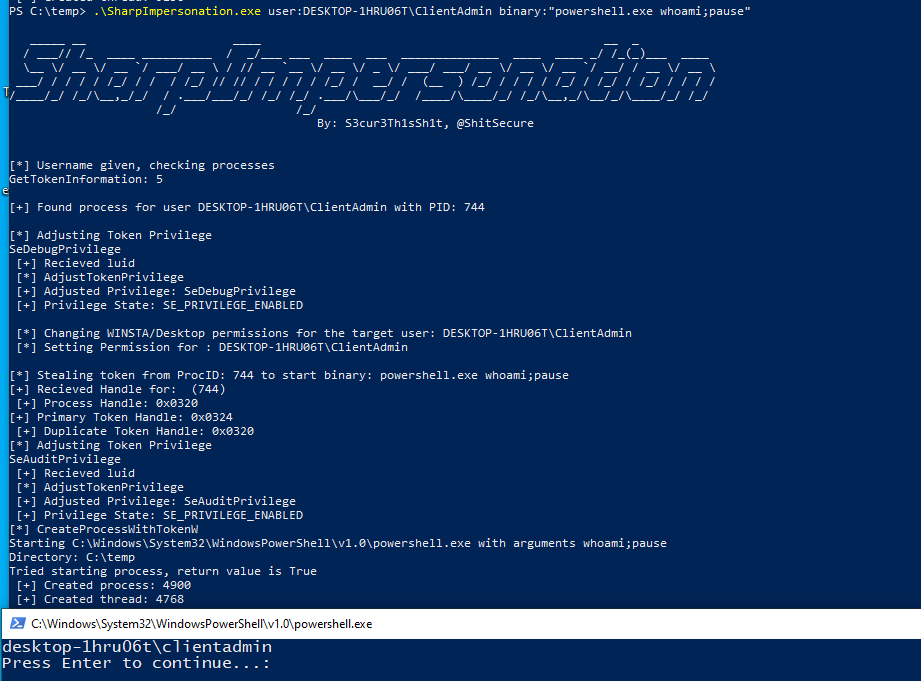 s3cur3th1ssh1t/sharpimpersonation
A User Impersonation tool - via Token or Shellcode injection
 presentdaypresenttime/shai_hulud
Worm written in python, abuses CVE-2020-7247
 manhndd/cve-2019-6329
Local Privilege Escalation in HP Support Assistant
 nettitude/sharpwsus
C# tool for lateral movement through WSUS by creating, approving, and deploying malicious updates to target Windows clients in Active Directory…
 nettitude/malsccm
Abuse SCCM servers to deploy malicious applications to managed hosts for lateral movement and red team operations.
 chron1k/oxide_hive
Exploit for CVE-2021-36934
 auduongxuan/cve-2022-26809
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.