
USP
 grahamhelton/usp
Establishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)
payload-developmentpersistence-mechanismspost-exploitation+2
153
grahamhelton/uspEstablishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)
 cracked5pider/eop24-26229
A firebeam plugin that exploits the CVE-2024-26229 vulnerability to perform elevation of privilege from a unprivileged user
 klezvirus/koppeling-p
Adaptive DLL hijacking / dynamic export forwarding - EAT preserve
 paranoidninja/brute-ratel-c4-community-kit
This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/)
 itzheartzz/mass-cve-2024-27956
Proof-of-concept exploit for CVE-2024-27956 SQL injection in ValvePress Automatic plugin. Creates admin users in WordPress to achieve remote code…
 mbadanoiu/cve-2023-51518
CVE-2023-51518: Preauthenticated Java Deserialization via JMX in Apache James
 cybersectroll/trolldump
Injects x64 managed DLLs into GUI processes via SetWindowsHook, with a modular C# payload runner and LSASS dump POC for red-team/offensive Windows…
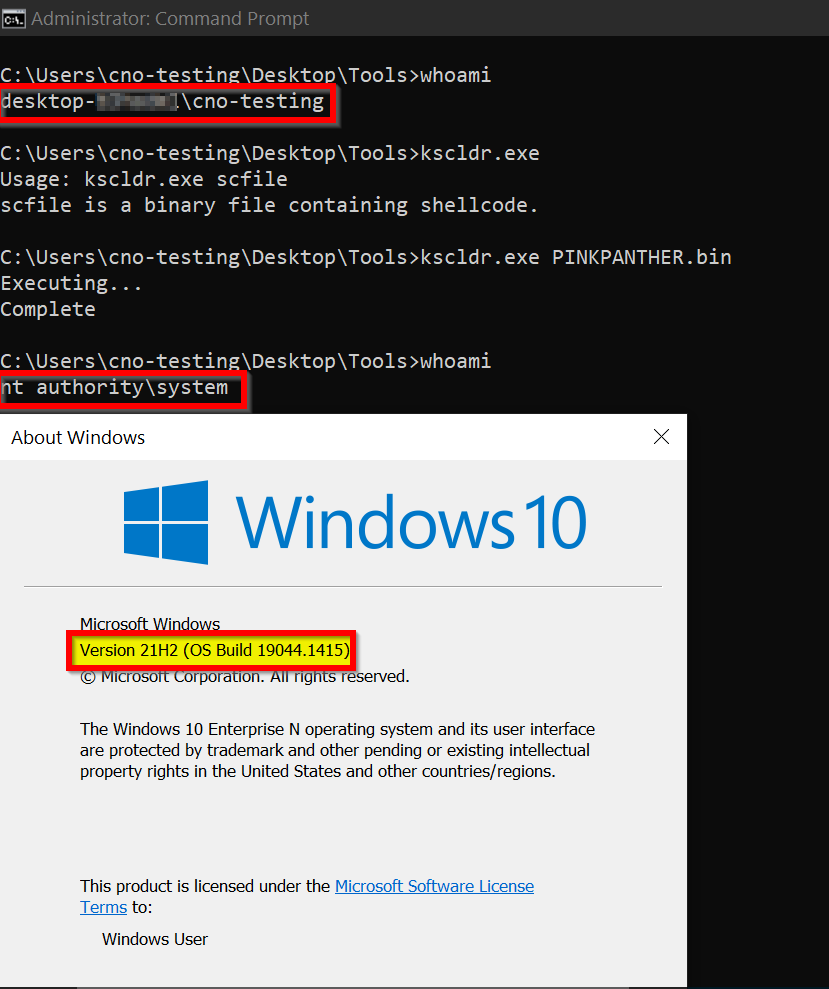 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 momika233/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, demonstrating command injection in Palo Alto PAN-OS with a Python-based backdoor, persistence via…
 void0red/cve-2023-32233
Linux kernel privilege escalation exploit for CVE-2023-32233 using nft_quota UAF, ROP chain, and modprobe_path overwrite to gain root on kernels…
 wra7h/flavortown
Various ways to execute shellcode
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
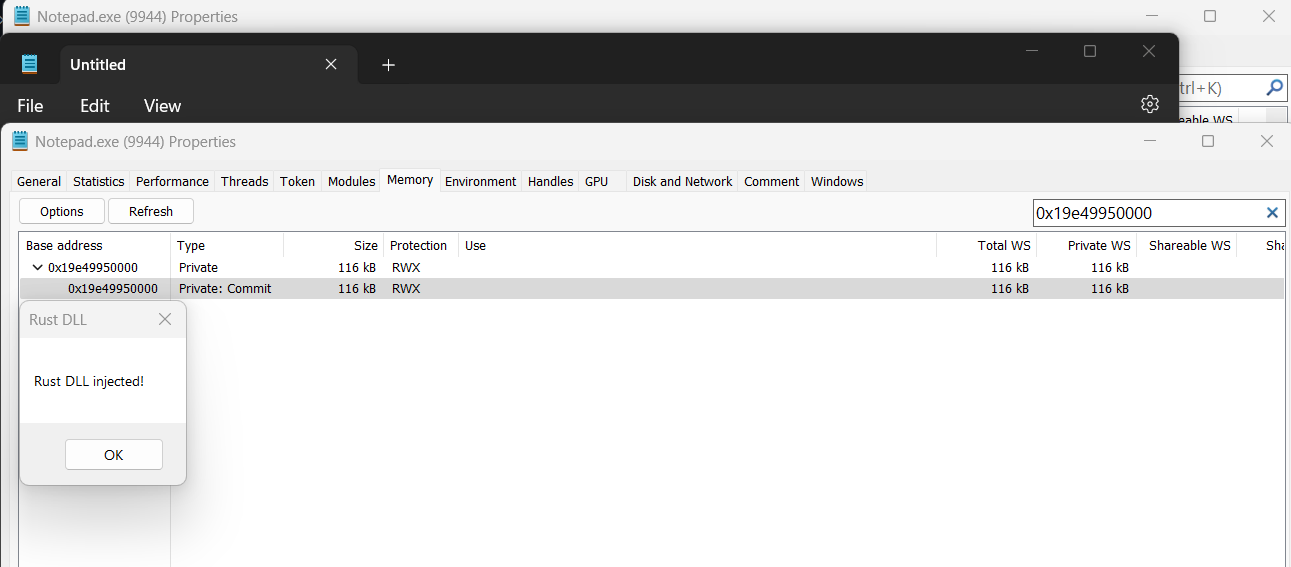 memn0ps/venom-rs
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
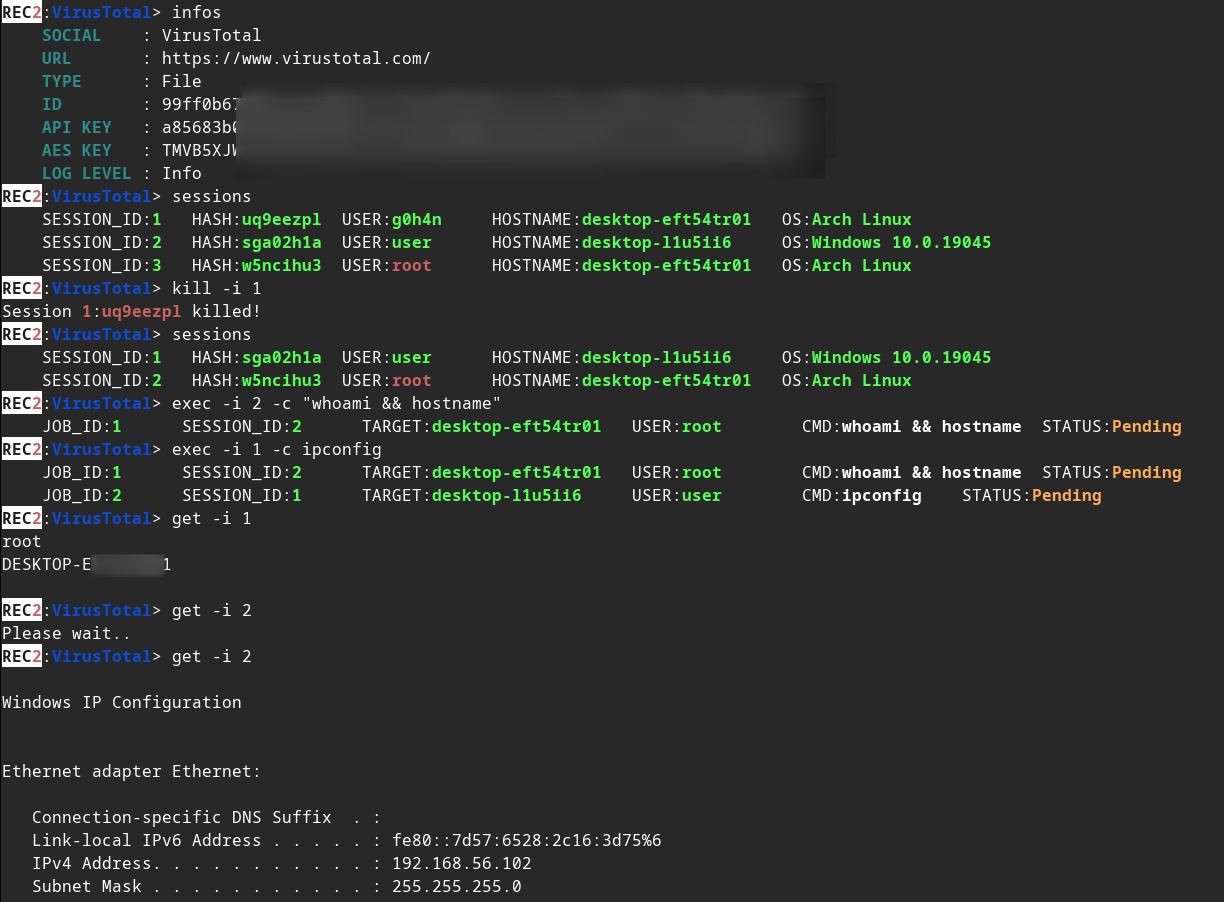 g0h4n/rec2
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…
 dosx-dev/dotnet_xorcryptor
A new simple and powerfull packer for malware
 leviathanfromdeepsea/iberyanbytes
PowerShell-based Active Directory enumeration tool for gathering network configuration, domain objects, user sessions, share permissions, and…
 whoami-chmod777/cve-2021-1675-cve-2021-34527
PowerShell exploit for PrintNightmare (CVE-2021-1675) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…