
CVE-2026-73678-PoC
 boreas37/cve-2026-73678-poc
CVE-2026-73678 — MindsDB Minds Platform unauthenticated RCE via scratchpad exec (CVSS 10.0). Verified end-to-end with real LLM
ai-securityexploitationvulnerability-analysis+1
1
boreas37/cve-2026-73678-pocCVE-2026-73678 — MindsDB Minds Platform unauthenticated RCE via scratchpad exec (CVSS 10.0). Verified end-to-end with real LLM
 iamrajkumar1995/cve-2025-5781_freepbx
Proof-of-concept exploit for FreePBX Endpoint module CVE-2025-5781: chains unauthenticated SQL injection with database manipulation and scheduled…
 alixploit22/cve-2026-6440
mencari sebuah kerentanan, wodpres dan mengungah shell di kerentanan wodpres tersebut
 alixploit22/cvex2shel
CVE-2026-64638 adalah kerentanan Pre-Auth Reflected Cross-Site Scripting (XSS) di WordPress yang ditemukan pada tahun 2026. Kerentanan ini…
 isukasanuj/cve-2025-70559
Python exploit for CVE-2025-70559 targeting an upload directory bypass/remote code execution; run with LHOST and LPORT to establish a reverse shell.

 nu11secur1ty/cve-2021-44228-vuln-app
Dockerized vulnerable web application demonstrating the Log4j CVE-2021-44228 remote code execution vulnerability for educational exploitation and…
 codeb0ssx/cve-2026-72898-poc
Proof-of-concept exploit for CVE-2026-72898 in Metabase, with technical reproduction steps and usage guidance for validating the vulnerability during…
 perfectpoh/cve-2019-10070-apache-atlas-xss
 cynepmyx/nginx-rift-check
Detects the CVE-2026-42945 rewrite pattern in nginx configs: rewrite with ? in the replacement plus an unnamed capture consumed in the same location
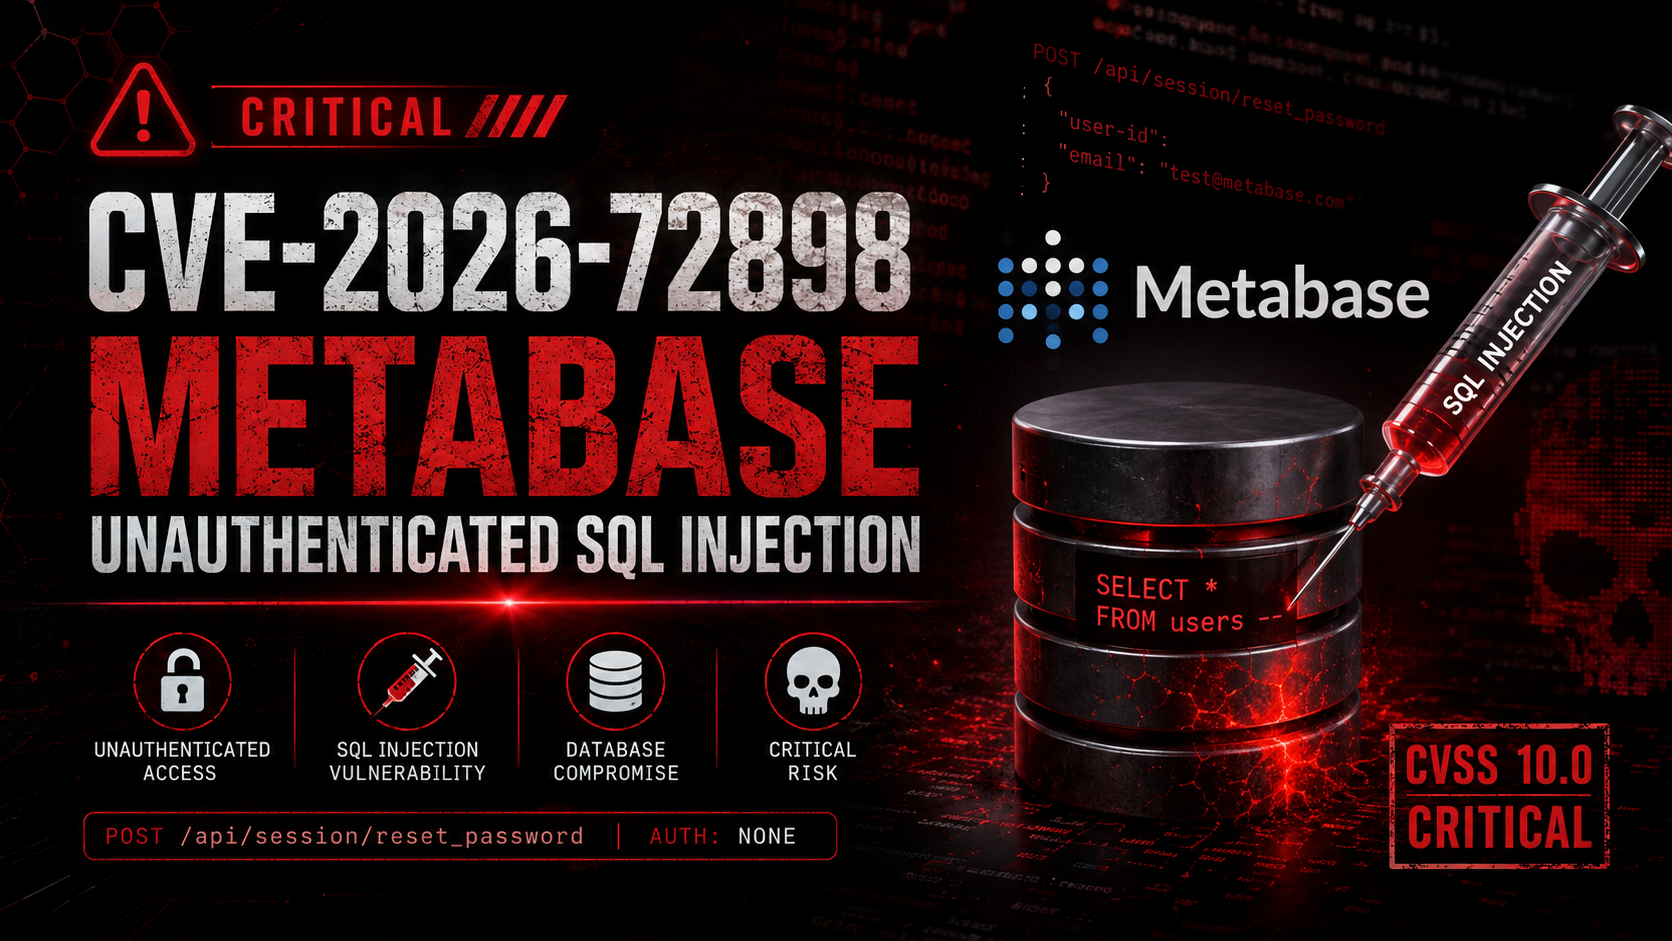 0xblackash/cve-2026-72898
CVE-2026-72898
 jobusa755-a11y/cve-2026-65640-
WordPress Core <= 7.0.3 - Authenticated (Author+) Remote Code Execution via Malicious File Upload
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 boreas37/cve-2026-33267-poc
CVE-2026-33267 — Apache Traffic Server @ header internal-metadata spoof (CVSS 10.0). Verified: @ headers leak to plugins on 10.1.2, stripped on 10.1.4
 leoelsolh/cve-2026-69263
MCP environment-variable blocklist bypass leads to unauthenticated RCE in Flowise 3.1.1
 dodgenefoli/cve-2025-64512
Automated proof-of-concept exploit for CVE-2025-64512 that accepts Target and Upload_dir parameters to test vulnerable file-upload functionality in…
 mluex0/cve-2026-23744-poc
CVE-2026-23744 is an unauthenticated command injection in MCPJam Inspector ≤1.4.2 via /api/mcp/connect. This POC exploits it by sending a crafted…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…